 Do Son
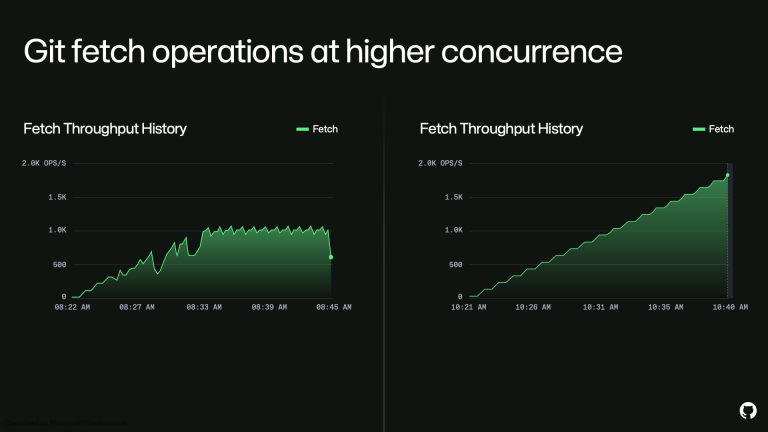
This week, Microsoft’s code hosting platform, GitHub, experienced a prolonged and widespread outage. This disruption significantly impacted...
Do Son
Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.
At a glance Malware family Projextor (Electron-based) Threat actor Unknown; shared code base, no confirmed single operator...
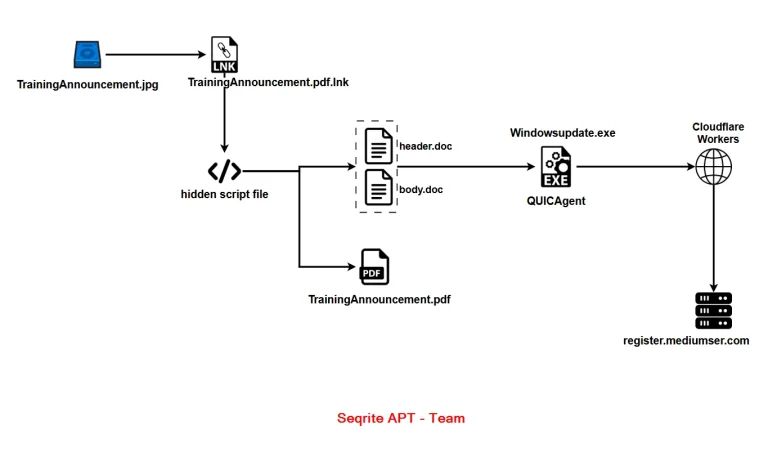
At a glance Actor or group Unnamed China-nexus actor (moderate confidence) Activity type Cyber espionage, custom Go...
Google continues to fortify the memory management framework across the Android ecosystem, as noted on the Android...
Following feedback from numerous gamers, Microsoft is officially investigating Windows 11 gaming issues that emerged after installing...
Japanese cloud computing and data center services provider Sakura Internet recently issued a security advisory disclosing that...
TL;DR CVE-2026-77647 is a CVSS 9.8 unauthenticated remote code execution flaw in the SPIP CMS. It affects...
TL;DR TP-Link patched three Omada gateway vulnerabilities. The most severe, CVE-2026-19586, is a pre-authentication OS command injection...
Update: Microsoft updated its safety alert on August 21, 2026. Initially, the report marked the bug as...
TL;DR VMware disclosed four Spring Security vulnerabilities. The most severe, CVE-2026-59270, rates CVSS 9.4 (CRITICAL). Its embedded...
TL;DR CVE-2026-77176 is a CVSS 8.1 flaw in Kata Containers genpolicy. A malicious operator can mount arbitrary...
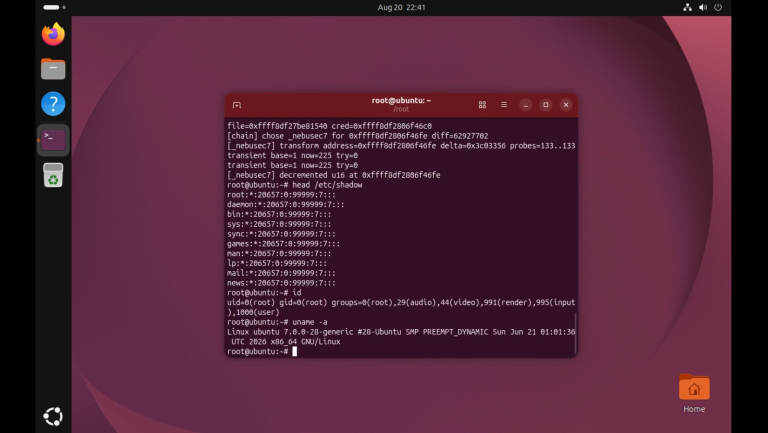
TL;DR A researcher published proof-of-concept exploit code for CVE-2026-52929, a Linux kernel SCTP flaw rated CVSS 7.5....
TL;DR VMware disclosed seven Spring GraphQL vulnerabilities and related Spring Cloud flaws on August 20, 2026. All...
TL;DR CISA added two TrueConf Server flaws to its Known Exploited Vulnerabilities catalog. Tracked as CVE-2026-72529 and...
At a Glance Actor Unattributed; infrastructure overlaps with DPRK-linked activity (Wiz) Activity Software supply chain attack via...
TL;DR Google shipped a Chrome Stable channel update with seven security fixes. The most severe, CVE-2026-76017, is...
Two high-severity Spring Integration vulnerabilities threaten application security. Specifically, CVE-2026-59307 allows remote code execution via a deserialization...
TL;DR Frauscher patched eight flaws in its FDS102 railway diagnostic system on August 20, 2026. The most...
TL;DR Apache InLong patched three flaws in version 2.4.0. The most notable is an Apache InLong SQL...
TL;DR Dell patched three flaws in its PowerStore T storage family. The most severe, CVE-2026-67271, scores a...
TL;DR The maintainers of vm2 patched three critical flaws on August 17, 2026. The most severe, CVE-2026-47686,...
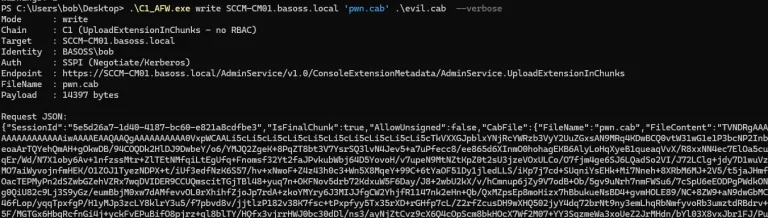
TL;DR Microsoft patched CVE-2026-47301, an elevation of privilege flaw in Configuration Manager (SCCM). A researcher published proof-of-concept...