 Do Son
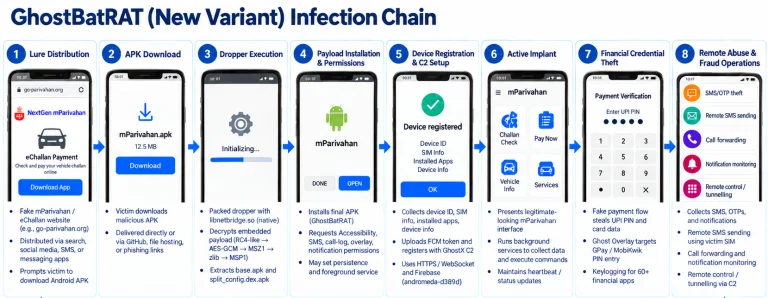
At a Glance Malware Family GhostBat RAT (operating within the GhostX operator ecosystem) Threat Actor Confirmed as...
Malware
At a Glance Malware Family Hirudo banking trojan (Android remote access trojan and app-patching toolkit) Threat Actor...
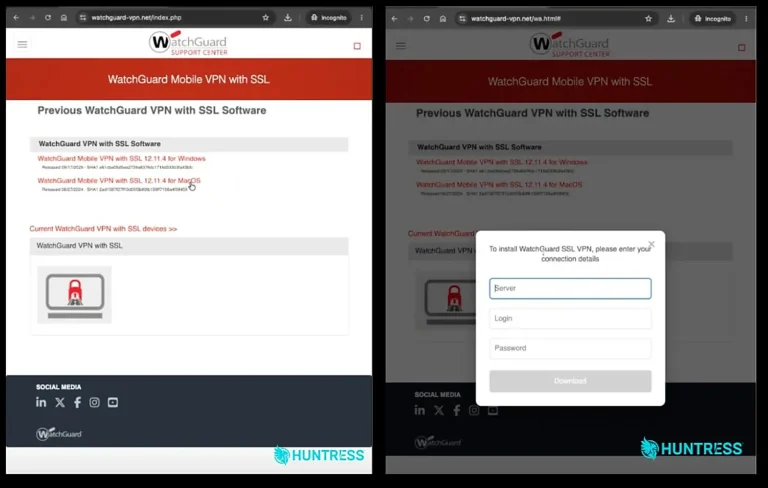
At a Glance Malware / Campaign Family Browser-based WatchGuard VPN phishing kit (popup.js credential harvester; no endpoint...
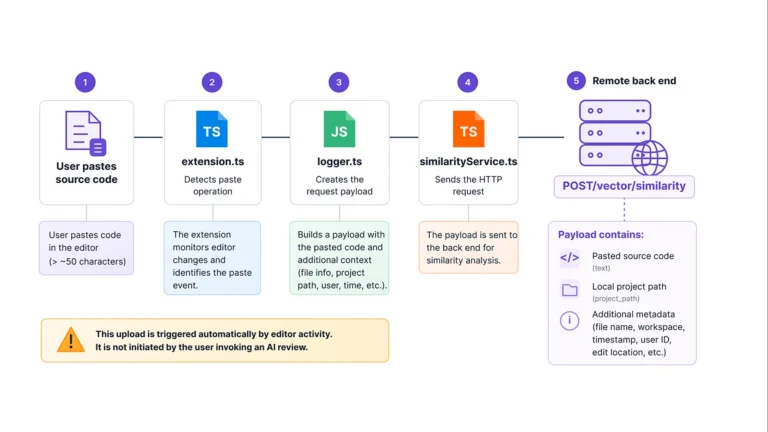
At a Glance Malware / Tool Family CodeAudit AI extension (intrusive IDE telemetry and data harvester) Threat...
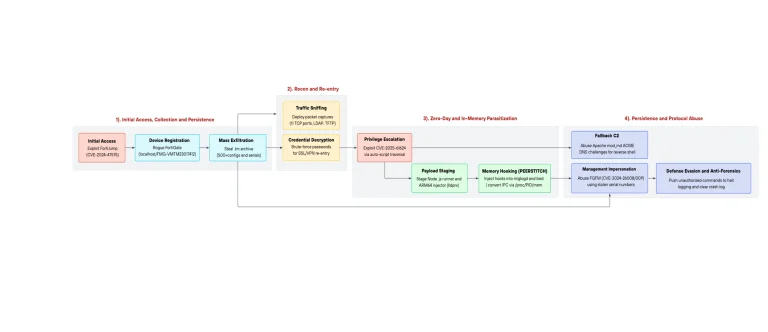
At a Glance Malware Family PEERSTITCH malware (64-bit Linux ARM64 in-memory process injector) Threat Actor Confirmed as...
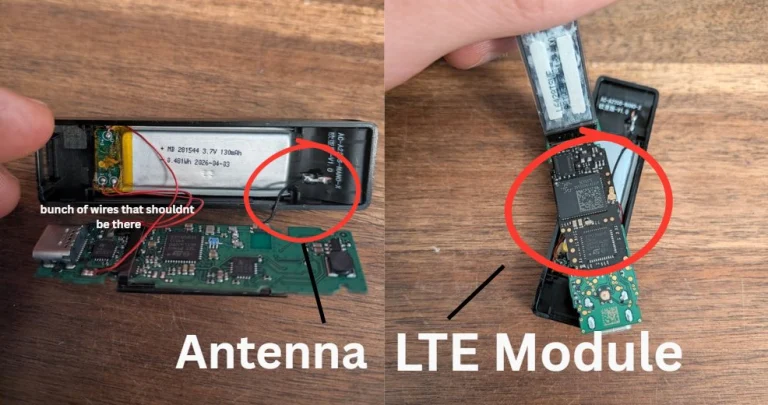
Investigators previously discovered that a Malaysian distributor for the French cryptocurrency hardware wallet manufacturer Ledger systematically tampered...
At a glance Malware family CloudSyncD (macOS) and a custom Windows information stealer Threat actor Unknown operators...
At a glance Malware family None new; public tools GodPotato and PrintSpoofer plus built-in Windows utilities Threat...
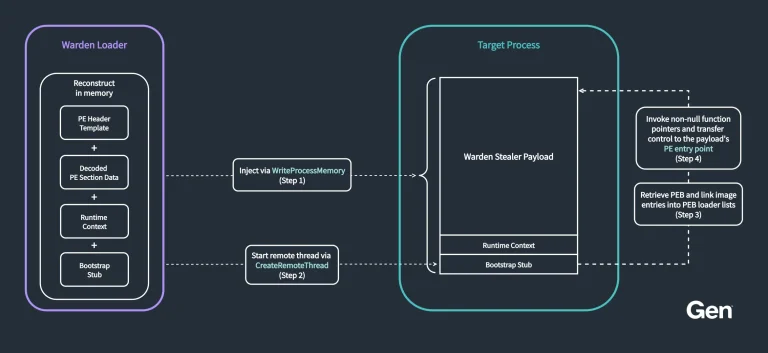
At a glance Malware family Warden Stealer (earlier tracked by Gen as CallbackBeaver) Threat actor Unnamed MaaS...
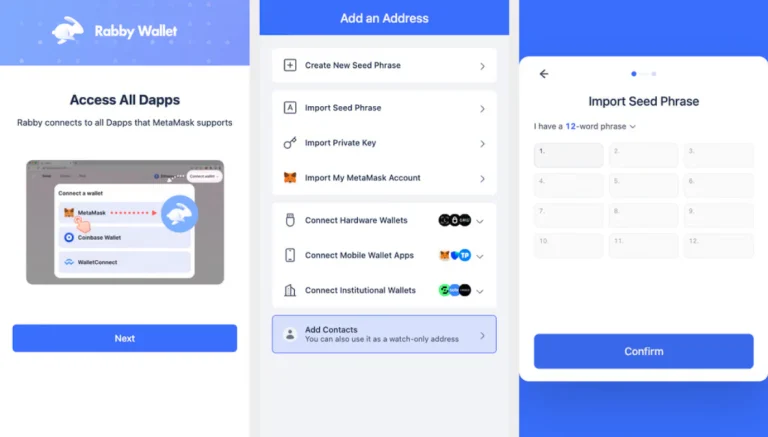
At a Glance Malware family Fake wallet extensions in two families: Rabby clones and OKX clones Threat...
The prominent cybersecurity firm Bitdefender recently published a comprehensive report revealing a massive malware campaign dubbed Midnight...
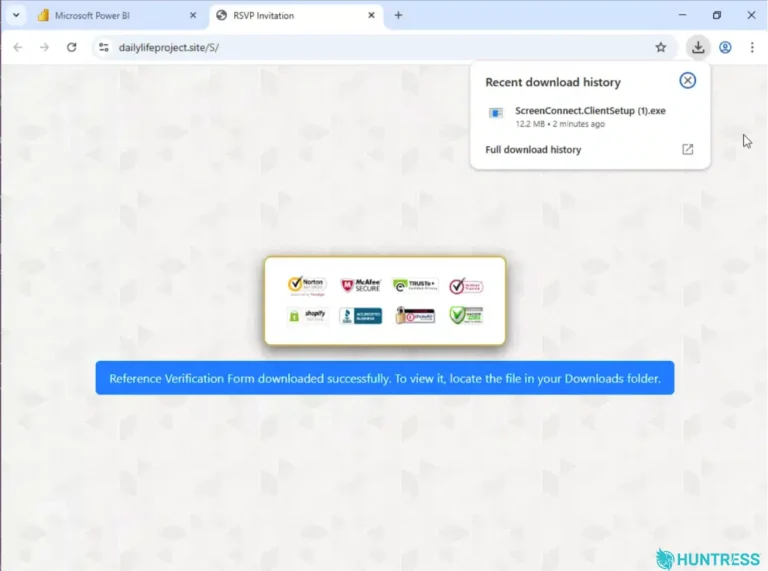
At a Glance Malware family Rogue ScreenConnect clients and a defense evasion tool Threat actor Unknown; no...
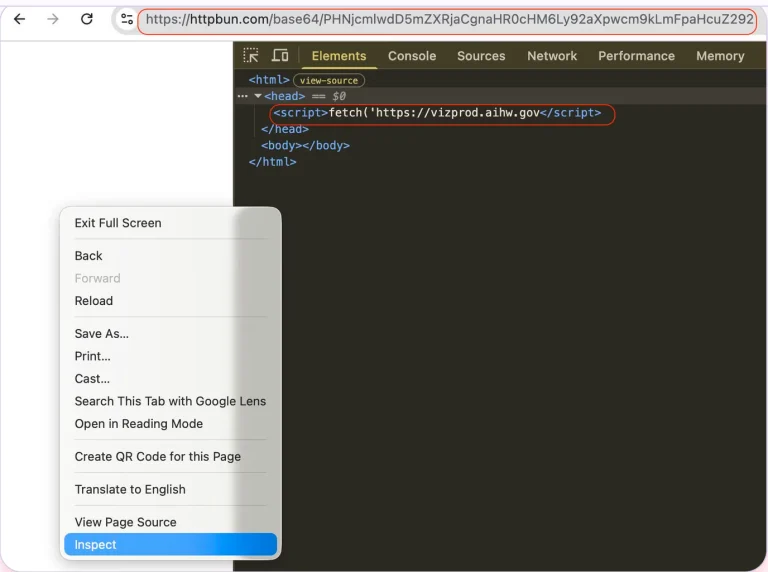
At a Glance Activity AI agents abusing a public URL scanner’s browsers to run JavaScript and evade...
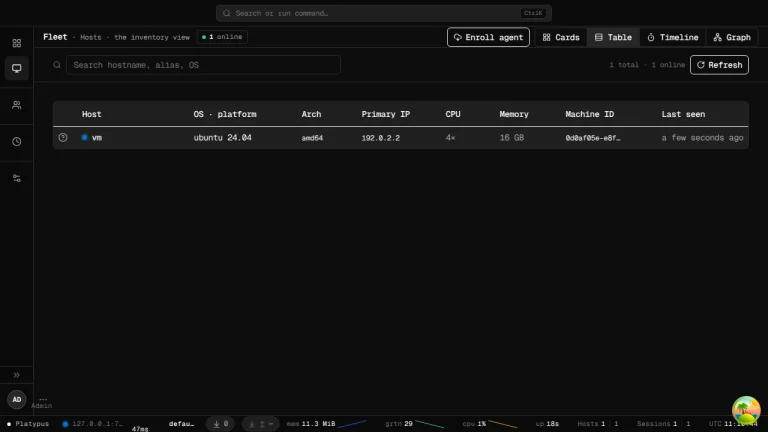
At a Glance Malware family PHP web shells, a Perl web shell installer, Platypus agents, and a...
At a Glance Malware family ClingSTUN, a Linux back-connect proxy backdoor Threat actor Unknown; no attribution Targets...
The Moroccan intelligence agency, DGST, allegedly employed not merely the Pegasus spyware, but an entire panopticon of...
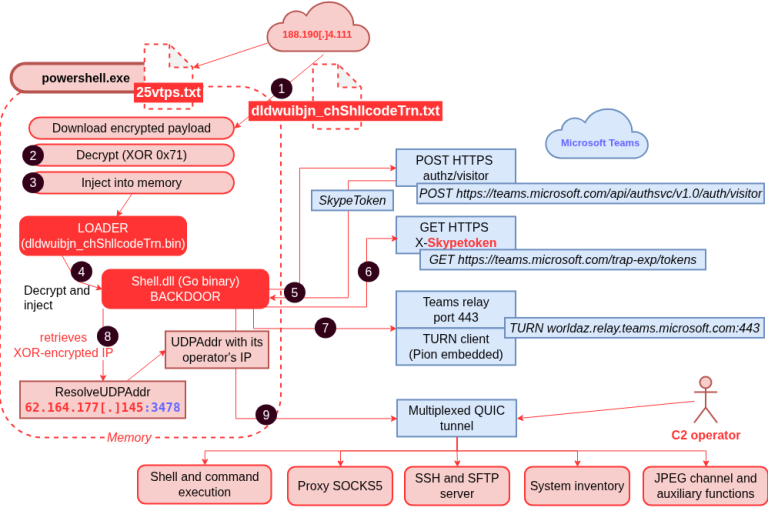
At a Glance Malware family Two backdoors: a Go-based in-memory implant and a persistent TURN/MQTT backdoor Threat...
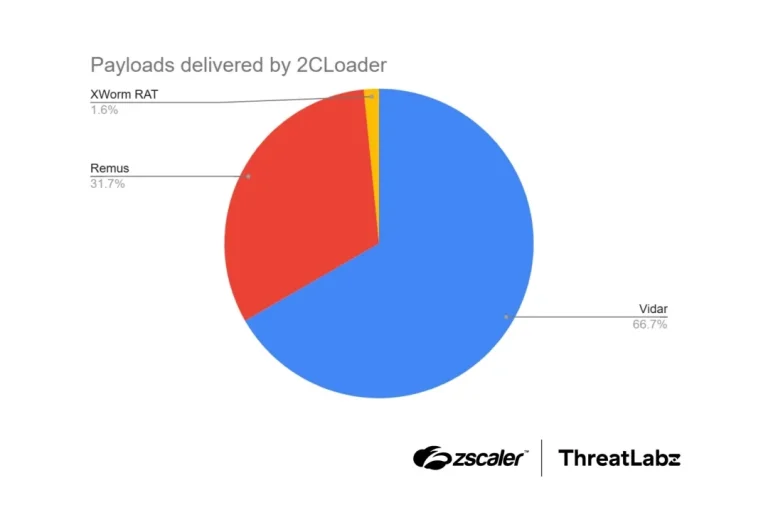
At a Glance Malware family 2CLoader (Windows loader) Threat actor Unknown; no attribution Targets Windows users; victim...
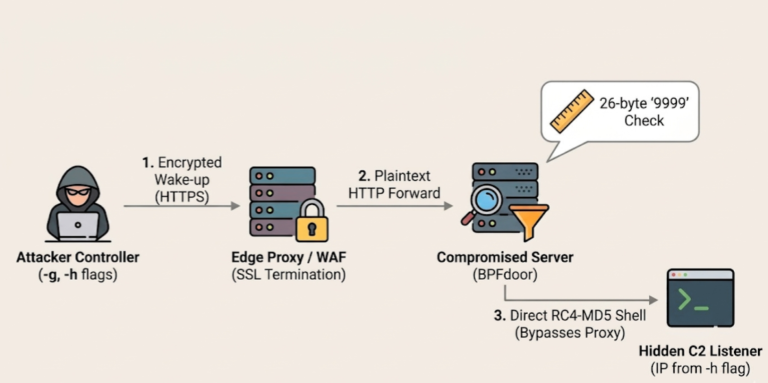
At a Glance Malware family BPFDoor variants, a BPF-enabled Rekoobe build, a dropper, and six AVERAT builds...
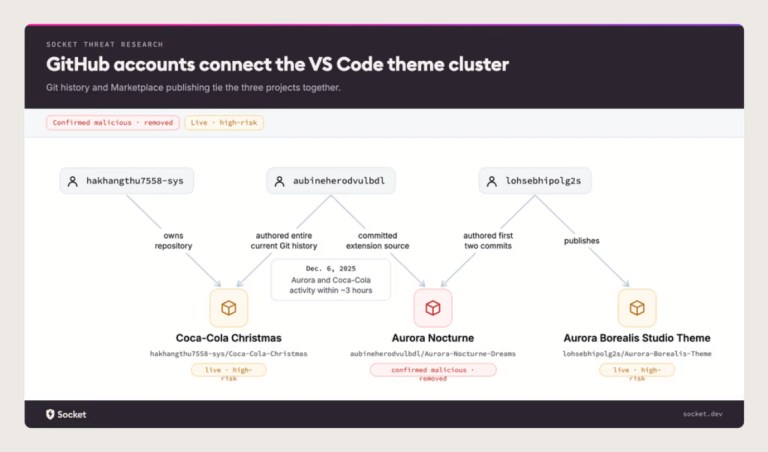
At a Glance Malware family GlassWorm loader; a separate Windows downloader Threat actor GlassWorm operators (high confidence...
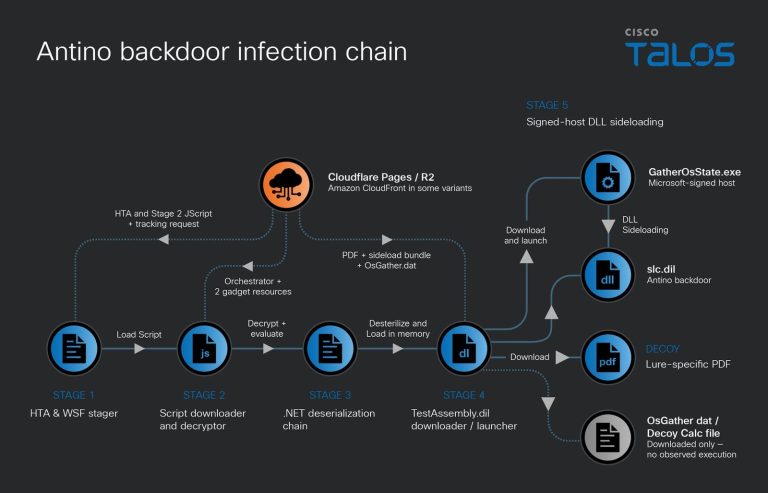
At a Glance Attribute Details Actor or Group UAT-11587 (suspected China-nexus group; overlaps with Jewelbug) Activity Type...
On August 31, 2026, attackers broke into a school’s print server and ended up owning its entire...