 Do Son
A FreeSWITCH vulnerability in api-chat enables remote code execution and is exploited in the wild. Upgrade to 1.11.3 now to stay safe.
Vulnerability
A Linux kernel vulnerability (CVE-2024-26582) has a public PoC that turns a TLS use-after-free into a root shell. Details and exploit are out.
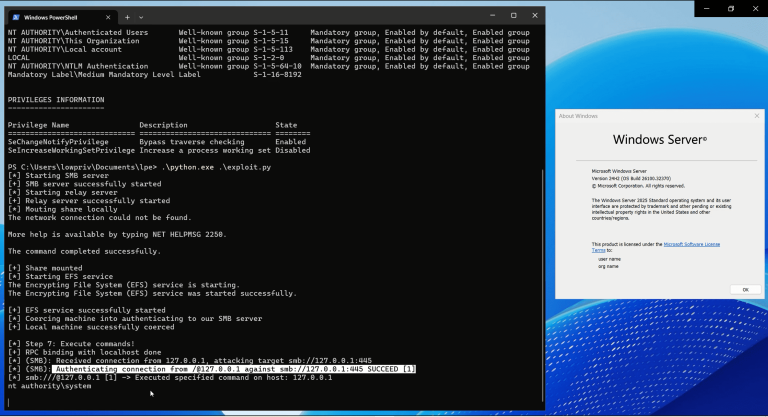
Synacktiv publicly disclosed an NTLM reflection bypass, CVE-2026-24294, with PoC exploit code. It gives SYSTEM on Windows Server 2025. Patch now.
Public details disclose an out-of-bounds read flaw (CVE-2026-43495) in the Linux kernel. This MediaTek t7xx WWAN flaw requires immediate patching.
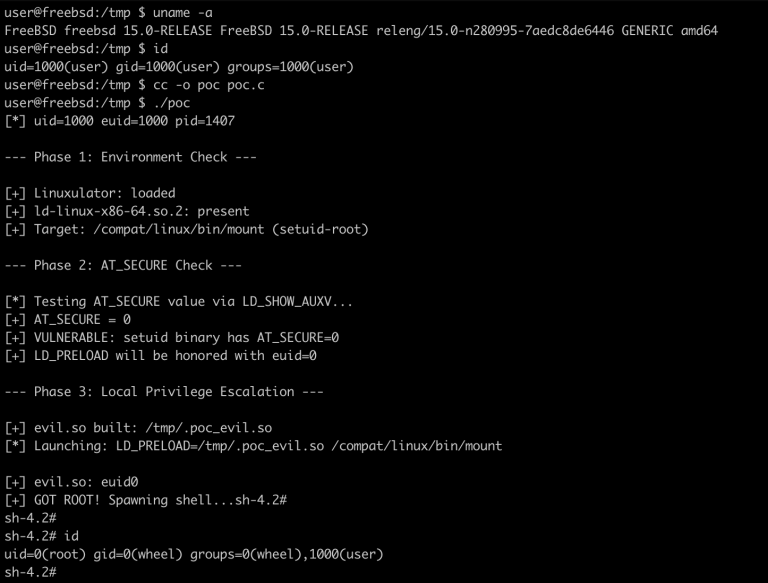
A FreeBSD privilege escalation flaw (CVE-2026-49413) in the Linuxulator lets local users get root. Public PoC exploit code makes patching urgent.

Full technical details and functional PoC code for the Redis DarkReplica exploit are out. Read our breakdown of this CVE-2026-23631 public disclosure.
New Mautic security vulnerabilities expose servers to takeover. Install the latest patches to fix these critical RCE flaws immediately.
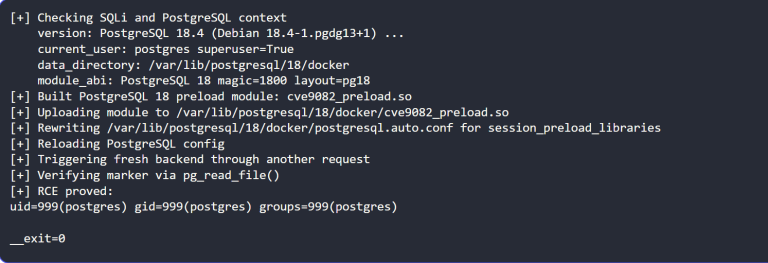
A critical Drupal SQL injection exploit is active in the wild. Read the analysis of this flaw now that the wild exploit PoC is fully public.
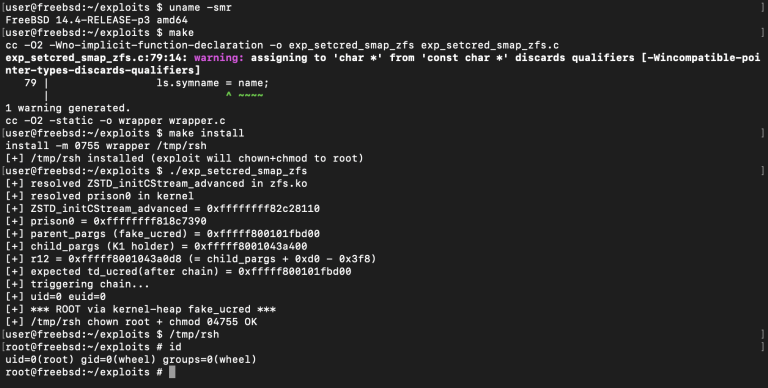
A critical FreeBSD kernel buffer overflow vulnerability is exposed. Learn more about this threat now that public exploit code released.
A critical Windows DNS Client RCE vulnerability (CVE-2026-41096) with a 9.8 CVSS has public PoC exploit code. Learn how to detect and patch it.
Fix the critical Dell Container Storage Modules vulnerability (CVE-2026-40710). Learn how hardcoded credentials expose systems and update now.

Technical details and a functional PoC exploit have been released for CVE-2026-41702, a VMware Fusion TOCTOU flaw granting instant root on macOS.

Technical details and a functional Python PoC exploit have been released for CVE-2026-4802, a critical Cockpit flaw giving low-privilege users root.

Urgent: Public PoC for Apache CVE-2026-23918. A critical double-free in mod_http2 enables unauthenticated DoS and RCE. Update to Apache 2.4.67 immediately.

Apache Tomcat RCE alert: CVE-2026-34486 exploit code and details are now public. A "fail-open" flaw enables RCE via Tribes clustering. Update immediately.
A public PoC has been disclosed for an Adobe Acrobat prototype pollution chain (CVE-2026-34621) actively exploited in the wild. Patch your systems today!
Full Exploit Disclosed: Public PoC and Technical Details Released for Critical ProFTPD SQL Injection
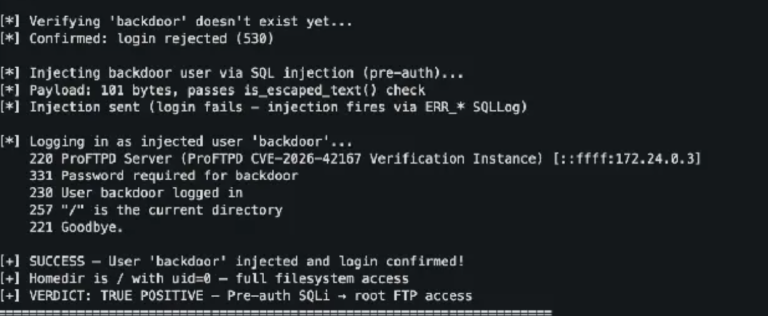
Full Exploit Disclosed: Public PoC and Technical Details Released for Critical ProFTPD SQL Injection
Critical SQLi in ProFTPD's mod_sql allows unauthenticated admin account injection. Full PoC code is public. Upgrade to v1.3.9a to secure your servers.
Technical details and PoC for Rclone’s critical 9.2 CVSS vulnerabilities (CVE-2026-41176/41179) are now public. Patch to version 1.73.5 to prevent RCE.
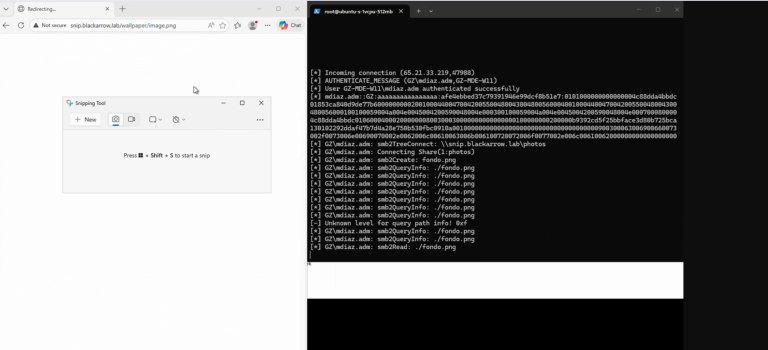
Detailed PoC and exploit code for CVE-2026-33829 are now public. See how the Windows Snipping Tool can leak NTLM hashes and how to patch the flaw.

Critical 9.1 CVSS flaw in Horner Automation PLCs allows unauthenticated brute force attacks. Secure your industrial systems—patch XL4, XL7, and Cscape now!

Use-after-free flaw in Rsync versions 3.0.1–3.4.1 allows DoS and info leaks via malicious xattr traffic. Learn how a simple qsort fix secures your syncs.

Python patches a critical 9.1 UAF flaw in decompressors and a browser command injection bypass. Protect your infrastructure—audit your CPython code today!