
 Do Son
Apache NiFi 2.9.0 fixes a high-severity RCE (CVE-2026-39816) in the Tinkerpop service. Secure your data pipelines and verify your annotations today!
Vulnerability

Sonatype patches a critical 9.4 CVSS RCE in Nexus Repository 3 (CVE-2026-3199). Secure your supply chain—upgrade to version 3.91.0 immediately!

Mitel patches a critical 9.8 CVSS SQL injection in MiCollab. Learn how this unauthenticated flaw chains to full system takeover. Upgrade to v10.2 SP1 now!

OpenStack Keystone CVE-2026-33551 allows low-privilege users to bypass role restrictions and seize full S3 bucket control. Patch your cloud environment now!
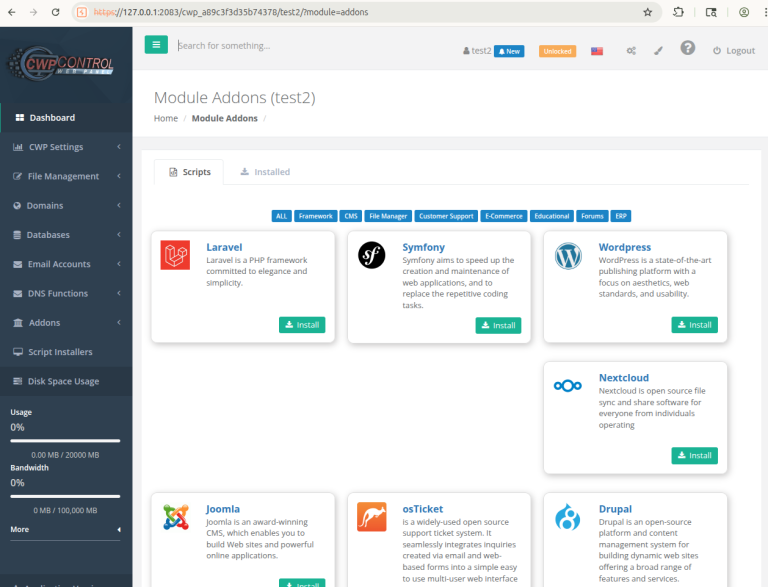
Fenrisk releases full PoC exploit for CVE-2025-48703, a critical CWP RCE flaw. Learn how unauthenticated attackers hijack non-root users. Patch now!

PolyShell Exposed: Public PoC and active exploitation disclosed for critical Magento RCE. With no official patch, your storefront is at risk. Secure it now!

Full disclosure: Technical details and a GitHub PoC for CVE-2025-39946 are live. This Linux TLS vulnerability allows root escalation via memory shaping.
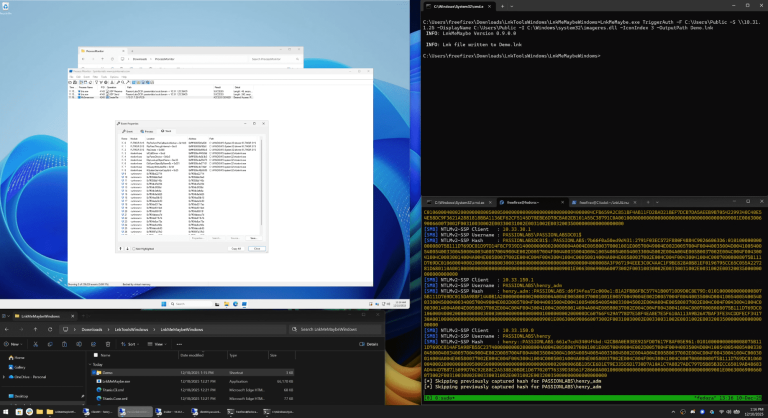
PoC exploit code is now public for CVE-2026-25185. Discover how a complex vulnerability in Windows .lnk shortcuts can be weaponized to leak network data.

Craft CMS patches CVE-2026-32267, a critical 7.7 CVSS flaw where a simple Live Preview token grants low-privilege users full admin access. Update today.
A critical Sudo vulnerability in the exec_mailer function allows local attackers to bypass security restrictions and escalate privileges to root access.
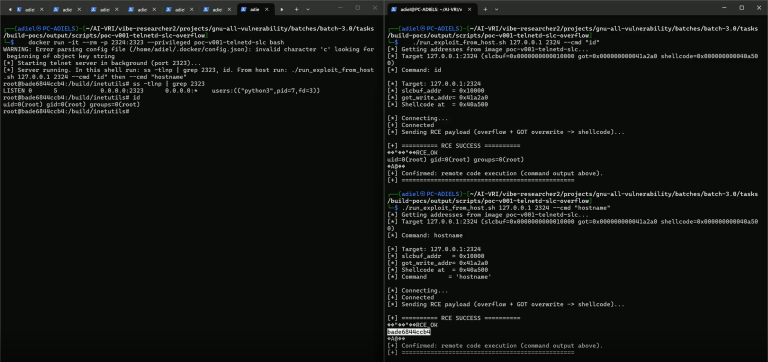
A critical 9.8 CVSS pre-auth buffer overflow in GNU Inetutils telnetd allows attackers to execute arbitrary code and gain root access. Patch immediately.

Apache IoTDB issues an urgent fix for a critical JEXL injection flaw (CVE-2026-24713) and insecure defaults. Upgrade to 1.3.7 or 2.0.7 to secure your IIoT data.

Centreon issues urgent patches for a 9.9 CVSS path traversal and a 9.1 RCE vulnerability in CLAPI. Secure your monitoring infrastructure—update now!
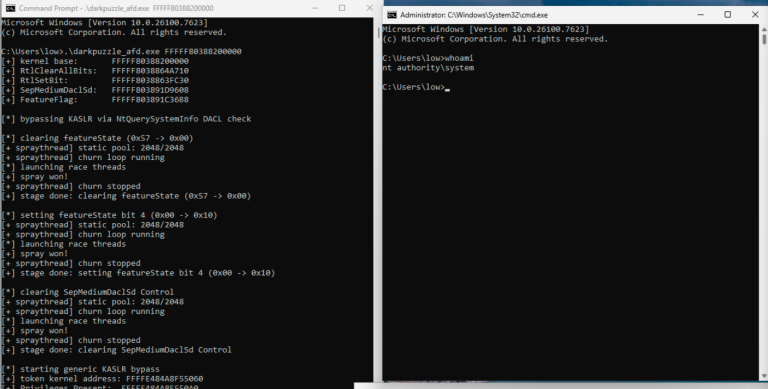
Windows kernel vulnerability CVE-2026-21241 (afd.sys) exposed! A new PoC exploit shows how local attackers can win a race condition to gain SYSTEM privileges.

IceWarp urges immediate patching for critical flaws allowing unauthorized server access, XSS, and arbitrary file reading. Update your instances today.

A critical Windows Error Reporting flaw (CVE-2026-20817) allows local privilege escalation to SYSTEM. With the PoC publicly disclosed, update immediately.

HAProxy patches high-severity QUIC flaws CVE-2026-26080 & 26081. Remote attackers can crash servers via malformed packets. Update to v3.0.16 now.

MongoDB patches high-severity flaw CVE-2026-25611. Unauthenticated attackers can crash servers via memory exhaustion. Update to v8.2.4 or v8.0.18 now.

Public PoC released for Windows Storage flaw CVE-2026-21508. Attackers can gain SYSTEM privileges via WUDFHost.exe. Patch Windows 11 immediately.
Acronis fixes 3 critical flaws (CVSS 10.0) in Cyber Protect. Attackers can manipulate backups without auth. Update to v16 Update 4 immediately.

Critical Lexmark printer flaws CVE-2025-65078 (CVSS 9.3) & CVE-2025-65077 allow remote code execution. Update firmware immediately to protect your network.