 Do Son
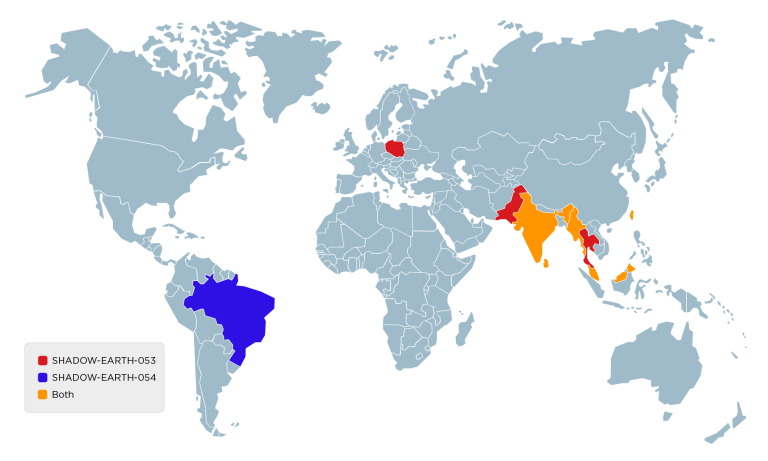
SHADOW-EARTH-053 is breaching governments and NATO using old ProxyLogon flaws and ShadowPad. Learn how this China-aligned group stays hidden via registry loading.
Cyber Security
Citizen Lab reveals "Tall Tales," a PRC campaign using GLITTER CARP and SEQUIN CARP to hunt activists and ICIJ journalists via private contractors.

Harvester APT expands to Linux using Microsoft Graph API for C2. Learn how the "GoGra" variant uses Outlook and "Zomato Pizza" lures to evade detection.
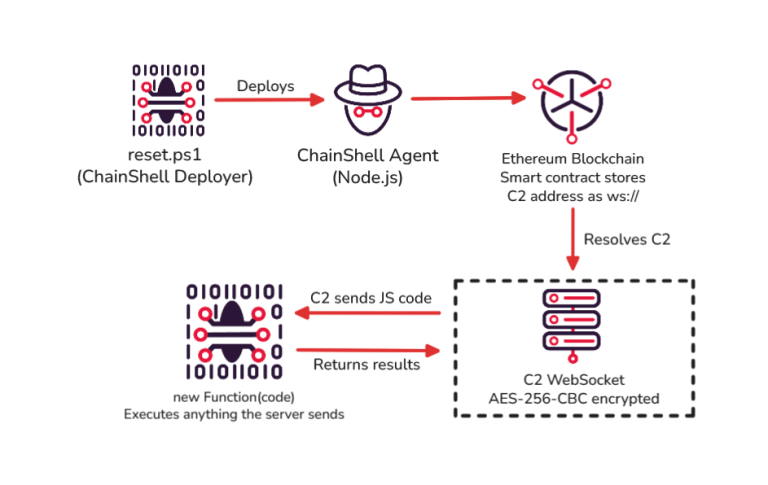
Iranian state actor Muddy Water adopts CastleRAT and ChainShell to hijack browsers and bypass MFA invisibly. A professional-grade shift in APT strategy.

DomainTools exposes North Korea’s "mature portfolio model": a compartmentalized cyber strategy designed for mission specialization and attribution resistance.
FBI and CISA warn of Iranian APTs hijacking internet-facing PLCs to disrupt U.S. energy and water systems. Learn the 2026 TTPs and how to defend your OT.
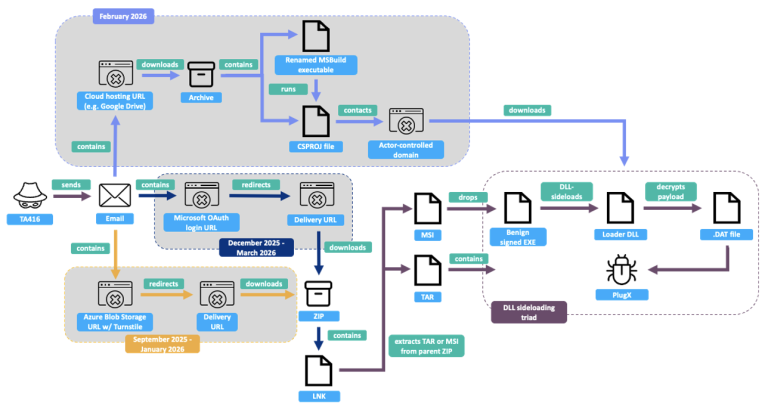
Proofpoint uncovers TA416's pivot to EU, NATO, and Middle East diplomacy. Learn how this state-linked actor uses updated PlugX and Cloudflare lures in 2026.

Check Point Research uncovers an Iran-linked password spraying campaign targeting M365 to support kinetic missile strikes and damage assessment in the ME.
The Triple-Headed Dragon: Inside the Three-Cluster Chinese Cyberespionage Campaign Targeting SE Asia

The Triple-Headed Dragon: Inside the Three-Cluster Chinese Cyberespionage Campaign Targeting SE Asia
Unit 42 uncovers a massive 3-cluster cyberespionage campaign by China-aligned actors in SE Asia using USBFect, Hypnosis loaders, and stealthy RATs.

Pawn Storm (APT28) debuts the PRISMEX suite, weaponizing Office zero-days against NATO logistics. Discover the stealth tactics behind this 2026 offensive.
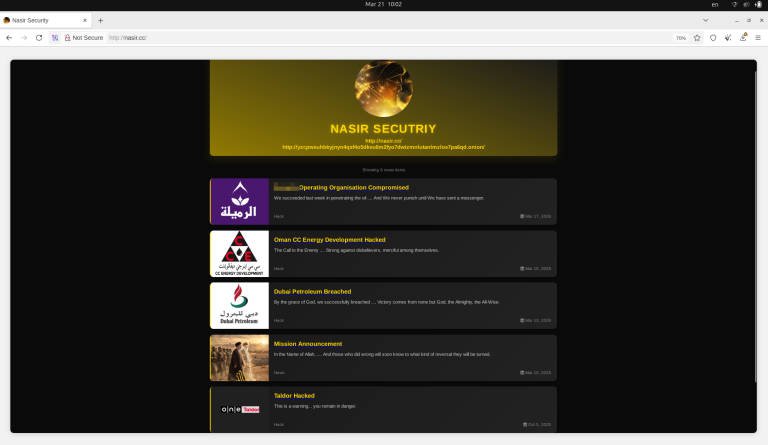
Resecurity uncovers Nasir Security, an Iranian threat actor using supply chain attacks and psy-ops to target Middle East energy vendors and leak blueprints.
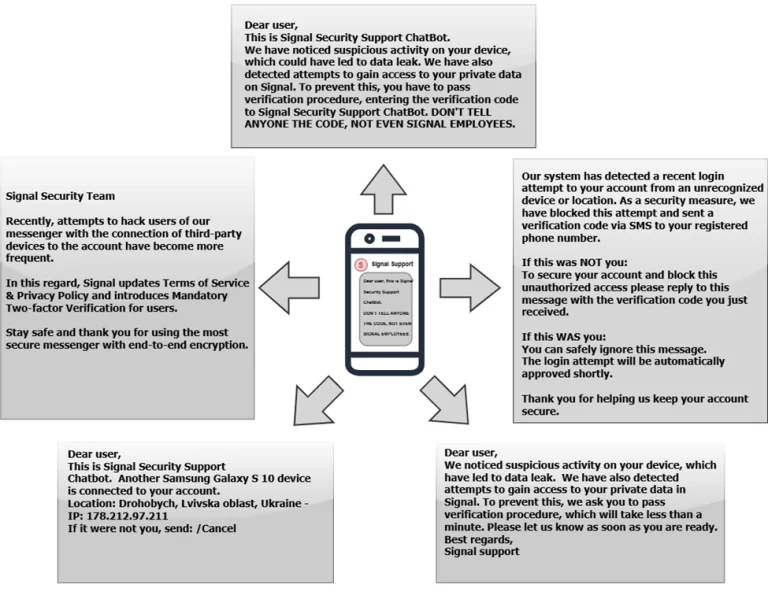
The FBI and CISA warn that Russian Intelligence is using sophisticated phishing to hijack Signal and other messaging apps via linked device features.
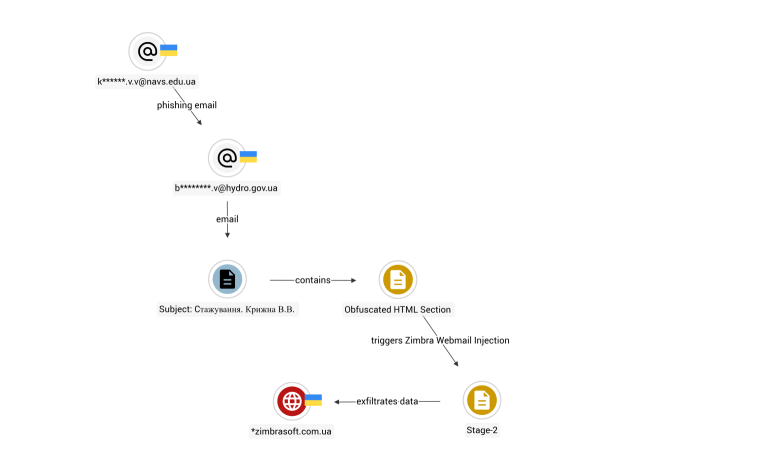
Seqrite Labs uncovers Operation GhostMail, an APT28-linked campaign using a zero-click XSS flaw in Zimbra to silently hijack Ukrainian government webmail.
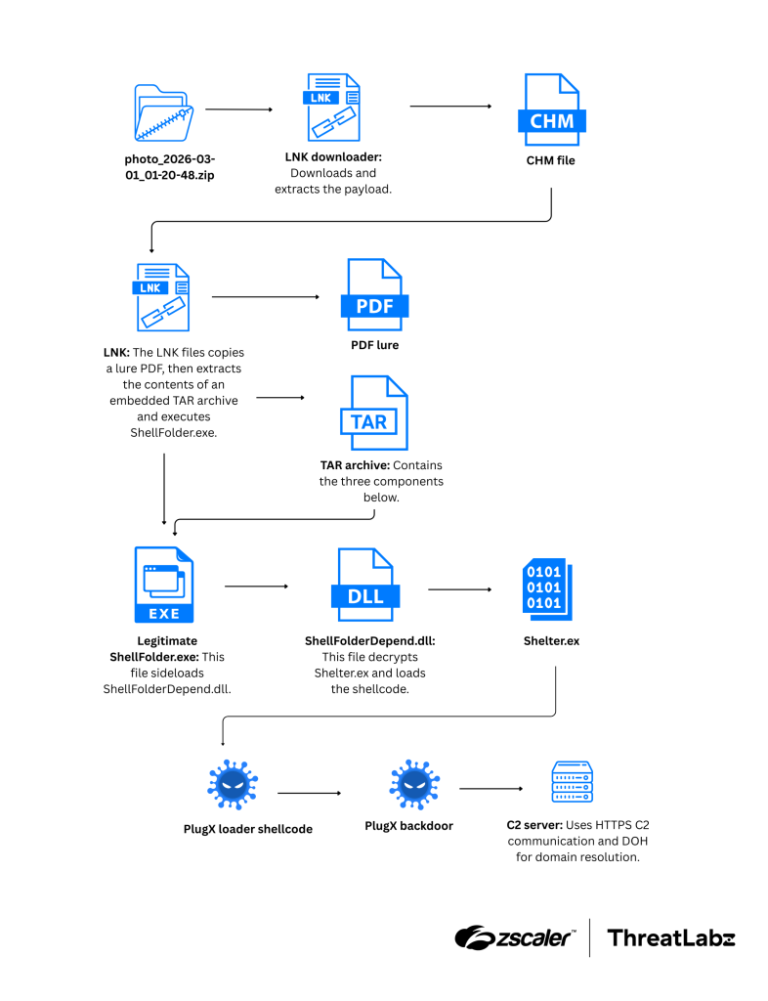
ThreatLabz reveals how China-nexus actor Mustang Panda weaponized Middle East conflict lures to deploy a stealthy PlugX backdoor within 24 hours.
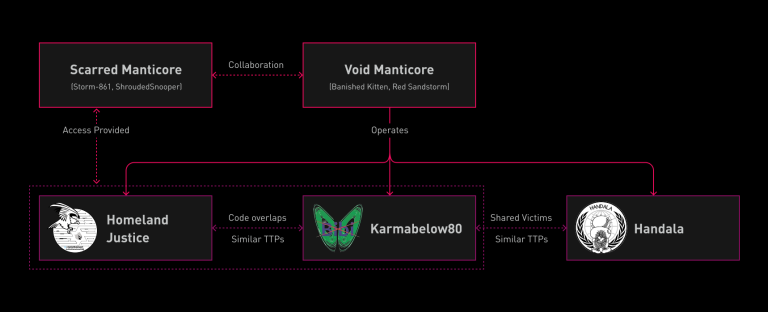
Check Point Research unmasks Handala Hack (Void Manticore), an Iranian MOIS threat actor using AI scripts and NetBird for destructive wiping attacks.
Unit 42 exposes CL-STA-1087, a suspected Chinese state-sponsored cyber espionage group using custom backdoors to infiltrate Asian military networks.
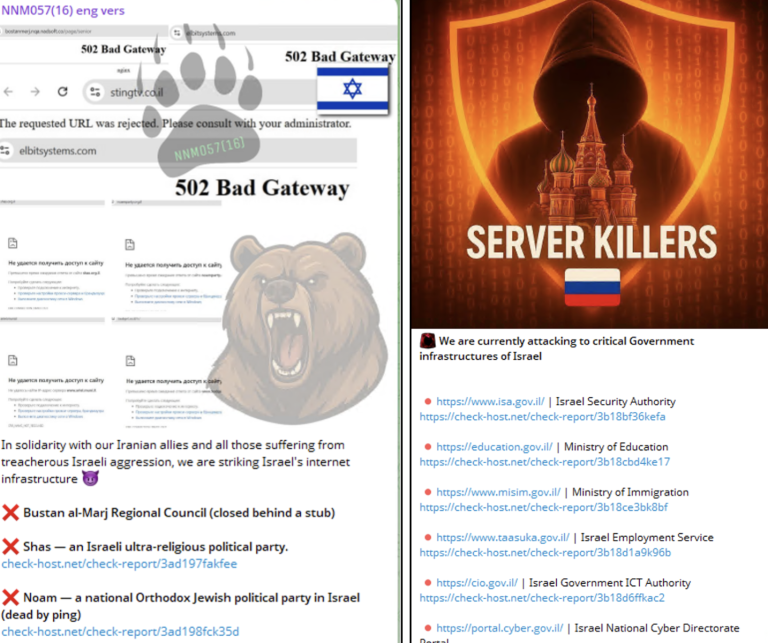
Rapid7 reveals a surge in state-directed cyber espionage and noisy hacktivism. Learn how actors like MuddyWater exploit critical CVEs to breach networks.
Proofpoint reveals Iran-aligned TA453 is exploiting Operation Epic Fury to launch targeted credential phishing campaigns against U.S. think tanks.

Chinese APTs like Camaro Dragon are targeting Qatar with PlugX malware and Cobalt Strike, weaponizing Middle East tensions for cyberespionage.

Cisco Talos exposes UAT-9244, a China-linked APT targeting South American telecoms with stealthy malware like the BitTorrent-based PeerTime and TernDoor.

Iranian APT Seedworm intensifies cyberespionage against US and Israeli networks using a new stealth backdoor called Dindoor. Read the full threat report.
Zscaler ThreatLabz uncovers Dust Specter, an Iran-linked cyber campaign hijacking Iraqi government infrastructure to deploy custom AI-assisted malware.