
 Do Son
A new Check Point Research report reveals how Iranian-nexus threat actors compromise IP cameras in the Middle East for real-time missile reconnaissance.
Cyber Security
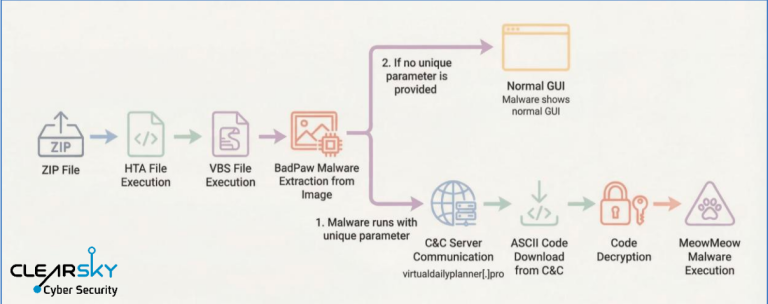
ClearSky uncovers a Russian campaign targeting Ukraine with BadPaw and MeowMeow malware, using steganography and feline decoys for stealthy espionage.

Check Point Research uncovers Silver Dragon, an APT41-linked group using the GearDoor backdoor and Google Drive for stealthy cyber espionage.

CYFIRMA reveals a new cyber espionage campaign by Transparent Tribe (APT36) targeting Indian defense with stealthy multi-stage malware and decoy PDFs.

A new Data Abyss report reveals how PRC-affiliated entities systematically exploited U.S. IARPA research to advance China's military capabilities.

Sophos X-Ops CTU warns of a surge in Iranian hacktivist cyber retaliation, including DDoS and targeted doxxing, following Operation Epic Fury.
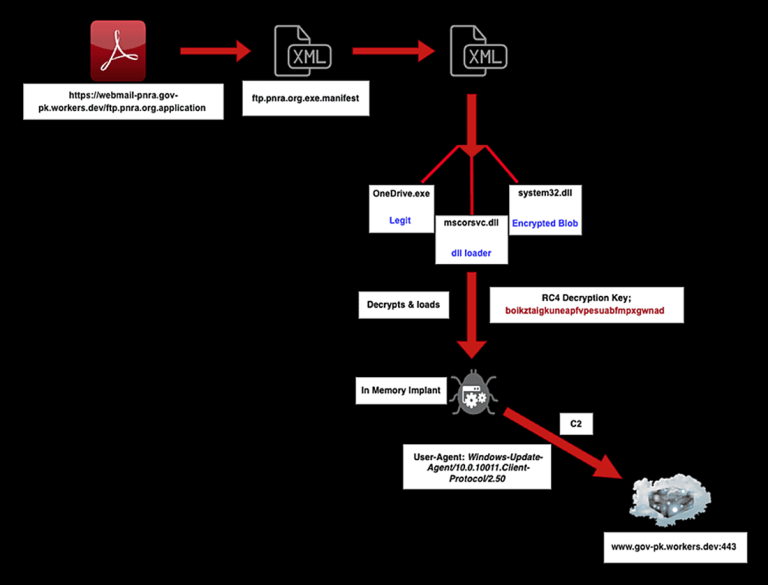
Arctic Wolf details a year-long cyber espionage campaign by Sloppy Lemming, deploying the custom BurrowShell malware against Pakistan and Bangladesh.

Unit 42 details the cyber fallout of Operation Epic Fury. Despite internet blackouts, autonomous hacktivists claim breaches of Israeli defense networks.
Recorded Future’s Insikt Group warns of a two-year escalation in Russian hybrid warfare. From cyber sabotage to airspace incursions, NATO faces a new doctrine.

US Treasury sanctions Sergey Zelenyuk and Operation Zero for brokering stolen government exploits and selling zero-days to foreign intelligence agencies.
Genians report reveals MuddyWater APT's shift to Rust-based malware and RMM tool abuse for long-term espionage across government and critical infrastructure.

Group-IB exposes Operation Olalampo: MuddyWater's new MENA campaign using AI-assisted Rust malware (CHAR) and Telegram bots for stealthy C2 communication.

Acronis uncovers CRESCENTHARVEST, a new spyware targeting Iranian dissidents. Attackers use protest lures & Google DLL sideloading to steal data.

Mandiant reveals UNC6201 exploiting Dell RecoverPoint zero-day CVE-2026-22769. Attackers use "Ghost NICs" & GRIMBOLT malware. Patch now.
APT28's "Operation MacroMaze" targets Europe using Spanish gov decoys. The campaign uses "low-tech" macros & Webhook.site to evade detection.
Lotus Blossom hijacked Notepad++ updates to target admins. The supply chain attack deployed Chrysalis backdoor. Update to v8.9.1 immediately.

Lazarus Group targets crypto developers with fake job offers in new "Graphalgo" campaign. Malicious npm packages deliver multi-stage malware. Stay alert.
GTIG report: Defense Industrial Base faces "constant siege" from Russian drone hackers & North Korean IT insiders. Learn the new threats.
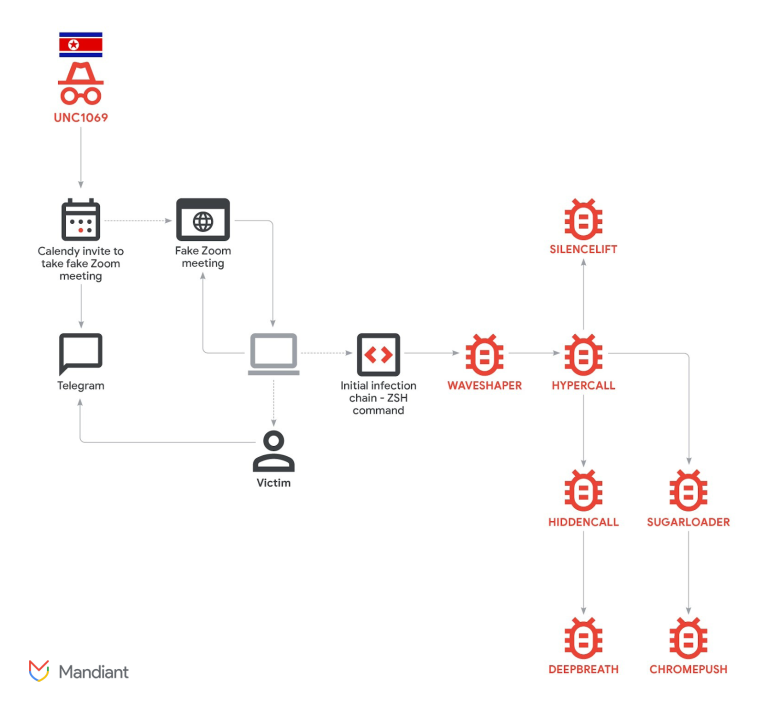
North Korean hackers (UNC1069) use AI deepfakes & "ClickFix" tactics to deploy SILENCELIFT malware. Learn how they target crypto firms via Zoom.

Cisco Talos exposes DKnife, a router malware that inspects traffic and swaps legitimate downloads for ShadowPad backdoors. Active since 2019.

TGR-STA-1030 (UNC6619) hits 70+ orgs in 37 countries. The Asia-based group uses the new ShadowGuard eBPF rootkit to hide in Linux kernels.
APT28 (Fancy Bear) weaponized CVE-2026-21509 in 24 hours to target NATO. New "BeardShell" and "NotDoor" malware steals emails. Patch Office now.