 Do Son
Critical Apache Tomcat authentication bypass (CVE-2026-133325) hits TLS 1.3 clusters. Read our Apache Tomcat authentication bypass 2026 fix guide.
Vulnerability
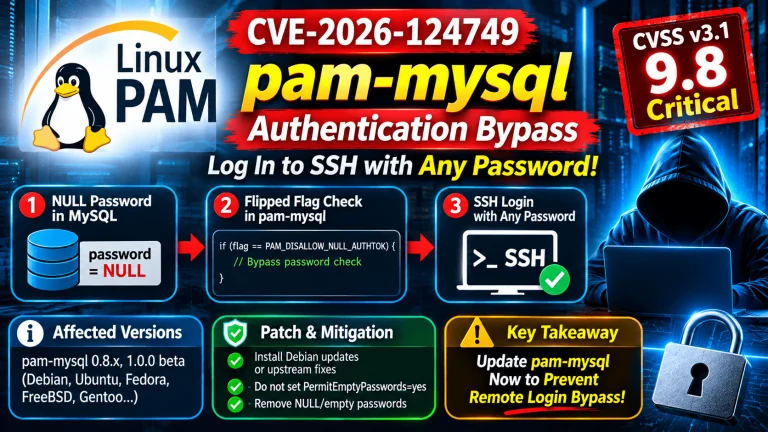
A critical pam-mysql authentication bypass (CVE-2026-124749) lets remote attackers log in via SSH. Read our pam-mysql authentication bypass 2026 guide.
GitLab patched the Ruby2Shell vulnerability (CVE-2026-132825) in 19.6.1. Read our Ruby2Shell vulnerability 19.6.1 report and upgrade now.
Okta security vulnerabilities November 2026 update fixes 8 Okta security vulnerabilities, including CVE-2026-130235, CVE-2026-130236, and CVE-2026-130151.
Spring security vulnerabilities November 2026 release patches 50 Spring security vulnerabilities, including CVSS 9.8 RCE CVE-2026-59273. Upgrade now.
IBM Guardium Data Protection 12.2.4 patches 14 flaws, including CVSS 9.8 bugs CVE-2026-84236 and CVE-2026-87977. Update IBM Guardium Data Protection now.
WatchGuard Dimension 2.3.2 fixes 15 WatchGuard Dimension vulnerabilities, including critical RCE CVE-2026-86130 and session hijack CVE-2026-86094.
Attackers actively exploit a Frappe authorization flaw in the wild. Read our report on Frappe authorization flaw and patch now.
Synology security advisories fix critical Synology DSM vulnerabilities CVE-2026-120382 and CVE-2026-123007 (NGINX2Root). Check affected versions and fixes.
Ubiquiti patched seven UniFi Access vulnerabilities in version 4.3.24. Read our UniFi Access vulnerabilities 2026 report on CVE-2026-132802 and more.
Splunk security updates November 2026 patch 146 flaws, including CVE-2026-131253, CVE-2026-76536, and CVE-2026-131202. Review affected versions and fixes.
Drupal core security update patches Drupal Remote Code Execution flaw CVE-2026-132165 and gadget chain CVE-2026-132166. Upgrade to 11.4.13 or 10.6.22 now.
CISA confirms active exploitation of CVE-2026-20320, a high-severity Cisco BroadWorks XXE flaw. Upgrade affected servers to RI.2026.07 now.
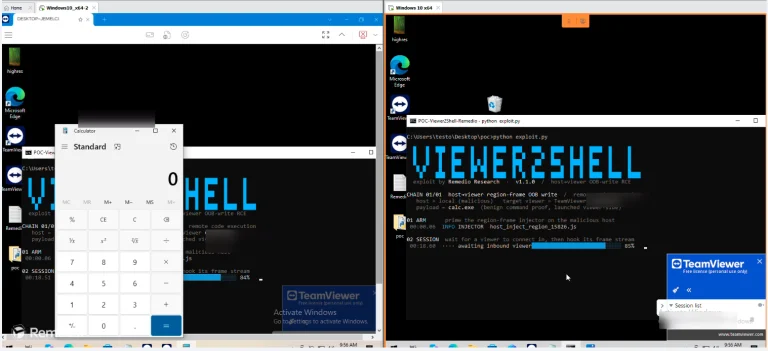
A high-severity TeamViewer client vulnerability allows compromised remote machines to trigger memory corruption and execute arbitrary code on admin devices.
A Bitcoin Core DoS vulnerability allows remote peers to trigger out-of-memory crashes on Windows, macOS, and BSD nodes via TCP socket handling errors.
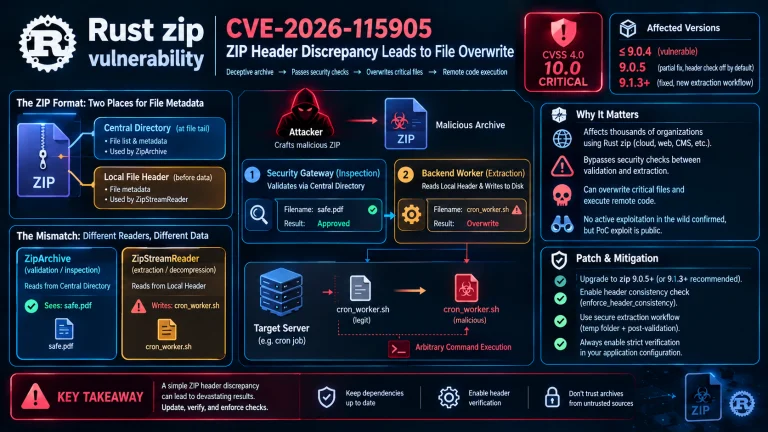
A critical Rust zip vulnerability CVE-2026-115905 allows attackers to bypass security gateways and overwrite server files using ZIP header discrepancies.
A severe Tailscale SSH vulnerability allows attackers on authorized nodes to exploit Unix socket forwarding and escalate privileges to root access.
An unpatched Electrum wallet vulnerability allowed malicious servers to manipulate RBF fee bumps, redirecting bitcoin payments to attacker addresses.
The cURL CVE-2026-92392 vulnerability enables remote code execution during HTTP/2 uploads. Update to cURL 8.23.0 or disable HTTP/2 to protect systems.
Discover the latest JetBrains software vulnerabilities, including TeamCity RCE bugs and Exposed SQLi flaws. Apply security patches immediately.
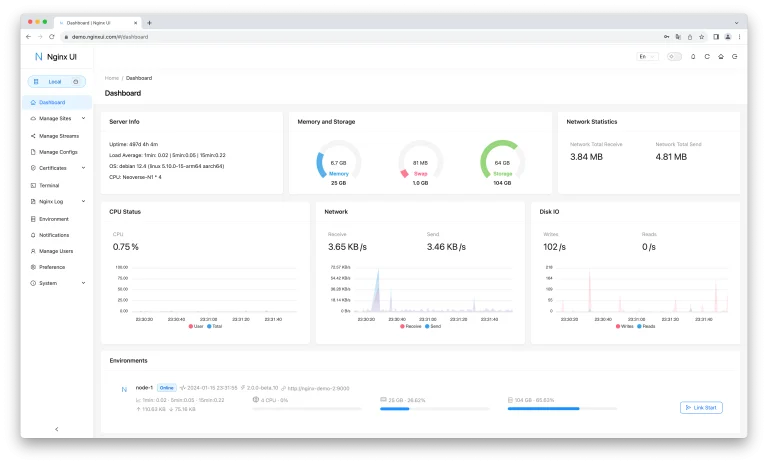
A critical Nginx UI RCE vulnerability (CVE-2026-107806) is publicly disclosed with PoC exploit code. Admins must patch now to prevent system takeover.
Discover how critical Apache Camel Karavan vulnerabilities (CVE-2026-103413 and CVE-2026-103412) allow code execution. Update to version 4.22.1 now.