 Do Son
A public exploit for CVE-2026-80521, an AF_UNIX use-after-free, enables Linux kernel privilege escalation. Fixed in 7.1.10, 6.12.111 and 7.2.
Do Son
Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.
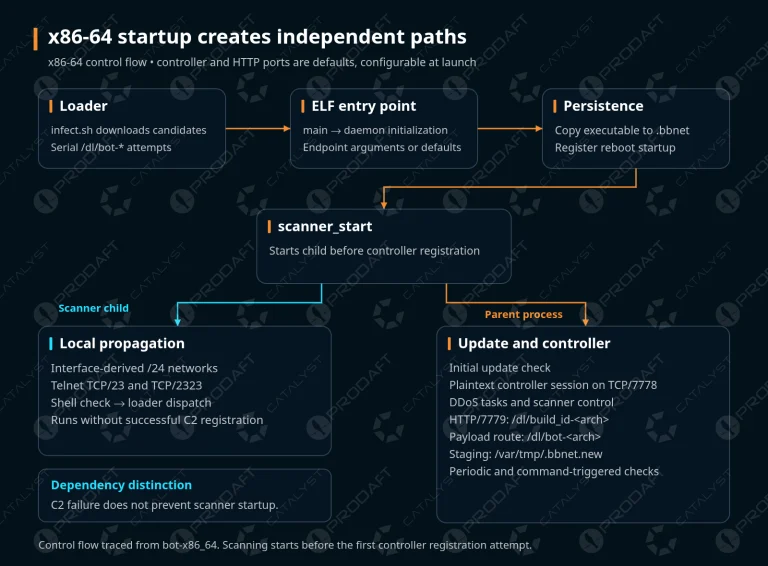
PRODAFT analyzes the BBNet Linux botnet across 13 ELF builds. See how the multi-architecture BBNet Linux botnet scans for React and Telnet flaws before C2.
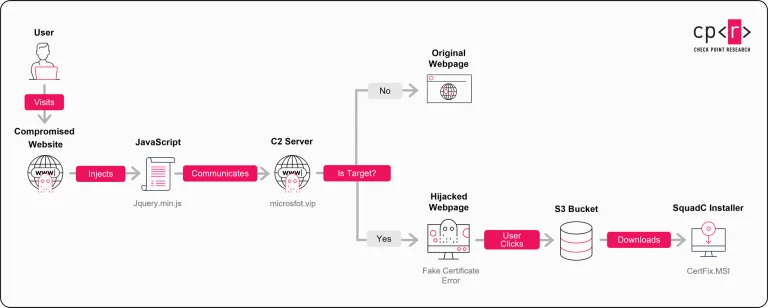
Check Point Research exposed the CopperDragon Sparrow framework malware ecosystem supplying China-nexus espionage clusters across three continents.
Indian CA eMudhra certificate revocation expands to eight RSA intermediate keys after a flawed Python migration script exposed private key material.
A massive Nitori data breach exposed up to 37.62 million personal and corporate customer records in Japan, raising severe impersonation scam risks.
Telegram fixes a Telegram Android RCE flaw after V12 showed remote code execution through a bot message. No CVE yet. Update the Android app now.
ConnectWise disabled five ScreenConnect extensions in 400 environments after attackers accessed ScreenConnect partner accounts. Act now.
Google Chrome security update 157.0.8103.78 fixes 83 flaws, including five Critical use-after-free bugs such as CVE-2026-126885. Update Chrome now.
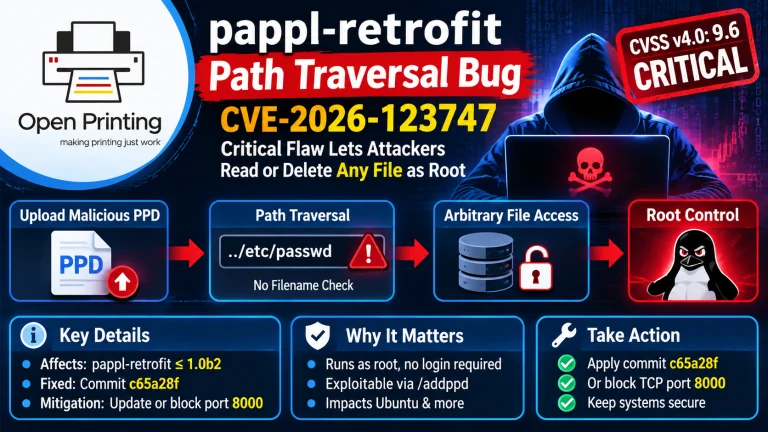
Full details and PoC exploit code for the critical pappl-retrofit path traversal flaw CVE-2026-123747 are now public. Apply commit c65a28f right away.
Zoho fixes eight ManageEngine vulnerabilities in DDI Central and ADAudit Plus, including Cisco router command injection and SQL injection flaws.
Go 1.27.4 and 1.26.11 deliver 12 Go security fixes, blocking cgo code execution at build time (CVE-2026-97033) and an HTTP/1 server crash.
Node.js fixes 17 bugs, including Node.js HTTP/2 vulnerabilities and a TLS heap leak (CVE-2026-123864). Update to 26.13.1, 24.22.3 or 22.23.5.
Update Apache HTTP Server to 2.4.71 now to fix CVE-2026-119618, a critical mod_http2 remote code execution flaw, alongside CVE-2026-106023.
The October Railway security incident exposed up to 100,000 workspaces in a targeted AI keys breach. Learn how the attack happened and what to do.
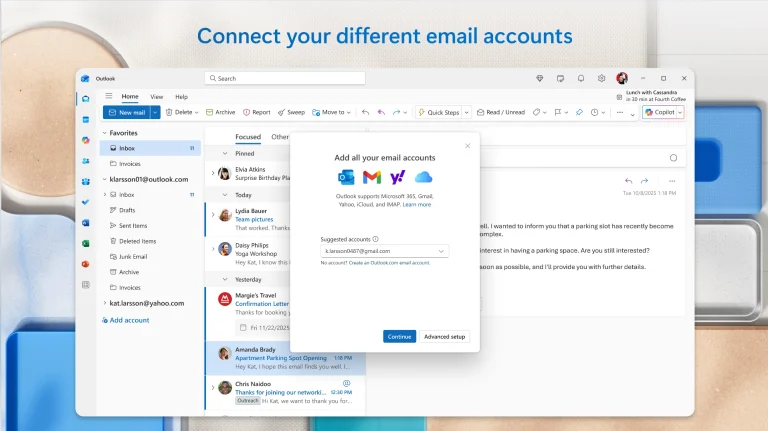
Microsoft is rolling out a classic Outlook interface update for Windows, introducing refreshed icons, spacing refinements, and What's New prompts.
N-able patches N-central vulnerabilities in 2026.4 HF2 as attackers scan with the public proof-of-concept exploit. Seven CVEs, up to CVSS 9.3.
Google Antigravity Knowledge Work interface launches, bringing AI agent productivity, data analysis, and document drafting to non-technical teams.
The unpatched worse_query iOS sandbox escape flaw allows malicious apps to bypass container restrictions and siphon crypto wallet data and photos.
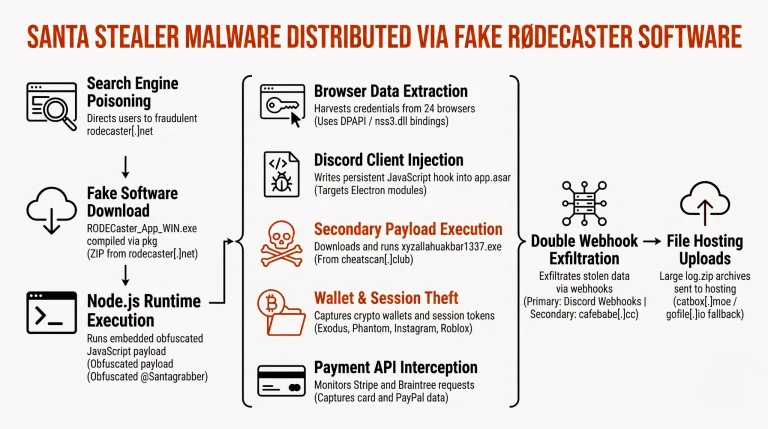
Unit 42 exposes Santa Stealer malware on a fake audio site. See how the RODECaster Santa Stealer malware loots 24 browsers, Discord, and crypto wallets.
A Claude Code email leak exposed user addresses in User-Agent headers, prompting Anthropic to issue privacy updates and command blocking.
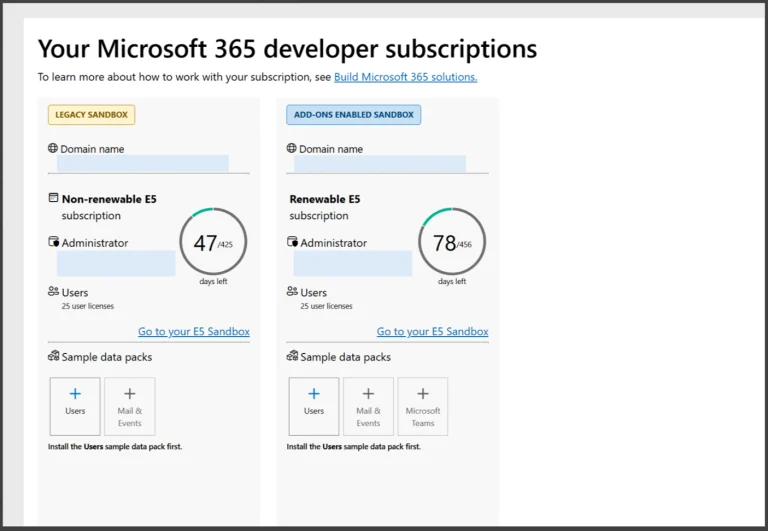
Microsoft is retiring legacy Microsoft 365 developer sandbox subscriptions, requiring manual tenant migration before permanent deletion.
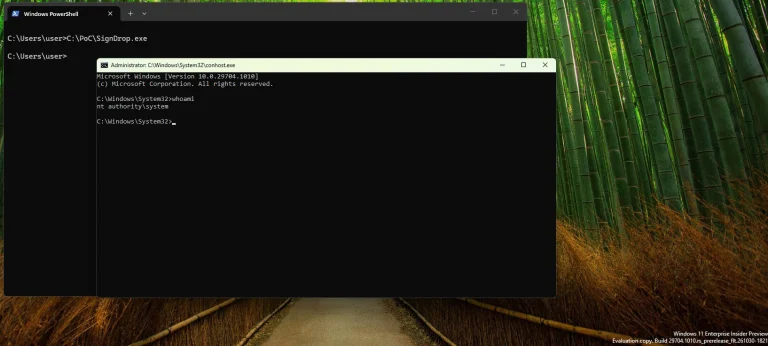
SignDrop, an unpatched Windows CLFS zero-day, now has a public proof-of-concept exploit that gives standard users SYSTEM privileges. No patch yet.