
 Do Son
Amaranth-Dragon (APT-41 nexus) weaponized WinRAR flaw CVE-2025-8088 in just 10 days. Southeast Asian govts targeted with malicious RAR archives.
Cyber Security

Lotus Blossom compromises Notepad++ infrastructure to deploy "Chrysalis" malware. Rapid7 reveals the group using Microsoft Warbird to evade detection.

BlueNoroff hackers use fake "audio issues" on Teams calls to trick macOS users. The "fix" runs terminal commands that steal Keychains. Watch out.

APT42 targets defense officials with "TAMECAT," a modular PowerShell backdoor. The malware uses social engineering and Telegram C2 to steal secrets.

CERT Polska reveals destructive attacks on energy infrastructure. "Static Tundra" used DynoWiper and LazyWiper to brick OT devices. Read more.

North Korea's LABYRINTH CHOLLIMA splits into 3 units: GOLDEN, PRESSURE, & Core. CrowdStrike reveals new strategy targeting crypto & defense.

APT28 launches "Operation Neusploit" targeting Europe. Hackers exploit CVE-2026-21509 to deploy MiniDoor malware via RTF files. Patch Office now.

"RedKitten" spies on Iranian protesters using AI-written malware. Attackers use fake death lists to deploy SloppyMIO surveillance tools.

Notepad++ confirms update infrastructure was compromised by state-sponsored actors targeting specific users. Update to version 8.8.9 immediately.

Cisco Talos warns of UAT-8099 targeting Asian IIS servers with region-locked BadIIS malware. New variants now attack Linux systems.
Pakistan-linked spies target India with "Sheet Attack," using Google Sheets for C2 and GenAI to build malware. Learn about SHEETCREEP and FIREPOWER.
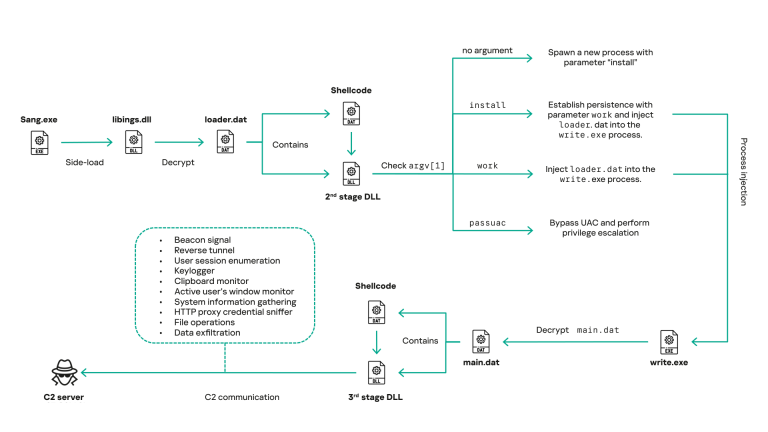
HoneyMyte (Mustang Panda) shifts to real-time surveillance using updated CoolClient. New 2025 campaign uses Pixeldrain for stealthy exfiltration.

New "Gopher Strike" & "Sheet Attack" campaigns hit Indian govt. Linked to Pakistan, attackers use GitHub C2 & GenAI malware to evade detection.

Trend Micro uncovers PeckBirdy, a JScript C&C framework used by China-aligned APTs. It uses lightweight, fileless tactics to target Asian governments.
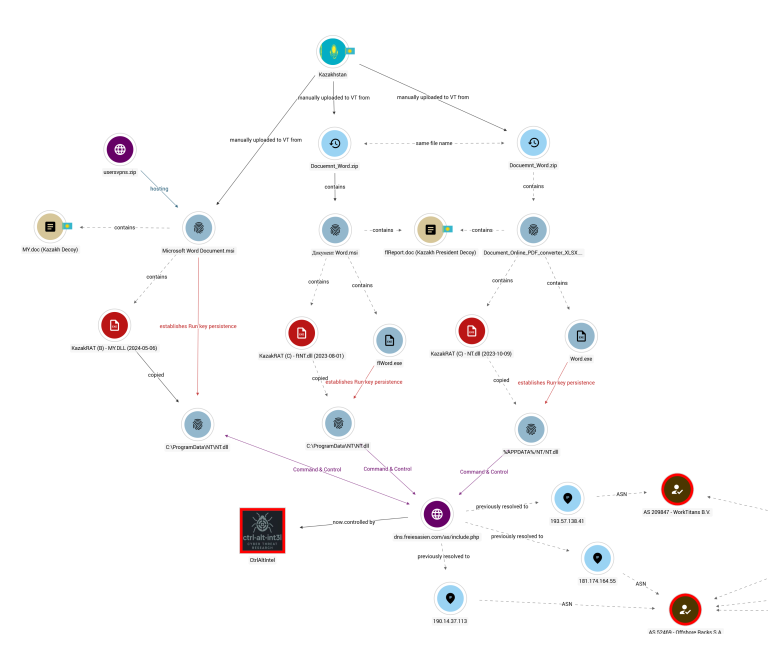
Researchers uncover "KazakRAT," a state-affiliated spyware targeting Kazakhstan & Afghanistan. A lapsed domain allowed experts to sinkhole the C2.

DPRK spies weaponize Visual Studio Code tunnels to bypass security. Darktrace reveals a campaign targeting South Korea with government decoys.

NCSC warns of Russian group NoName057(16) targeting UK sectors with DDoS attacks. Defenders must ensure scalability and plan for graceful degradation.

Nomad Leopard targets Afghan officials with fake ministry docs. SEQRITE reveals how the "afghanking777000" OPSEC fail exposed the spies.

Genians reveals "Operation Poseidon": Konni APT exploits Google & Naver ad redirects to bypass defenses and deploy EndRAT.

Mustang Panda targets US gov with new LOTUSLITE backdoor. Campaign uses Venezuela lures and DLL sideloading to evade detection.
Cisco Talos warns: China-linked UAT-8837 targets North American infrastructure using zero-days (CVE-2025-53690) & open-source tools.

MuddyWater APT deploys new "RustyWater" malware against Middle East targets. CloudSEK reveals how the group is ditching PowerShell for stealthy Rust tools.