 Do Son
Apple issued warnings across 99 nations as the Apple mercenary spyware threat targets investigative journalists with sophisticated surveillance tools.
News
Anthropic introduces Claude Message Threads to slash payload sizes from 800KB to 1.8KB and cut response latency by 35 percent across long chats.
TWCA announces emergency TWCA certificate revocation after researchers discovered non-compliant serial number entropy across ten intermediate CAs.
Ubuntu puts fixes for CVE-2026-98432, a Linux kernel TCP flaw rated CVSS 9.8, in the proposed pocket for 22.04 LTS and newer. Older releases wait.
The FBI attributed the $6.3 billion Binance crypto heist to North Korean state hackers, sparking denials from Pyongyang amid ongoing asset recovery efforts.
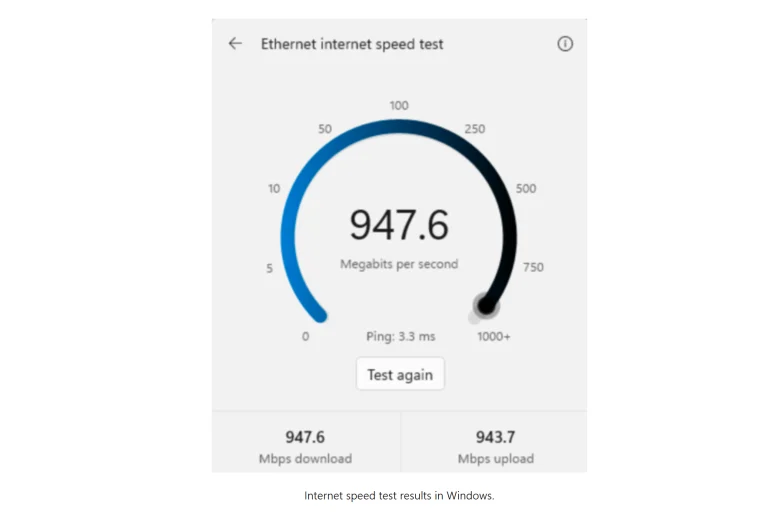
Microsoft introduces a native Windows 11 speed test tool developed with AI agents, measuring network latency, download rates, and upload performance.
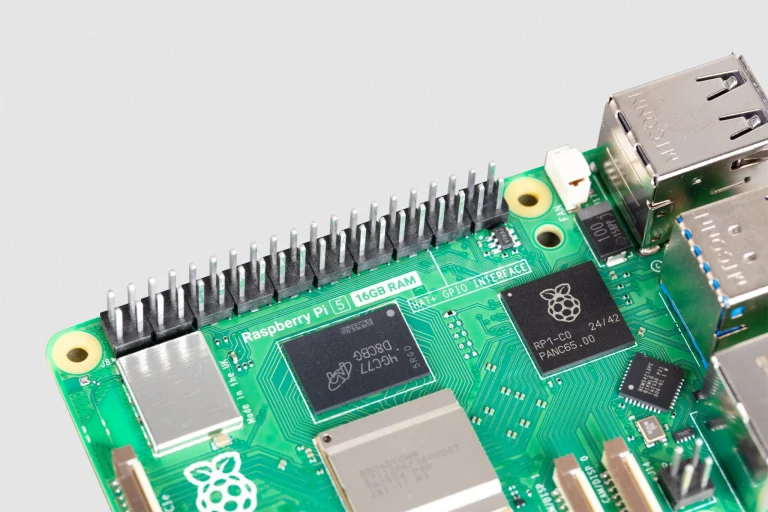
The Raspberry Pi 16GB price jumps to $385 as persistent DRAM supply shortages force manufacturer price hikes across high-memory flagship boards.
cPGuard supply chain attack: an update channel compromise pushed a backdoor in versions 5.88.12-5.88.19. Update to 5.88.25 and rotate credentials.
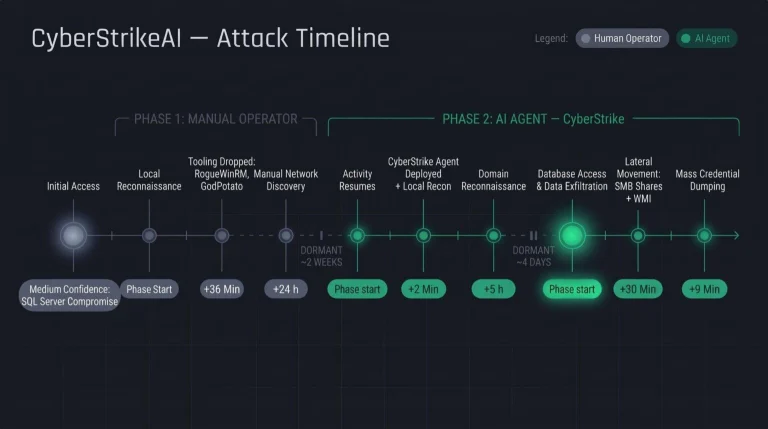
Kaspersky uncovered CyberStrikeAI framework attacks using AI to automate post-exploitation and compromise domains across education networks.
Microsoft expands the Windows 11 26H2 upgrade rollout to eligible Windows 10 PCs, offering optional full feature updates via Windows Update.
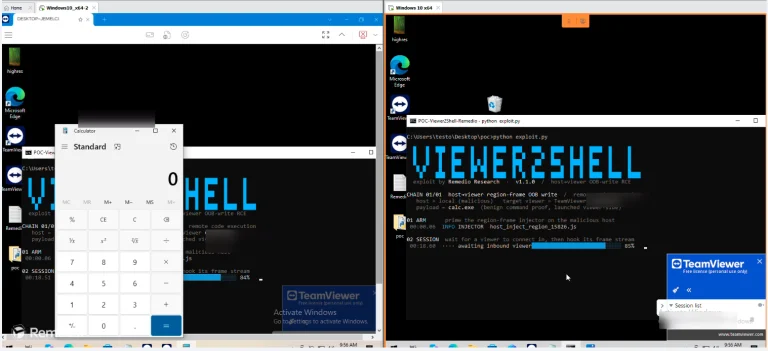
A high-severity TeamViewer client vulnerability allows compromised remote machines to trigger memory corruption and execute arbitrary code on admin devices.
Anthropic updated Claude Opus 5.5 and Claude Code to block Claude video game cloning, preventing unauthorized remakes of commercial titles.

Pluto Research exposes Hugging Face malware. This Hugging Face malware campaign drops cryptominers and backdoors on self-hosted AI servers.
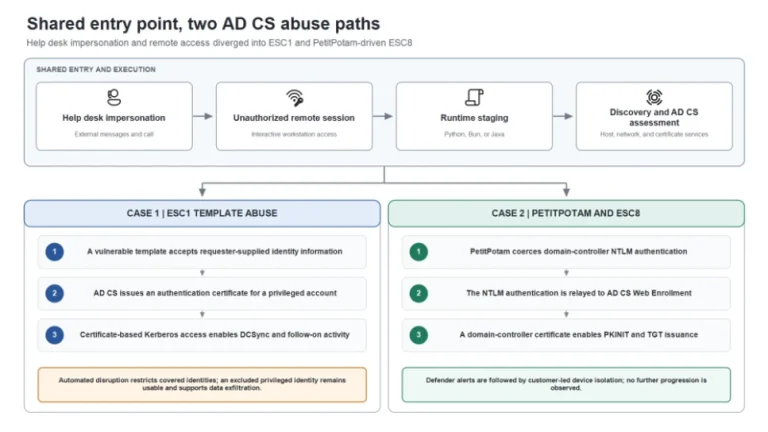
Microsoft details help desk impersonation on Teams that led to AD CS abuse via ESC1 and ESC8, giving attackers privileged certificates.
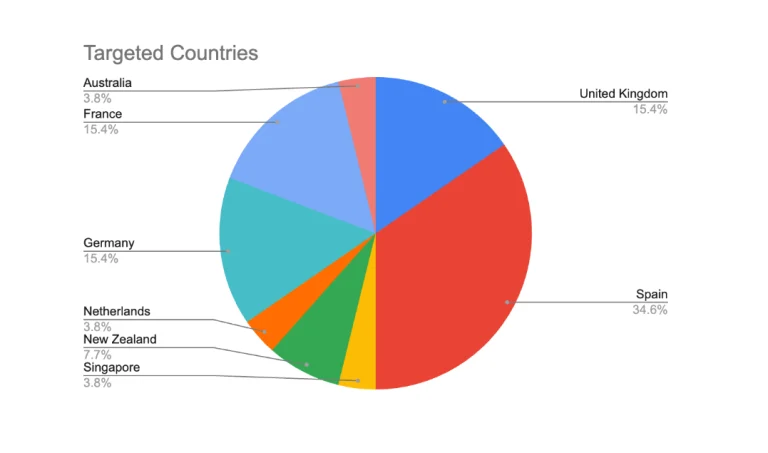
StyleSmuggler exploitation of CVE-2026-75650 drops the PSK Agent RAT and a PHP webshell on Magento stores. See how to detect and respond.
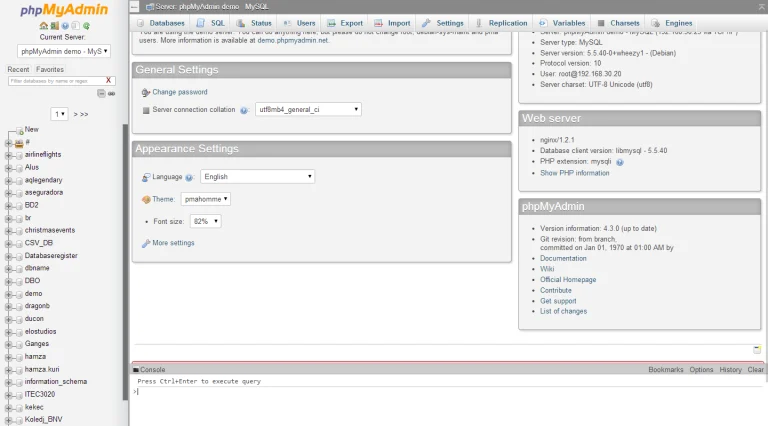
Discover seven unpatched phpMyAdmin vulnerabilities exposing servers to SQL injection and auth bypass. Learn how to secure your databases today.
The ASF patched Apache security vulnerabilities with new Apache security fixes for Syncope, Arrow, and Fineract, including critical flaw CVE-2026-64618.
SUSE fixed Rancher security vulnerabilities, including Rancher credential leak CVE-2026-88811, an SSRF flaw, and an unauthorized shell bypass. Update now.
The November 2026 Android security update fixes 216 flaws, including zero-click remote code execution bugs CVE-2026-58868 and CVE-2026-58936.
Arista fixed critical Arista security vulnerabilities CVE-2026-111497 and CVE-2026-98432 that allow unauthenticated remote code execution. Update now.
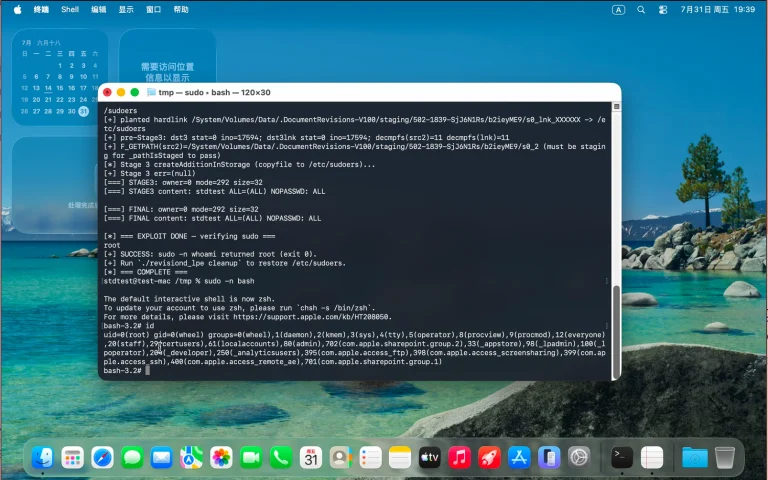
Technical details and a macOS revisiond vulnerability PoC exploit for CVE-2026-112487 are public, allowing root elevation. Update macOS immediately.
Details and an Axis Camera Station RCE PoC are public. Patch CVE-2025-30026, CVE-2025-30023, and CVE-2026-63286 to prevent camera credential theft.