 Do Son
Linux kernel vulnerabilities this week: 129 CVEs, including critical iSCSI flaws CVE-2026-99154 and CVE-2026-99153. Get the kernel security update.
News
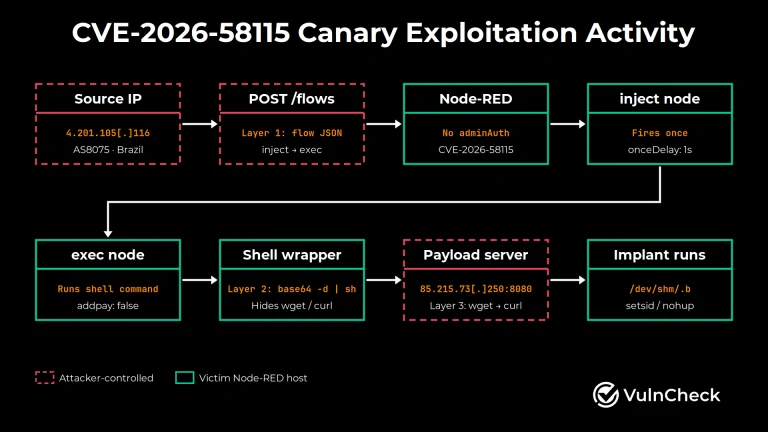
A critical 10.0 CVSS Node-RED RCE vulnerability (CVE-2026-58115) is exploited in the wild to deploy Linux bot malware. Secure your exposed instances now.
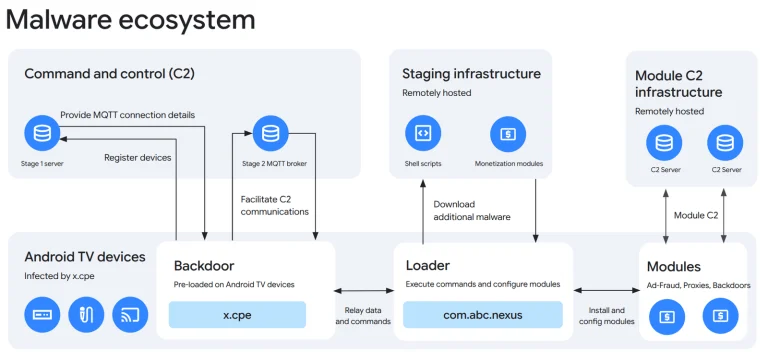
Google dismantled the Videostrong XCPE botnet infecting 1.3M set-top boxes. The XCPE botnet sold residential proxy access to cybercrime affiliates.
A suspected supermarket freezer hack altered refrigeration units to 50C across Sweden, Belgium, and Estonia, spoiling food and forcing store closures.
Patch two Barracuda vulnerabilities, CVE-2026-116606 and CVE-2026-111560, that allow attackers to gain Barracuda root access across multiple appliances.
OpenAI announced new ChatGPT violence restrictions and teen safety protections, restricting weapon queries and terminating hazardous conversations.
An Amadeus airline data breach compromised passenger travel records across Malaysia Airlines, JAL, ANA, and Cathay Pacific via compromised credentials.
Tech giants support a new AI training preference standard in robots.txt, giving publishers granular control over model training data.
The November 2026 bulletin resolves critical MediaTek vulnerabilities, including modem flaws CVE-2026-20499, CVE-2026-20545, and CVE-2026-20546.
Google Project Suncatcher achieved orbital AI inference using datacenter TPUs and Gemma 4 aboard a prototype satellite to generate space poetry.
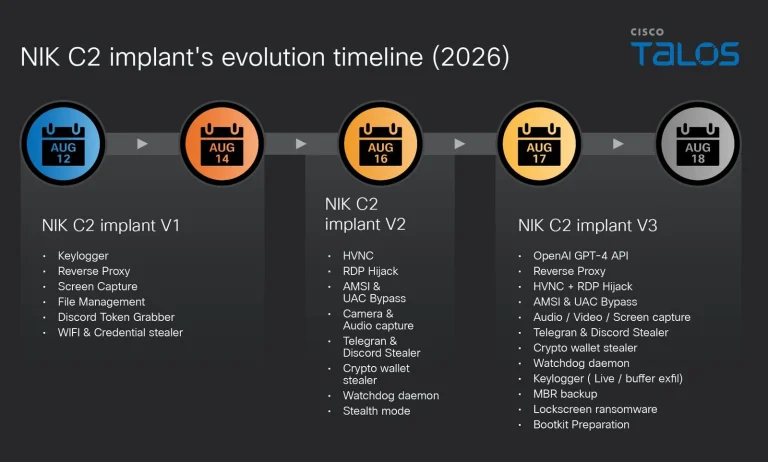
Cisco Talos uncovers the NIK C2 framework. This Windows NIK C2 framework abuses OpenAI APIs to analyze stolen victim data and deploy screen lockers.
OpenAI announced that ChatGPT Codex usage limits will merge under a shared token quota across Plus, Pro, and Business plans starting December 2026.
Anthropic unveiled the Claude Ultra subscription tier, removing 5-hour rate limits for verified accounts and bundling $200 in monthly API credits.
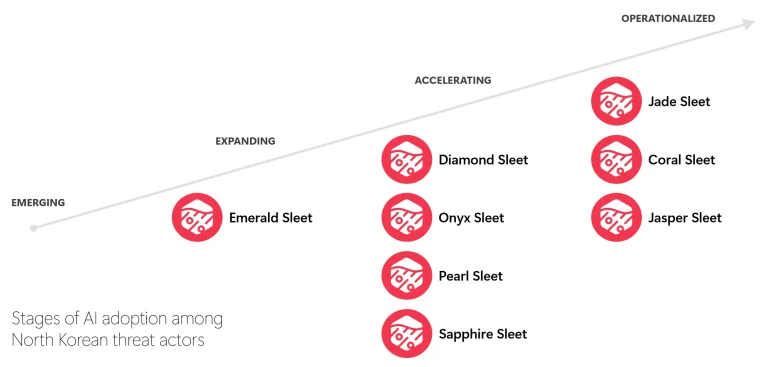
Microsoft reveals how North Korean threat actors use tools like ARTEX. See how AI-enabled North Korean threat actors speed up cyber operations.
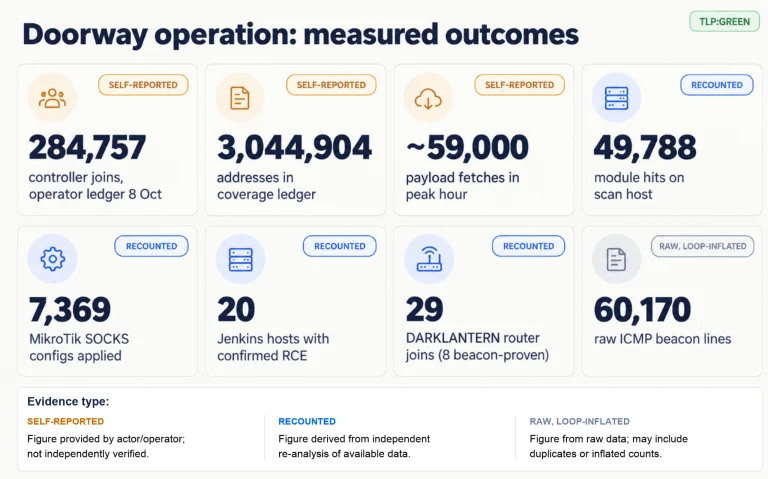
CloudSEK uncovers the Doorway botnet. The Rust Doorway botnet exploits routers, cameras, and servers to build a global proxy network.
Details and a Linux kernel vulnerability PoC exploit are public for CVE-2026-31419. Patch this high-severity flaw to prevent local privilege escalation.
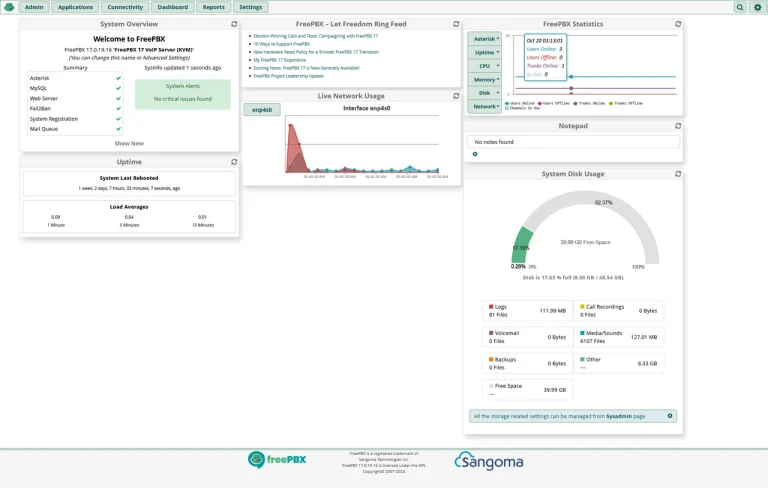
Apply the latest update to fix critical FreePBX vulnerabilities, including a 9.3 CVSS authentication bypass and privilege escalation in User Manager.
The rise of vibe manufacturing AI allows makers to transform conversational prompts into physical hardware, custom sheet metal, and printed circuit boards.
Apache Wicket vulnerabilities: a security update fixes 19 flaws, including CVE-2026-84170 upload DoS and XSS bugs. Upgrade to 8.20.0, 9.25.0 or 10.12.0.
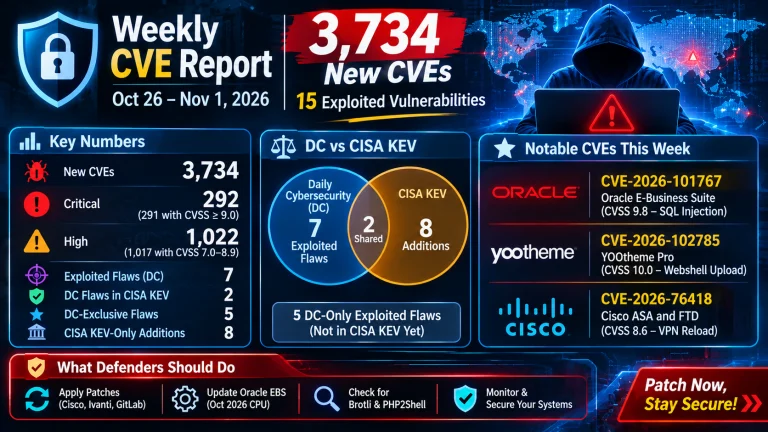
Our weekly CVE report for Oct 26-Nov 1, 2026 tracks 3,734 new CVEs and 15 exploited vulnerabilities, including Oracle EBS flaws not in CISA KEV.
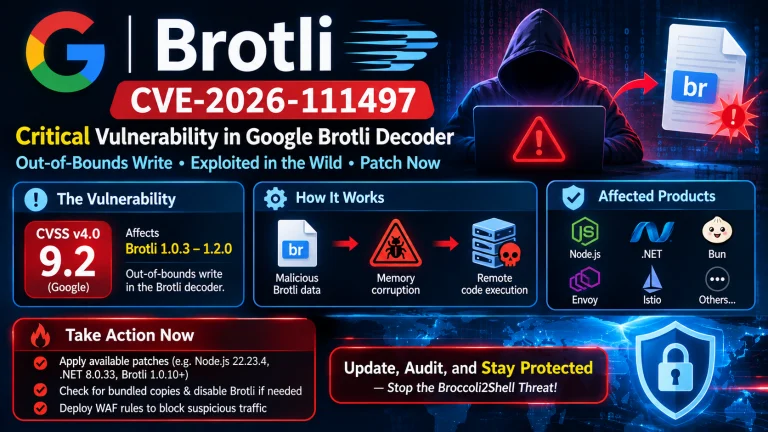
Brotli vulnerability CVE-2026-111497 affected products list: fixes for Node.js, .NET, Envoy, PAN-OS and distros, plus VMware and others still unpatched.
The PostgreSQL project resolved 15 critical pgAdmin 4 vulnerabilities in version 9.19, fixing command injection flaw CVE-2026-116241 and credential leaks.