 Do Son
A critical Metabase SQL injection zero-day (CVSS 10) is exploited in the wild. Unauthenticated attackers gain admin access. Patch now.
sql injection
A pgAdmin 4 RCE flaw, CVE-2026-17566, lets attackers run OS commands via psql. Two more critical bugs also got fixed in version 9.17.
Adobe patched critical Adobe Campaign Classic flaws. CVE-2026-48331 scores CVSS 10.0 and enables arbitrary code execution. Update to build 9399 now.
CVE-2026-16462 is a critical SQL injection in Weidmueller PROCON-WEB SCADA, rated CVSS 9.8. An unauthenticated attacker can run SQL commands. Patch now.
A CodeIgniter4 RCE vulnerability, CVE-2026-63223 (CVSS 9.8), enables remote code execution via file upload. Patch to v4.7.4 to fix four flaws.
A PHP SQL injection flaw, CVE-2026-17543, was patched alongside two memory bugs. Update to PHP 8.2.33, 8.3.33, 8.4.24, or 8.5.9 now.
Apache Syncope patches an SQL injection (CVE-2026-57308) and a privilege escalation flaw (CVE-2026-62183). Update to 4.0.7 or 4.1.2 to stay safe.
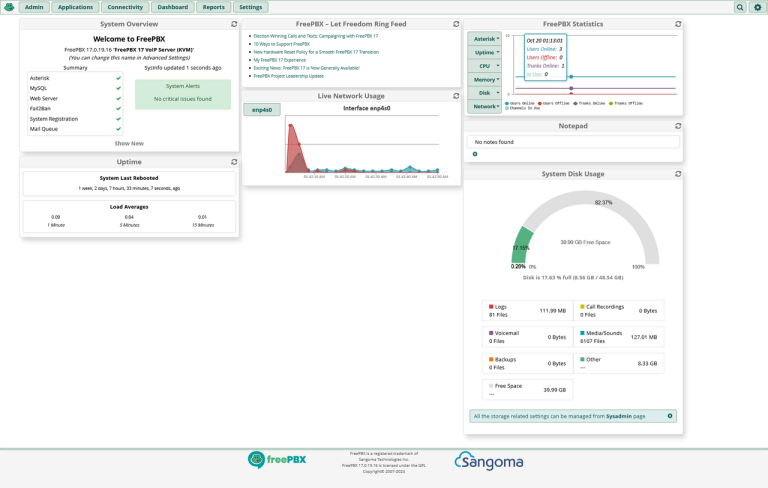
Two critical FreePBX vulnerabilities allow unauthenticated RCE and administrator takeover via UCP and missedcall. Patch FreePBX now.
CISA added four flaws to its KEV catalog, including WordPress RCE (CVE-2026-63030) and Langflow RCE (CVE-2026-0770). All are exploited in the wild.
Three Apache Fineract SQL injection flaws (CVE-2026-57821, CVE-2026-56287, CVE-2026-35152) let authenticated users exfiltrate data. Upgrade to 1.15.0.
WordPress pre-auth RCE CVE-2026-63030 chains a REST batch bug with SQL injection. Details and a public PoC are out. Update to WordPress 7.0.2 now.
CVE-2026-1207 is a Django SQL injection flaw (CVSS 8.3) in PostGIS raster lookups. Canada's CCCS says it is exploited in the wild. Patch now.
Ubiquiti's UniFi security advisory 066 patches 25 flaws, including a critical command injection (CVE-2026-50746) scoring 10.0. Update your devices now.
A public PoC is available for CVE-2026-57517, a critical CVSS 9.8 Control Web Panel SQLi flaw allowing unauthenticated remote code execution.
Five StoneFly Storage Concentrator flaws include two CVSS 10 command injection bugs allowing unauthenticated root RCE. Update to 8.0.4.29 now.
Cacti vulnerabilities in 1.2.30 include pre-auth SQL injection and LFI, both CVSS 9.8 (CVE-2026-39955, CVE-2026-39938). Update to 1.2.31 now.
Mitel patched 12 critical MiCollab vulnerabilities, several at CVSS 10.0. Unauthenticated command injection and SQL injection flaws need urgent updates.
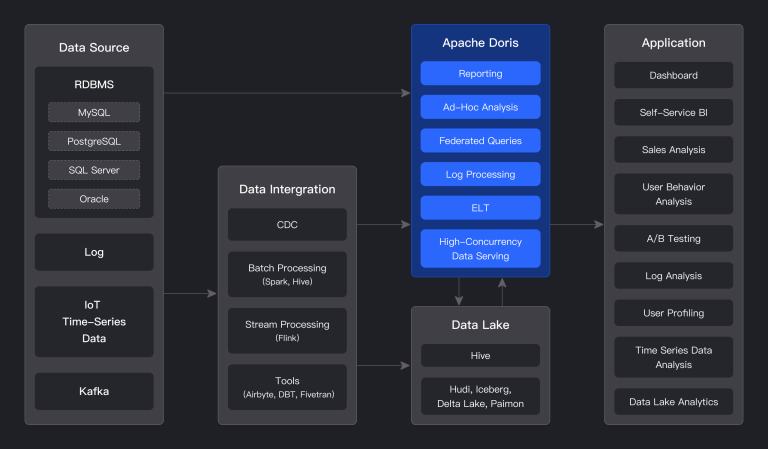
A critical Apache Doris SQL injection vulnerability identified as CVE-2025-66336 allows attackers to bypass authentication. Upgrade your servers now.
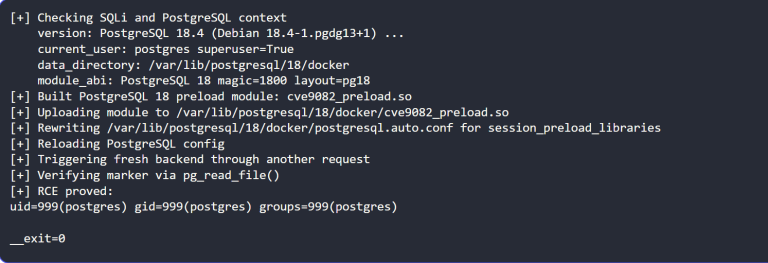
A critical Drupal SQL injection exploit is active in the wild. Read the analysis of this flaw now that the wild exploit PoC is fully public.
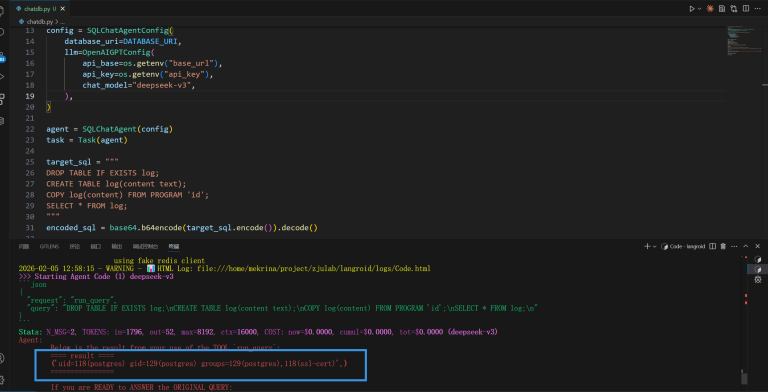
A critical Langroid vulnerability causes RCE via prompt injection. Learn how this LLM security flaw impacts database hosts and how to patch it.
New Roundcube Webmail updates fix security flaws that could expose mailboxes. See which versions are affected and update your server now.
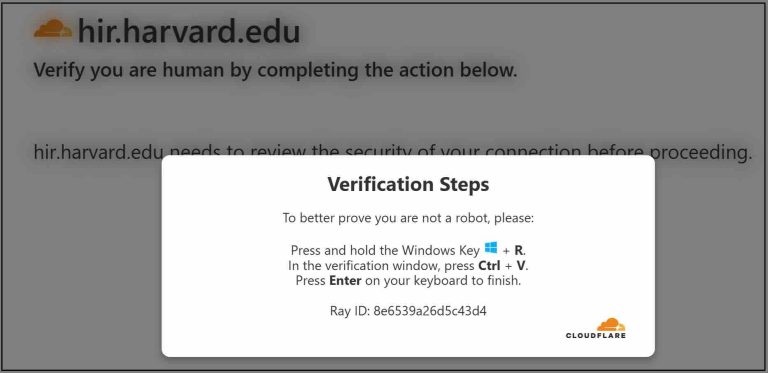
XLab uncovers a massive Ghost CMS poisoning campaign utilizing CVE-2026-26980 to launch FakeCaptcha attacks. Learn how to secure your site.