 Do Son
A critical Drupal SQL injection exploit is active in the wild. Read the analysis of this flaw now that the wild exploit PoC is fully public.
sql injection
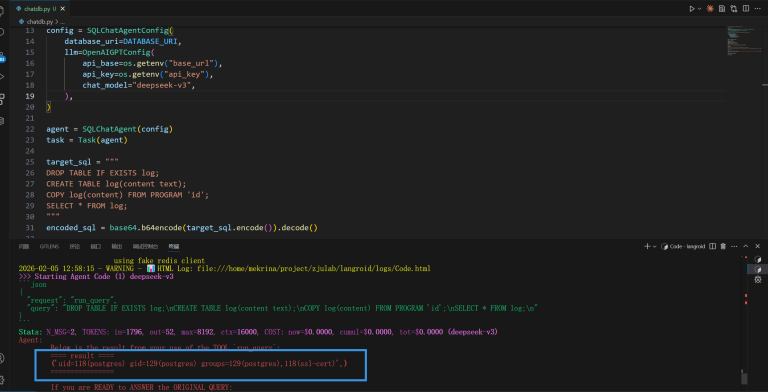
A critical Langroid vulnerability causes RCE via prompt injection. Learn how this LLM security flaw impacts database hosts and how to patch it.
New Roundcube Webmail updates fix security flaws that could expose mailboxes. See which versions are affected and update your server now.
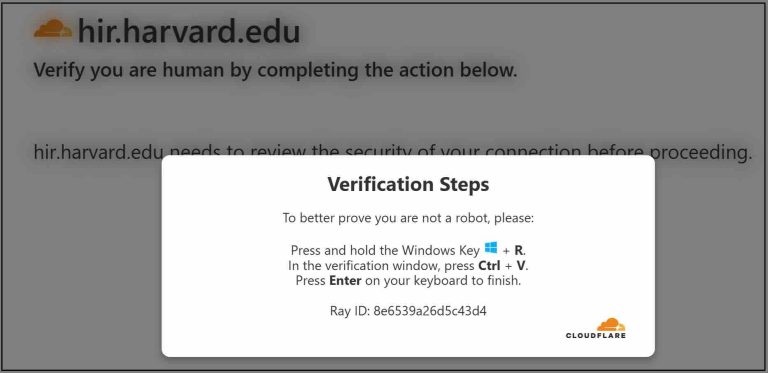
XLab uncovers a massive Ghost CMS poisoning campaign utilizing CVE-2026-26980 to launch FakeCaptcha attacks. Learn how to secure your site.

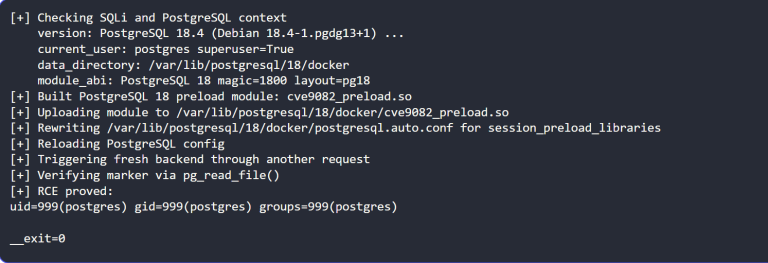
Urgent: Drupal releases patches for highly critical SQLi flaw CVE-2026-9082. Unauthenticated attackers can exploit PostgreSQL backends for full remote RCE.

PostgreSQL releases updates for versions 14-18 fixing 11 vulnerabilities (CVSS 8.8). Plus, critical End-of-Life deadline issued for Postgres 14.
Marten .NET library suffers a critical 9.8 CVSS SQL injection flaw (CVE-2026-45288). Learn how to block the exploit and patch your databases now!

Critical CVE-2026-35194 flaw in Apache Flink allows RCE via SQL injection on TaskManagers. Upgrade your clusters immediately to secure your data!
Two critical flaws in Strapi CMS (CVE-2026-27886 & CVE-2026-22599) allow unauthenticated admin takeover and SQL injection. Update your nodes now!

cPanel & WHM fix 5 critical vulnerabilities (CVE-2026-29205). Fixes for arbitrary file read, SQLi, and privilege escalation are now live. Update now!

pgAdmin 4 v9.15 fixes a 9.4 CVSS auth bypass and multiple RCE flaws. Attackers can execute OS commands via SQL tools. Upgrade your pgAdmin server now!

SAP’s May 2026 Patch Day fixes two 9.6 severity flaws in S/4HANA and Commerce Cloud. Prevent SQL injection and RCE by updating your SAP landscape today.
Full Exploit Disclosed: Public PoC and Technical Details Released for Critical ProFTPD SQL Injection
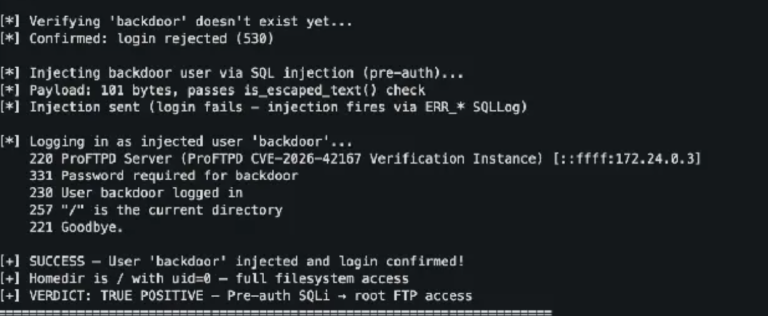
Full Exploit Disclosed: Public PoC and Technical Details Released for Critical ProFTPD SQL Injection
Critical SQLi in ProFTPD's mod_sql allows unauthenticated admin account injection. Full PoC code is public. Upgrade to v1.3.9a to secure your servers.
Spring AI discloses two critical injection flaws (CVE-2026-40967 & 40978) in Vector Store implementations. Upgrade to v1.0.6 or v1.1.5 now to prevent data leaks.
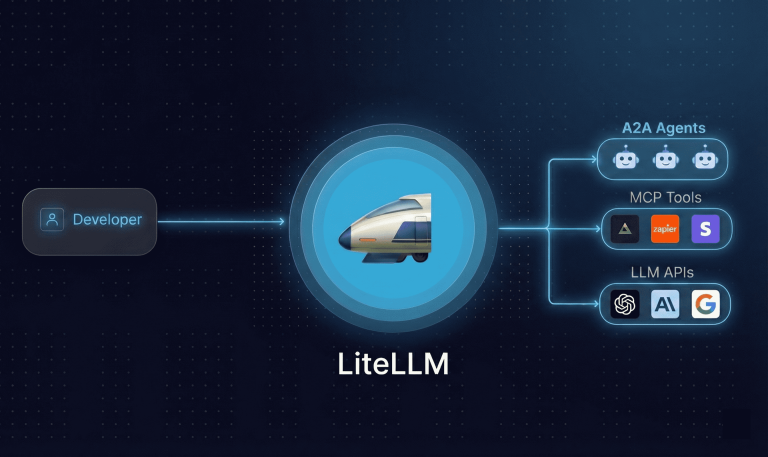
LiteLLM CVE-2026-42208 is under active exploitation. Attackers are using SQL injection to steal AI credentials. Patch to v1.83.7 and rotate keys immediately.
ElectricSQL reveals a critical 10.0 CVSS SQL injection (CVE-2026-40906). Attackers can hijack PostgreSQL and bypass tenant isolation. Patch to v1.5.0 now.
Critical 10.0 CVSS flaw in Firebird Database allows RCE via path traversal in the engine loader. Attackers gain root/SYSTEM privileges. Patch to 5.0.4+ now.
Vendure Core faces a critical 9.1 SQL Injection via the Shop API. Unauthenticated attackers can hijack databases—upgrade to 3.6.2, 3.5.7, or 2.3.4 now!

SAP’s April 2026 updates fix a critical 9.9 CVSS SQL injection in Business Warehouse and 19 other security flaws. Audit your S/4HANA and BPC systems today.

Movable Type patches a critical 9.8 CVSS RCE vulnerability in its Listing Framework. Secure your CMS against Perl code execution and SQLi—update today!

Mitel patches a critical 9.8 CVSS SQL injection in MiCollab. Learn how this unauthenticated flaw chains to full system takeover. Upgrade to v10.2 SP1 now!

SonicWall patches critical SMA 1000 flaws, including a 7.2 SQL injection for privilege escalation and Unicode-based MFA bypasses. Secure your VPN—update now!