 Do Son
CISA KEV Catalog adds CVE-2026-123158, CVE-2026-116779, CVE-2026-123218, and CVE-2026-102895 after attackers exploit these four flaws in the wild.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
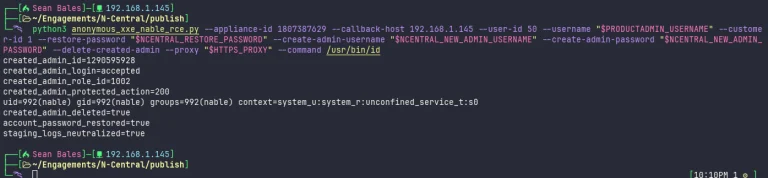
Details and a proof-of-concept exploit for 33 N-central vulnerabilities are public. N-able took hosted N-central offline and is building a hotfix.
Google fixes Chrome zero-day CVE-2026-125350, exploited in the wild, plus 8 more flaws. Install the Chrome security update to 157.0.8103.50 now.
Roundcube Webmail 1.6.21 and 1.7.6 fix 17 bugs, including Sieve injection, SSRF and CSRF bypasses. Apply the Roundcube security update now.
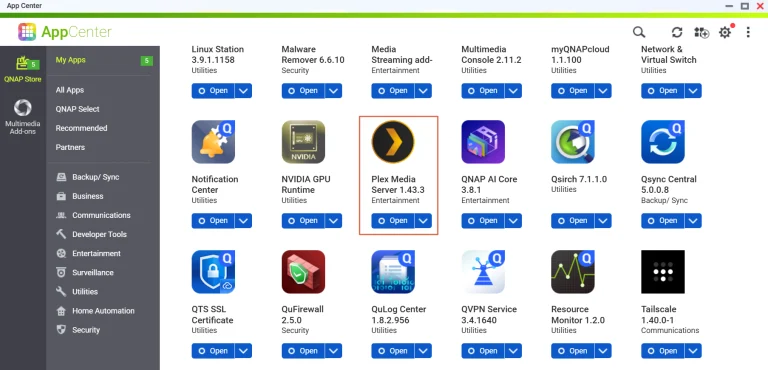
QNAP warns that exploited Plex2Shell vulnerabilities in Plex Media Server 1.43.2 hit QNAP NAS users. Update to 1.43.3.10861 and check for compromise.
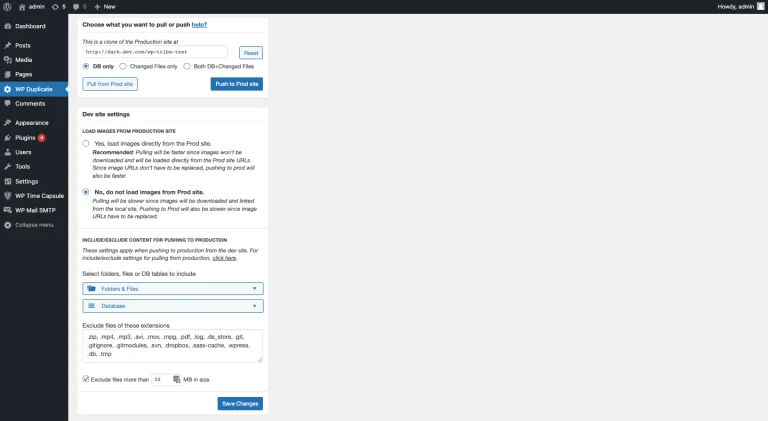
WP Duplicate vulnerability CVE-2026-123751 is exploited in the wild, letting attackers upload files and run code. No patch exists, so remove the plugin.
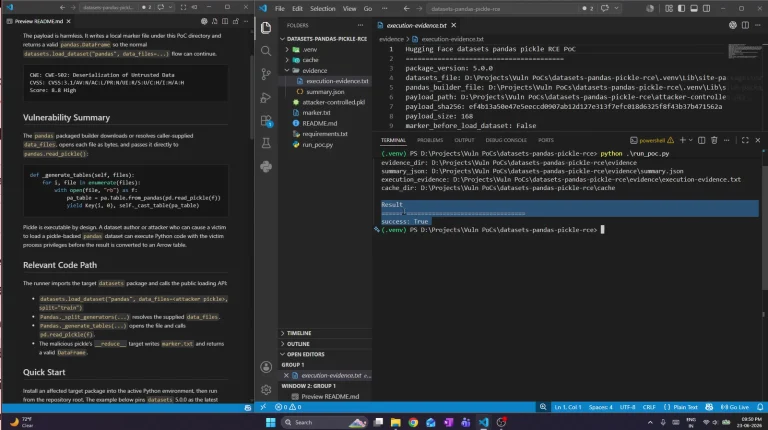
Hugging Face datasets RCE CVE-2026-57845 (CVSS 8.8) has a public proof-of-concept. The library sees 38M monthly downloads, and no fixed release exists.
Openwave Webtop vulnerability CVE-2026-111793 is exploited in the wild, per JPCERT/CC. Upgrade Webtop Media Transcoder to 1.1.22.0 or later.
ModSecurity vulnerabilities CVE-2026-104269 and CVE-2026-73857 now have public details and a proof-of-concept. Upgrade to libmodsecurity 3.0.17.
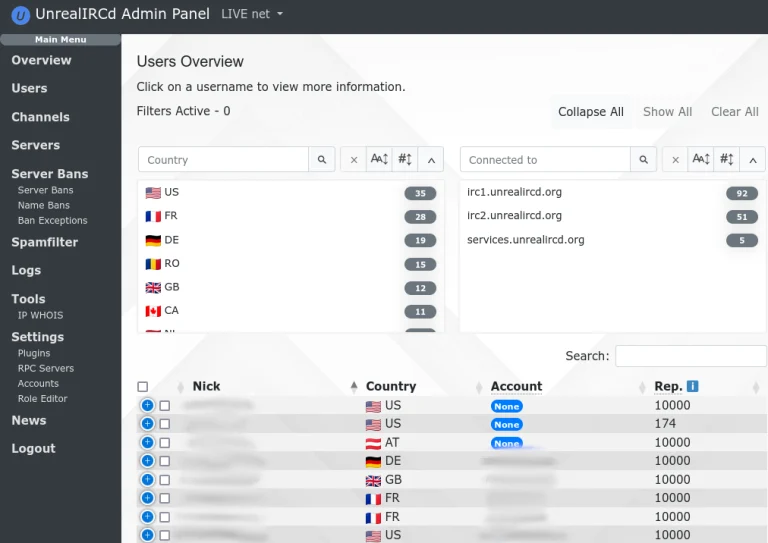
UnrealIRCd vulnerability CVE-2026-114713 is exploited in the wild, letting users run IRCOp commands. Hot-patch or upgrade to 6.2.7.1 now.
A uutils coreutils vulnerability (CVSS 9.9) let translation files inject code; details and a proof-of-concept are now public. Upgrade to uucore 0.12.0.
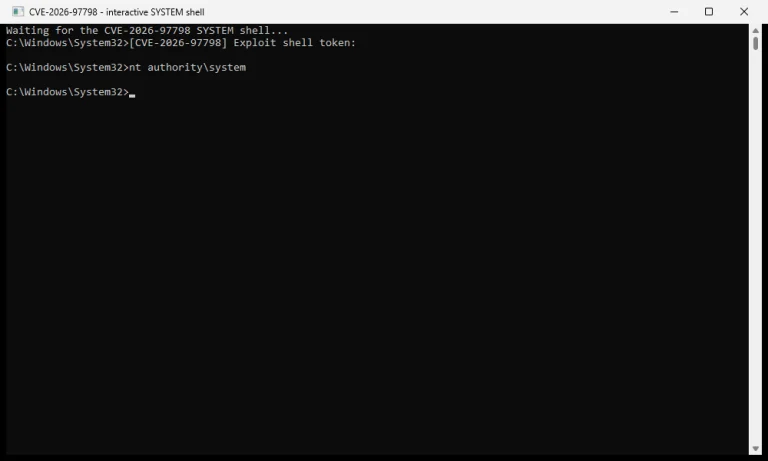
A proof-of-concept exploit for CVE-2026-97798, a Windows Error Reporting vulnerability, gives a SYSTEM shell. Install the October 2026 update now.
IBM API Connect vulnerabilities: 208 flaws, including authentication bypass CVE-2026-17301 and hard-coded credentials. Apply IBM's fixes now.
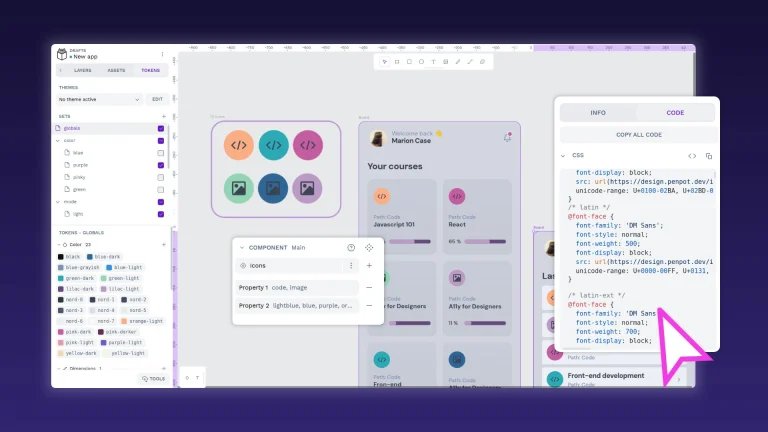
Technical details and PoC exploit code for the critical Penpot file takeover flaw are now public. Upgrade to version 2.18.0 now.
Attackers exploit the SonicWall SonicOS SSLVPN flaw CVE-2026-19868 in the wild. Update Gen7 and Gen8 firewalls now to patch CVE-2026-107155 and 6 bugs.
Update your Veeam Software Appliance and Backup & Replication servers now to fix CVE-2026-98432, a critical 9.8 CVSS Linux kernel flaw.
Install the latest JetBrains security updates now to patch CVE-2026-123294, CVE-2026-123279, and 59 other flaws across Hub, Datalore, and IntelliJ IDEA.
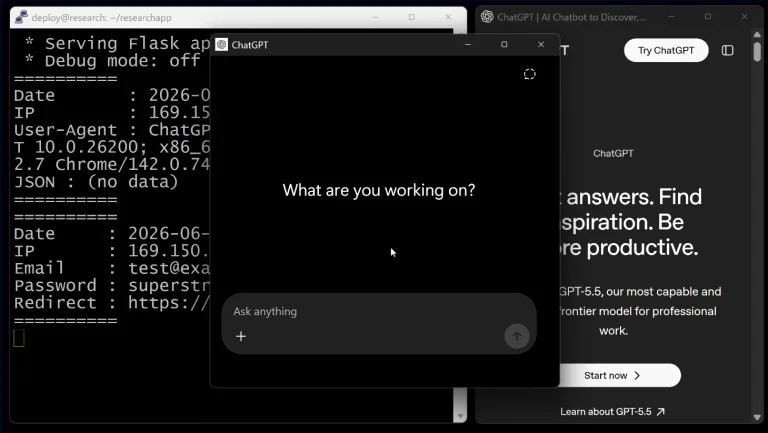
Check Point uncovered a ChatGPT Lockdown Mode bypass in HTML previews, enabling zero-click data exfiltration and phishing before OpenAI deployed a patch.
Microsoft patched Windows Paint RCE vulnerability CVE-2026-83844 with an 8.1 CVSS score. Update now to block potential remote code execution attacks.
CISA warns of critical Subnet Solutions PowerSYSTEM Center flaws CVE-2026-63017 and CVE-2026-63774 that allow authorization bypass and SQL injection.
Patch ManageEngine Key Manager Plus, Log360, and PAM360 now to fix CVE-2026-77690, CVE-2026-13594, and nine other critical and high flaws.
Update Sonatype Nexus Repository 3 to version 3.98.0 now to fix CVE-2026-113373, CVE-2026-113374, and five other critical security flaws.