 Do Son
Chrome security update: Chrome 157 fixes 213 flaws, including critical bugs CVE-2026-121156 in Dawn and CVE-2026-121035 in Prerender. Update now.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
Ubuntu puts fixes for CVE-2026-98432, a Linux kernel TCP flaw rated CVSS 9.8, in the proposed pocket for 22.04 LTS and newer. Older releases wait.
cPGuard supply chain attack: an update channel compromise pushed a backdoor in versions 5.88.12-5.88.19. Update to 5.88.25 and rotate credentials.
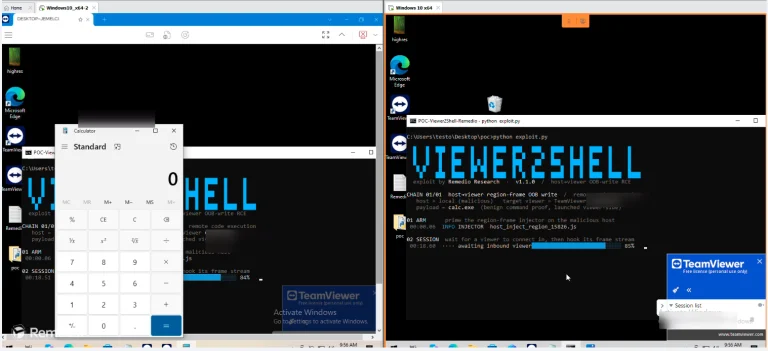
A high-severity TeamViewer client vulnerability allows compromised remote machines to trigger memory corruption and execute arbitrary code on admin devices.
Discover seven unpatched phpMyAdmin vulnerabilities exposing servers to SQL injection and auth bypass. Learn how to secure your databases today.
The ASF patched Apache security vulnerabilities with new Apache security fixes for Syncope, Arrow, and Fineract, including critical flaw CVE-2026-64618.
SUSE fixed Rancher security vulnerabilities, including Rancher credential leak CVE-2026-88811, an SSRF flaw, and an unauthorized shell bypass. Update now.
The November 2026 Android security update fixes 216 flaws, including zero-click remote code execution bugs CVE-2026-58868 and CVE-2026-58936.
Arista fixed critical Arista security vulnerabilities CVE-2026-111497 and CVE-2026-98432 that allow unauthenticated remote code execution. Update now.
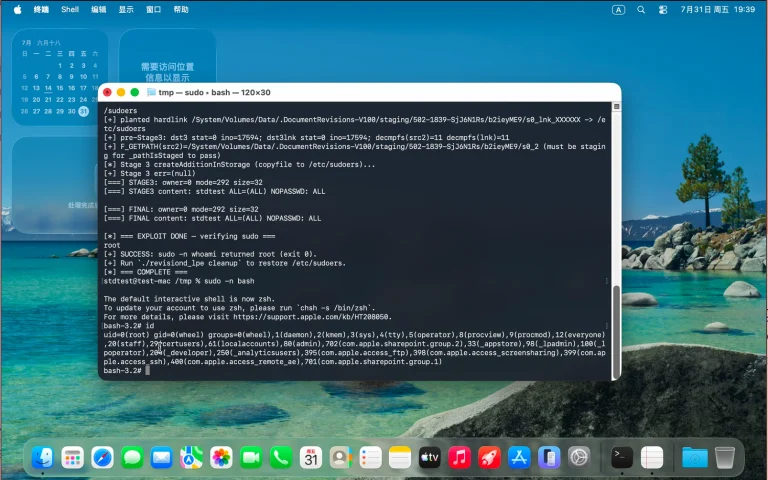
Technical details and a macOS revisiond vulnerability PoC exploit for CVE-2026-112487 are public, allowing root elevation. Update macOS immediately.
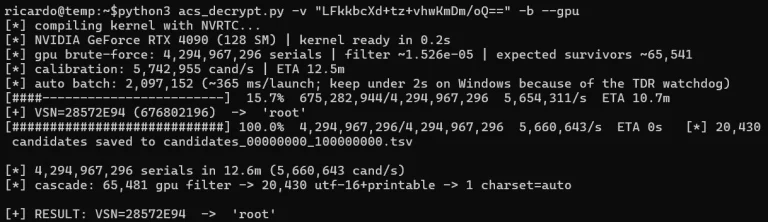
Details and an Axis Camera Station RCE PoC are public. Patch CVE-2025-30026, CVE-2025-30023, and CVE-2026-63286 to prevent camera credential theft.
Linux kernel vulnerabilities this week: 129 CVEs, including critical iSCSI flaws CVE-2026-99154 and CVE-2026-99153. Get the kernel security update.
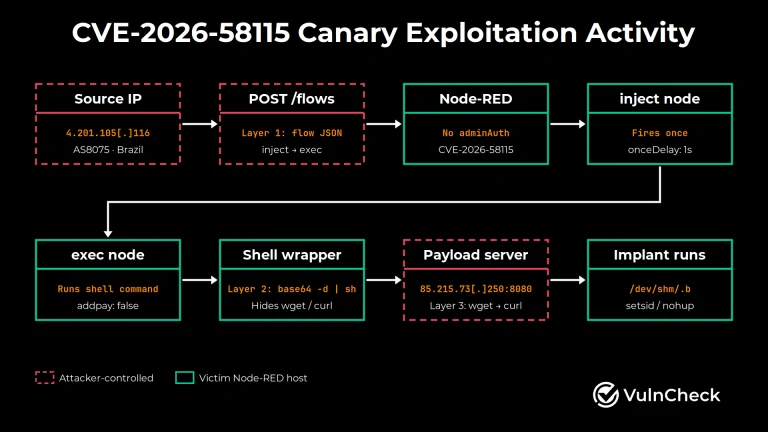
A critical 10.0 CVSS Node-RED RCE vulnerability (CVE-2026-58115) is exploited in the wild to deploy Linux bot malware. Secure your exposed instances now.
Patch two Barracuda vulnerabilities, CVE-2026-116606 and CVE-2026-111560, that allow attackers to gain Barracuda root access across multiple appliances.
The November 2026 bulletin resolves critical MediaTek vulnerabilities, including modem flaws CVE-2026-20499, CVE-2026-20545, and CVE-2026-20546.
Details and a Linux kernel vulnerability PoC exploit are public for CVE-2026-31419. Patch this high-severity flaw to prevent local privilege escalation.
Apply the latest update to fix critical FreePBX vulnerabilities, including a 9.3 CVSS authentication bypass and privilege escalation in User Manager.
Apache Wicket vulnerabilities: a security update fixes 19 flaws, including CVE-2026-84170 upload DoS and XSS bugs. Upgrade to 8.20.0, 9.25.0 or 10.12.0.
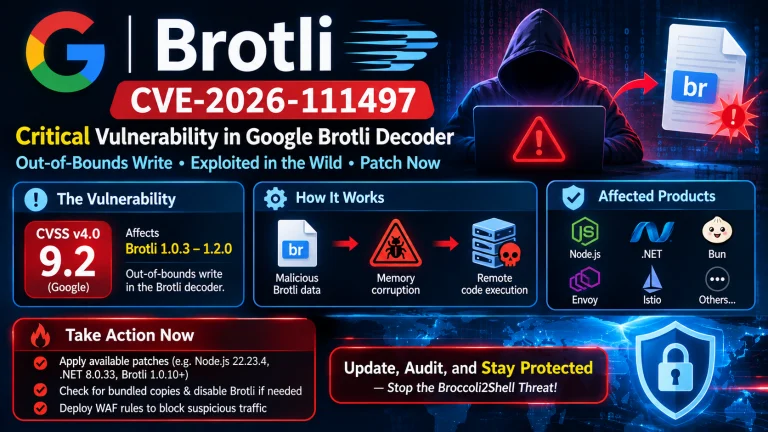
Brotli vulnerability CVE-2026-111497 affected products list: fixes for Node.js, .NET, Envoy, PAN-OS and distros, plus VMware and others still unpatched.
The PostgreSQL project resolved 15 critical pgAdmin 4 vulnerabilities in version 9.19, fixing command injection flaw CVE-2026-116241 and credential leaks.
Dell fixes 44 PowerStore vulnerabilities, including seven CVSS 9.8 SDNAS flaws such as CVE-2026-116443. Upgrade to PowerStoreT OS 5.1.0.0-2798105.
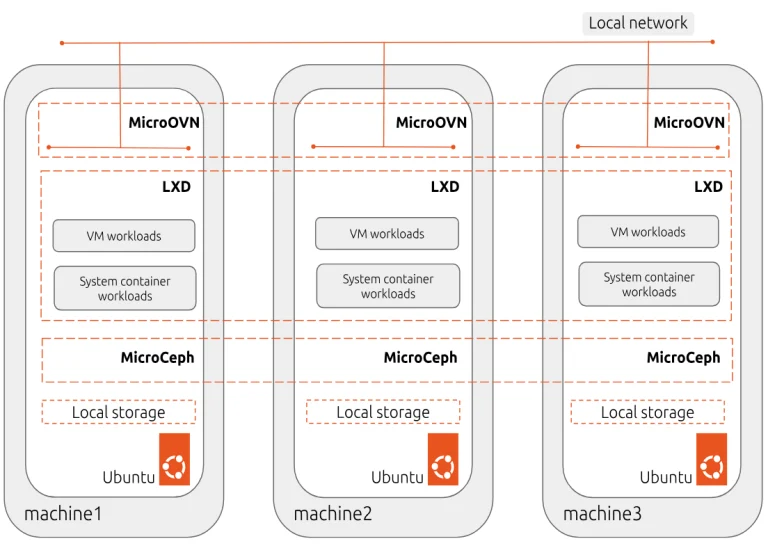
Canonical fixes LXD vulnerability CVE-2026-112816 (CVSS 10) in LXD and MicroCloud, letting attackers impersonate trusted TLS clients. Update now.