 Do Son
15 Apache Traffic Server vulnerabilities, including CVSS 10.0 CVE-2026-111813, allow cache poisoning and smuggling. Upgrade to 10.2.1.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
Cisco's security hardening release fixes Cisco Unified CM vulnerabilities, including CVSS 9.8 flaws CVE-2026-76473 and CVE-2026-76474.
Oracle fixed 98 MySQL vulnerabilities in October 2026, including CVSS 9.8 bugs CVE-2025-15467 in OpenSSL and CVE-2026-9547 in curl.
Upgrade to Apache bRPC 1.18.0 to patch 35 Apache bRPC vulnerabilities, including high-severity flaws CVE-2026-48830 and CVE-2026-56388.
Update the Duplicator WordPress plugin to 5.0.0 to fix CVE-2026-82814, a high-severity PHP Object Injection flaw risking RCE and site takeover.
Apply the GitLab critical patch release to fix 12 GitLab vulnerabilities, including 10.0 CVSS RCE flaw CVE-2026-110264 and CVE-2026-15723.
ISC fixes four BIND 9 vulnerabilities, including CVE-2026-94300 memory corruption and denial of service bugs. Upgrade to BIND 9.20.30 or 9.21.27.
Node.js 26.12.1, 24.22.1 and 22.23.4 fix 10 flaws, including Brotli RCE CVE-2026-111497 and TLS hostname check bypasses. See which versions to install.
PHP fixes two critical PHP RCE vulnerabilities, CVE-2026-109618 and CVE-2026-109619, allowing remote code execution. Update to 8.5.12 or 8.4.27.
Atlassian's October 2026 security bulletin fixes 176 third-party vulnerabilities, 14 critical, in Jira, Confluence, Crowd and Bitbucket.
A CVSS 10.0 E-Business Suite vulnerability, CVE-2026-101809, lets unauthenticated attackers take over Workflow. Oracle fixed 194 EBS flaws.
Six Apache CouchDB vulnerabilities, including CVSS 9.3 CVE-2026-86471, are fixed in 3.5.3. Retired Apache Cocoon gets four unpatched flaws.
Oracle Fusion Middleware vulnerabilities include four CVSS 10.0 bugs such as CVE-2026-87337 in Access Manager and SOA Suite takeover flaws.
Mozilla blocked eight keys in the eMudhra certificate compromise via OneCRL in under three hours, then shipped Firefox 158.0.1 and NSS 3.131.1.
The Chrome 156 security update fixes 353 flaws, including six critical vulnerabilities such as CVE-2026-113341. Update to 156.0.8078.47.
Eight Apache Tomcat vulnerabilities, including a JNDIRealm authentication bypass, are fixed in 11.0.27, 10.1.61 and 9.0.123. Upgrade now.
MariaDB critical vulnerabilities, including CVE-2026-92262 (CVSS 9.9), risk remote code execution. Upgrade to the October 2026 releases.
Oracle Critical Patch Update for October 2026 fixes 1,209 CVEs, including six CVSS 10.0 bugs such as CVE-2026-101809 in E-Business Suite.
30 Advantech ADAM-3600 vulnerabilities, including CVE-2026-43836, allow remote code execution and auth bypass. Update EdgeLink to 2.8.5.0.
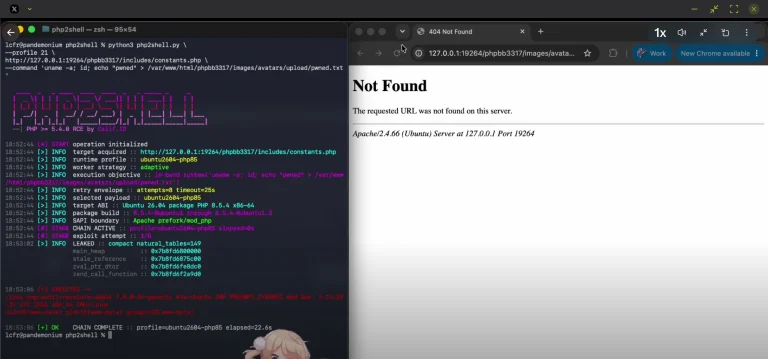
CVE-2026-109618 and CVE-2026-109619 are critical PHP RCE flaws rated CVSS 9.2. Cloudflare reports early attacks. See who is at risk and what to patch.
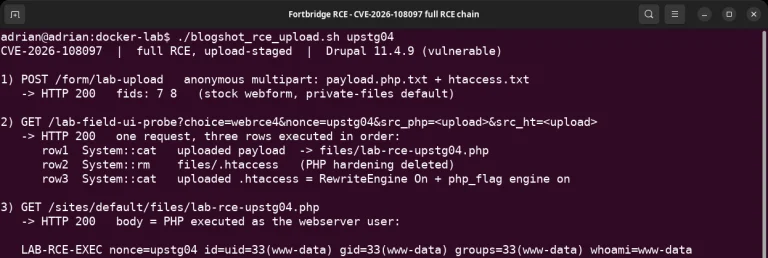
Details and PoC code are public for the Drupal RCE vulnerability CVE-2026-108097 in Field UI. Update to 11.4.10, 11.3.19 or 10.6.19 now.
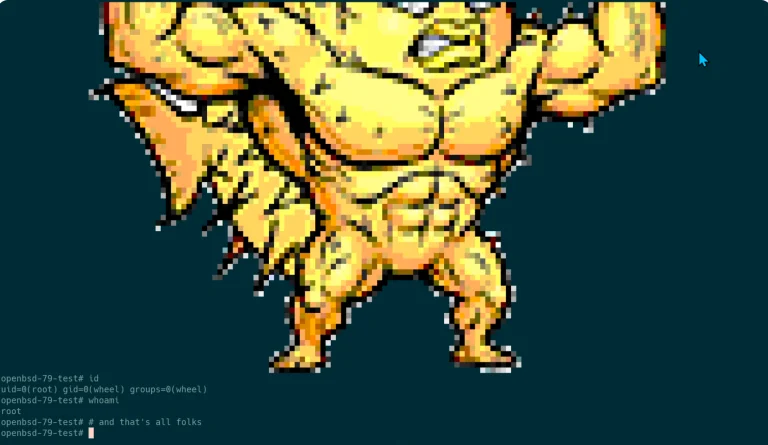
Calif released details and PoC code for an OpenBSD kernel vulnerability enabling local privilege escalation to root. Apply errata 018 and 026.