 Do Son
Threat actors are actively abusing critical AhsayCBS vulnerabilities in the wild to deploy cryptominers. Patch unpatched AhsayCBS vulnerabilities now.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
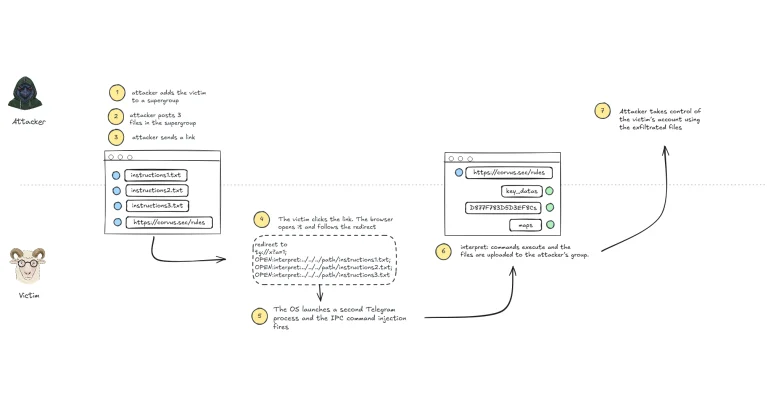
A critical Telegram Desktop account takeover vulnerability (CVE-2026-107181) exposes users to session hijacking. Exploit details and PoC are now public.
HPE fixes a critical HPE iLO 7 vulnerability, CVE-2026-79820, and iMC authentication bypass CVE-2026-79842. Update iLO to 1.25.01 now.
Critical Citrix NetScaler vulnerability CVE-2026-107406 (CVSS 9.5) can lead to RCE on SAML-configured ADC and Gateway. Upgrade now.
IBM fixes 23 IBM DataPower Gateway vulnerabilities, including critical RCE flaws CVE-2026-15762 and CVE-2026-16340. Upgrade to 11.0.0.3 now.
Six Apache DolphinScheduler vulnerabilities, including CVE-2026-71896 and Kubernetes credential leak CVE-2026-71895, are fixed in 3.4.3.
wolfSSH 1.6.0 fixes five wolfSSH vulnerabilities, including critical host key flaw CVE-2026-16516 and Windows login bug CVE-2026-83540.
A Cisco Finesse vulnerability, SSRF flaw CVE-2026-20362, has been publicly disclosed. Fixes arrive in early 2027, with no workarounds.
A VMware VMXNET3 vulnerability, CVE-2026-59346 (CVSS 9.3), allows VM escape. Full details and PoC exploit code are now public. Patch to 26H1u1.
Splunk fixes 22 Splunk Enterprise vulnerabilities, including critical Patroni API flaw CVE-2026-76268 and CVE-2026-76281. Upgrade to 10.4.3 now.
An active WordPress XSS campaign exploits Ninja Forms flaw CVE-2026-94504 and CVE-2026-93836 to plant hidden admin accounts. Patch now.
Cisco License On-Prem vulnerabilities include CVSS 10 flaw CVE-2026-76482 and password reset bug CVE-2026-20328. APIC and Meraki also patched.
Cisco NX-OS vulnerabilities fixed, including critical NX-API RCE flaw CVE-2026-76471 and CVE-2026-76455, across Nexus, MDS and UCS gear. Patch now.
Four critical Cisco Nexus vulnerabilities, including CVE-2026-76485 and CVE-2026-76465 (CVSS 9.8), allow root RCE on NX-OS switches. Patch now.
Four critical Argo CD vulnerabilities, including AppProject bypass CVE-2026-77459, threaten the repo-server and clusters. Upgrade to v3.5.4 now.
Two Apache Jackrabbit vulnerabilities, including critical session hijack flaw CVE-2026-92414 (CVSS 9.3), are fixed. Upgrade to 2.23.6 now.
A Gitea security update fixes 27 flaws, including SSRF bug CVE-2026-101027 and SSH key flaw CVE-2026-103059. Upgrade to Gitea 28.1.0 now.
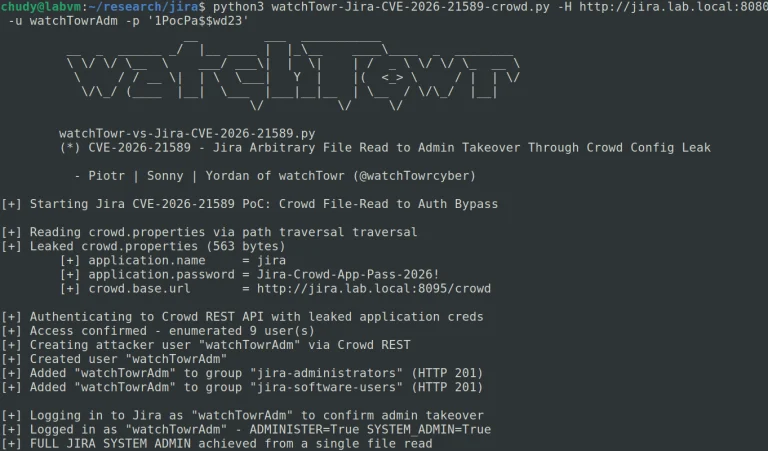
CVE-2026-21589 exploitation is underway against Atlassian servers after researchers published arbitrary file read PoC and technical details.
Elastic fixes 14 Elastic Stack vulnerabilities, including Kibana flaw CVE-2026-102406 and Elasticsearch bug CVE-2026-103007. Upgrade now.
Four ASUS router vulnerabilities are fixed, including critical XSS flaw CVE-2026-14911 and code execution bug CVE-2026-19386. Update firmware now.
Critical ASUSTOR ADM vulnerability CVE-2026-105324 (CVSS 9.2) allows unauthenticated arbitrary file read on NAS devices. Update ADM now.
Nine HPE AOS-Switch vulnerabilities, including unauthenticated RCE flaw CVE-2026-76744 (CVSS 9.8), are fixed. Upgrade to AOS-S 16.11.0032.