 Do Son
Two Handlebars.js vulnerability disclosures (CVE-2026-106445, CVE-2026-106446) enable RCE. Details and PoC are public. Update to 4.7.10 now.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
The Chrome 155 security update fixes 247 flaws, including critical use after free bugs CVE-2026-106382 and CVE-2026-106197. Update now.
Critical Arista CloudVision CUE vulnerability CVE-2026-102159 (CVSS 9.8) and five more flaws hit CV-CUE. Update to WiFi 2026.2.1 now.
HPE fixes 28 ClearPass Policy Manager vulnerabilities, including unauthenticated RCE flaw CVE-2026-76750 (CVSS 9.8). Upgrade to CPPM 6.14.1.
Critical Veeam Backup vulnerability CVE-2025-64393 (CVSS 9.4) enables RCE by low-privileged users. Update to 12.3.2 P4 now.
The WordPress 7.1.3 security update is a WordPress security release that fixes stored XSS, SQL injection and more. Update your site now.
SonicWall SMA1000 vulnerability CVE-2026-102255 (CVSS 10) allows pre-auth SSRF. Three more flaws fixed. Upgrade to 12.5.0-03082 now.
Progress DataDirect vulnerability CVE-2026-91140 enables command injection via crafted OpenAPI files in AI agents. Pull version 2.1 now.
Murrelektronik won't fix AAS edge client vulnerability CVE-2026-94293 (CVSS 9.8), which allows unauthenticated data changes. Remove it now.
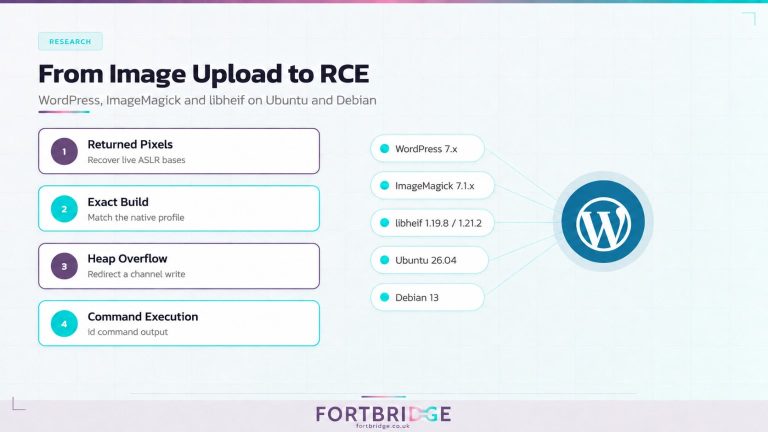
A WordPress libheif RCE chain and its PoC are now public. The libheif vulnerability turns an HEIC upload into code execution. Patch to 1.23.3.
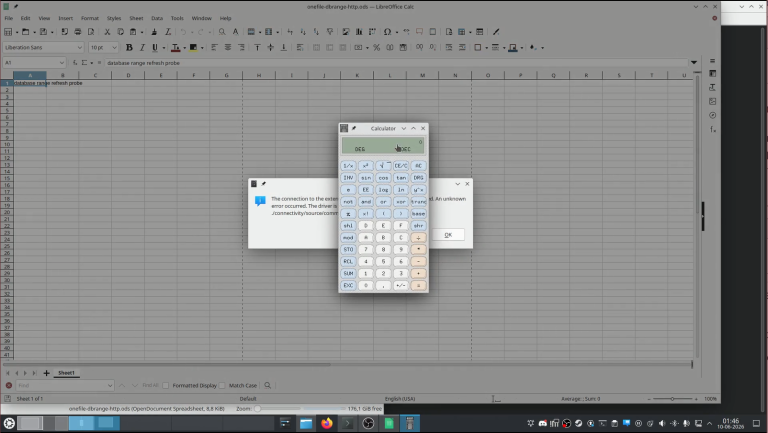
PoC released for LibreOffice Calc vulnerability CVE-2026-63277, which runs code when a file opens. Five more flaws fixed. Upgrade to 26.2.5.
Atlassian Data Center vulnerability CVE-2026-21589 (CVSS 9.3) allows arbitrary file access in Jira, Confluence and Bitbucket. Patch now.
Twenty CRM vulnerability CVE-2026-105763 (CVSS 9.6) enables plaintext password disclosure of IMAP and SMTP accounts. Upgrade to 2.7.0.
IBM fixes 25 Langflow vulnerabilities, including critical RCE flaw CVE-2026-104334 (CVSS 9.8). Upgrade to Langflow 1.12.3 now.
Apache Thrift 0.25.0 fixes 61 Apache Thrift vulnerabilities, including critical heap overflow CVE-2026-91135. Upgrade every binding now.
AMD RCCL vulnerability CVE-2026-43598 in the ROCm Communication Collectives Library could allow RCE on Instinct GPUs. Update to ROCm 7.14.
Struts 7.4.0 fixes four Apache Struts vulnerabilities, including OGNL injection CVE-2026-104711 and a REST plugin DoS. Upgrade now.
Perforce fixes six P4 Search vulnerabilities, including CVE-2026-100103 (CVSS 10) and a JDWP RCE flaw. Upgrade to 2026.4.2 now.
MediaTek security bulletin for October 2026 fixes 31 flaws, including critical MediaTek modem vulnerability CVE-2026-20519. Update now.
PoC and details released for macOS HFS+ vulnerability CVE-2026-43682, a CVSS 9.8 kernel heap overflow. Update to macOS Tahoe 26.6 now.
Citrix NetScaler CVE-2026-88779 is exploited in the wild against NetScaler SAML authentication setups. Upgrade to 14.1-73.41 now.
Unpatched Apache OpenOffice vulnerability CVE-2026-59265 runs code via crafted files. Apache Directory LDAP API and Traffic Server fixes out.