 Do Son
Attackers exploit CVE-2026-100382, a CVSS 10 unauthenticated MediaWiki RCE in External Data. PoC is public. Upgrade to 3.7 now.
Vulnerability News
Vulnerability news from Daily CyberSecurity. We report new CVEs, zero-day flaws, and vendor security advisories as they are published. Each article lists affected versions, severity scores, exploitation status, and the fix. For live data, see CVE Watchtower and the Top Exploited CVEs list.
Discover the latest ModSecurity security vulnerabilities, including WAF evasion and pointer dereferences. Patch these OWASP WAF engine flaws today.
Discover critical Axios security vulnerabilities impacting the Node.js HTTP adapter. Learn how to patch these flaws and protect your applications today.
Dell patched critical Dell Terraform Provider vulnerabilities. CVE-2026-91881 exposes BMC traffic to attackers. Upgrade your providers to stay safe.
Kiteworks vulnerabilities fixed in 9.5.1 include CVE-2026-102115, a 9.8 password reset flaw that enables admin account takeover. Patch now.
Eight Apache MINA SSHD vulnerabilities allow authentication bypass. Fix critical Apache MINA SSHD vulnerabilities by upgrading your Java apps now.
Six critical Apache WSS4J vulnerabilities expose servers to attacks. Update now to resolve these Apache WSS4J vulnerabilities and secure SOAP messages.
CPython developers fixed critical Python SSL vulnerabilities. Update now to resolve these Python SSL vulnerabilities and protect secure network sockets.
CISA warns the Viidure dashcam app leaks hardcoded cloud credentials (CVE-2026-96587) and public storage (CVE-2026-94204). The vendor has not responded.
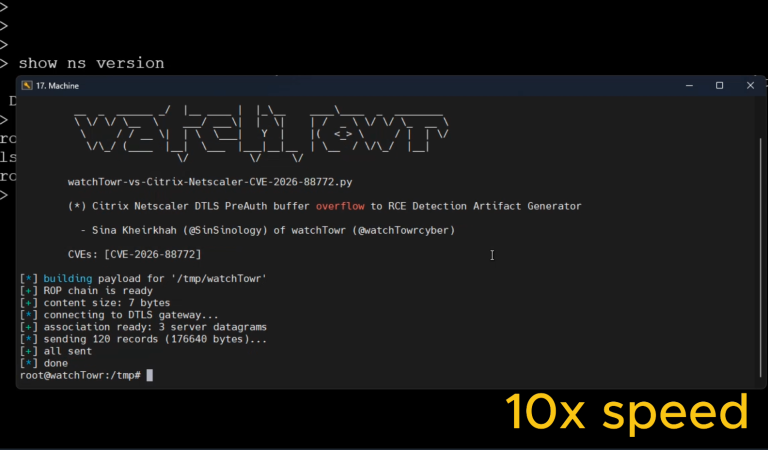
CVE-2026-88772, a Citrix NetScaler DTLS memory overflow, is exploited in the wild. A watchTowr PoC and full details are now public. Patch NetScaler now.
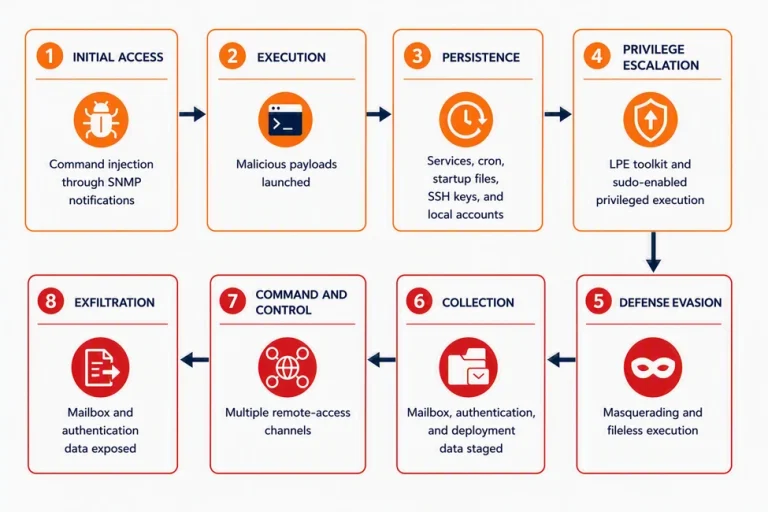
Zimbra CVE-2026-73570 lets one crafted email run code. Microsoft details the Zimbra command injection attacks: web shells, root access, and key theft.
Attackers exploit CVE-2026-76504, a 9.8 authentication bypass in Cisco SD-WAN Manager that grants admin API access. Patch now.
A critical Apache PLC4X vulnerability, CVE-2026-102508, lets attackers impersonate OPC UA servers and steal credentials. Upgrade to PLC4X 1.0.0 now.
Update to 15.82 now. Five high-severity TeamViewer vulnerabilities include CVE-2026-92370, CVE-2026-19743 and CVE-2026-92368 in Full Client and Host.
Five high-severity Electron vulnerabilities, including CVE-2026-102676, CVE-2026-102673 and CVE-2026-102674, weaken sandbox isolation. Update Electron now.
HPE fixed 18 HPE Instant ON vulnerabilities in its access points, including CVSS 9.8 RCE flaws CVE-2026-76721 and CVE-2026-76722. Update to 3.4.2.0.
WatchGuard patched 14 Fireware OS vulnerabilities, including CVSS 9.2 RCE flaw CVE-2026-86131 in BOVPN Over TLS. Update Firebox appliances now.
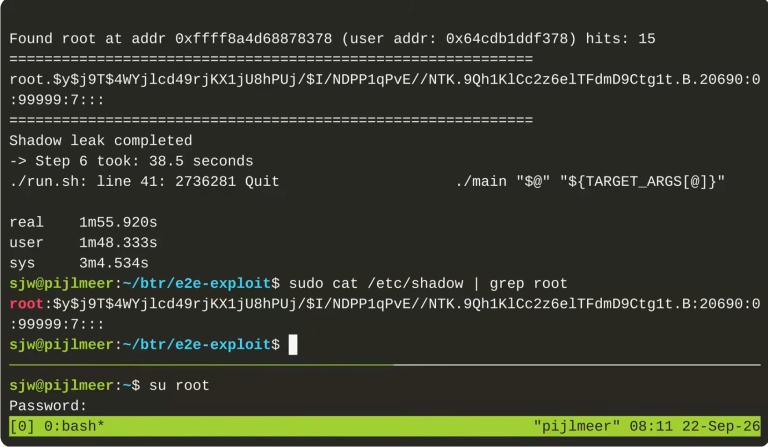
VUSec released details and PoC code for Branch Target Reuse, a Spectre-v2 attack on JIT engines that leaked Linux root password hashes. Patch now.
A CVSS 10 GeoServer Cloud vulnerability in a GitHub Actions workflow could have leaked repository secrets. No abuse found, and the workflow is gone.
A CVSS 10.0 Podman vulnerability, CVE-2026-94603, lets container images disable sandboxing in podman run. Upgrade to Podman 6.1.3 or 5.8.8 now.
A JupyterLab Desktop vulnerability, CVE-2026-102530 (CVSS 9.4), turns a malicious server URL into remote code execution. Update to 4.6.2-1 now.
Google's Chrome security update 154.0.8037.92 fixes 32 flaws, including critical ANGLE bug CVE-2026-102331 and six V8 issues. Update Chrome now.