Six Linux Kernel Flaws Disclosed With Public PoC Exploits for Root Access and Container Escape
 Do Son
TL;DR
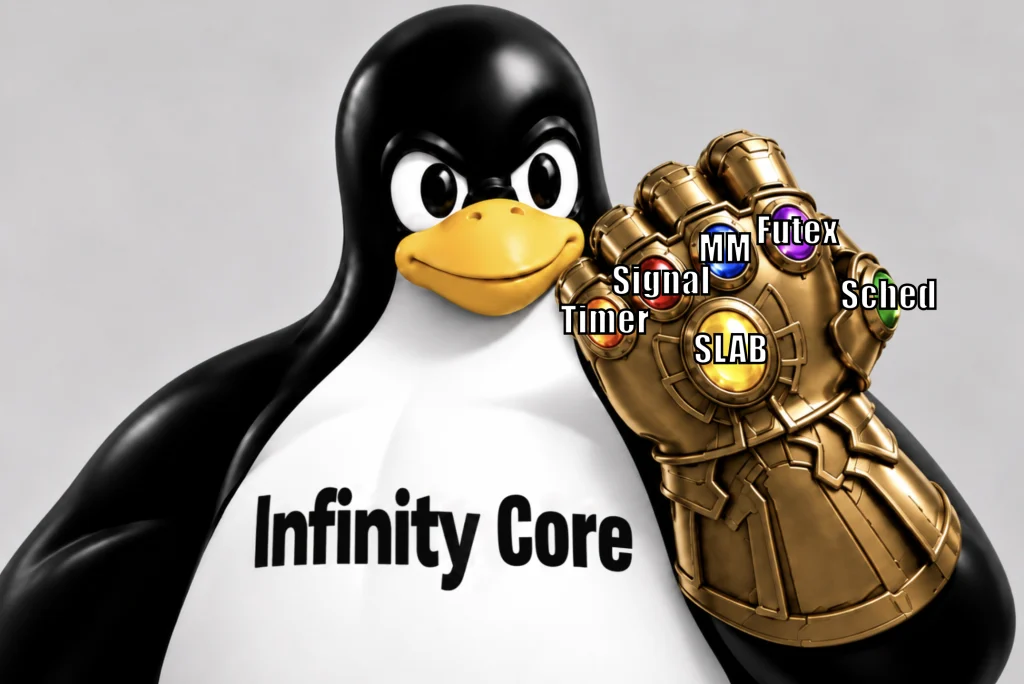
Researcher Hyunwoo Kim has published full details and proof-of-concept exploits for six Linux kernel vulnerabilities he calls “Infinity Core.” Five of them lead to local privilege escalation and container escape, and one crashes the kernel. Upstream fixes exist, so admins should install patched kernels now.
- Total: 6 CVEs
- Severity: 4 High · 2 Unrated
- Actively exploited: None confirmed
- Highest severity: 7.8 (High · CVSSv3) — CVE-2026-98260
- Action: Apply the latest security updates now
Notable CVEs
| CVE | CVSS (CVSSv3) | Type | Fixed in | Status |
|---|---|---|---|---|
| CVE-2026-98260 | 7.8 | exec: Cleanup POSIX timers right after de_thread() | 6f1977cea3e85cd8ab55fb337d3e1725fe61d1ce, d9ae467e617ca29b825493a362bf0d75ad5f4ac3, 75aa08b93c65766040f9ca99f41ac85ad22596b6 (+7) | Not exploited |
| CVE-2026-98256 | 7.8 | signal: Prevent exec() race | 621c365739828900f32a0c1cdfe5387528a62176, 934bd95f1a6404dbb845951b823547abab05a649, d2710c8d938ae6a825a6463158e6e6f31eac792a (+3) | Not exploited |
| CVE-2026-89754 | 7.8 | mm/pagewalk: fix stale walk->action escaping walk_pmd_range() | 895cd4ecbb2e03d7583103c65ee5adaae126ed6d, c05cdc2ab365b98099386e6c166b9865a4f2a9d3, aedf2efd18977e0cef7eb963166e2b1fcc0aa321 (+4) | Not exploited |
| CVE-2026-97941 | 7.8 | mm/slab: take n->list_lock in __slab_try_return_freelist() to avoid race | 570a6aaf6b52c6ec098f4811cdb52b1496f13d15, 4a724bcf5d703e18957397914d79156fa2cf1174, 7.2.7 (+1) | Not exploited |
| CVE-2026-80775 | Awaiting analysis | futex: Fix race on the initial mm->futex.phash.ref allocation | 86d12b34bafc9a4c271a9edefea88855a934d6e5, ff252ed45c8263525f2f54d81c5fa6d547fba344, c4b4972d8edcdf50b6518f55119e129d2f668a10 (+5) | Not exploited |
| CVE-2026-98385 | Awaiting analysis | sched/cache: Decouple sched_cache_group from mm to fix UAF | 852ecb6bc0bc0106f44f74ba3944524732486025, 28f9c0e0a0b94c5d3e1b634db545f6e1f94858c5, 7.2.9 (+1) | Not exploited |
Why It Matters
These bugs sit in core kernel code: timers, signals, memory management, futex, the scheduler and the SLAB allocator. Kim notes that these areas “have historically seen relatively few security issues.” In addition, his research excludes noisier areas such as networking, BPF and bugs that need a user namespace.
That makes the set more dangerous. Most hardening guides restrict user namespaces or BPF to shrink the attack surface. However, those controls do not block these flaws. Any local user, or code inside a container, could reach them. On shared hosts, that means one compromised container could become a full host takeover. For cloud providers and Kubernetes clusters, these Linux kernel vulnerabilities turn a small foothold into privilege escalation across every workload on the node.
Exploit details are now public
Kim reported the flaws to the linux-distros list under embargo. Once the embargo ended, he posted the details to oss-security and released the Infinity Core write-up and PoC exploits on GitHub. According to the write-up, the public PoCs turn five of the Linux kernel vulnerabilities into a root shell from an unprivileged account.
The timer flaw goes further. Kim says it can give “full root privileges” on a Samsung Galaxy S26 Ultra from a normal app sandbox. He has held back that Android exploit until Samsung patches its devices, publishing only a hash of it for now.
How the Attack Works
All six bugs are memory safety flaws triggered by races or edge cases in kernel code. An attacker needs local code execution first. From there, the bugs corrupt kernel memory, and the PoCs turn that corruption into root access.
- CVE-2026-98260 (Timer): a use-after-free when exec() fails in a multithreaded process with CPU timers.
- CVE-2026-98256 (Signal): a use-after-free from a race between exec() and signal queue cleanup.
- CVE-2026-89754 (MM): an out-of-bounds write in the page table walker used by mincore().
- CVE-2026-80775 (Futex): a use-after-free from a race in private futex hash setup.
- CVE-2026-98385 (Scheduler): a use-after-free in scheduler cache accounting. It only applies when the optional scheduler cache feature is built in and switched on.
- CVE-2026-97941 (SLAB): list corruption in the SLUB allocator. Its PoC causes a kernel panic, and Kim says no privilege escalation chain exists yet.
Exploitation status
Public PoC code exists for all six flaws. However, no source reports exploitation in the wild, and none of the CVEs appears in CISA’s KEV catalog.
Affected Versions
Kim tested the exploits on Ubuntu 26.04 (kernel 7.0.0-30-generic) and Arch Linux (7.2.4-arch1-2). The kernel CVE records list these fixed stable releases:
- CVE-2026-98260: affects kernels since 5.7. Fixed in 6.6.158, 6.12.112, 6.18.54 and 7.2.8.
- CVE-2026-98256: affects kernels since 6.15. Fixed in 6.18.54 and 7.2.8.
- CVE-2026-89754: affects 7.0 and some 6.18 and 6.19 backports. Fixed in 6.18.50 and 7.2.4.
- CVE-2026-80775: affects kernels since 6.17. Fixed in 6.18.47, 7.1.11 and 7.2.1.
- CVE-2026-98385: affects 7.2. Fixed in 7.2.9.
- CVE-2026-97941: affects 7.2. Fixed in 7.2.7.
Patch and Mitigation Steps
- Install your distribution’s latest kernel update and reboot.
- Prioritize multi-tenant hosts, container nodes and shared build servers.
- Check that your vendor kernel includes the fix commits, since backports vary.
- Android users should apply Samsung’s security updates once they ship.
Coverage on freenode warns that container, multi-tenant and Android builds that lag upstream face the most exposure. With working exploits public, these Linux kernel vulnerabilities should move to the top of the patch queue.
Support Our Threat Intelligence
Find our vulnerability reports and weekly recaps helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
