 Do Son
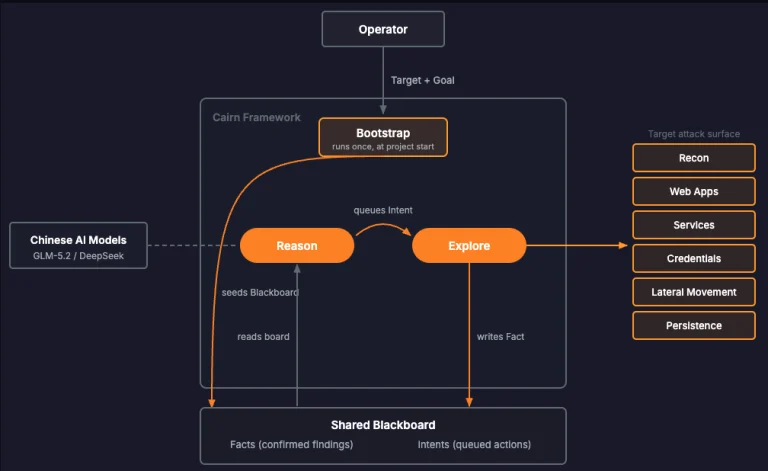
Unit 42 uncovered the Cairn framework CL-STA-1238 campaign using DeepSeek and Zhipu GLM models to autonomously breach 10 organizations.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.
A widespread DarkSword iOS malvertising campaign compromised NextDay Media ad tags across Dutch and Belgian sites, targeting unpatched iPhones.
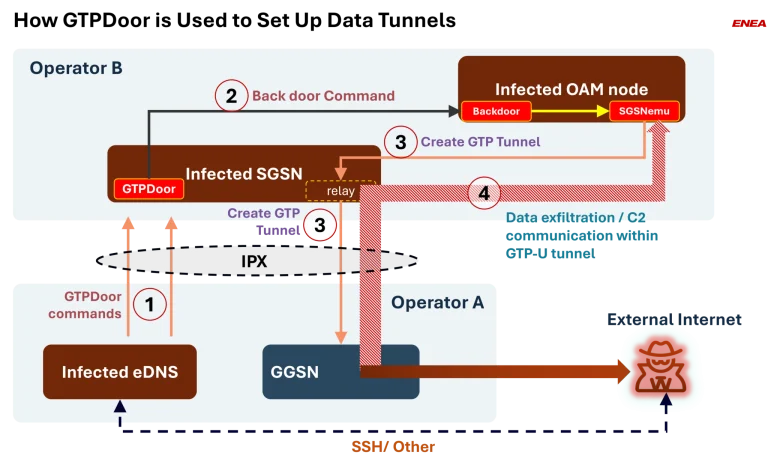
Enea exposed LIMINAL PANDA SilentAir GTPDoor v3 and SS7 signaling attacks compromising mobile operators to intercept 2FA codes in Taiwan and Asia.
A mysterious Bitly link hijack repurposed dormant URLs from Trump, McDonald's, and Burger King posts since 2009 into unrelated Wikipedia pages.
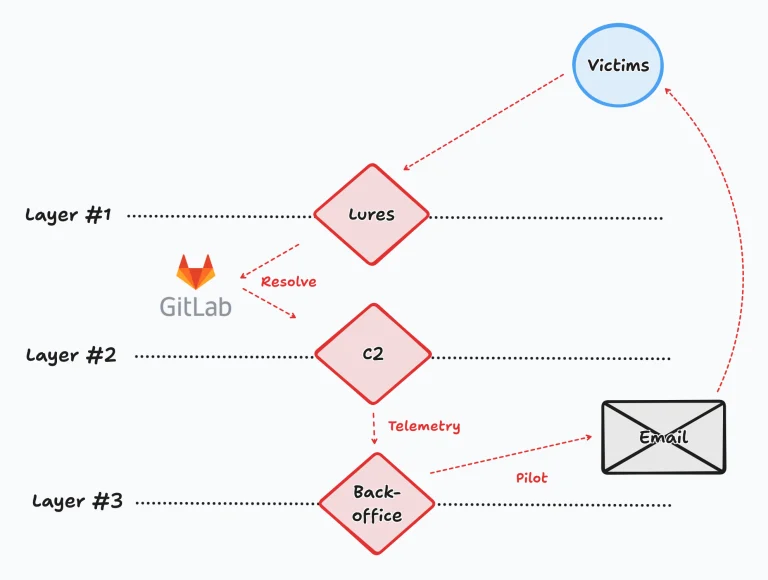
Stormshield exposed the North Korean Trigram campaign spoofing 50 Web3 and AI brands with ClickFix lures and GitLab relays to infect developers.
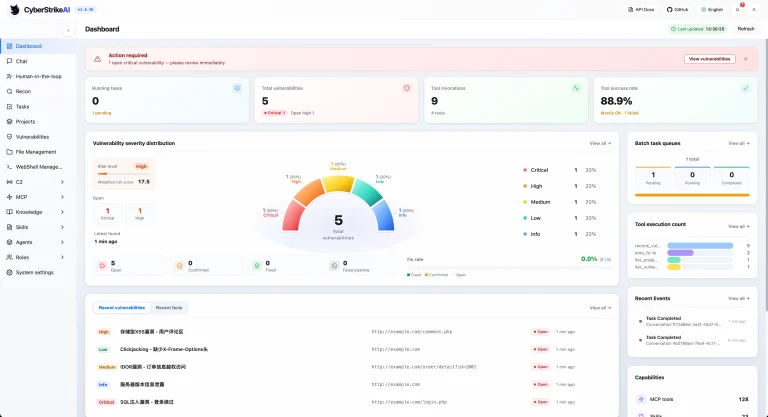
Elastic Security Labs uncovered a CyberStrikeAI AWS intrusion and CyberStrikeAI AWS CloudTrail intrusion that pulled 56 EC2 scripts in 141 milliseconds.
Wiz, Sentra, and Mandiant uncovered a supply chain attack abusing Qubole cross-account access and Qubole AWS cross-account access roles to steal S3 data.
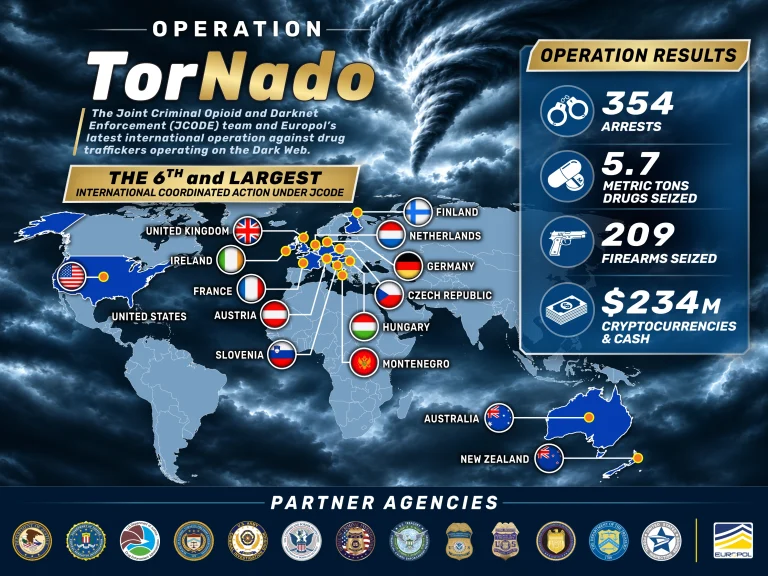
The DOJ and Europol arrested 354 suspects and seized $234M in the Operation TorNado dark web crackdown on fentanyl and opioid vendors.
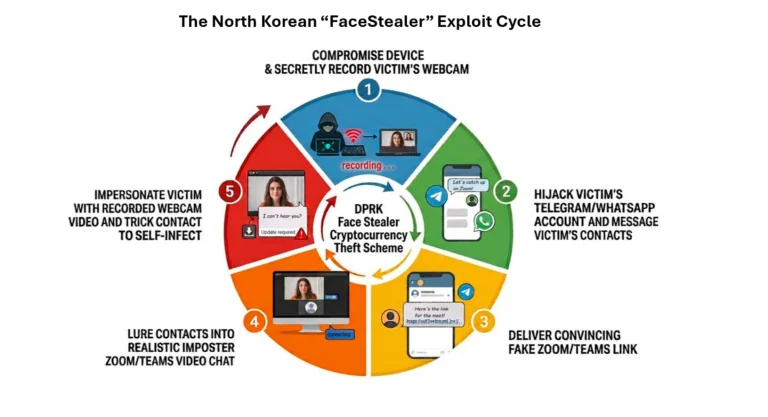
The DOJ and FBI disrupted the North Korea FaceStealer scheme after $400M in crypto thefts and seized $1.2B stolen in a $6B Binance exchange hack.
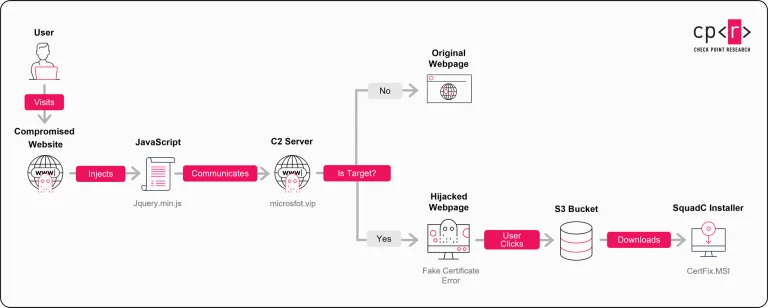
Check Point Research exposed the CopperDragon Sparrow framework malware ecosystem supplying China-nexus espionage clusters across three continents.
ConnectWise disabled five ScreenConnect extensions in 400 environments after attackers accessed ScreenConnect partner accounts. Act now.
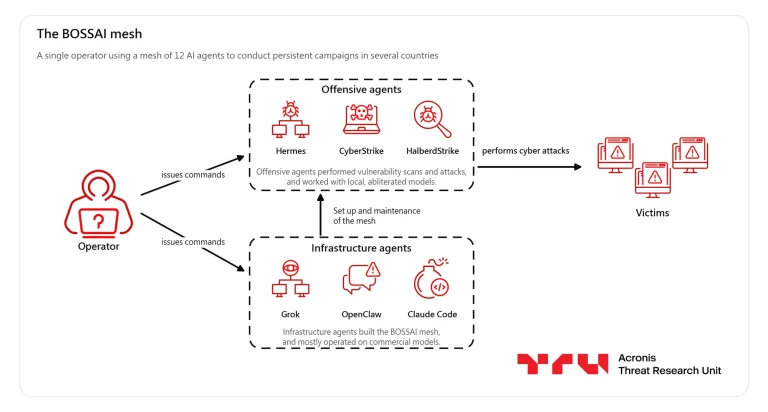
Acronis TRU uncovered the BOSSAI attack mesh Taiwan campaign using 12 AI agents to breach emergency services, banks, and universities in 11 countries.
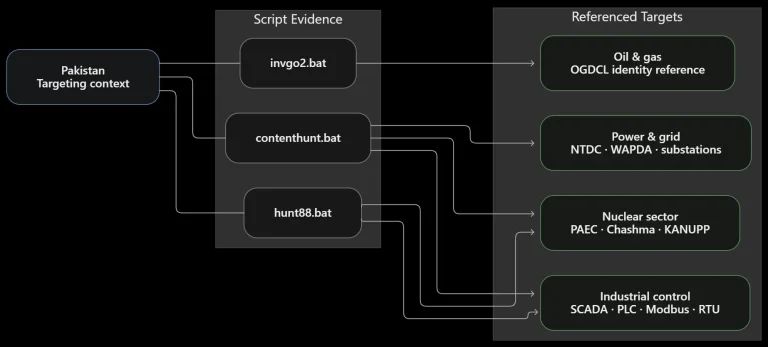
Researchers found an open server hosting a DoNot APT toolkit targeting Pakistan nuclear, power grid, and ICS networks with Inveigh and Go shells.
A French blood bank cyberattack targeted EFS plasma refrigeration units, altering temperature thresholds before emergency alarms prevented product loss.

Sekoia uncovered an APT29 watering hole campaign mobile exploits operation using Plerdy analytics and watering holes to compromise unpatched phones.
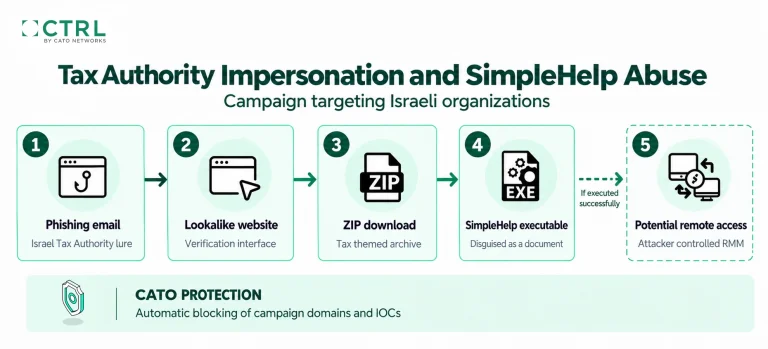
Cato CTRL exposed the MuddyWater SimpleHelp campaign in Israel using tax lures. Learn how the MuddyWater SimpleHelp campaign abuses RMM tools.
A vague mSecure security notification warns users to rotate credentials, reset two-factor keys, and revoke passkeys following suspicious service activity.

Mandiant warns that enterprise LLMJacking cloud attacks drain API quotas. Attackers use LLMJacking cloud attacks to resell access via illicit mixer portals.
The VULONE Team reveals that the Kimsuky Operation GitPower campaign remains live on GitHub, with Operation GitPower repos staging AnyDesk malware.
The Binance hack hit USD 6.34B via a fake job interview, an abused AI tool and EIP-7702 delegation. The FBI points to North Korea.
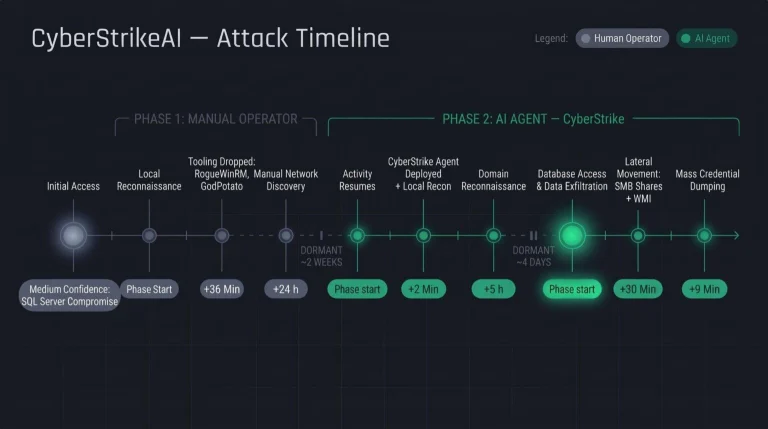
Kaspersky uncovered CyberStrikeAI framework attacks using AI to automate post-exploitation and compromise domains across education networks.
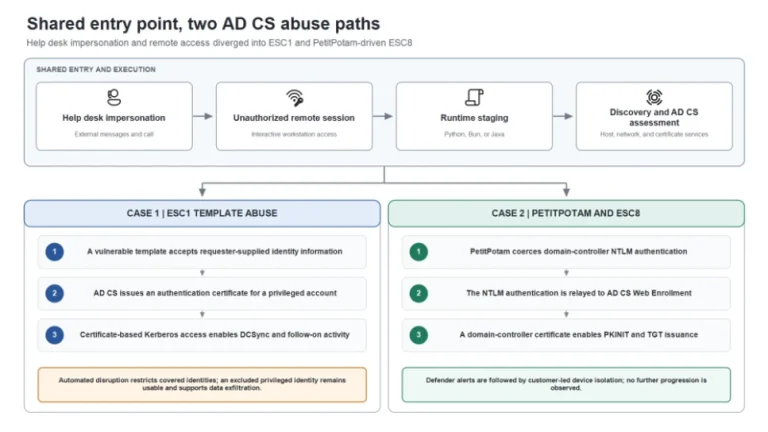
Microsoft details help desk impersonation on Teams that led to AD CS abuse via ESC1 and ESC8, giving attackers privileged certificates.