 Do Son
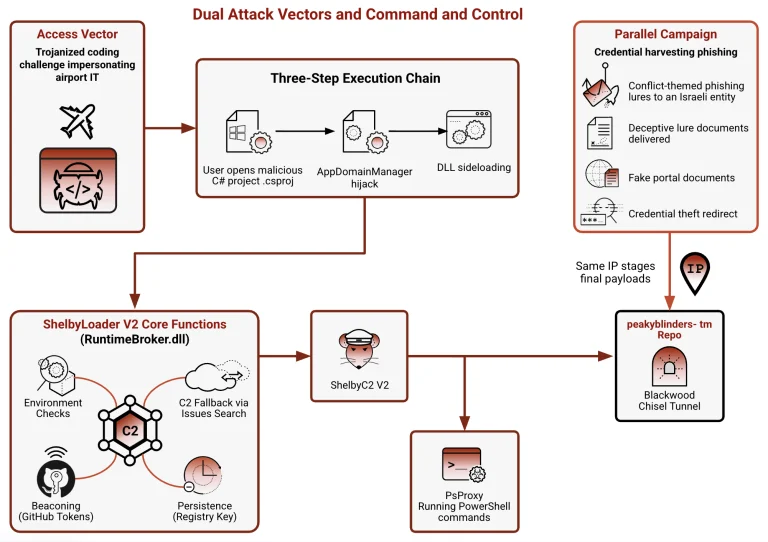
The Blinder Tunnel campaign used a fake Dubai Airports coding test to drop ShelbyLoader V2 on an Iraqi target. See how it works and how to defend.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.
A ccTLD registry hijack of .gh, .sl, and .as let attackers obtain rogue TLS certificates. See how Chrome responded and how to check yours.
A ShinyHunters hacker arrest in Jordan may aid the FBI, as an alleged member reportedly shares devices and chats. Here is what we know.
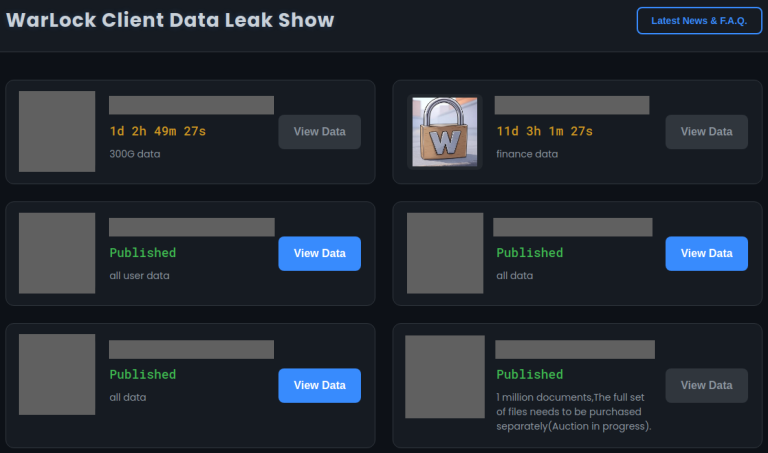
The Warlock ransomware group still exploits SharePoint vulnerabilities, hitting a water utility, a telecom firm, and more. Here is how to defend.
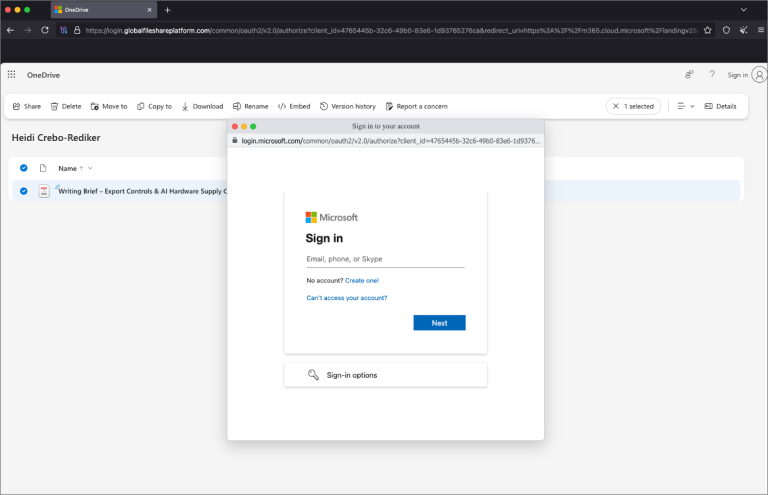
Proofpoint exposed China-aligned TA419 credential phishing targeting AI experts. This TA419 credential phishing campaign uses AitM lures to steal logins.
A new campaign shows how phishing abuses RMM tools for access. See how phishing abuses RMM tools like MSP360 to install ScreenConnect clients.
Attackers exploit Citrix NetScaler zero-day CVE-2026-88772 for root access, then hide WHIPSHOT web shells and a SLAPSHOT tunneler. Patch now.
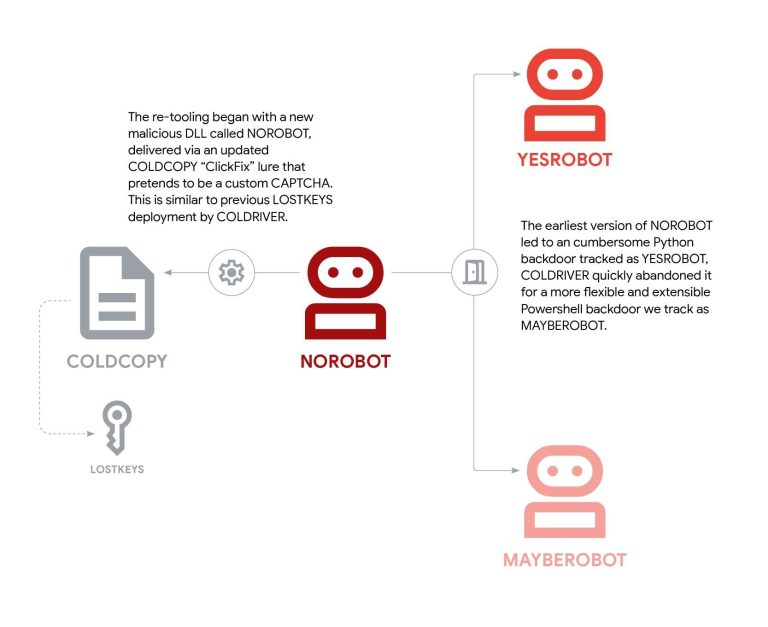
Star Blizzard RedFlick phishing hit 100+ groups that back Ukraine, using scheduled tasks to drop the CosmicPulse backdoor after a single click.
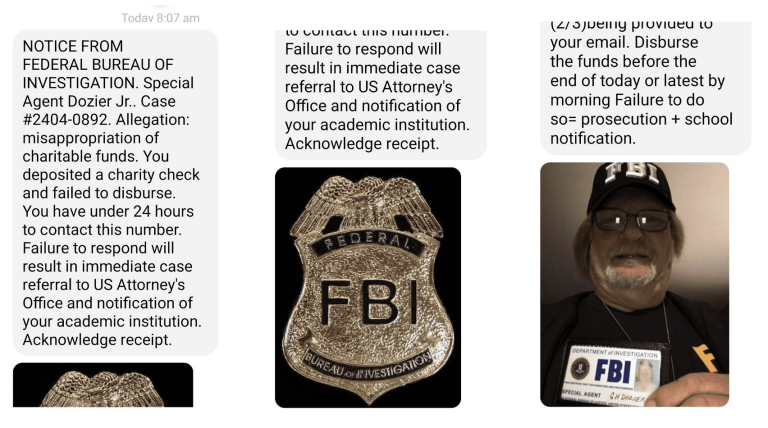
University job scams are spreading through .edu account takeover. Proofpoint shows how fraudsters phish logins, then send fake jobs and bogus checks.
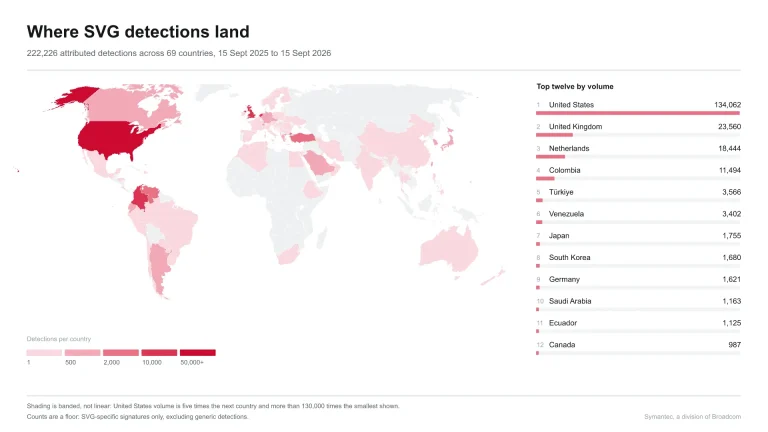
SVG phishing attacks jumped in August 2026. Symantec explains how SVG smuggling hides fake logins and malware inside image files, and how to stop it.
Microsoft ties a JADEPUFFER Azure attack to Storm-3168, the agentic ransomware actor that tried to delete 100+ storage accounts in seven minutes.
ShinyHunters PeopleSoft attacks are back. A one-letter WAF bypass lets the group exploit CVE-2026-35273 and plant web shells on unpatched servers.
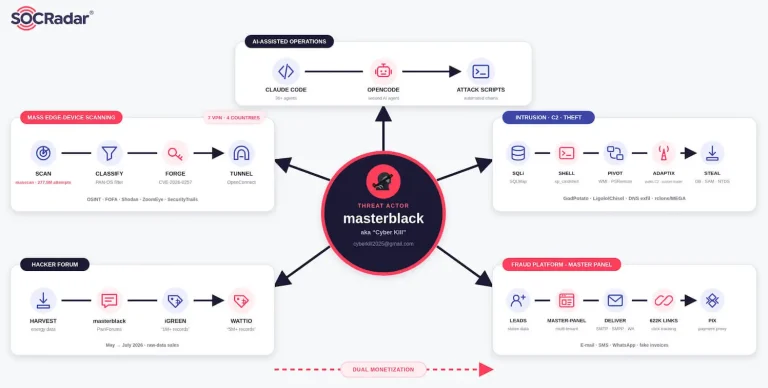
Operation Master used a GlobalProtect flaw to steal utility data, then fed it into an invoice fraud platform that sent 2.4M+ fake bills in Brazil.
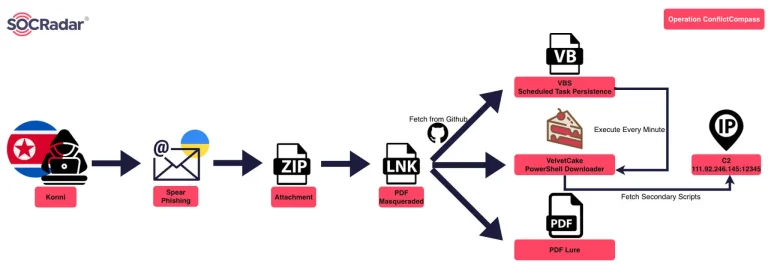
SOCRadar uncovered the Konni Operation Conflict Compass campaign targeting Ukraine. Learn how Operation Conflict Compass uses fake PDFs and VelvetCake.
Learn why Kiteworks issued a mandatory precautionary server shutdown over an unconfirmed zero-day threat following warnings from federal authorities.

SentinelOne discovered how new TraderTraitor macOS backdoors hit IT firms. Learn how TraderTraitor macOS backdoors use weaponized Terraform files.

A new TeamFiltration password spray campaign targeted Chilean firms. Learn how this TeamFiltration password spray compromised dormant cloud accounts.
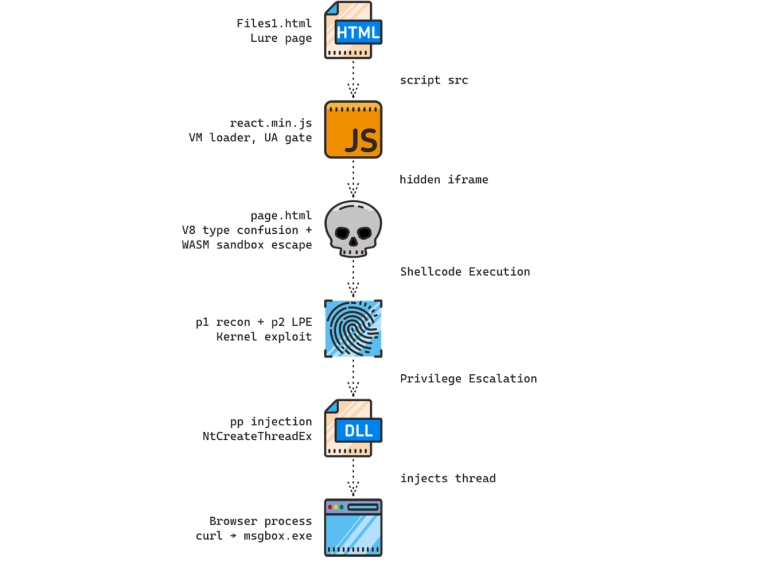
Chinese UTA0565 zero-day exploits strike global targets. Learn how the UTA0565 zero-day exploits deploy CLEANGULP malware.
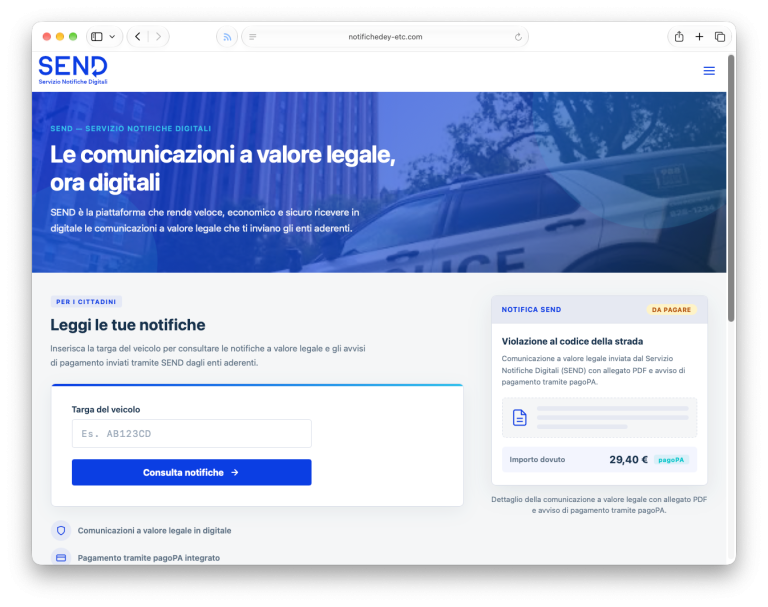
Learn about the new Italian phishing campaign delivering an iOS exploit chain. This Italian phishing campaign targets outdated iPhones using fake SEND portals.
The SideCopy APT campaign deploys custom RATs. Learn how the SideCopy APT campaign malware exploits mshta to target academic and government networks.
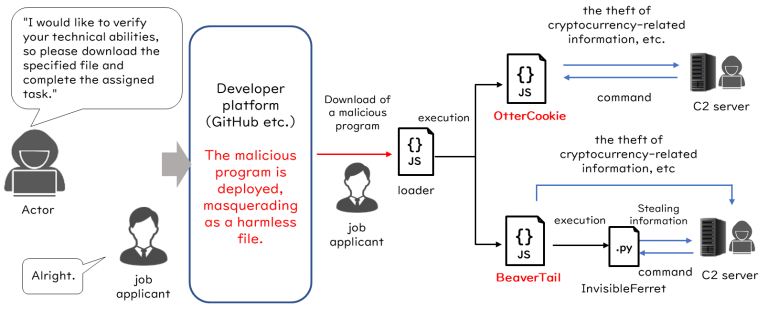
Discover how the North Korean WaterPlum cyber actor group uses fake job interviews to steal crypto and infiltrate networks globally.
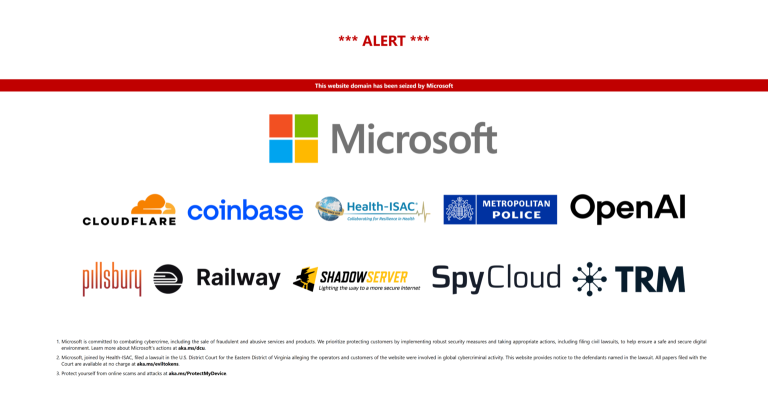
Microsoft led a coalition disrupting EvilTokens cybercrime platform. Learn how the EvilTokens cybercrime platform used AI and device code phishing.