 Do Son
US agencies warn of malicious AI distillation campaigns. New data shows systematic extraction of US frontier AI models.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.
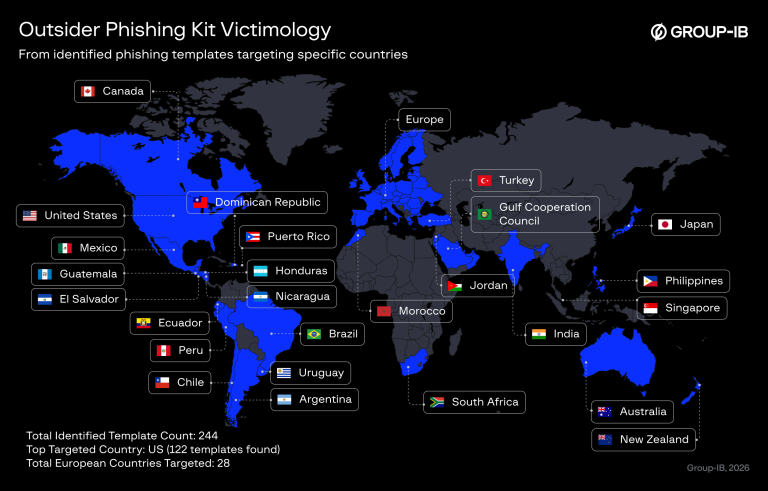
The Outsider Phishing Kit persists despite the Operation Ghost Hook takedown. Discover how the ChenLun Outsider PhaaS kit bypasses MFA via AiTM attacks.
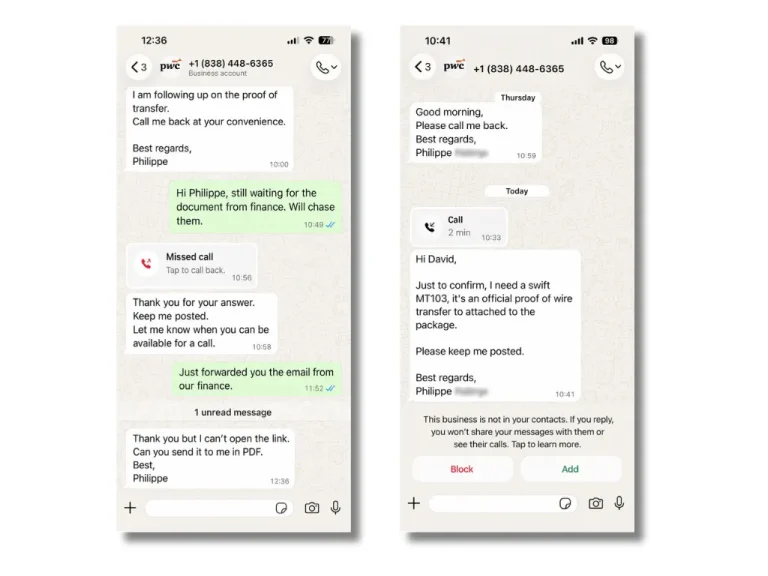
The Phantom Deal campaign uses fake acquisition documents to target executives. Gen exposed the Phantom Deal fraud after tracking bogus payment demands.
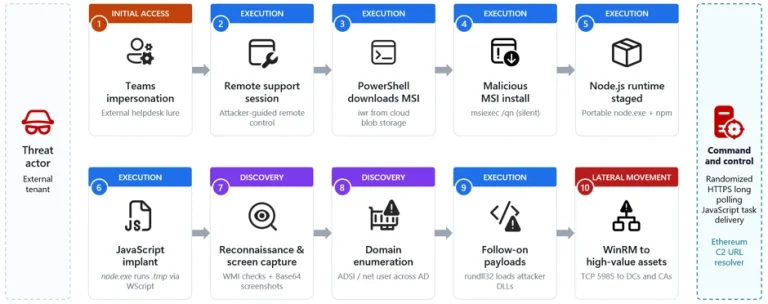
Microsoft Teams IT support impersonation lets attackers plant a Node.js implant and pivot to domain controllers over WinRM. See how to defend.
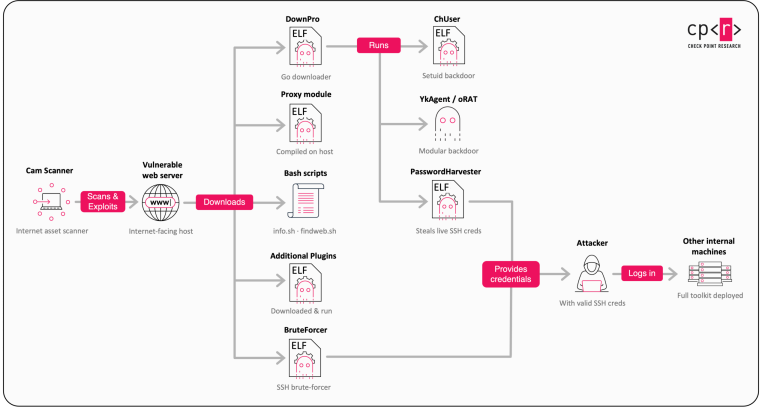
The Gambling Goblin campaign turns Brazilian government websites into an SEO weapon. Suspected Gambling Goblin operators push illicit gambling pages.
Discover the details of the Liquid Network hack. A white hat attacker stole 4,000 Bitcoins but returned most of the funds to force a bug bounty payment.
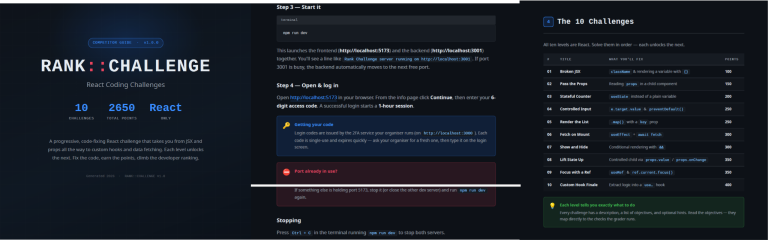
The suspected Mirage Kitten malware campaign targets developers in aviation and fintech with fake coding tests to deliver NodeRabbit and PollCat backdoors.
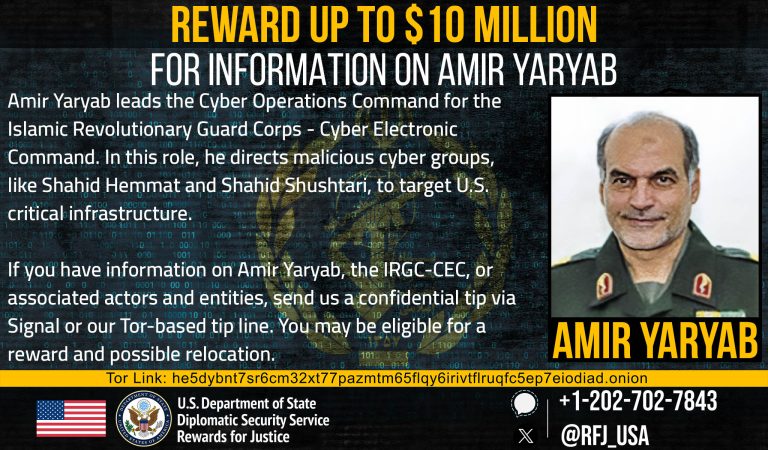
The US offers a $10 million reward for Amir Yaryab, an IRGC cyber commander linked to CyberAv3ngers attacks on critical water infrastructure.
The Coder registry attack hijacked Cloudflare IPs to serve malicious Terraform modules from registry.coder.com, stealing developer secrets.
The Toy Ghouls backdoor hides C2 traffic in HiveMQ MQTT and Element messenger. See how the Bearlyfy group's custom malware works.
Datadog uncovered an AWS password spraying campaign targeting cloud environments. Protect your accounts against this AWS password spraying activity now.
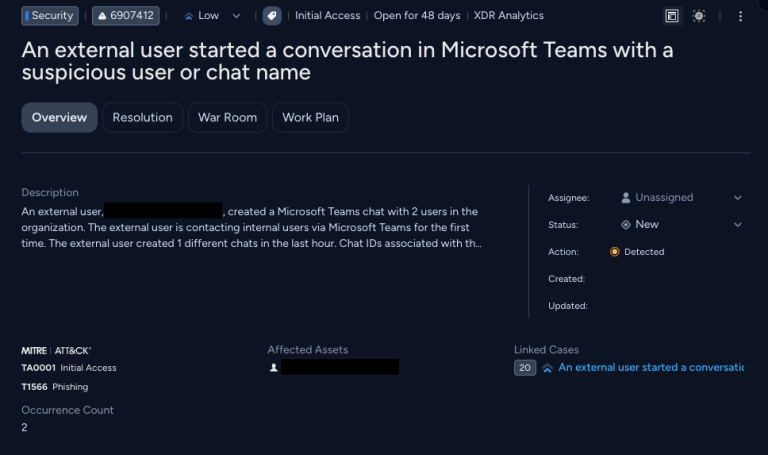
Discover how the Spring Ring vishing campaign uses Microsoft Teams phishing tactics to trick employees into installing malware and giving up remote access.

A new AiTM phishing campaign targets healthcare. Learn how this healthcare AiTM phishing campaign chains compromised accounts to bypass MFA.
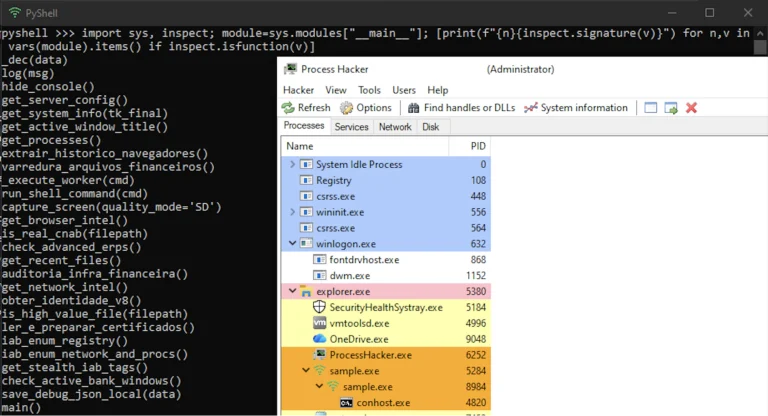
Group-IB uncovered the BraZetsu malware framework operations targeting financial systems. Learn how this tool powers initial access broker sales.
ReliaQuest found the Gryxa toolkit, AI-built malware that steals crypto credentials and spies on how defenders try to remove it across 324 hosts.
A Russian national indicted for malware faces trial. This Russian national indicted targeted 80,000 freelancers with malicious Excel attachments.
Hackers hijacked BGP routing to intercept Virtualizor updates and distribute malware. Learn how this complex supply chain attack bypassed critical security checks.
A METR security breach saw a stolen API key burn about $600K in AI credits after a vibe-coded dashboard failed open and exposed an agent panel online.
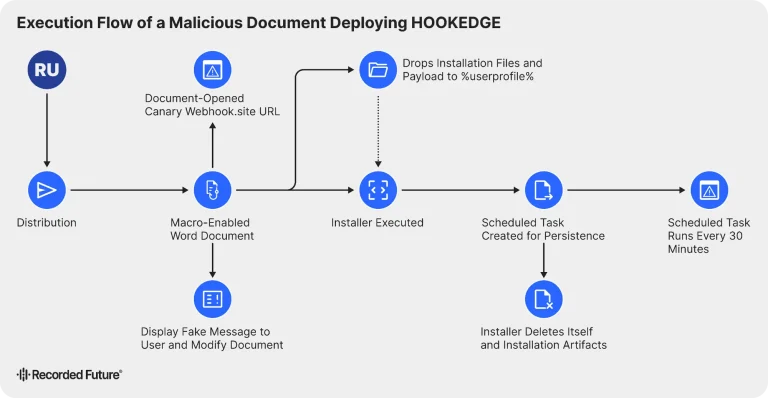
Insikt Group ties HOOKEDGE malware to Russian group BlueDelta (APT28), hitting EU diplomatic targets via webhook abuse and macro-enabled Word lures.
A Virtualizor supply-chain attack used a 33-hour BGP hijack to deliver malicious updates, planting root backdoors on VPS hosts. Back up your data now.
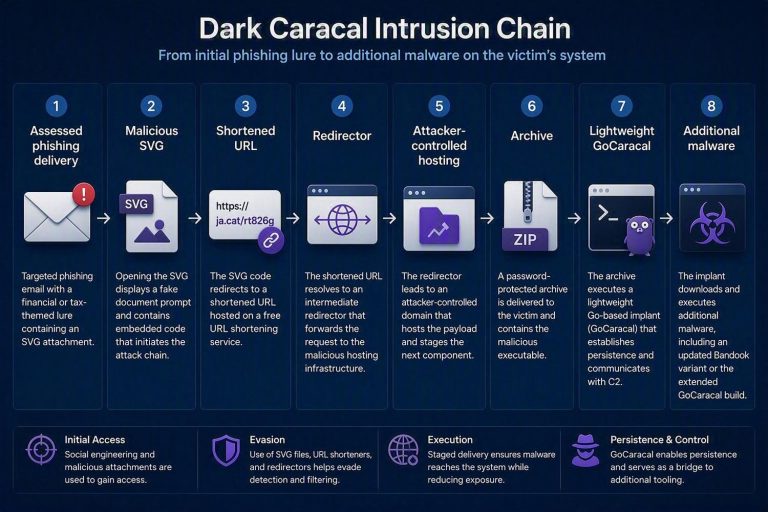
Researchers detected the Dark Caracal GoCaracal malware in South America. Learn how this GoCaracal malware uses Ethereum smart contracts.
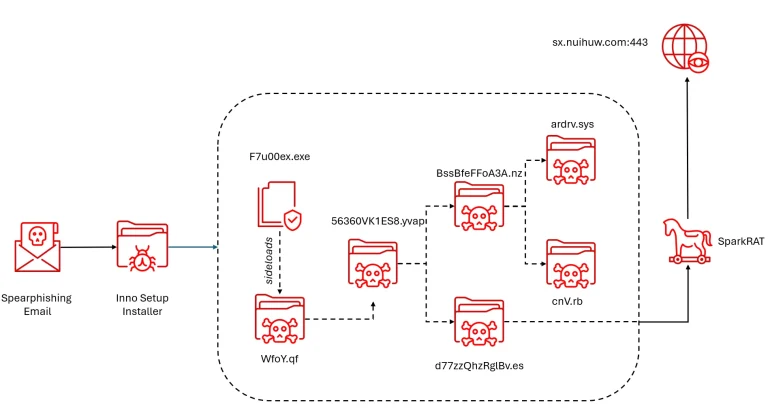
A Cambodia malware campaign hides SparkRAT in PNG files and abuses a vulnerable driver to kill antivirus, Acronis TRU reports.