
 Do Son
APT28 used the Hookedge backdoor, SSH tunnels, and a new loader to spy on a naval shipbuilder and defense firms in two NATO countries.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.
A China-linked operator ran an AI-driven hacking campaign from one server, hitting ministries in Vietnam, Taiwan, Indonesia, and India.
In Operation FlashHole, the Lazarus Group used AI-made lure sites, CrossWeb EX, and GitHub C2 to spy on South Korean firms. Here is how.
Hackers abused a SkyKick API secret in a ConnectWise Cloud Backup breach, accessing 300+ Microsoft 365 tenants and planting rogue app credentials.
Ahold Delhaize cyberattack took brand sites offline in Europe and the US. Albert Heijn outage ends as the app returns; no data theft found yet.
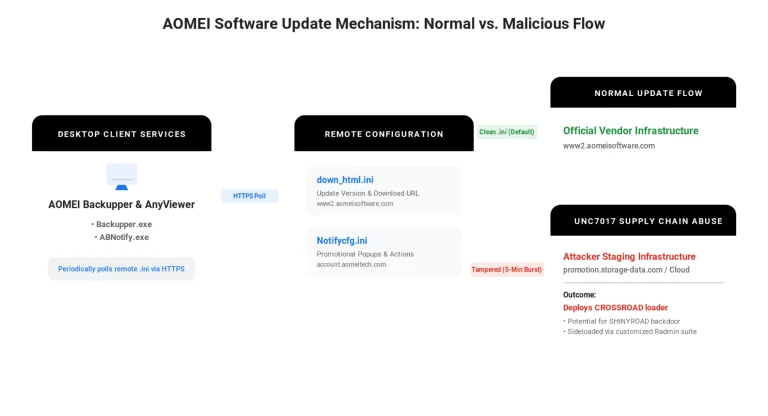
Google and Mandiant uncovered the AOMEI supply chain attack UNC7017 campaign using 5-minute server tampering to drop CROSSROAD and SHINYROAD malware.
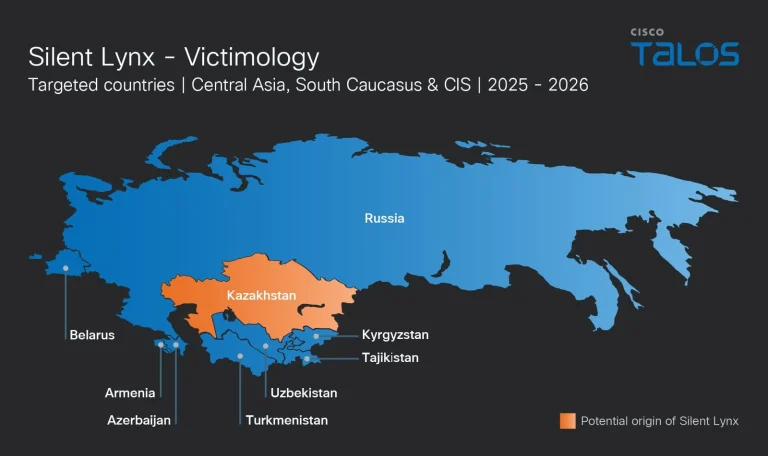
Cisco Talos and Recorded Future exposed the UAT-6275 threat actor targeting CIS governments with WinRAR exploits and custom reverse shells.
Microsoft and Proofpoint executed a CoGUI phishing kit takedown, seizing domains from YAM Store and Iron Man after 1B scam messages hit 75,000 firms.
A scam crackdown on West Africa scam centers by Meta, tech firms and police removed 3.7M accounts, led to 28 arrests and freed 117 victims.
DOJ officials announced an OpenAI recording device arrest after an engineer allegedly hid bugs in executive rooms. Read the case details.
The DOJ and FBI raided DPRK IT worker laptop farms in Texas, seizing 187 devices and charging 14 suspects in a $3M fraud scheme hitting 70+ US firms.
UTA0576 chained an Ivanti Connect Secure zero-day, CVE-2026-104935, with a root exploit to steal AD credentials. Patch now and check memory.
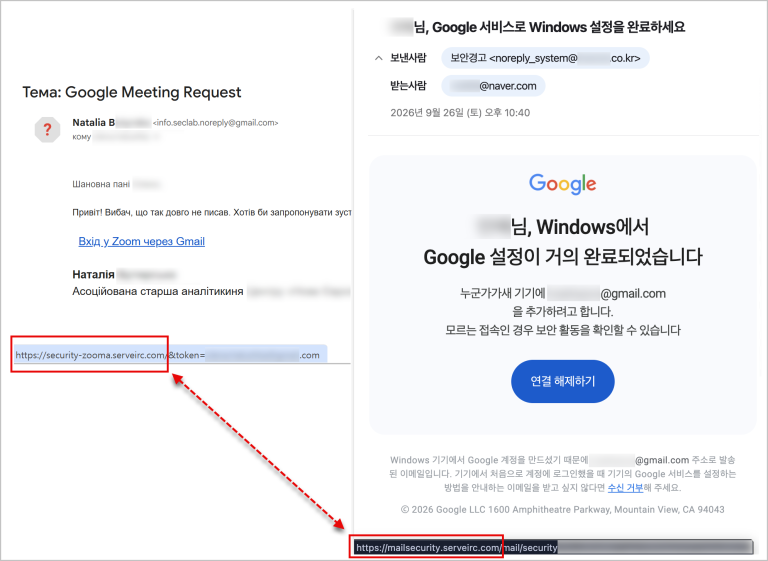
Kimsuky spear phishing lures target Ukrainian security experts with fake invitations, as Operation GitPower abuses GitHub and GitLab.
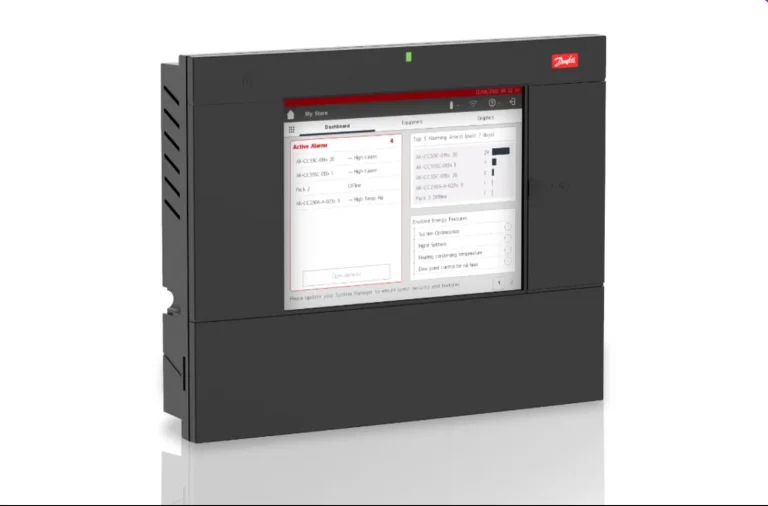
A massive French supermarket cyberattack targeted Danfoss refrigeration systems, causing catastrophic food spoilage and fires across 400 retail locations.
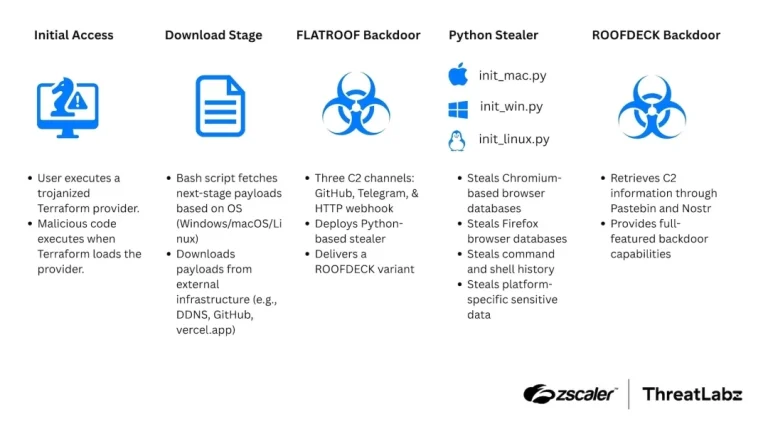
Suspected TraderTraitor hackers used a trojanized Terraform provider to drop FLATROOF and ROOFDECK malware on macOS, Linux, and Windows.
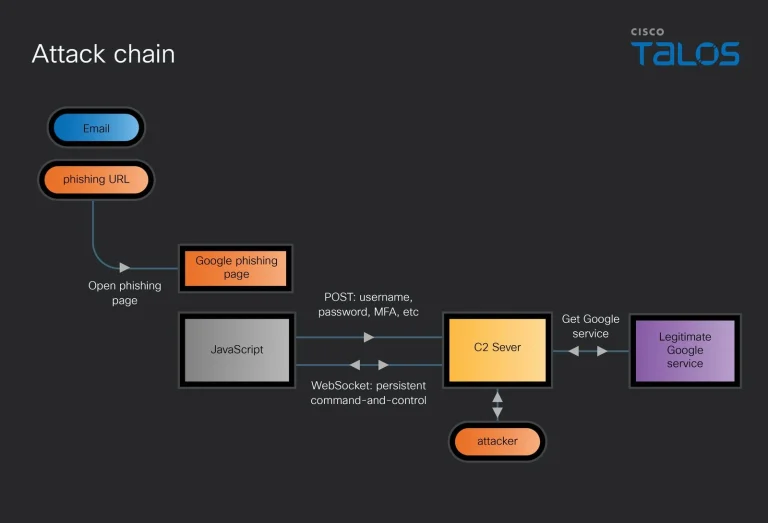
UAT-11985 used AI-written lures and an AitM phishing kit in a Taiwan spear-phishing campaign that steals Google logins and bypasses MFA.
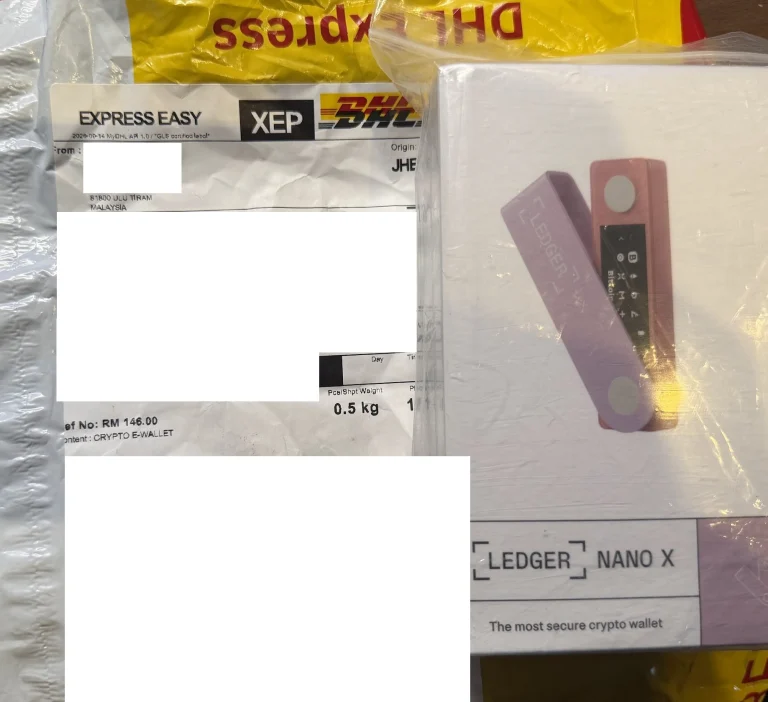
Discover details of the Ledger hardware wallet hack. Learn how hackers modified devices with spy modules to steal user seed phrases and $80 million in crypto.
Discover the MonsterCloud ransomware decryption fraud. Learn how Zohar Pinhasi allegedly deceived clients by secretly paying hackers for data recovery keys.
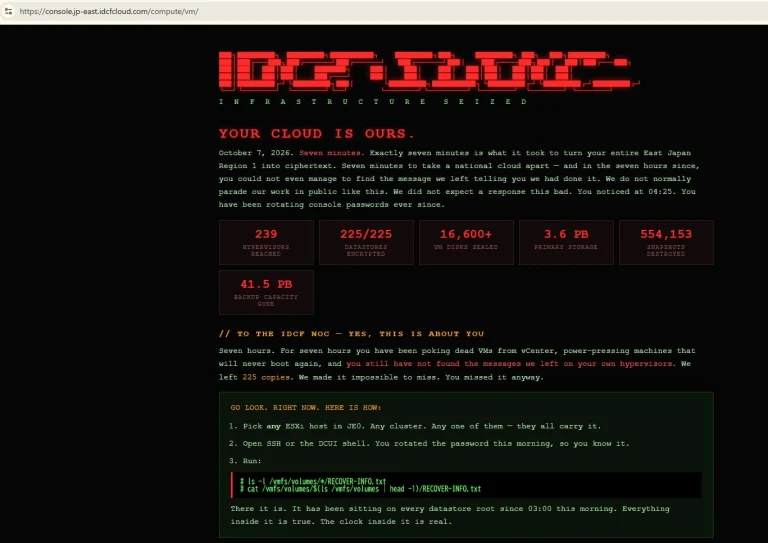
Explore the devastating SoftBank IDCF Cloud ransomware attack. Read the hackers' humiliating note revealing the massive East Japan Region 1 outage.
CrowdStrike links the ARTEX AI tool to breaches at South Korean banks, run by a suspected Chinese-speaking, profit-driven attacker.
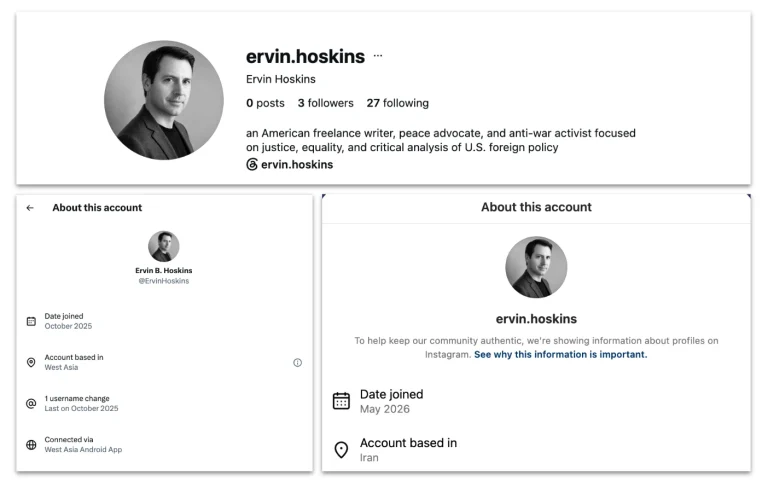
OpenAI disrupted state-backed AI false front operations. Threat actors ran covert false front operations using fake personas to manipulate global media.

Chinese state hackers allegedly use Integrity Technology Group tools for botnet data theft. Protect your networks from this massive cyberespionage campaign.