 Do Son
EclecticIQ report details Luna Moth's callback phishing attacks using legitimate RMM tools to breach US legal, financial firms for multi-million dollar ransoms.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.

PRODAFT report details Nebulous Mantis (Cuba/STORM-0978), a Russian-speaking group using RomCom RAT for espionage and ransomware.
Intrinsec reveals shared infrastructure between Eye Pyramid C2 and ransomware groups like Rhysida and Vice Society in new threat intelligence report.
Bitdefender uncovers a large network of convincing mystery box scams on social media stealing credit card data via hidden subscriptions. Watch out!

Commvault updates its March advisory after detecting nation-state threat activity in Azure; no data breach confirmed, advanced defenses deployed.

Proofpoint uncovers TA2900, a French-speaking BEC actor exploiting rental payments via fake IBANs and compromised education accounts to steal funds.
Infoblox uncovers $5.7B lost to investment scams in 2024, driven by RDGAs, DNS abuse, and fake profit platforms run by sophisticated threat actors.

SentinelOne reveals real-world attacks from DPRK, ransomware groups, and Chinese APTs, exposing evolving threats facing cybersecurity vendors in 2025.

A Nigerian national received a 97-month sentence for a $6M inheritance scam targeting over 400 victims, many elderly. Learn about this fraud.

A Nevada woman admitted guilt in a $15 million prize notice fraud scheme targeting thousands, especially the elderly. Learn about this deceptive scam.
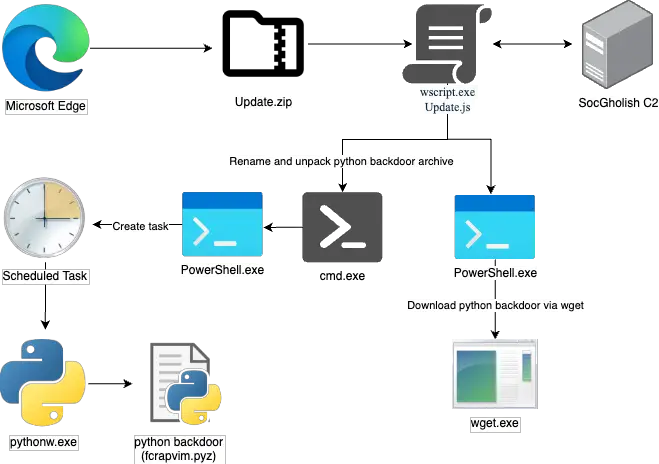
eSentire TRU discovers a campaign combining SocGholish malware with RansomHub affiliates, using fake updates and Python backdoors to compromise networks.

DeviceCodePhishing exploits OAuth Device Code Flow to bypass MFA and FIDO protections, redirecting victims to real sites with no phishing signs.

Silent Push uncovers Lazarus Group's campaign using fake crypto job offers to spread malware (BeaverTail, InvisibleFerret, OtterCookie), targeting job seekers.

Discover SessionShark, a sophisticated phishing toolkit designed to bypass Microsoft Office 365 multi-factor authentication by stealing session tokens.
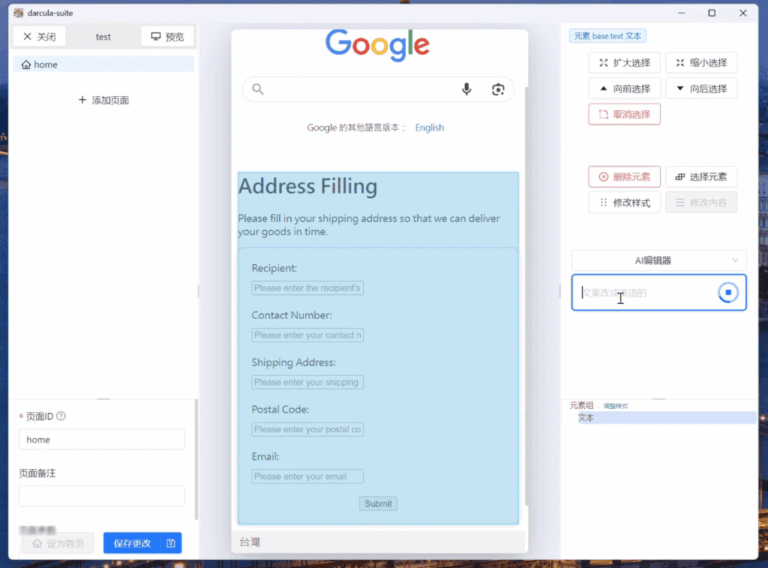
Darcula-Suite integrates AI to supercharge phishing-as-a-service operations, enabling faster, scalable, and more convincing phishing campaigns worldwide.
Report details how North Korean operatives use AI to create fake personas and infiltrate tech companies, funneling funds to the DPRK regime.

Trend Micro reveals how Russian IP networks support North Korea’s cybercrime—from crypto theft to malware-laced fake job interviews and potential espionage.
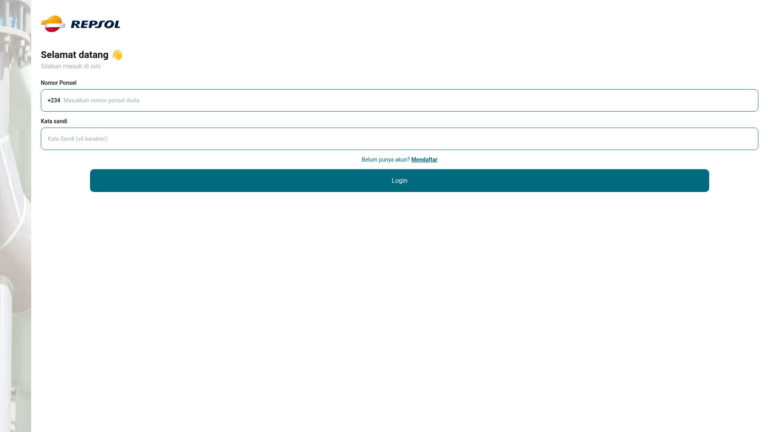
Power Parasites targets users with job and investment scams using fake domains mimicking Siemens, Repsol, Netflix, and more, Silent Push reports.

A new phishing campaign targets WooCommerce users with fake security alerts. Learn how attackers use IDN homographs and malicious plugins to compromise stores.

Kimsuky revives PebbleDash malware using spear-phishing and patched RDP DLLs for stealthy access and control, warns new ASEC March 2025 report.

Cisco Talos uncovers ToyMaker's IAB activity, paving the way for Cactus ransomware. Learn how LAGTOY backdoor & credential theft led to a major breach.

Resecurity uncovers massive NFC fraud wave using Ghost Tap attacks, with Chinese cybercriminals targeting global payment systems and loyalty programs.