
 Do Son
ViciousTrap is hijacking over 5,000 SOHO routers to build a distributed honeypot-like surveillance network, exploiting Cisco flaws for covert observation.
Cybercriminals
Cybercrime news focused on the people and groups behind attacks. This section profiles ransomware gangs, state-backed APT groups, initial access brokers and fraud operations, and follows the tools and tactics they use. You will also find reports on arrests, indictments, sanctions and law enforcement takedowns of criminal infrastructure around the world.

The U.S. Department of Justice charged 16 individuals for the $50M DanaBot malware operation, which infected over 300,000 computers worldwide.

Europol and Microsoft led Operation Endgame, a global takedown disrupting 300+ servers and 650 malicious domains linked to major ransomware malware strains.

Global operation neutralizes Lumma Stealer, infecting hundreds of thousands of PCs. Europol & Microsoft seized over 1,300 malicious domains.
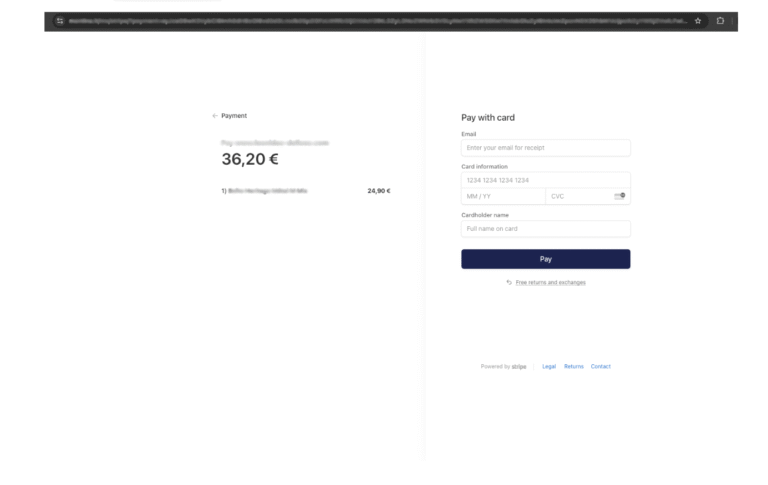
Attackers exploit JSONP flaws in Google APIs to inject malicious scripts into e-commerce sites, silently redirecting users to fake payment pages.

Hazy Hawk is exploiting DNS misconfigurations and CNAME hijacking to take over subdomains of high-profile organizations for scams and malware.

Beware fake Kling AI sites! A new campaign uses deceptive filenames to trick users into downloading infostealers, stealing crypto and browser data.

A sophisticated North Korea-linked employment scam, the Saja Network, is using fake developer profiles to infiltrate tech companies.

Phishing campaign uses deceptive domains to target Kuwaiti sectors. Details on how attackers impersonate brands and steal credentials.

An Alabama man faces prison for a brazen SIM swap attack that hijacked the SEC's X account, falsely announcing a Bitcoin ETF and crashing crypto markets.

Hackers exploited GovDelivery to send fake TxTag toll emails via Indiana government accounts. Learn how the phishing scam unfolded and how to stay protected.

Horabot malware targets Latin America with fake invoices, hijacking Outlook to spread phishing emails and steal data via stealthy scripting.

Europol-backed operation busts €3M investment fraud network deceiving 100+ victims via fake trading platform. Arrests made in Cyprus, Israel, Albania.

Dior notified customers in China of a data breach. Learn what customer information was accessed and what steps Dior is taking to address the incident

Attackers exploit fake AI video tools to deploy Noodlophile Stealer and XWorm, stealing credentials and data via Telegram bots.
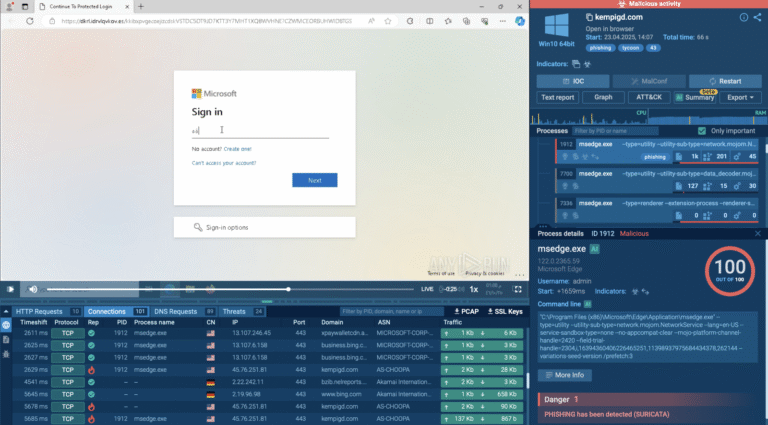
Explore the vulnerabilities in multi-factor authentication and effective strategies to prevent attackers from bypassing it.

A massive, long-running proxy botnet using outdated IoT devices for criminal anonymity has been dismantled in a global law enforcement operation.

Massive FreeDrain crypto phishing campaign uses Google SEO and free hosting to steal wallets. Trezor, Ledger users beware!

New email campaign uses tricky tactics and legitimate services to deliver the RATty Trojan in Spain, Italy, and Portugal. Stay alert for invoice scams!

Watch out! Sophisticated Facebook ads lure crypto users to download malware via fake platforms and celebrity endorsements. Bitdefender warns of data theft.

Cisco Talos warns of a Brazil-focused spam campaign abusing legitimate remote access tools (N-able, PDQ) to gain full system control. Stay vigilant!

The DOJ unsealed charges against four foreign nationals and the FBI seized domains for the Anyproxy and 5socks botnets, used to hijack routers globally.