ViciousTrap: New Cyber-Espionage Group Hijacks Routers for Honeypot Surveillance
 Do Son
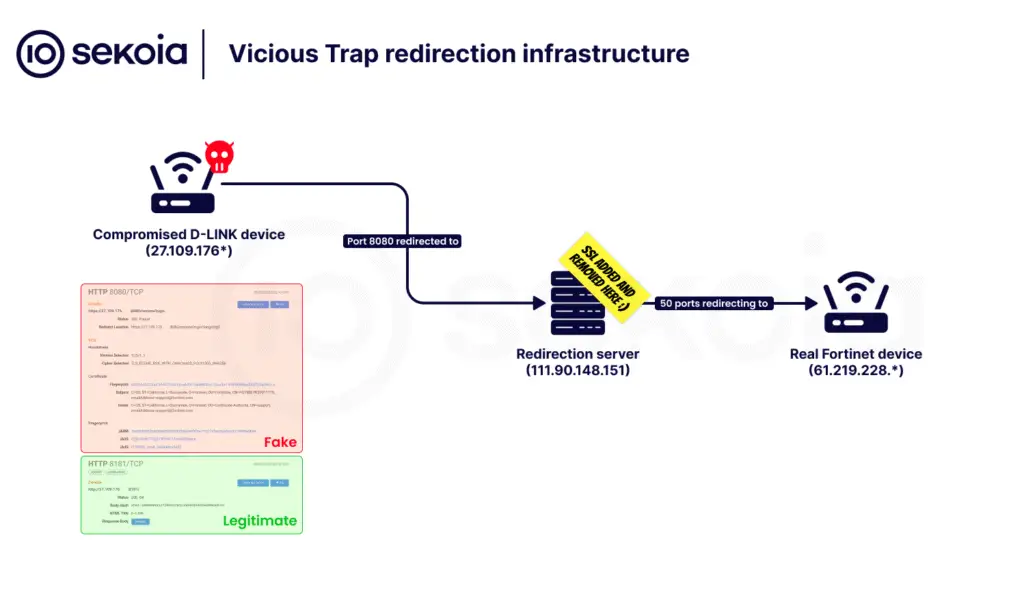
Image: Sekoia
Sekoia.io’s Threat Detection & Research (TDR) team has unveiled a novel adversary, dubbed “ViciousTrap”, that hijacks compromised SOHO routers to build a distributed honeypot-like surveillance network across Asia, Taiwan, and the U.S., with over 5,000 confirmed infections.
The actor’s campaign hinges on exploiting CVE-2023-20118, a critical vulnerability in Cisco SOHO routers, to deploy a redirection script named NetGhost. Once infected, devices silently reroute incoming network traffic to servers controlled by the attacker, allowing for man-in-the-middle (MitM) surveillance, traffic logging, and potentially the collection of zero-day exploitation attempts.
“The infection chain involves the execution of a shell script, dubbed NetGhost, which redirects incoming traffic from specific ports of the compromised router to a honeypot-like infrastructure under the attacker’s control,” Sekoia TDR reported.
According to telemetry from Sekoia’s honeypots, the campaign’s exploitation unfolds in a methodical, multi-stage script chain:
- Initial Exploit – The attacker uses CVE-2023-20118 to download a bash script via ftpget.
- Binary Deployment – A custom wget binary compiled for MIPS64 is manually installed to aid later communications.
- C2-Aware Script Retrieval – The attacker re-exploits the router to fetch a secondary script (main.sh) filtered by a UUID-based allowlist ensuring payloads only reach verified victims.
Once executed, the script wipes itself to evade detection, probes for open ports (80, 8000, 8080), and uses iptables to redirect traffic to a remote infrastructure.
“This malicious script, internally named NetGhost, is designed to redirect network traffic… effectively enabling Man-in-the-Middle (MitM) capabilities,” the report explains.
Unlike conventional botnets, ViciousTrap doesn’t primarily seek direct monetization via spam or DDoS. Instead, it seems to be constructing a decentralized observation network by:
- Repurposing end-of-life devices (e.g., Cisco RV042, D-LINK DIR-850L, ASUS routers) as passive interception nodes.
- Mimicking honeypot behavior by rerouting ports to attacker-controlled reverse proxies hosted at Malaysian provider Shinjiru (AS45839).
- Potentially collecting exploitation attempts or stolen data for reuse or sale.
Sekoia observed that “interactions on TDR’s honeypots revealed attempts by the attacker to reuse a previously documented web shell,” suggesting that ViciousTrap may be harvesting tools used by others in transit.
Using telemetry, port scans, and JARM fingerprinting, Sekoia confirmed that:
- Over 5,000 devices have been infected with NetGhost.
- More than 9,500 ASUS routers may have been compromised via CVE-2021-32030.
- Devices in Macao, Taiwan, and the U.S. are disproportionately affected.
- The attacker’s infrastructure includes 1,690 open ports on monitored servers and approximately 60 monitored device types, from DVRs to NAS and BMC controllers.
“We identified nearly 5300 unique compromised hosts… across 84 countries,” Sekoia confirmed.
The ViciousTrap campaign is a departure from typical IoT botnets. Instead of pushing malware, it silently listens—capturing live threat telemetry, stolen data, or unknown vulnerabilities.
“The redirection mechanism effectively positions the attacker as a silent observer,” Sekoia wrote. “This is the first time Sekoia.io has observed such activity, involving the transformation of compromised edge devices into potential relay nodes for a honeypot system.”
While attribution remains uncertain, Sekoia notes the deliberate exclusion of Chinese IPs from infections, suggesting a possible Chinese-speaking origin. The operation’s scale, technical discipline, and choice of EOL devices highlight the growing complexity of modern cyber threats—and the strategic role that router exploits now play in threat actor infrastructure.
Related Posts:
- New Cuttlefish Malware Evades Detection, Targets SOHO Routers
- France Leads International Effort to Eradicate PlugX Trojan from 3,000 Systems
- AVrecon RAT hidden in SOHO routers infected 70,000 devices in 20 countries in two years
- Interlock Ransomware Uses Evolving Tactics to Evade Detection
Support Our Threat Intelligence
Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!
 Buy Me a Coffee
