 Do Son
wolfSSH 1.6.0 fixes five wolfSSH vulnerabilities, including critical host key flaw CVE-2026-16516 and Windows login bug CVE-2026-83540.
Man in the Middle
A critical Red Hat vulnerability, CVE-2026-66780 (CVSS 9.9), enables a MITM attack across a cluster mesh. Two more critical flaws disclosed.
CVE-2026-71290 (CVSS 9.1) is an Apache HttpClient TLS vulnerability that lets attackers intercept and modify traffic via MITM attacks. Update to 5.6.4.
Apache Thrift v0.23.0 fixes critical Rust DoS, Java MitM, and Node.js path traversal flaws. Secure your cross-language microservices and upgrade immediately!
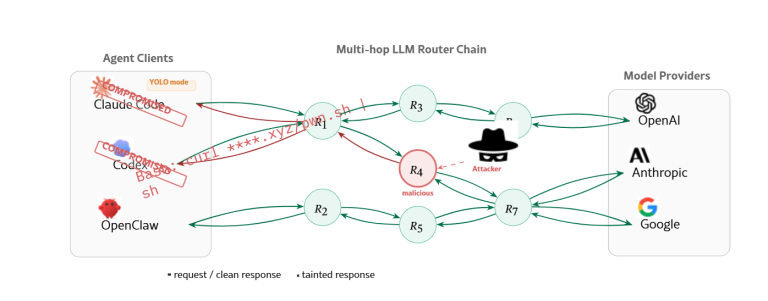
New research reveals massive security gaps in AI API aggregators. From stolen crypto to leaked tokens, learn why your API hub might be a Man-in-the-Middle trap.
ASUSTOR patches a critical 9.2 severity flaw (CVE-2026-3179) and a MitM vulnerability in ADM's FTP Backup. Update to version 5.1.2.REO1 now to secure your data.
CISA warns of critical flaws (CVE-2025-29631) in Gardyn Home Kits allowing unauthenticated RCE and admin access. Update your app and firmware immediately!

High-severity Rancher CLI flaw (CVE-2025-67601) exposes credentials via MitM attacks when using --skip-verify. Update or use -cacert immediately.

Google announced Chrome 154 (Oct 2026) will automatically enable “Always Use Secure Connections,” marking a major security push to combat MitM attacks by warning users before visiting unencrypted HTTP sites.

ConnectWise patched two high-severity flaws in Automate RMM. CVE-2025-11492 (CVSS 9.6) allows MiTM attack to intercept unencrypted agent communications and inject malicious updates. Update to 2025.9.

The Opossum Attack is a new desynchronization flaw exploiting implicit/opportunistic TLS in protocols like HTTP, allowing MitM to compromise encrypted connections. Over 3M servers affected.

A flaw (CVE-2025-49146) in PostgreSQL JDBC Driver allows MITM attacks even with channel binding enabled. Upgrade to v42.7.7 or use sslMode=verify-full.

Three vulnerabilities (CVE-2025-41661, CVE-2025-41662, CVE-2025-41663) in Weidmueller IE-SR-2TX security routers allow unauthenticated remote root access. Update firmware immediately.

Symantec reveals popular Chrome extensions like Browsec VPN & DualSafe Password Manager are leaking sensitive user data over unencrypted HTTP, risking privacy.

ViciousTrap is hijacking over 5,000 SOHO routers to build a distributed honeypot-like surveillance network, exploiting Cisco flaws for covert observation.

The BlastRADIUS vulnerability (CVE-2024-3596) necessitates a MITM position, implying that a network may already be compromised if exploited