 Do Son
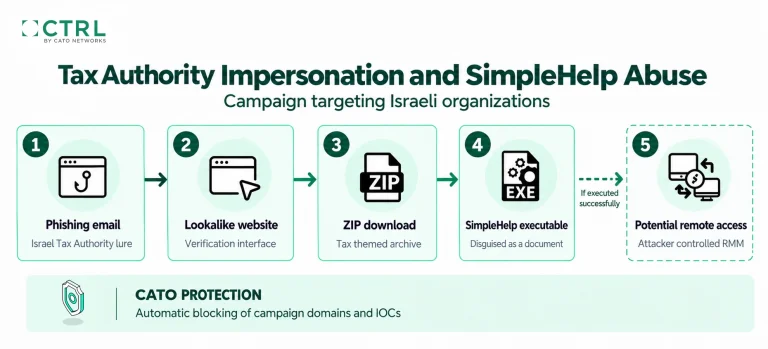
Cato CTRL exposed the MuddyWater SimpleHelp campaign in Israel using tax lures. Learn how the MuddyWater SimpleHelp campaign abuses RMM tools.
cyber-espionage
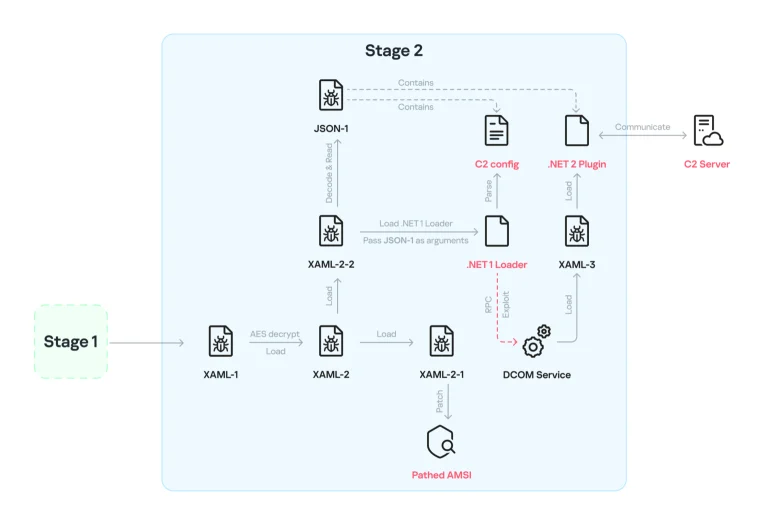
NetamLoader, a new XAML-based .NET loader, points to a supply chain attack on a custom Windows build used by government entities in Asia.
BRONZE SANDCASTLE uses Sandboxie DLL sideloading to run a modified Meterpreter backdoor in memory against targets in Asia and Africa.

APT28 used the Hookedge backdoor, SSH tunnels, and a new loader to spy on a naval shipbuilder and defense firms in two NATO countries.
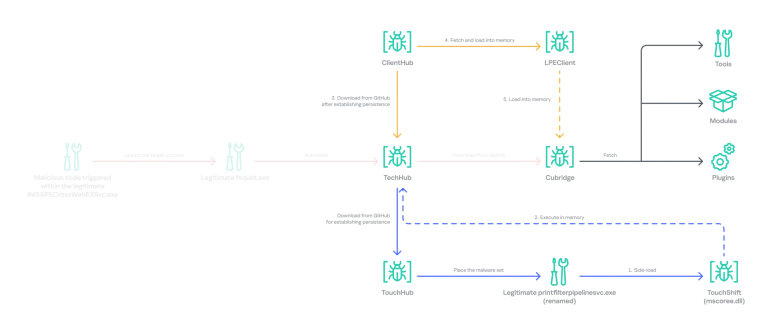
In Operation FlashHole, the Lazarus Group used AI-made lure sites, CrossWeb EX, and GitHub C2 to spy on South Korean firms. Here is how.
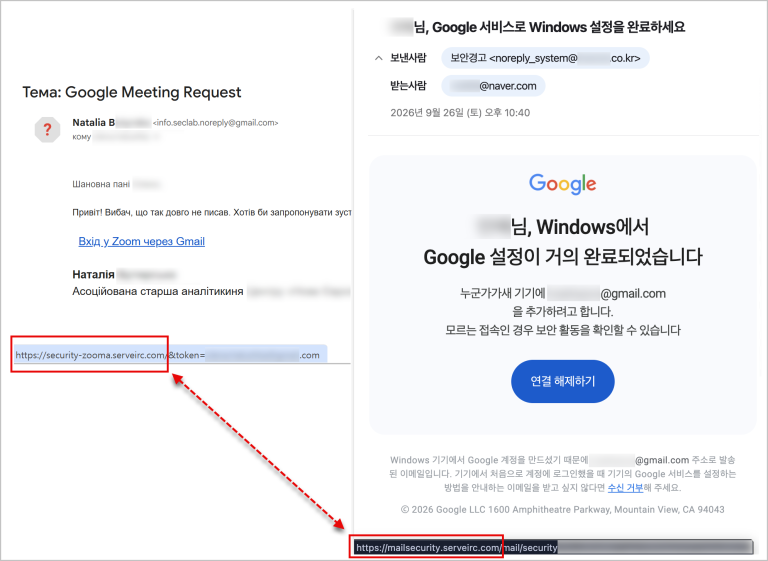
Kimsuky spear phishing lures target Ukrainian security experts with fake invitations, as Operation GitPower abuses GitHub and GitLab.
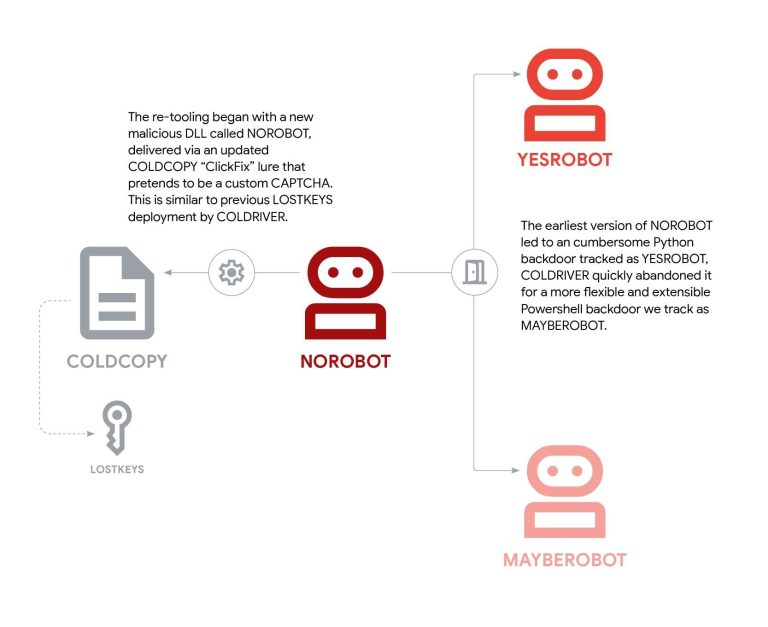
Star Blizzard RedFlick phishing hit 100+ groups that back Ukraine, using scheduled tasks to drop the CosmicPulse backdoor after a single click.
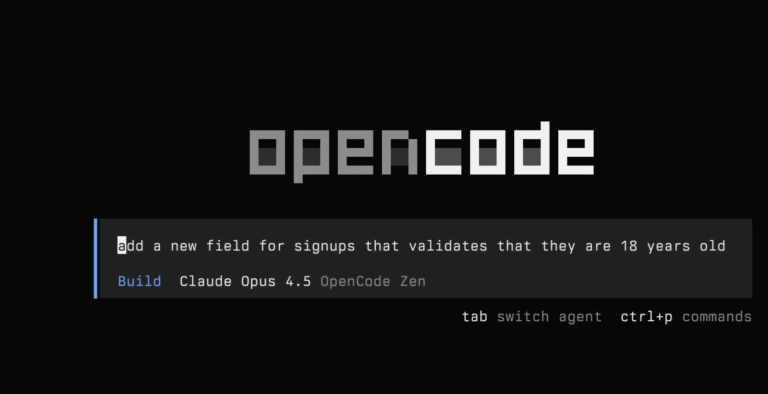
Threat analysts reveal Kimsuky uses AI agent opencode to mass-produce phishing decoys. Discover how the group leverages AI to enhance its LNK attacks.
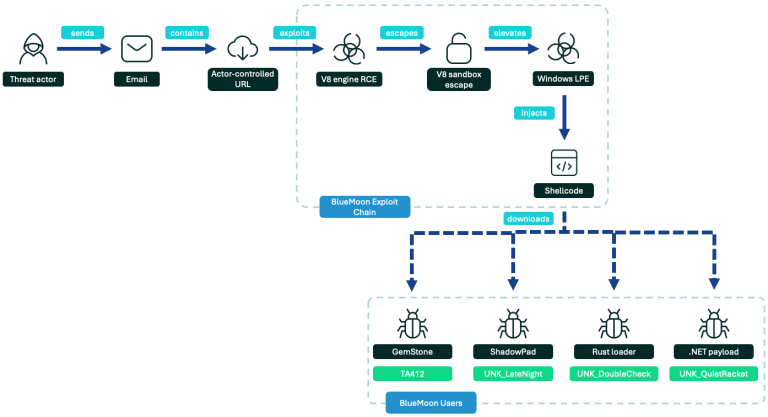
Espionage groups use the BlueMoon exploit kit in new attacks. Discover how BlueMoon exploit kit campaigns exploit Chrome zero-days.
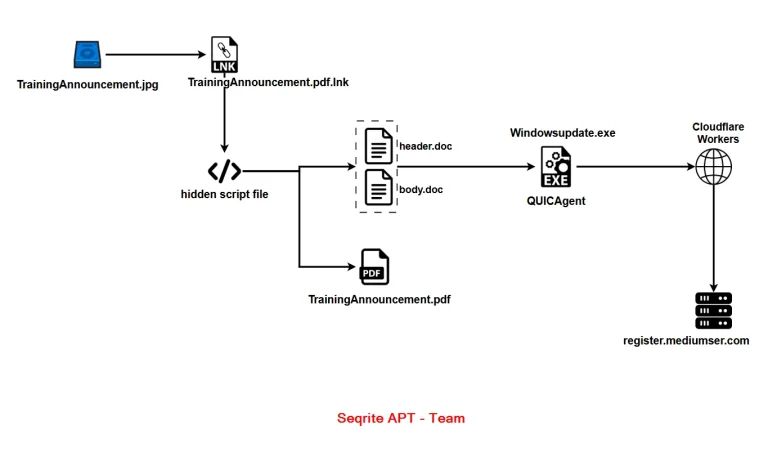
Seqrite links Operation QUICSILVER to a China-nexus actor deploying the QUICAgent Go backdoor against Myanmar government targets via a VHD lure.
The Jewelbug APT group runs espionage alongside cryptocurrency scams. Read our report on Jewelbug APT group operations.

Acronis ties a new PATCHCORD malware APT36 campaign to Afghan telecom and Indian targets. SHEETCORD malware abuses Google Sheets for C2.

Kaspersky analyzed the Project CAV3RN framework. Read our Project CAV3RN framework analysis to see how attackers abuse DNS and Google Apps Script.

Kaspersky GReAT uncovered OctLurk and SilkLurk, two new memory-resident backdoors targeting Central Asian governments since January 2025.

Mirage Kitten malware, tied to the UNC1549 APT, hit aviation and telecom targets across the Middle East and Africa with new backdoors and tunnelers.
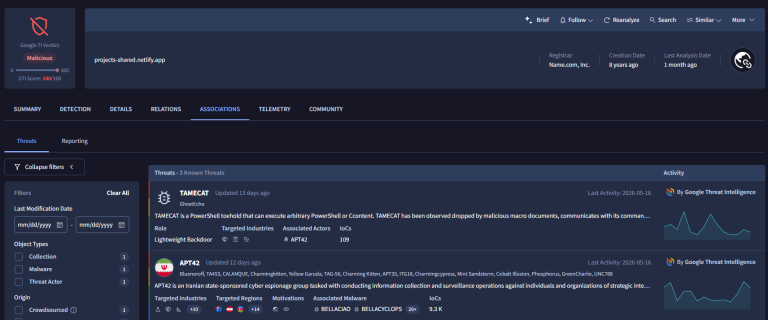
APT42 TAMECAT malware now blends AI-assisted phishing with cloud C2 to steal credentials from defense and nuclear-sector targets.
GoSerpent backdoor drives a patient cyber espionage campaign against Southeast Asian governments, stealing files and credentials since at least 2021.

The DoNot APT hit Bangladesh military targets with a fake officer biography. Cyderes traced a live, multi-stage implant to active C2 servers.
Symantec found Daxin malware active in Taiwan in May 2026, alongside a new Stupig backdoor that runs commands from the Windows logon screen.

HOLLOWGRAPH malware turns Microsoft 365 calendars into covert C2 through Microsoft Graph API abuse. Group-IB links it to the Cavern framework.
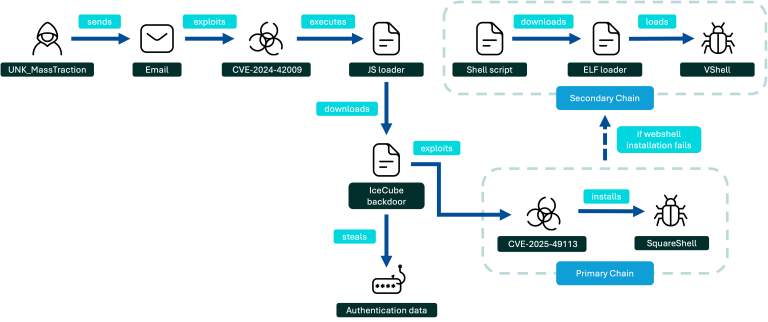
UNK_MassTraction, a suspected China-aligned actor, exploits Roundcube webmail flaws to steal credentials and deploy the VShell backdoor at universities.

Mustang Panda targets India's government and hydropower sectors, abusing Zoho WorkDrive for C2. Acronis found new ZOHOMURK and MINIRECON implants.