
 Do Son
Interlock Ransomware breached AMTEC, leaking sensitive defense data and raising concerns over espionage and national security risks.
cyber-espionage

North Korean threat actor TA406 intensifies cyber espionage against Ukraine, using phishing and malware to gather political intelligence.

Earth Ammit’s VENOM and TIDRONE campaigns target Taiwan and South Korea’s drone, military, and satellite sectors via stealthy supply chain attacks.

Swan Vector cyber-espionage campaign uses sophisticated malware to target institutions in Japan and Taiwan. Learn how they evade detection and steal data

A cyber-espionage campaign linked to Türkiye is exploiting a zero-day flaw in Output Messenger to target entities in Iraq. Learn about the attack.
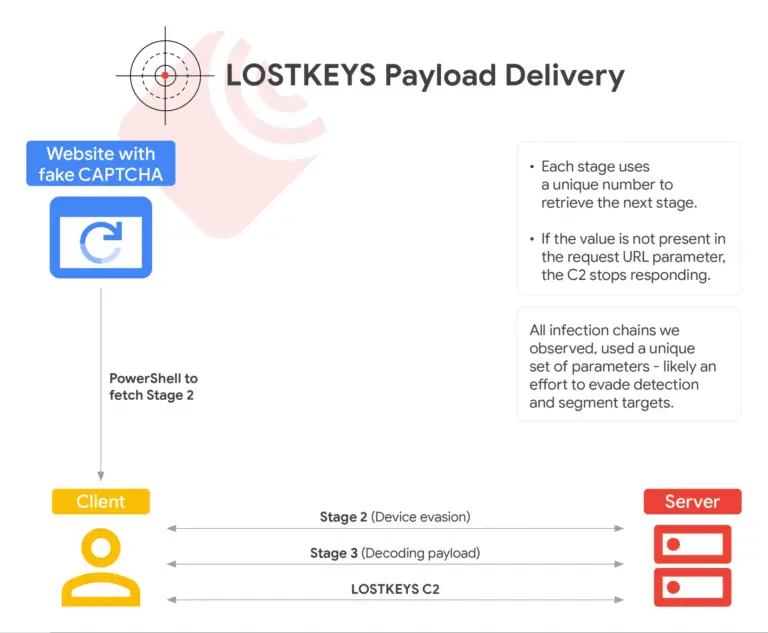
Google's GTIG reveals LOSTKEYS malware, a new tool by Russian actor COLDRIVER, targeting NATO advisors and Ukraine via fake CAPTCHAs.
Unit 42 uncovers Iranian cyber espionage using a fake modeling agency website to selectively target victims with sophisticated techniques.
Seqrite Labs uncovers APT36 phishing campaign using Pahalgam terror attack-themed lures to deploy Crimson RAT against Indian government targets.
FortiGuard reveals an Iranian APT's multi-stage intrusion into Middle Eastern critical infrastructure using custom malware and stealthy persistence.

PRODAFT report details Nebulous Mantis (Cuba/STORM-0978), a Russian-speaking group using RomCom RAT for espionage and ransomware.

ANSSI reveals sustained cyber espionage by APT28 (Fancy Bear) targeting French institutions since 2021. Learn about their tactics and targets.
Earth Kasha targets Taiwan and Japan in a March 2025 spear-phishing campaign using ANEL and NOOPDOOR backdoors for stealthy cyber espionage.

Kaspersky uncovers "Operation SyncHole," a sophisticated cyber-espionage campaign by the Lazarus Group targeting critical South Korean sectors using advanced malware.

Trend Micro reveals how Russian IP networks support North Korea’s cybercrime—from crypto theft to malware-laced fake job interviews and potential espionage.

Volexity uncovers Russian threat actors abusing Microsoft 365 OAuth flows via phishing, impersonation, and device registration to access email accounts.

NVISO's report details BRICKSTORM, a China-linked backdoor targeting European industries, using sophisticated techniques to evade detection

The Knownsec 404 team reports on the DarkHotel APT group's latest attacks, featuring upgraded frameworks and sophisticated evasion techniques.

A China-nexus APT group exploited Ivanti Connect Secure VPN vulnerabilities to infiltrate organizations globally, deploying the SPAWNCHIMERA malware toolkit
The NCSC reveals DAMASCENED PEACOCK, a sophisticated malware targeting the UK MOD, using spear-phishing, code signing, and COM Hijacking.

Rapid7 reveals details of Ivanti zero-day CVE-2025-22457, a critical stack-based buffer overflow actively exploited by a China-linked group. Learn about the vulnerability and available patches.

A new report reveals Russia-linked Shuckworm's evolved cyber campaign targeting a military mission in Ukraine, featuring sophisticated malware and stealthy tactics.
Uncover the tactics of the CNC group in Operation Sea Elephant targeting academic and research institutions in South Asia.