
 Do Son
Salt Typhoon, a China-MSS linked APT, targets global telecoms and military networks for long-term espionage, exploiting network edge devices for future cyber warfare ops.
cyber-espionage

Cisco Talos uncovers a long-running espionage campaign using a new PlugX backdoor. The malware shows strong links to Chinese APT groups Naikon and BackdoorDiplomacy.

An Iranian state-aligned APT, Nimbus Manticore, is targeting European defense and telecom firms with sophisticated spear-phishing campaigns and new malware.

A new report reveals Subtle Snail, an Iran-nexus group, is using fake LinkedIn jobs to deliver a custom backdoor for espionage against European telecom and defense firms.
A new APT28 campaign targets Ukraine's military with a blend of steganography, open-source tools, and legitimate cloud services for covert C2.

North Korean threat group Kimsuky is using AI-generated deepfakes in a new spear-phishing campaign, signaling a new frontier in cyber warfare.

A new report reveals a Chinese APT group compromised a Philippine military company with a fileless malware framework called EggStreme, which uses DLL sideloading for stealth.

A new report reveals a ToneShell backdoor from Mustang Panda. The malware targets Myanmar and uses anti-analysis tricks to evade detection.
A new report reveals North Korea's APT37 is using Rust-based malware called Rustonotto, marking a shift toward modern languages and multi-platform attacks.

A new report uncovers 45 previously unknown domains linked to the Chinese APT group Salt Typhoon. The findings reveal a long-term, multi-year espionage infrastructure.

A new report reveals Noisy Bear, an APT group targeting Kazakhstan’s oil and gas sector with spear-phishing and multi-stage malware, mimicking internal communications.

A new report reveals that the North Korean Kimsuky APT is using social engineering on Facebook and Telegram to deliver AppleSeed malware to targets in South Korea.
A new report reveals North Korea's APT-37 is using malicious LNK files in a campaign, "Operation HanKook Phantom," to spy on South Korean government and research.

An Iranian-aligned group abused a compromised Omani Foreign Ministry mailbox to send spear-phishing emails to diplomats and international organizations in a global campaign.

A new report reveals the TAOTH cyber-espionage campaign, which hijacks software updates and uses spear-phishing to deliver malware to high-value targets in Asia.

Amazon has disrupted a watering hole campaign by Russia's APT29. The hackers used compromised sites to trick users into authorizing attacker-controlled devices via Microsoft.
A new Group-IB report reveals ShadowSilk, a hybrid Chinese and Russian-speaking threat cluster that uses Telegram bots for cyber espionage against Central Asian governments.

The NSA, CISA, and partners have released a joint advisory exposing how Chinese APT groups are compromising telecom and government networks for global espionage.
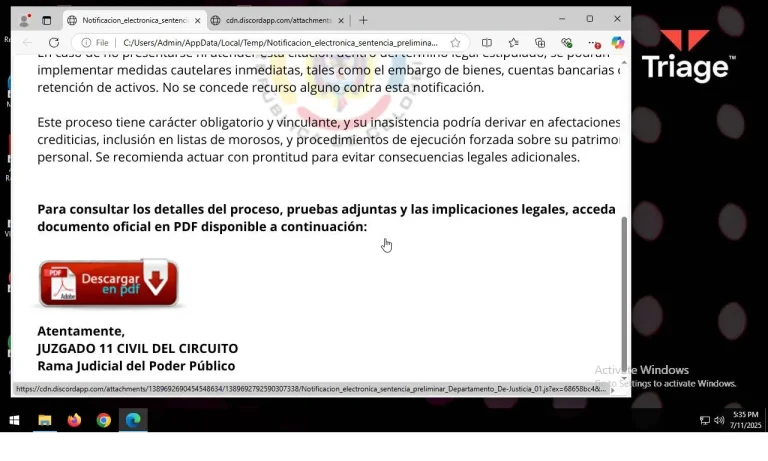
A new report reveals the Blind Eagle hacking group is using spearphishing and commodity RATs to conduct cyber espionage against Colombian government and private sector targets.

A new Google report reveals a Chinese APT group is hijacking captive portals and disguised plugins to deliver malware for espionage against diplomats in Southeast Asia.
A new report reveals that the Pakistan-linked APT36 is now targeting Indian government and defense entities with Linux-specific malware delivered via Google Drive.

A data leak from an alleged North Korean APT group's workstation has revealed its use of a commercial proxy service, offering a rare look into its anonymizing infrastructure.