
 Do Son
New "Gopher Strike" & "Sheet Attack" campaigns hit Indian govt. Linked to Pakistan, attackers use GitHub C2 & GenAI malware to evade detection.
cyber-espionage

Trend Micro uncovers PeckBirdy, a JScript C&C framework used by China-aligned APTs. It uses lightweight, fileless tactics to target Asian governments.
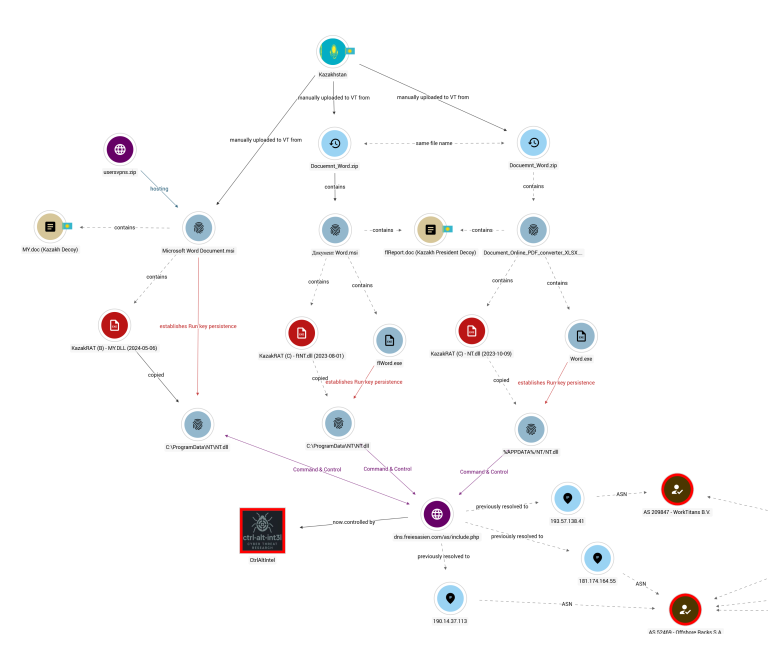
Researchers uncover "KazakRAT," a state-affiliated spyware targeting Kazakhstan & Afghanistan. A lapsed domain allowed experts to sinkhole the C2.
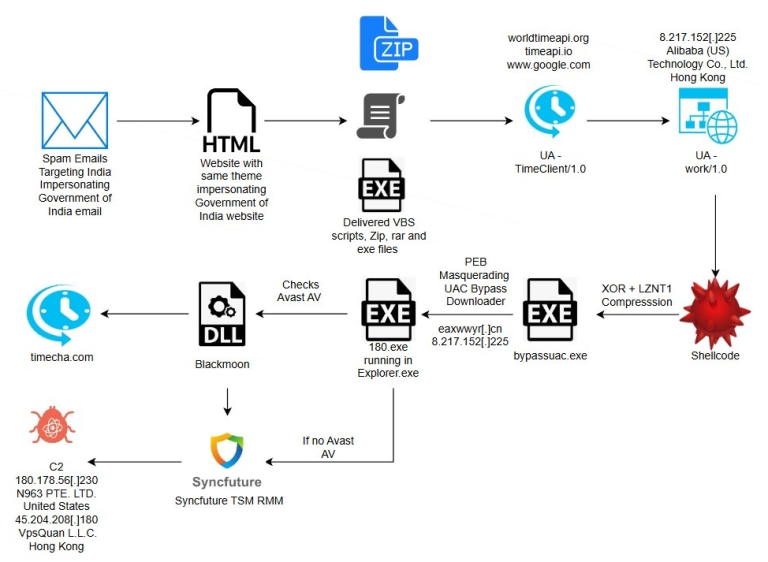
"SyncFuture" spies on Indian users via fake Income Tax emails. This advanced campaign bypasses antivirus & installs Chinese IT tools for total surveillance.

DPRK spies weaponize Visual Studio Code tunnels to bypass security. Darktrace reveals a campaign targeting South Korea with government decoys.
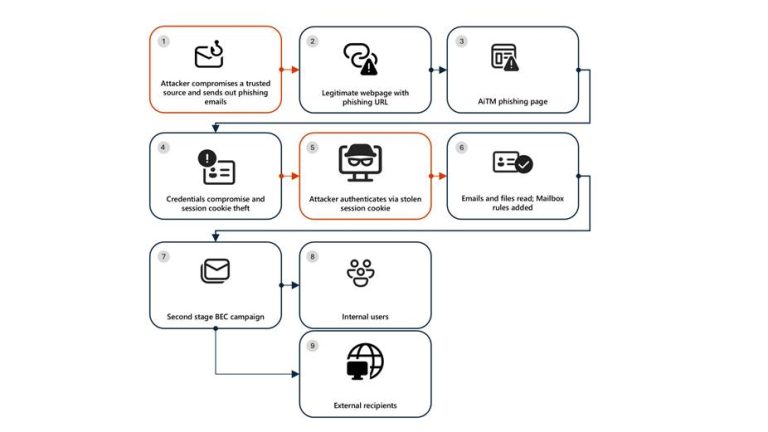
Microsoft warns of an AiTM phishing campaign targeting the energy sector. Hackers steal session cookies and abuse SharePoint to launch internal attacks.

Seqrite exposes "Operation Covert Access": A Rust RAT targeting Argentina's legal system via fake court rulings. Includes anti-analysis & encryption tools.

Nomad Leopard targets Afghan officials with fake ministry docs. SEQRITE reveals how the "afghanking777000" OPSEC fail exposed the spies.

Resecurity finds PDFSIDER, a new APT malware using DLL side-loading and AES-256-GCM encryption to bypass EDR and open covert backdoors.

Genians reveals "Operation Poseidon": Konni APT exploits Google & Naver ad redirects to bypass defenses and deploy EndRAT.

KnownSec leak exposes a "vertically integrated espionage stack." See how ZoomEye and GhostX power China's state-aligned cyber operations.

Cisco Talos reveals UAT-7290, a China-nexus group targeting global telecoms. They act as both spies and infrastructure builders for other hackers.

Russian group BlueDelta targets energy researchers in Europe & Middle East. Learn how they abuse free web services for credential harvesting.

Threat actor uses React2Shell to deploy Sliver C2 on FortiWeb devices, using a Bangladesh Airforce decoy to target govt and financial sectors.
CYFIRMA unmasks APT36's latest campaign: a fake JLPT exam lure using fileless LNK malware to evade antivirus and spy on Indian government targets.

Koi Security unmasks DarkSpectre, a Chinese threat group that used 300+ browser extensions to spy on 8.8M users and steal corporate meeting data.

Kaspersky unmasks HoneyMyte's 2025 campaign, using the ProjectConfiguration.sys kernel rootkit to deploy ToneShell backdoors with elite stealth.

Hackers bribed Ubisoft outsourced staff for backend access, leading to a $339T currency exploit and a massive source code leak. Is outsourcing to blame?

GreyNoise reveals a massive Japan-based holiday campaign: 2.5 million attacks targeting 767 CVEs to harvest access for ransomware gangs.
EmEditor confirms its official site was compromised, redirecting users to a malicious MSI signed by WALSHAM INVESTMENTS LIMITED to steal sensitive data.

CloudSEK’s TRIAD unmasks Silver Fox APT, a China-linked group using Valley RAT to target India while hiding behind misattributed tax phishing lures.

Kaspersky exposes Evasive Panda’s AitM campaign, hijacking DNS to deliver MgBot through fake updates for SohuVA and Tencent QQ.