
 Do Son
LAB52 exposes a new China-aligned espionage campaign using fake meeting invitations and G DATA antivirus components to stealthily deploy the PlugX RAT.
cyber-espionage

OpenAI’s Feb 2026 report reveals "cyber special operations," Cambodian "Date Bait" scams, and Russian content farms using AI to automate global disruption.
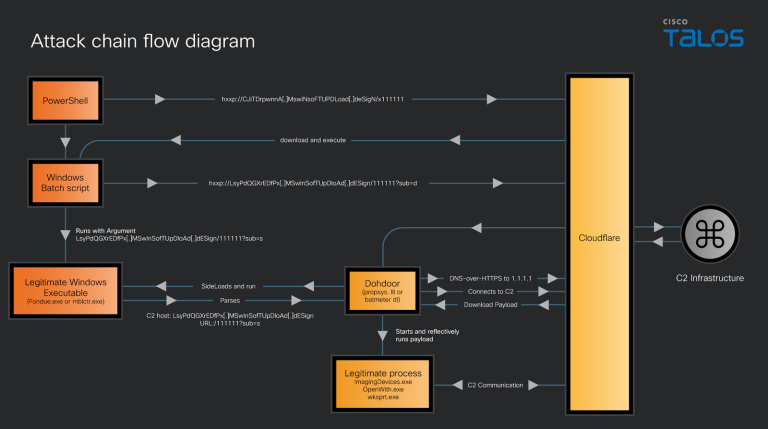
Cisco Talos uncovers "Dohdoor," a stealthy backdoor used by UAT-10027. It abuses DNS-over-HTTPS via Cloudflare to spy on U.S. healthcare and education sectors.
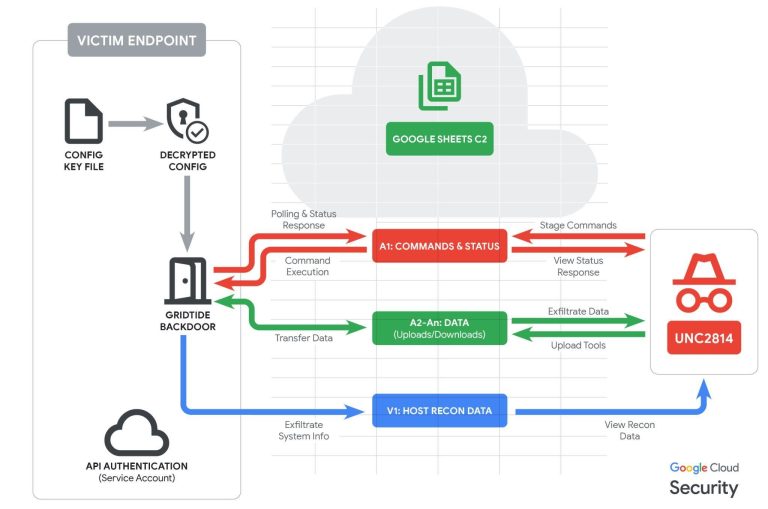
Google and Mandiant disrupt UNC2814, a China-nexus group using the GRIDTIDE backdoor to hide command-and-control traffic inside Google Sheets across 42 nations.
BlueVoyant uncovers a shift in Mercenary Akula (UAC-0050) tactics, targeting European financial institutions via spoofed judicial lures and RMS malware.

Threat hunters expose North Korean state actors using Medusa ransomware to fund global espionage. U.S. healthcare and non-profits are the primary targets.

US Treasury sanctions Sergey Zelenyuk and Operation Zero for brokering stolen government exploits and selling zero-days to foreign intelligence agencies.

Acronis uncovers CRESCENTHARVEST, a new spyware targeting Iranian dissidents. Attackers use protest lures & Google DLL sideloading to steal data.

APT28's "Operation MacroMaze" targets Europe using Spanish gov decoys. The campaign uses "low-tech" macros & Webhook.site to evade detection.
GTIG report: Defense Industrial Base faces "constant siege" from Russian drone hackers & North Korean IT insiders. Learn the new threats.

New campaign targets Ivanti EPMM with dormant in-memory backdoors. Attackers use CVE-2026-1281 to plant "sleeper" agents. Restart servers immediately.

Silent Push's Traffic Origin technology strips away VPN masks to reveal the true location of threat actors. Detect North Korean & Russian proxies now.

TGR-STA-1030 (UNC6619) hits 70+ orgs in 37 countries. The Asia-based group uses the new ShadowGuard eBPF rootkit to hide in Linux kernels.

Stan Ghouls group targets Uzbekistan via fake court emails and malicious Java loaders. Learn how they deploy NetSupport RAT to spy on victims.

Silver Fox APT targets users with fake LINE installers delivering ValleyRat. New campaign uses rare "PoolParty" injection to evade detection.

APT42 targets defense officials with "TAMECAT," a modular PowerShell backdoor. The malware uses social engineering and Telegram C2 to steal secrets.

North Korea's LABYRINTH CHOLLIMA splits into 3 units: GOLDEN, PRESSURE, & Core. CrowdStrike reveals new strategy targeting crypto & defense.
APT28 launches "Operation Neusploit" targeting Europe. Hackers exploit CVE-2026-21509 to deploy MiniDoor malware via RTF files. Patch Office now.

"RedKitten" spies on Iranian protesters using AI-written malware. Attackers use fake death lists to deploy SloppyMIO surveillance tools.

Cisco Talos warns of UAT-8099 targeting Asian IIS servers with region-locked BadIIS malware. New variants now attack Linux systems.
Pakistan-linked spies target India with "Sheet Attack," using Google Sheets for C2 and GenAI to build malware. Learn about SHEETCREEP and FIREPOWER.
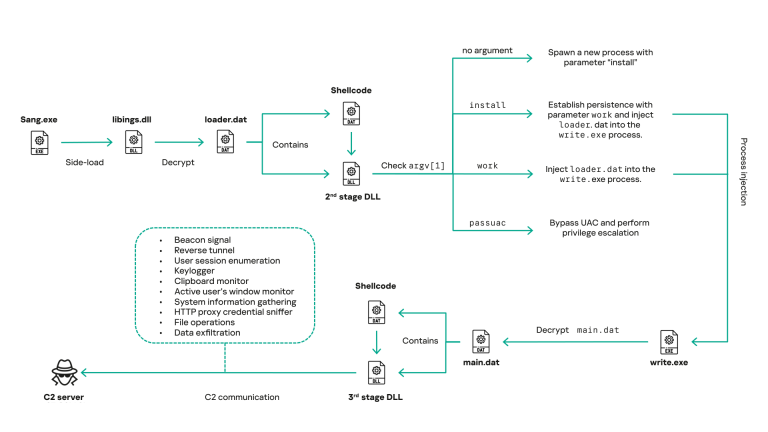
HoneyMyte (Mustang Panda) shifts to real-time surveillance using updated CoolClient. New 2025 campaign uses Pixeldrain for stealthy exfiltration.