 Do Son
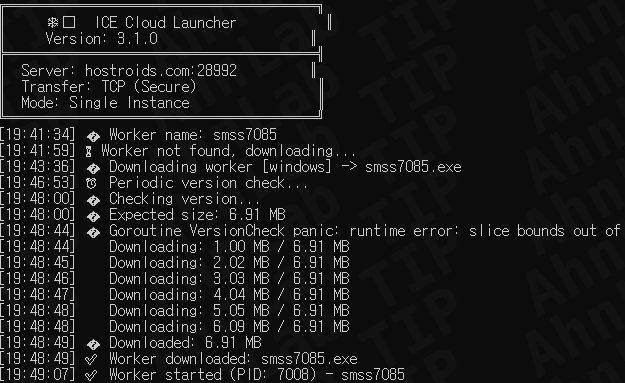
Larva-26002 strikes again with "ICE Cloud," a Go-based scanner using AI-assisted code to hijack MS-SQL servers. Discover the technical breakdown and defense.
cyber-espionage
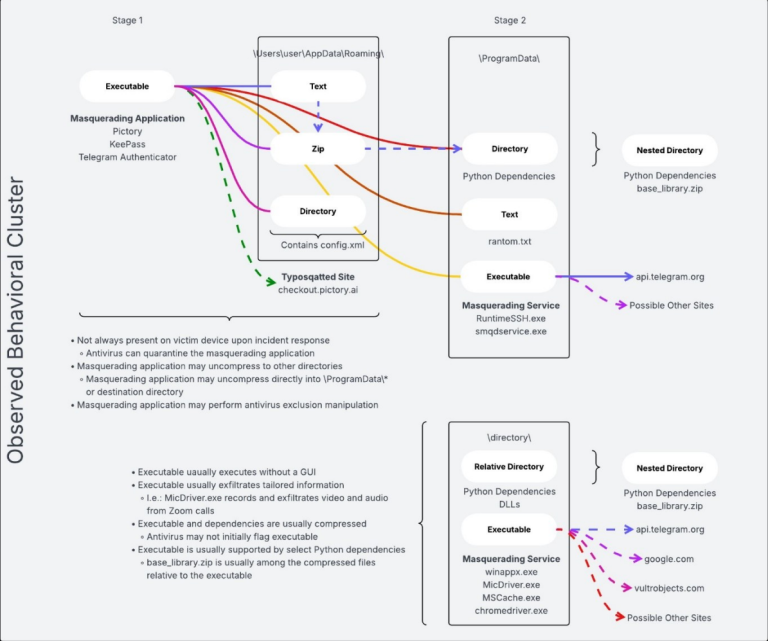
The FBI warns that Iran's MOIS is weaponizing Telegram as a Command-and-Control hub to deploy malware against global dissidents and journalists.

The US DOJ has seized four domains used by Iran's MOIS to orchestrate global cyberwarfare, doxing, and death threats against dissidents and governments.
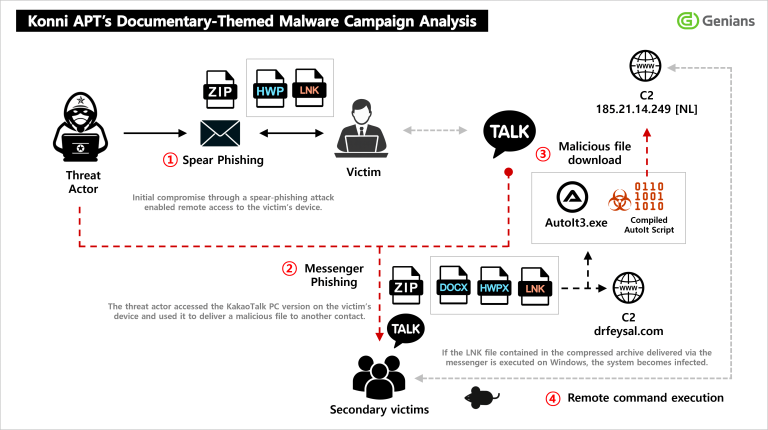
Genians Security Center reveals a new Konni APT campaign hijacking KakaoTalk PC sessions to distribute EndRAT, RftRAT, and RemcosRAT to trusted contacts.
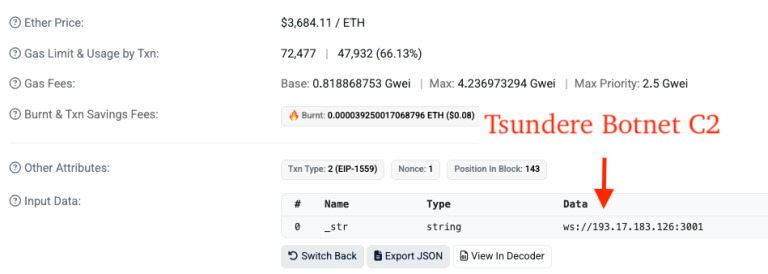
eSentire TRU reveals Iranian group Muddy Water deploying the Russian-linked Tsundere botnet, utilizing Ethereum smart contracts for stealthy C2 communication.

LAB52 uncovers the DRILLAPP backdoor, a novel espionage campaign targeting Ukraine that weaponizes Microsoft Edge for screen recording and surveillance.

Seqrite Labs exposes Operation CamelClone, a global cyber espionage campaign using the HOPPINGANT loader and public cloud services to evade detection.
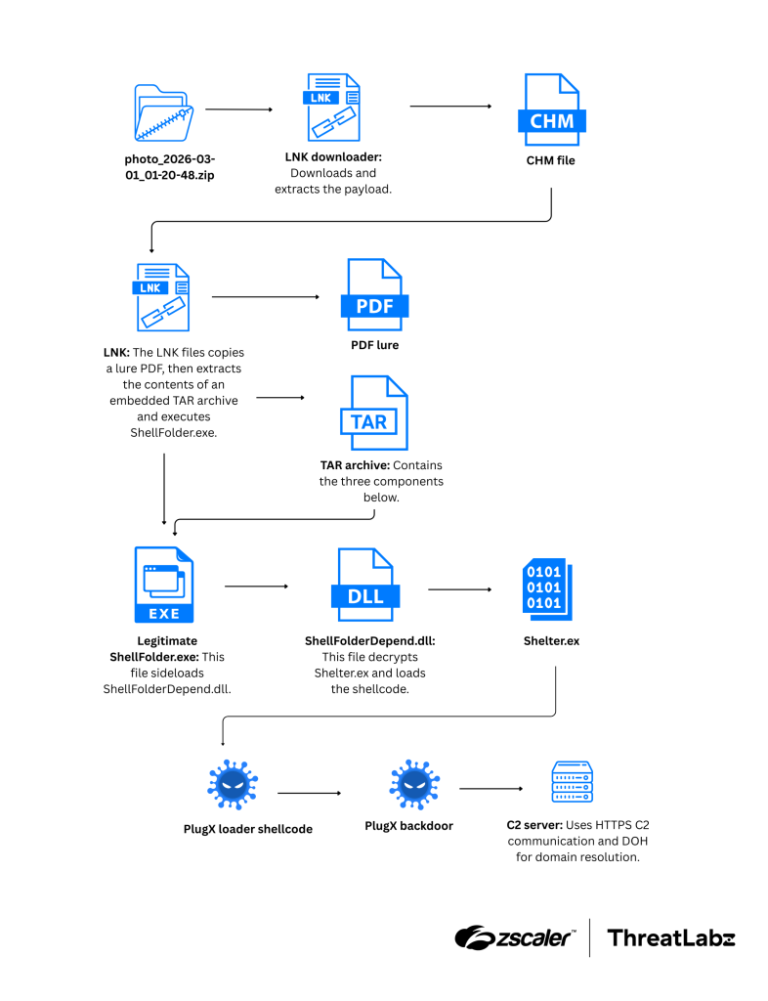
ThreatLabz reveals how China-nexus actor Mustang Panda weaponized Middle East conflict lures to deploy a stealthy PlugX backdoor within 24 hours.
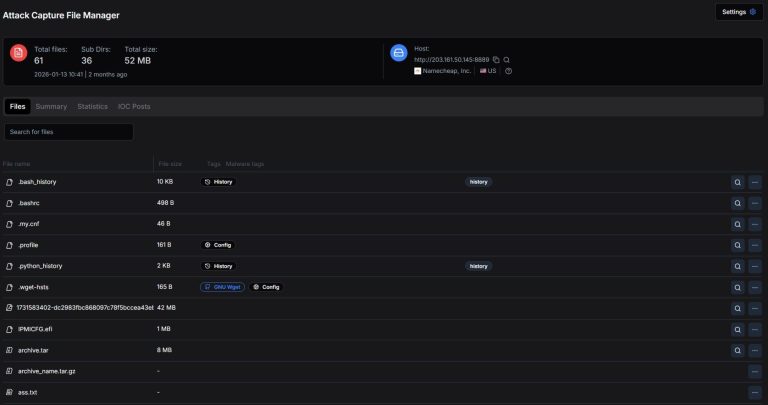
Hunt Intelligence unmasks APT28's 'Roundish' toolkit from an exposed server, revealing advanced CSS side-channel attacks and stealthy Linux implants.

Unit 42 exposes CL-STA-1087, a suspected Chinese state-sponsored cyber espionage group using custom backdoors to infiltrate Asian military networks.
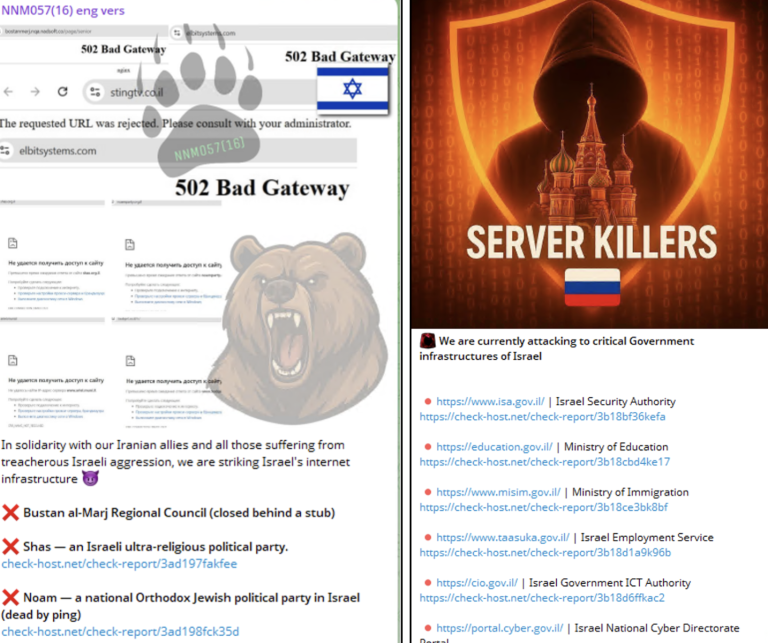
Rapid7 reveals a surge in state-directed cyber espionage and noisy hacktivism. Learn how actors like MuddyWater exploit critical CVEs to breach networks.
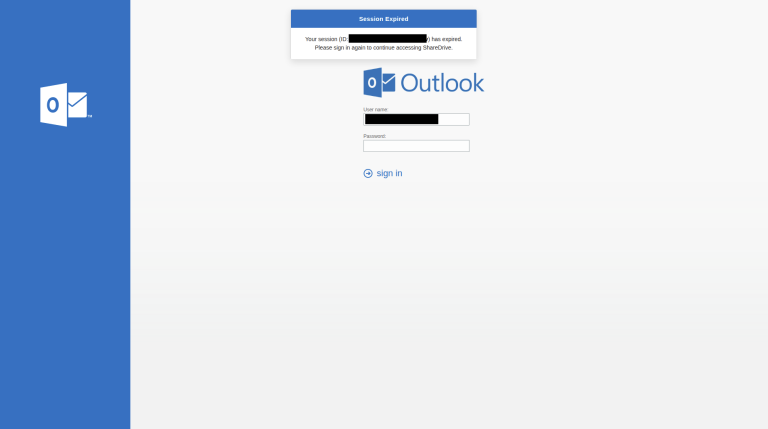
Proofpoint reveals Iran-aligned TA453 is exploiting Operation Epic Fury to launch targeted credential phishing campaigns against U.S. think tanks.
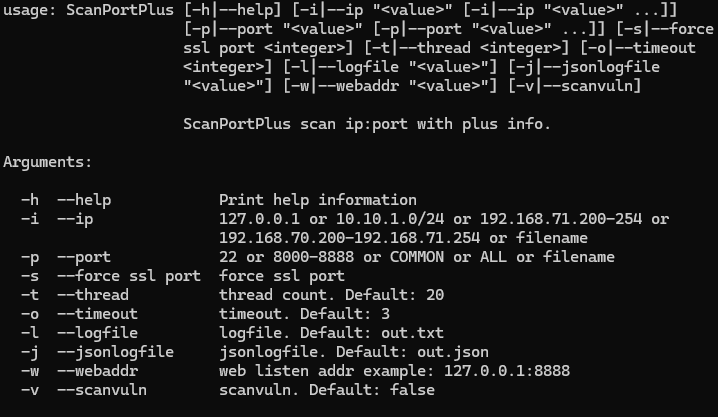
Unit 42 uncovers CL-UNK-1068, a Chinese APT targeting Asian critical infrastructure using stealthy web shells, LOLBINs, and screen-printed exfiltration.

Dutch intelligence (MIVD/AIVD) warns of a global campaign using social engineering to silently hijack Signal and WhatsApp accounts of high-profile targets.
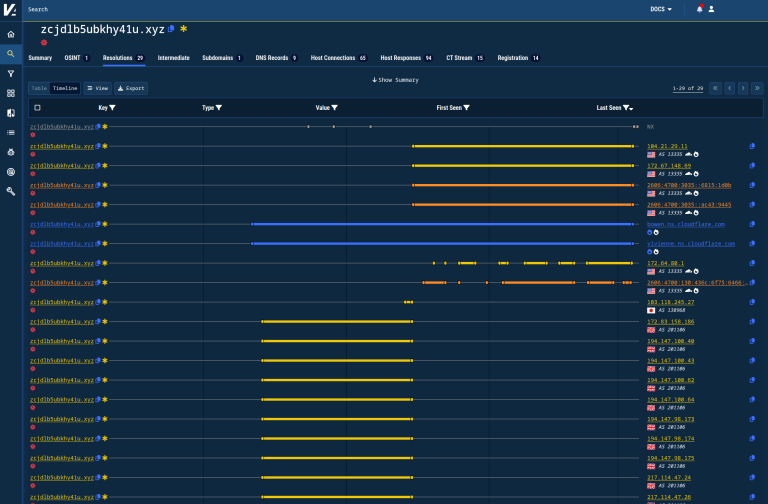
Validin reveals how the Coruna iOS exploit kit evolved from targeted surveillance to mass crypto-draining and geopolitical watering hole attacks.
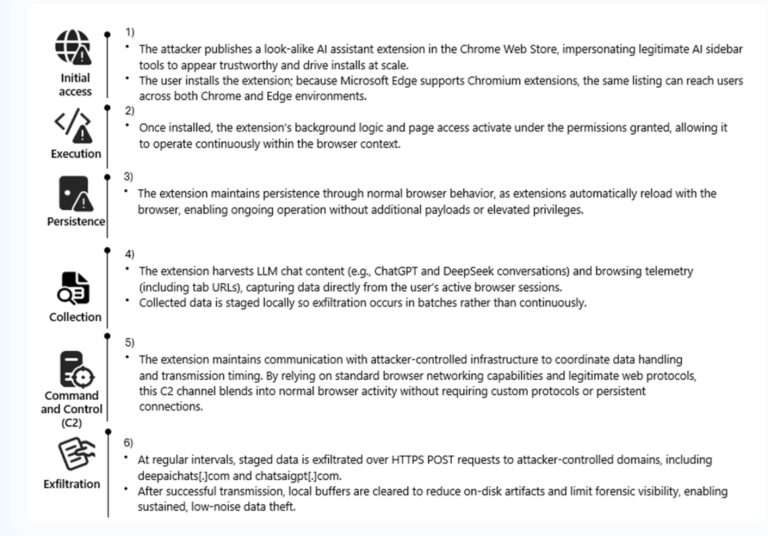
Microsoft Defender uncovers a massive campaign of malicious Chromium extensions impersonating AI tools to steal data from 900,000 users. Audit browsers now.

Cisco Talos exposes UAT-9244, a China-linked APT targeting South American telecoms with stealthy malware like the BitTorrent-based PeerTime and TernDoor.

Zscaler ThreatLabz uncovers Dust Specter, an Iran-linked cyber campaign hijacking Iraqi government infrastructure to deploy custom AI-assisted malware.
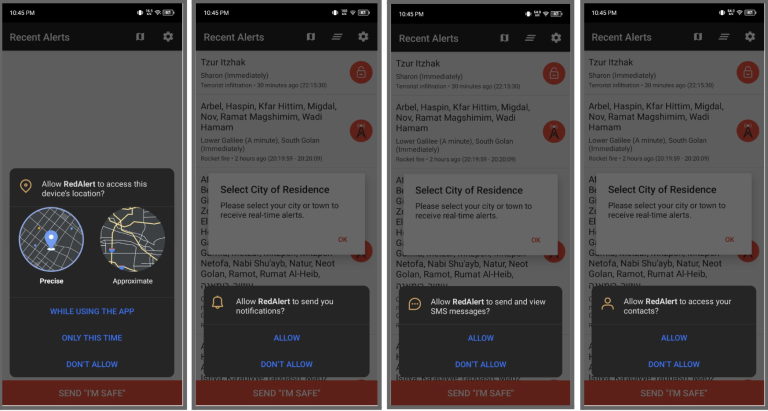
CloudSEK exposes a smishing campaign spreading a trojanized "Red Alert" app. The fake emergency tool tracks locations and steals data during air raids.

CYFIRMA reveals a new cyber espionage campaign by Transparent Tribe (APT36) targeting Indian defense with stealthy multi-stage malware and decoy PDFs.

Moonlock Lab uncovers a North Korean-aligned malware campaign targeting Web3 pros. Attackers use fake VC profiles and ClickFix CAPTCHAs to deploy malware.
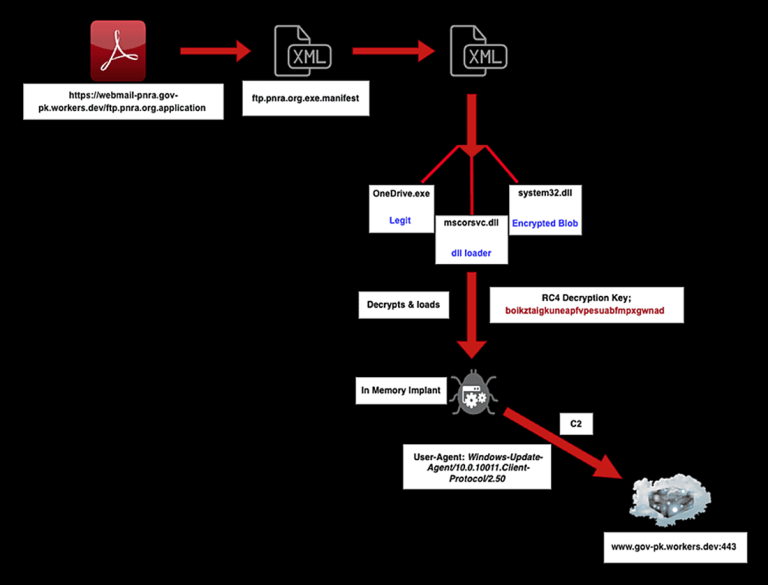
Arctic Wolf details a year-long cyber espionage campaign by Sloppy Lemming, deploying the custom BurrowShell malware against Pakistan and Bangladesh.