 Do Son
CISA warns as North Korean and Russian hackers weaponize ConnectWise and Windows Shell flaws. Patch by May 12, 2026, to prevent state-sponsored espionage.
cyber-espionage

PRC national Xu Zewei extradited to the US for HAFNIUM intrusions and targeting COVID-19 research. He faces a 9-count indictment for state-sponsored hacks.
Cisco Talos uncovers the FIRESTARTER backdoor in Arcane Door's latest attack on Firepower devices. Patch CVE-2025-20333 now to stop state-sponsored espionage.

Harvester APT expands to Linux using Microsoft Graph API for C2. Learn how the "GoGra" variant uses Outlook and "Zomato Pizza" lures to evade detection.
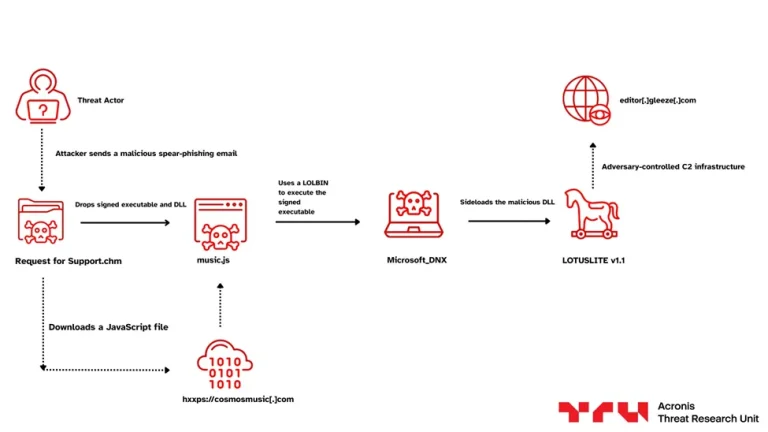
Mustang Panda targets India’s financial sector with the LOTUSLITE malware. Learn how this DLL sideloading campaign bypasses defenses for cyber-espionage.
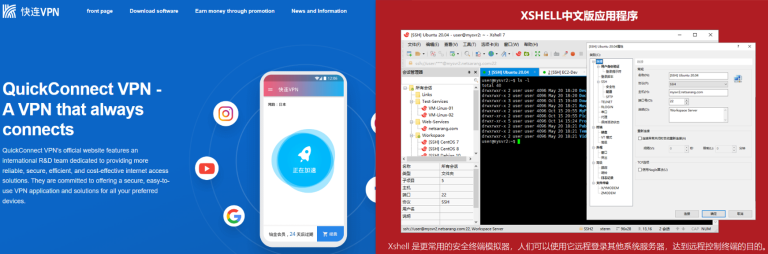
Kong RAT: A year-long SEO poisoning campaign targeting developers with trojanized SSH/VPN tools and .NET NativeAOT stealth. Learn how to stay protected.
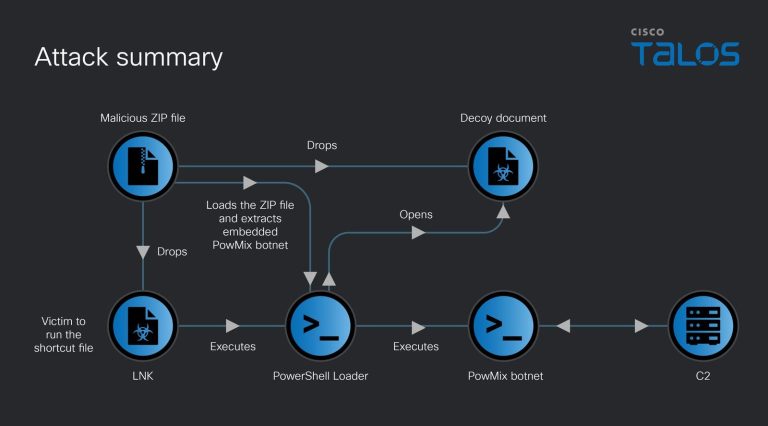
Cisco Talos uncovers PowMix, a stealthy botnet targeting Czech HR via AMSI bypass and Heroku-hosted C2. Learn how this malware evades modern EDR systems.
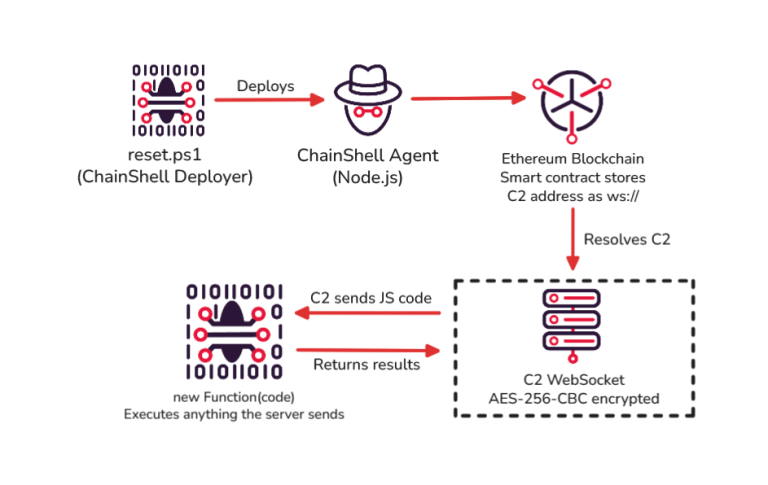
Iranian state actor Muddy Water adopts CastleRAT and ChainShell to hijack browsers and bypass MFA invisibly. A professional-grade shift in APT strategy.
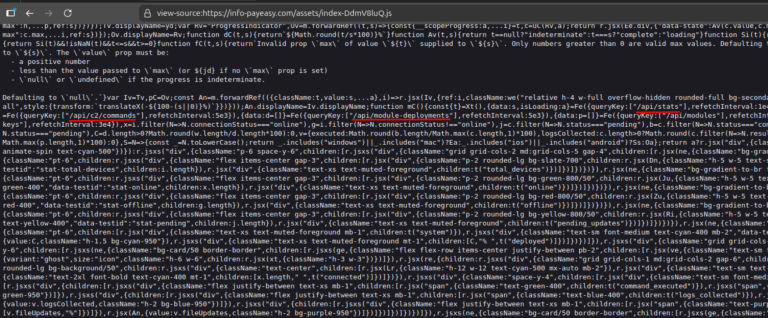
Hunt.io discovers Canis C2, an AI-assisted surveillance framework targeting all major OSs. An exposed API revealed payloads and source code. Read more here.
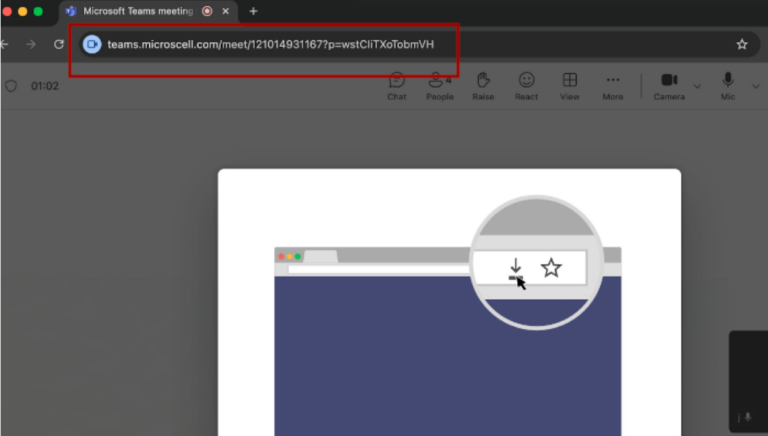
North Korean group UNC1069 (BlueNoroff) targets Web3 with fake Zoom/Teams links. 164 domains blocked. Secure your crypto assets and browser extensions now!
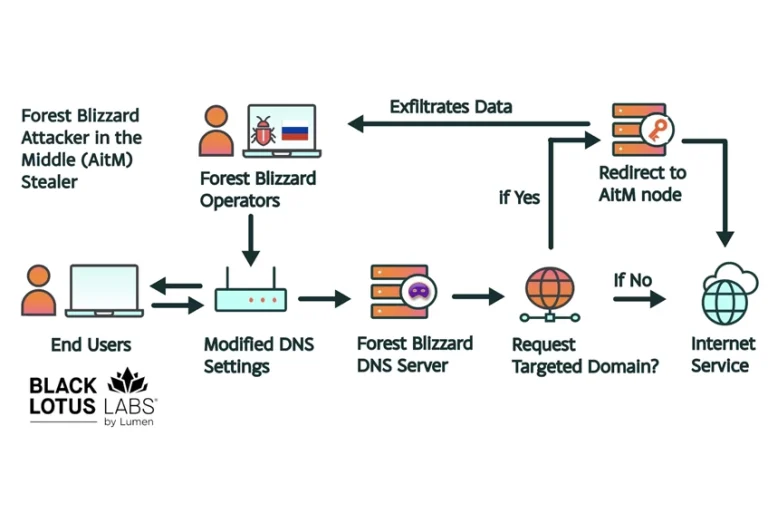
Russian-linked Forest Blizzard's FrostArmada campaign hijacked 18,000+ routers to steal OAuth tokens via DNS redirection. Learn how they stayed invisible.
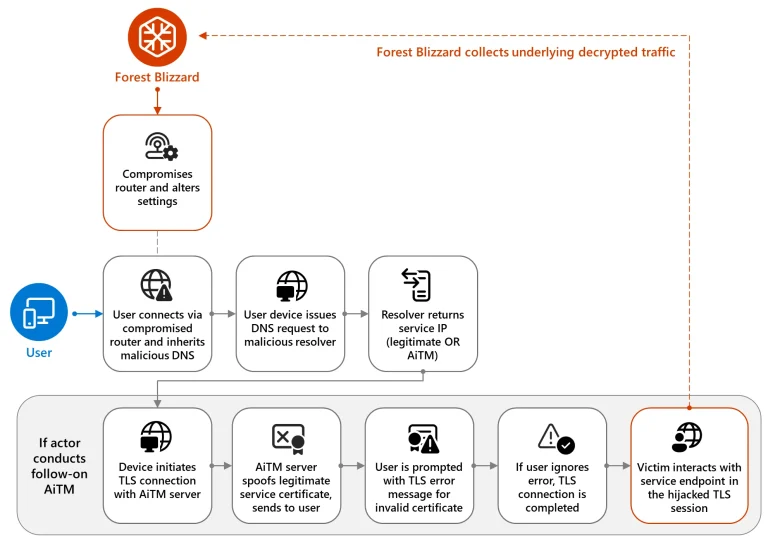
Microsoft exposes Forest Blizzard’s hijacking of 5,000+ SOHO routers for DNS spying and AiTM attacks on Microsoft 365 and governments. Patch your router now!

ASEC uncovers Kimsuky’s evolved LNK-to-Python chain abusing Dropbox for stealthy persistence. Learn how to detect this complex multi-stage backdoor.
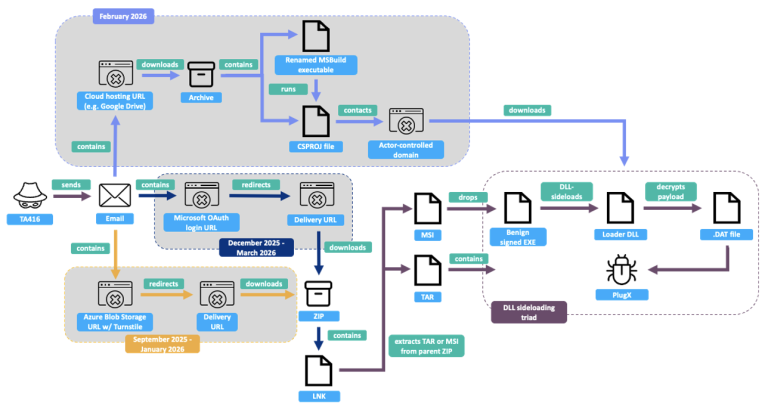
Proofpoint uncovers TA416's pivot to EU, NATO, and Middle East diplomacy. Learn how this state-linked actor uses updated PlugX and Cloudflare lures in 2026.

Check Point Research uncovers an Iran-linked password spraying campaign targeting M365 to support kinetic missile strikes and damage assessment in the ME.
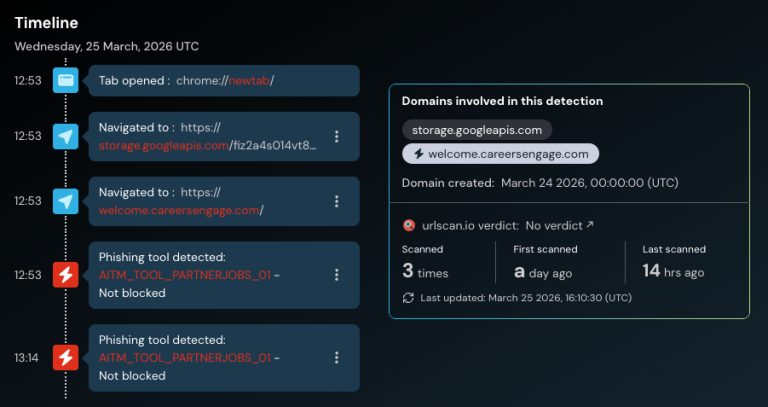
Researchers uncover a novel AiTM campaign targeting TikTok for Business. Attackers bypass MFA to steal Google SSO tokens and hijack corporate ad accounts.
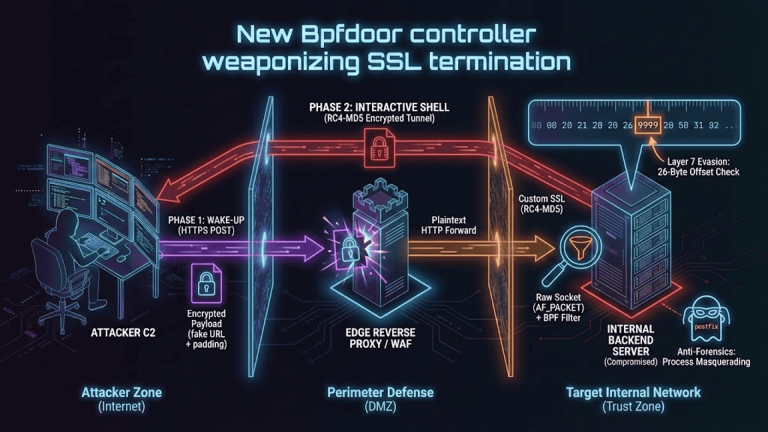
Rapid7 uncovers Red Menshen’s BPFdoor backdoor in global telecom cores. Learn how this China-nexus actor uses kernel-level stealth for mass surveillance.

Pawn Storm (APT28) debuts the PRISMEX suite, weaponizing Office zero-days against NATO logistics. Discover the stealth tactics behind this 2026 offensive.
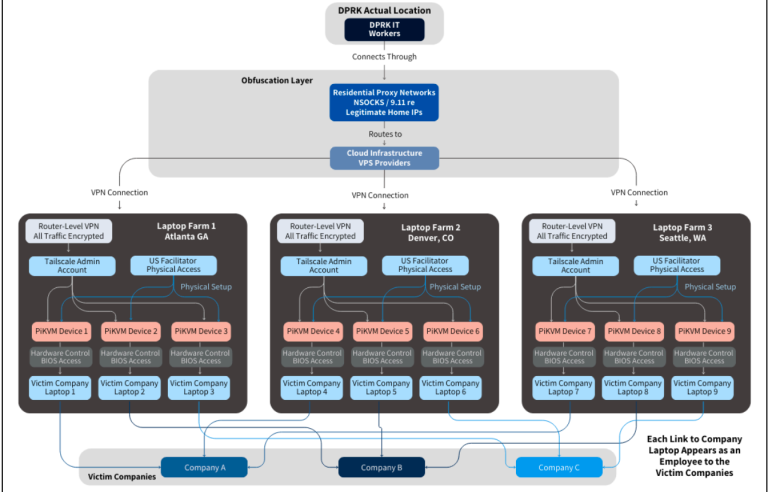
Nisos exposes a North Korean IT worker scheme involving a Florida-based laptop farm, AI-generated resumes, and PiKVM devices. Don't fall for the ruse.
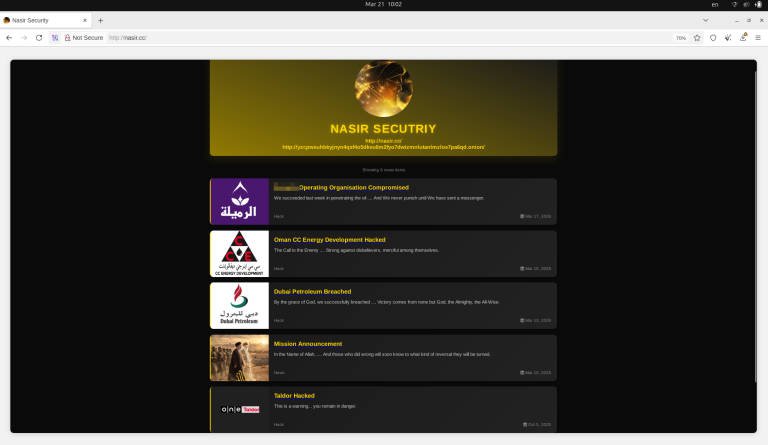
Resecurity uncovers Nasir Security, an Iranian threat actor using supply chain attacks and psy-ops to target Middle East energy vendors and leak blueprints.
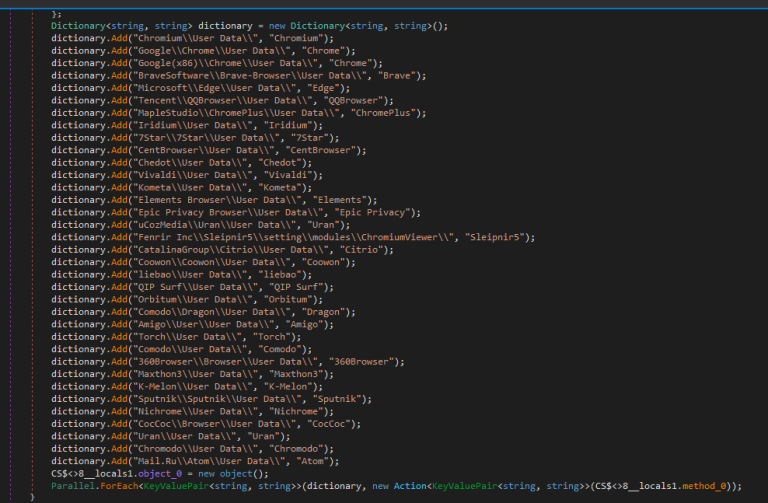
Malwarebytes uncovers a PureHVNC RAT campaign using Google Forms to bait professionals. Learn how this stealthy infection chain targets 2026 business docs.
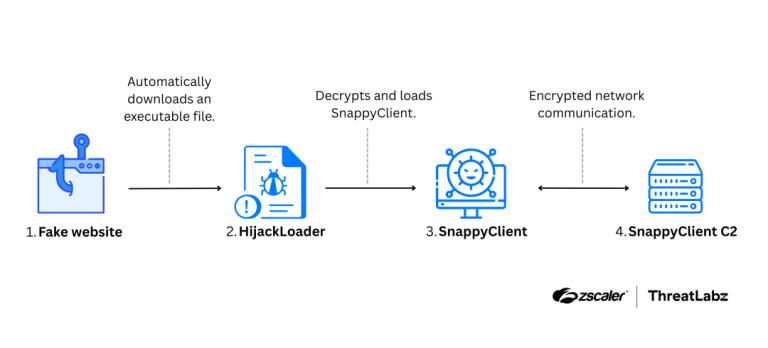
Zscaler ThreatLabz unmasks SnappyClient, a C++ C2 framework linked to HijackLoader. It uses AMSI bypass and Heaven’s Gate to steal crypto and gain remote access.