Skip to content
October 27, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Cybercriminals
  • Russian Hackers Abuse Microsoft 365 OAuth in Sophisticated Phishing Attacks
  • Cybercriminals

Russian Hackers Abuse Microsoft 365 OAuth in Sophisticated Phishing Attacks

Do Son April 24, 2025 3 minutes read
0
OAuth Phishing Microsoft 365 OAuth

Image: Volexity

Add Daily CyberSecurity as a preferred source on Google

Volexity has identified a series of advanced social engineering operations by suspected Russian threat actors targeting Microsoft 365 (M365) OAuth authentication flows. The campaigns, which began in March 2025, represent a concerning evolution in phishing techniques—leveraging legitimate Microsoft authentication infrastructure to gain unauthorized access to victim accounts.

“Volexity is currently tracking what is believed to be at least two Russian threat actors, which it tracks as UTA0352 and UTA0355, that are behind these attacks,” the report states.

UTA0352 primarily uses secure messaging apps like Signal and WhatsApp to impersonate diplomats and government officials. Victims are invited to join fake video calls discussing sensitive topics—especially the conflict in Ukraine—and are sent Microsoft OAuth URLs as part of the ruse.
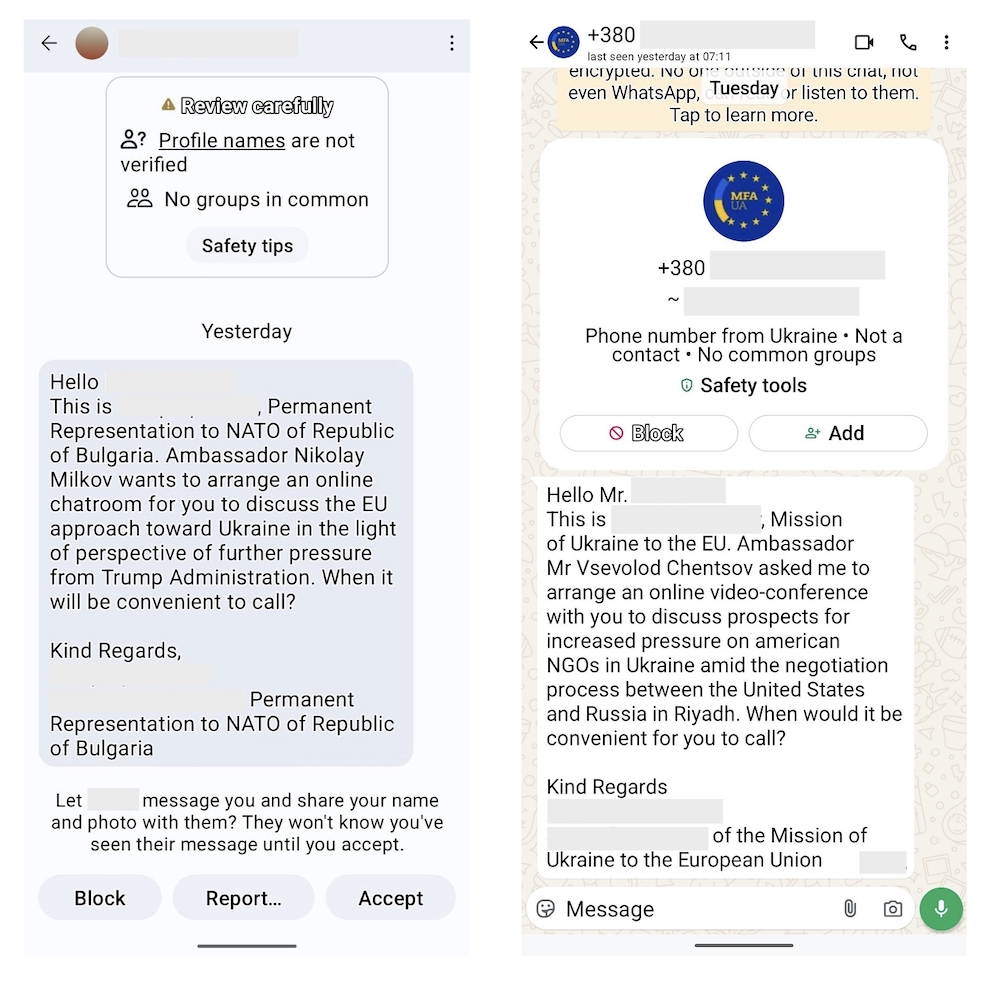
Initial outreach messages sent by UTA0352 impersonating various identities on Signal (left) and WhatsApp (right) | Image: Volexity 

“The victim is asked to return the Microsoft-generated OAuth code back to the attacker… which ultimately allows access to the victim’s M365 account.”

In one example, targets received PDF instructions from the “Romanian Ministry of Foreign Affairs,” leading them to URLs like:

https://login.microsoftonline.com/organizations/oauth2/v2.0/authorize?...&redirect_uri=https://insiders.vscode.dev/redirect

These links point to first-party Microsoft services, including Visual Studio Code, to extract OAuth authorization codes. Once obtained, these codes are exchanged for access tokens—providing full access to the victim’s M365 resources.

In these phishing flows, the attackers cleverly abuse legitimate features of Microsoft’s OAuth implementation. “Clicking the link alone would not be enough… The code would need to be supplied back to the attacker,” Volexity explains.

In one scenario, users were redirected to a VS Code interface designed to expose the OAuth code in the browser’s address bar or dialog window. This code, valid for up to 60 days, grants access to Microsoft Graph APIs, potentially exposing all emails, files, and collaboration data.

The second threat actor, UTA0355, used a more elaborate multi-stage approach. It started with emails sent from a compromised Ukrainian government account to NGOs and human rights advocates, followed by social engineering via messaging apps.

“This time, the campaign started with an email from a legitimate, compromised Ukrainian Government email account… followed by messages sent via Signal and WhatsApp.”

Instead of accessing Graph APIs directly, UTA0355 targeted the Device Registration Service in Microsoft Entra ID (formerly Azure AD), registering a new device to the victim’s identity.

After this, the attacker socially engineered the target to approve a 2FA request, giving full control over the email account. Post-compromise activity revealed the email contents were downloaded from the newly registered machine.

Volexity offers numerous recommendations to identify and mitigate these attacks:

  • Alert on OAuth flows using client_id aebc6443-996d-45c2-90f0-388ff96faa56 with suspicious redirect URIs.
  • Block access to insiders.vscode.dev and vscode-redirect.azurewebsites.net if feasible.
  • Monitor for unusual device registrations in Microsoft Entra ID.
  • Educate users about unsolicited contact through secure messaging apps.
  • Implement conditional access policies restricting access to approved or managed devices.

Unlike conventional phishing that relies on fake websites or malware, these campaigns abuse first-party Microsoft infrastructure. The OAuth flow is technically legitimate, but users unknowingly grant attackers access by sharing sensitive tokens—a method harder to detect and even harder to defend against.

“The victim is only ever asked to interact with legitimate Microsoft 365 services, which users may inherently see as trustworthy,” Volexity warns.

Related Posts:

  • Phishing for Profits: Attackers Mine Crypto & Spam Through OAuth Apps
  • Volexity: Indian APT hacker organization Patchwork target US think tanks
  • Massive XSS Threat: Millions of Websites Vulnerable via OAuth Flaw
  • Russian Hackers Exploit Microsoft Device Code Authentication in Targeted Attacks Against M365 Accounts

Related coverage

  • Russian APT UTA0355 Steals Microsoft 365 OAuth Tokens via Fake Security Conference Lures and WhatsApp Support
  • AI in the Driver’s Seat: How the ‘Bissa’ Scanner Hijacked 900+ Firms in Weeks
  • Sophisticated TA4922 Cybercrime Operations Expand Globally
  • KillSec Ransomware Strikes Brazilian Healthcare Provider, Exposing Patient Data
  • The AI Phishing Trap: Zscaler Exposes Fake Brazilian Government Websites Generated by AI to Steal Payments
  • Seychelles Commercial Bank Hacked: Customer Data Compromised, Suspected Espionage Disguised as Cybercrime
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Account Takeover cyber-espionage cybersecurity Entra ID Microsoft 365 OAuth OAuth Abuse OAuth Phishing phishing Russian APT Russian threat actors social engineering UTA0352 UTA0355 Volexity

Leave a Reply Cancel reply

You must be logged in to post a comment.

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2012-20005CVSS 5.1
    SocialFit plugin for WordPress through 1.2.2 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to inject...
    Watchtower Verified📅 Updated: Oct 28, 2026
  • CVE-2015-20123CVSS 8.7
    Aspose Doc Exporter plugin for WordPress before 2.0 contains a path traversal vulnerability that allows unauthenticated attackers to...
    Watchtower Verified📅 Updated: Oct 28, 2026
  • CVE-2016-20101CVSS 9.2
    Issuu Panel plugin for WordPress before 1.6.6 contains a PHP file inclusion vulnerability that allows unauthenticated attackers to...
    Watchtower Verified📅 Updated: Oct 28, 2026
  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 27, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 27, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 27, 2026
  • CVE-2026-102785CVSS 10.0
    Joomla Extension - yootheme.com - Unauthenticated remote code execution in YOOtheme Pro 5.0.0-5.0.52 - YOOtheme Pro’s publicly accessible...
    Admin intel📅 Updated: Oct 27, 2026
  • CVE-2026-48356CVSS 9.3
    Adobe Commerce is affected by an Unrestricted Upload of File with Dangerous Type vulnerability that could result in...
    CISA KEV📅 Added to KEV: Oct 27, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-48356CVSS 9.3
    Adobe Commerce is affected by an Unrestricted Upload of File with Dangerous Type vulnerability that could result in...
    CISA KEV📅 Added to KEV: Oct 27, 2026📅 Updated: Oct 27, 2026
  • CVE-2026-111497CVSS 9.2
    A buffer overflow vulnerability in the Brotli decoder (c/dec/decode.c) in Google Brotli versions 1.0.3 through 1.2.0 on all...
    CISA KEV📅 Added to KEV: Oct 27, 2026📅 Updated: Oct 27, 2026
  • CVE-2026-112352CVSS 9.1
    Sunhillo SureLine before 9.1.5 contains an authentication bypass vulnerability that allows an unauthenticated remote attacker to impersonate any...
    📅 Updated: Oct 27, 2026
  • CVE-2024-31026CVSS 9.8
    An issue in Greek Universities Network (GUnet) Open eClass Platform v.3.15 allows a remote attacker to execute arbitrary...
    📅 Updated: Oct 27, 2026
  • CVE-2024-34320CVSS 9.8
    ProPhoenix Law RMS v2022.2403.3.101 was discovered to contain an incorrect access control issue in sensitive API endpoints.
    📅 Updated: Oct 27, 2026
  • CVE-2024-34323CVSS 10.0
    ProPhoenix Law RMS v2022.2403.3.101 was discovered to contain an Insecure Direct Object Reference (IDOR) via the usrLogin$hdnPFID parameter....
    📅 Updated: Oct 27, 2026
  • CVE-2024-4457CVSS 9.1
    The Management Console fails to properly validate input related to the configuration of JDBC user stores. This weakness...
    📅 Updated: Oct 27, 2026
  • CVE-2026-105008CVSS 9.0
    No cwe for this issue in Windows Schannel allows an unauthorized attacker to perform spoofing over a network.
    📅 Updated: Oct 27, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.