 Do Son
An ARTEX AI agent campaign against IT and software vendors overlaps with Storm-0940, targeting Okta, Entra ID, and AWS Cognito logins.
Entra ID
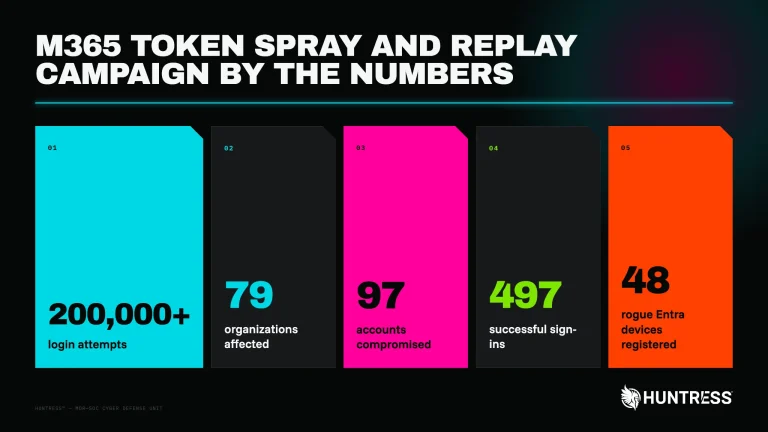
A token replay attack hit 79 organizations, bypassing MFA to set up Microsoft 365 BEC with rogue devices and hidden inbox rules.
CVE-2026-69836 is a CVSS 10 Entra ID remote code execution flaw exploited in the wild. Microsoft has fully mitigated it server-side.
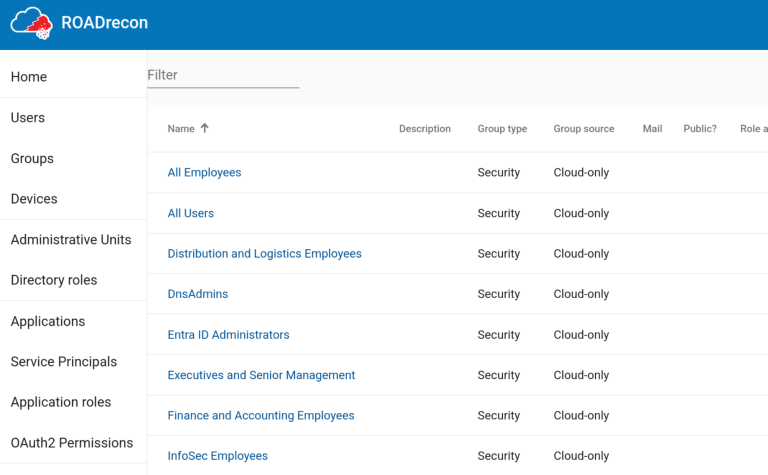
Discover how nation-state hackers leverage the ROADtools cloud attack toolkit to compromise Entra ID environments and bypass MFA controls.

Microsoft has retired its legacy telephone activation system. Learn how to use the new Web Activation Portal to license Windows and Office without an internet connection.
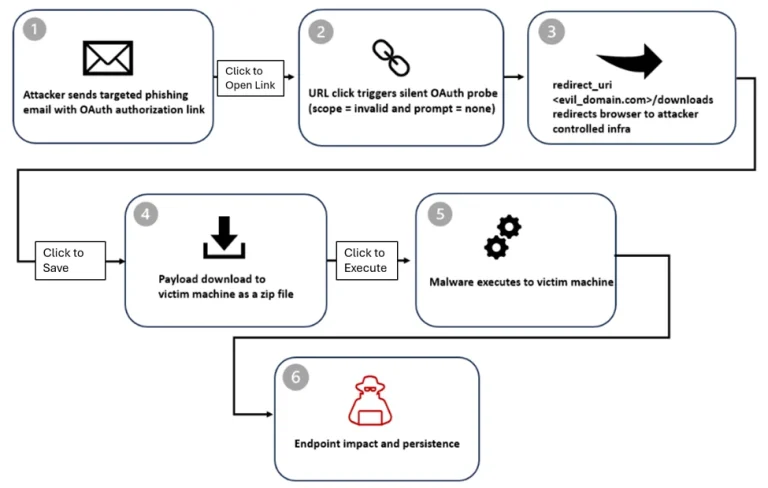
Microsoft Defender reveals a new phishing campaign abusing OAuth redirect URIs to bypass security and deliver stealthy malware to your system.

Microsoft is integrating Entra ID (formerly Azure AD) into WebView2, enabling seamless, modern authentication like passkey and Conditional Access for embedded web apps.

Microsoft Authenticator will purge Entra ID credentials from jailbroken/rooted devices starting Feb 2026 to block token theft, enforcing security for enterprise accounts.

Microsoft Threat Intelligence details how APTs abuse Teams and Entra ID integration for recon, vishing, and C2. Attackers use RMM tools and spoofed accounts to breach enterprise environments.

A new Microsoft report reveals that the Storm-0501 threat actor is pivoting to cloud-native ransomware, using cloud tools to exfiltrate and destroy data without malware.

Datadog reveals a method to impersonate any hybrid Entra ID user, including Global Admins, by exploiting Office 365 Exchange Online service principal. Microsoft calls it "expected behavior."

Volexity uncovers Russian threat actors abusing Microsoft 365 OAuth flows via phishing, impersonation, and device registration to access email accounts.