Skip to content
November 19, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • ADVISORIES
    • Microsoft
    • Fortinet
    • Ivanti
    • Cisco
    • Linux
    • Citrix
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q3 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Malware
  • Vulnerability News
  • Submit Press Release
Light/Dark Button
  • Home
  • News
  • Cybercriminals
  • AiTM Attacks Bypass MFA Despite Widespread Adoption
  • Cybercriminals

AiTM Attacks Bypass MFA Despite Widespread Adoption

Do Son May 4, 2025 3 minutes read
0
cyber

Despite widespread adoption of multi-factor authentication (MFA) as a critical safeguard against unauthorized access, cybercriminals are once again one step ahead. According to a detailed report by Cisco Talos, threat actors are now bypassing MFA mechanisms using Adversary-in-the-Middle (AiTM) attacks—a tactic that exploits reverse proxies to intercept credentials and session cookies, enabling full account takeover.

“Cybercriminals are bypassing multi-factor authentication (MFA) using adversary-in-the-middle (AiTM) attacks via reverse proxies, intercepting credentials and authentication cookies,” the report explains.

The rise of Phishing-as-a-Service (PhaaS) toolkits allow even low-skill attackers to run campaigns with professional-level infrastructure.

Among the most dangerous:

  • Tycoon 2FA
  • Evilproxy
  • Greatness
  • Rockstar 2FA
  • Mamba 2FA

“The developers behind Phishing-as-a-Service (PhaaS) kits like Tycoon 2FA and Evilproxy have added features to make them easier to use and harder to detect,” the report wanrs.

These platforms often feature:

  • Pre-built phishing templates for popular services
  • Link access control and geofencing
  • Anti-bot and anti-crawler logic
  • Delayed lure activation to avoid email scanners
  • Obfuscated JavaScript injection for cookie harvesting

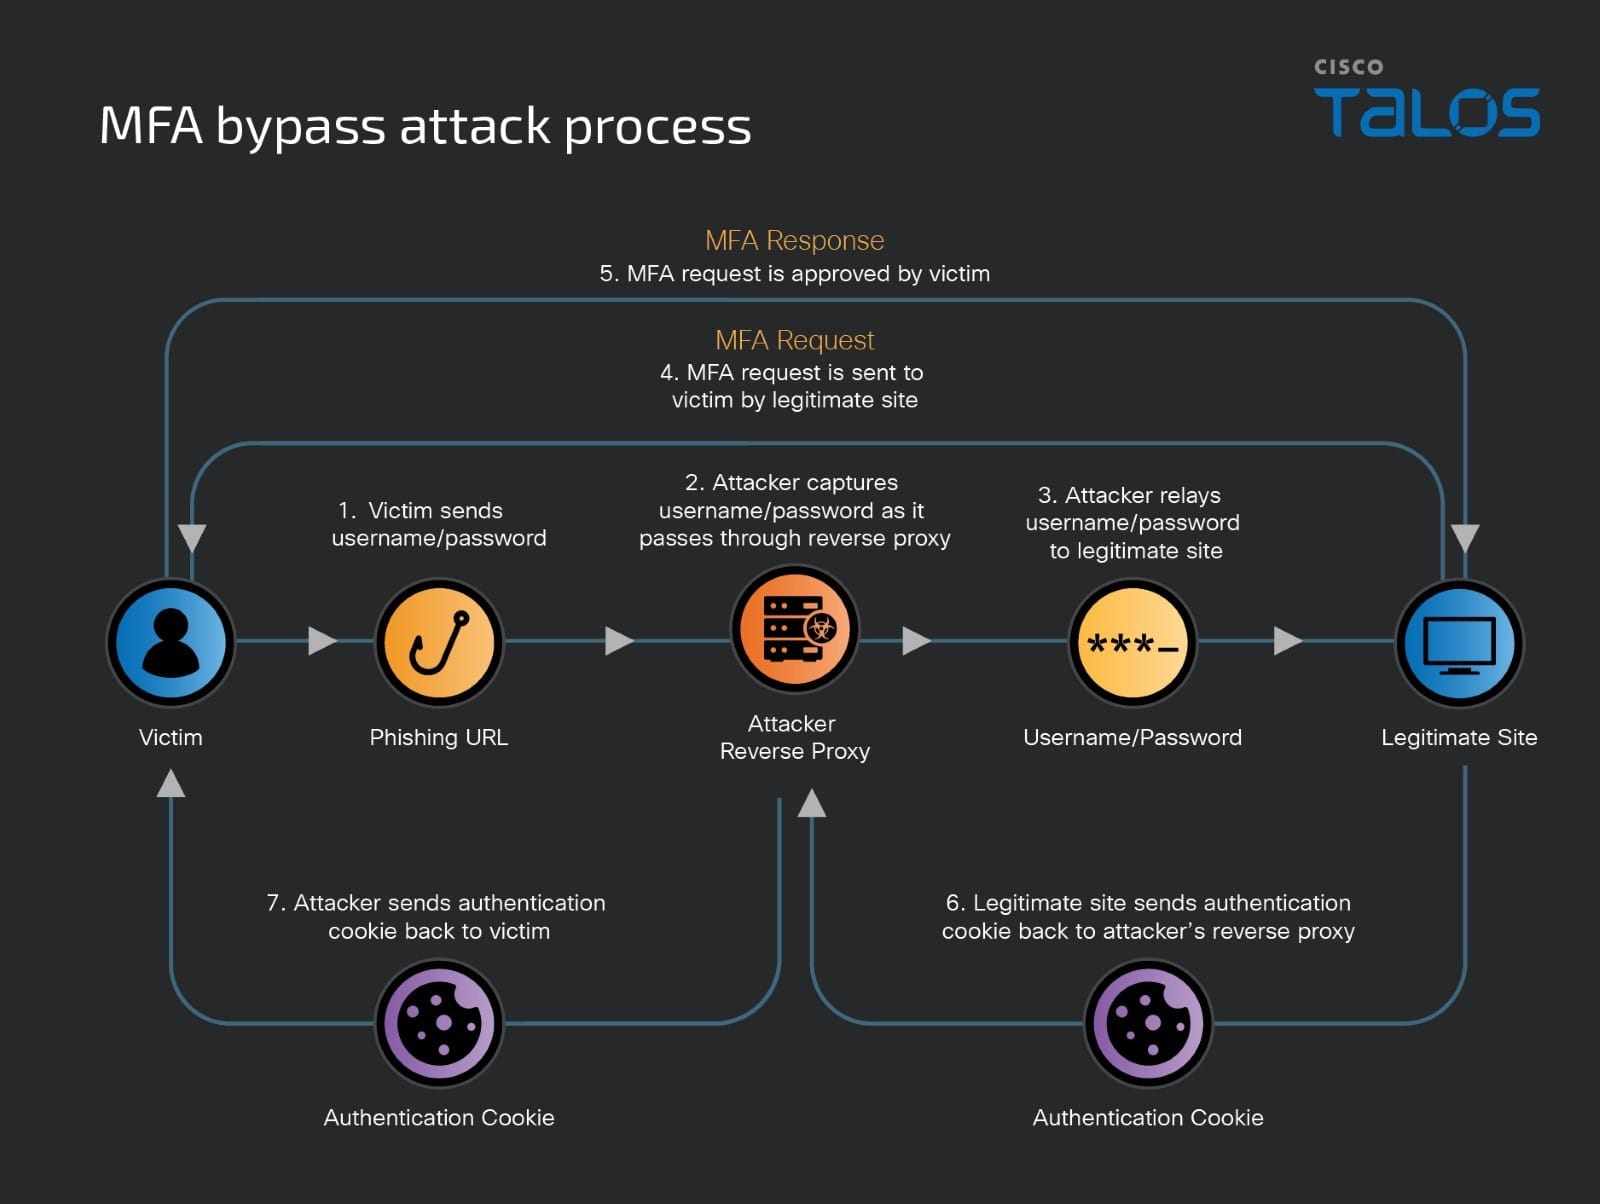
AiTM phishing campaigns follow a distinct pattern:
AiTM attacks, MFA bypass
Image: Cisco Talos
  1. Victim receives a phishing link (e.g., to a fake login page).
  2. That link connects to a reverse proxy server, not a clone.
  3. Victim enters credentials, which are relayed to the legitimate site.
  4. The MFA prompt is passed to the victim as normal.
  5. Upon approval, the authentication cookie is intercepted.
  6. Attacker uses this cookie to hijack the session—MFA already passed.

“The attacker now possesses both the victim’s username/password as well as an authentication cookie from the legitimate site,” the report explains.

Tools like Evilginx, originally built for red-team testing, are now fueling many of these attacks. Though open source and legitimate in intent, it has been repurposed by malicious actors.

Cisco Talos notes several indicators of Evilginx-powered attacks:

  • New or suspicious TLS certificates from Let’s Encrypt
  • Session cookies used simultaneously from different IPs
  • URL path anomalies from servers not matching legitimate services
  • TLS fingerprint mismatches between proxies and real domains

“Unless the attacker is careful, for a time, there will be two different users with different User-Agents and IP addresses using the same session cookie.”

The report highlights WebAuthn, a passwordless authentication method using public-key cryptography, as a robust defense against AiTM threats.

“WebAuthn is essentially passwordless… No passwords are ever entered into a web form, and no passwords are transmitted over the internet.”

WebAuthn protects users in two key ways:

  • Origin binding: credentials are tied to specific domains, breaking proxy-based phishing chains.
  • No password entry: removes the opportunity for interception entirely.

Unfortunately, adoption remains low despite its strength. Cisco Talos’ telemetry data suggests WebAuthn still accounts for a very small portion of all MFA traffic.

Cisco Talos urges organizations to rethink their authentication strategy in light of these evolving threats:

  • Implement phishing-resistant MFA like WebAuthn or hardware tokens
  • Audit logs for signs of MFA bypass (e.g., new MFA devices or session reuse anomalies)
  • Educate users on verifying URLs and recognizing AiTM lures
  • Monitor newly registered domains mimicking internal portals

Related Posts:

  • Google Chrome and Mozilla Firefox will support the new password-free standard, WebAuthn
  • Tycoon 2FA: The Evolving Threat Bypassing Multi-Factor Authentication
  • ESET’s Discovery: Blackwood’s AitM Attacks and the NSPX30 Implant
  • Phishing Campaign Bypasses MFA to Target Meta Business Accounts, Putting Millions at Risk
  • CISA Warns of Credential Risks Tied to Oracle Cloud Breach
Add Daily CyberSecurity as a preferred source on Google

Related coverage

  • Microsoft Agent Framework PyPI Attack Targets Developer Credentials
  • Ubuntu Edge AI Patches Speed Up Vulnerability Fixes
  • Apple Patches worse_query iOS Vulnerability in 27.3 Beta 2
  • macOS 27.3 Permissions Introduce Folder and App Controls
  • uBlock Origin UXSS Vulnerability Allows Arbitrary Cross-Site Scripts
  • DarkSword iOS Malvertising Targets Unpatched Apple Devices
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of Daily CyberSecurity. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Account Takeover AiTM authentication cybersecurity MFA Multi-Factor Authentication phishing

Leave a Reply Cancel reply

You must be logged in to post a comment.

🚨 Active Exploits in the Wild

  • CVE-2010-20126CVSS 5.1
    Virtual Keyboard plugin for SquirrelMail through 0.9.1 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2012-20007CVSS 9.3
    ThinkPHP 2.0 through 2.2 and 3.0 Lite mode contains an eval injection vulnerability in the Dispatcher PATH_INFO parsing,...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2012-20008CVSS 8.7
    openSIS 5.1 before 9.0 contains a local file inclusion vulnerability that allows authenticated users to include arbitrary files...
    Watchtower Verified📅 Updated: Nov 18, 2026
  • CVE-2026-119618CVSS 8.1
    Concurrent Execution using Shared Resource with Improper Synchronization vulnerability in Apache HTTP Server's mod_http2 in assign_headers() can lead...
    Admin intel📅 Updated: Nov 18, 2026
  • CVE-2024-10441CVSS 9.8
    Improper encoding or escaping of output vulnerability in the system plugin daemon in Synology BeeStation OS (BSM) before...
    CISA KEV📅 Added to KEV: Nov 18, 2026
  • CVE-2026-40217CVSS 8.8
    LiteLLM through 2026-04-08 allows remote attackers to execute arbitrary code via bytecode rewriting at the /guardrails/test_custom_code URI.
    CISA KEV📅 Added to KEV: Nov 18, 2026
  • CVE-2026-90817CVSS 9.8
    An unauthenticated Remote Code Execution vulnerability was found in the survey passthrough routing and Data Import processing logic,...
    CISA KEV📅 Added to KEV: Nov 18, 2026
  • CVE-2026-90436CVSS 9.8
    ** UNSUPPORTED WHEN ASSIGNED ** Deserialization of an inbound SOAP fault in Apache Axis 1.x allows unauthenticated remote...
    CISA KEV📅 Added to KEV: Nov 18, 2026
Powered by CVE Watchtower

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Get free CVE alerts Pro from $7/mo

Critical Vulnerabilities

  • CVE-2026-131287CVSS 9.6
    Remote Code Execution (RCE) through the REST API in Splunk SOAR. In Splunk SOAR versions below 8.8.0, a...
    📅 Updated: Nov 19, 2026
  • CVE-2026-131253CVSS 9.9
    Remote Code Execution (RCE) through the App Wizard in Splunk SOAR. In Splunk SOAR versions below 8.8.0, an...
    📅 Updated: Nov 19, 2026
  • CVE-2026-131202CVSS 9.1
    Remote Code Execution (RCE) through REST API Path Traversal in Splunk Enterprise Security. In Splunk Enterprise Security versions...
    📅 Updated: Nov 19, 2026
  • CVE-2026-76535CVSS 9.1
    Authentication Bypass through the RapidDiag REST API in Splunk Enterprise. In Splunk Enterprise versions below 10.6.1, 10.4.5, 10.2.9,...
    📅 Updated: Nov 19, 2026
  • CVE-2026-76536CVSS 9.4
    Authentication Bypass through the Cluster Configuration REST API in Splunk Enterprise. In Splunk Enterprise versions below 10.4.5, 10.2.9,...
    📅 Updated: Nov 19, 2026
  • CVE-2026-123965CVSS 9.3
    A prompt injection vulnerability in all versions of Jet Admin Cloud Platform allows a remote attacker with a...
    📅 Updated: Nov 19, 2026
  • CVE-2026-131914CVSS 9.3
    Deserialization of untrusted data in double-submit cookie vs. form field validation in Idunno.AntiCsrf versions through 0.9.1 Beta on...
    📅 Updated: Nov 19, 2026
  • CVE-2024-10441CVSS 9.8
    Improper encoding or escaping of output vulnerability in the system plugin daemon in Synology BeeStation OS (BSM) before...
    CISA KEV📅 Added to KEV: Nov 18, 2026📅 Updated: Nov 19, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About Daily CyberSecurity
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DMCA
  • Privacy Policy

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.