 Do Son
A Claude Code email leak exposed user addresses in User-Agent headers, prompting Anthropic to issue privacy updates and command blocking.
phishing
Google brings Chrome Incognito Safe Browsing real-time checks to private sessions, blocking fast-moving phishing domains while protecting user privacy.
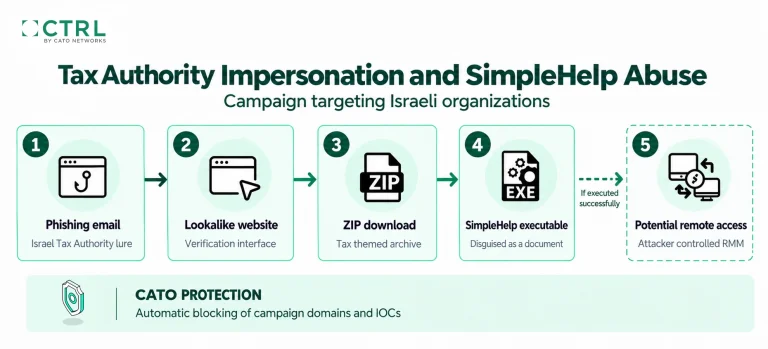
Cato CTRL exposed the MuddyWater SimpleHelp campaign in Israel using tax lures. Learn how the MuddyWater SimpleHelp campaign abuses RMM tools.
A CAPCOM ID data breach exposed 11.77 million records, including emails and login activity. No payment data was leaked.
The EU's Booking.com DSA investigation targets fake listings, Booking.com phishing scams and hidden ads. Fines could hit 6% of global turnover.
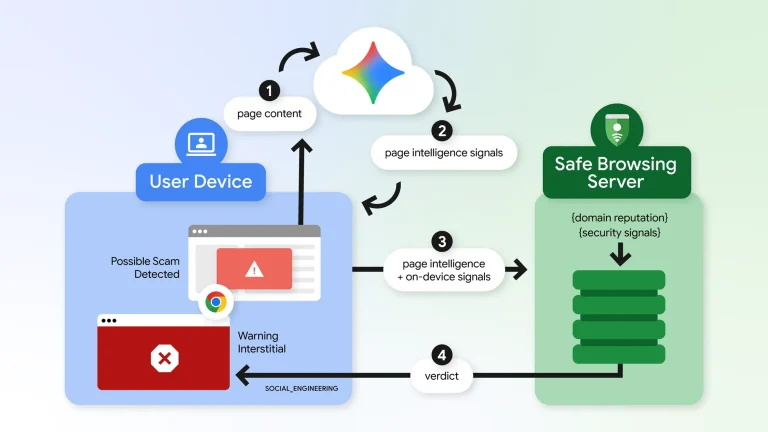
Chrome ClickFix protection in Enhanced Protection flags risky clipboard commands and uses cloud Gemini AI to block scam sites.
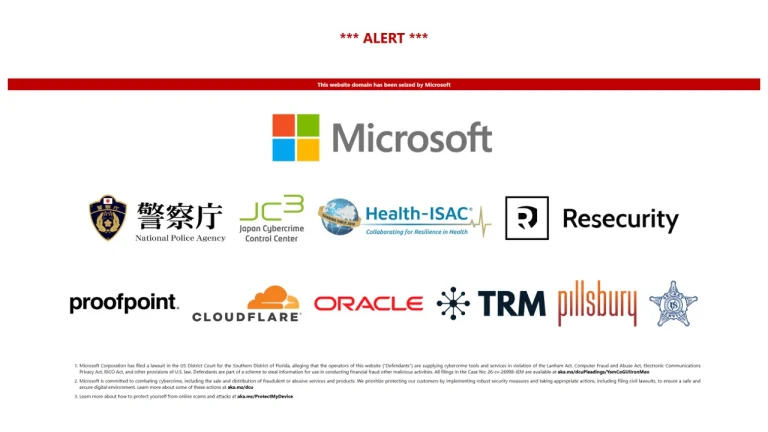
Microsoft and Proofpoint executed a CoGUI phishing kit takedown, seizing domains from YAM Store and Iron Man after 1B scam messages hit 75,000 firms.
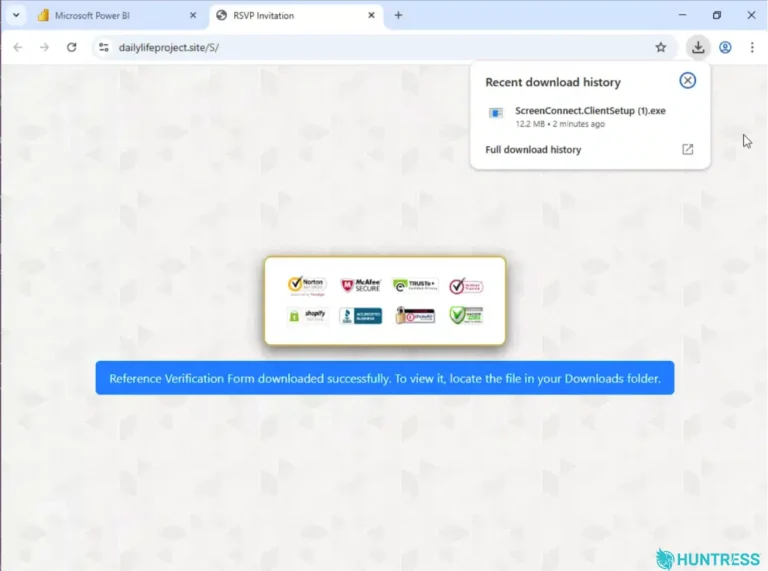
A Power BI phishing campaign uses Microsoft's real domain to install rogue ScreenConnect clients. Learn how it works and how to block it.
Denmark CPR data breach: attackers abused a firm's access, leaving CPR numbers exposed for 8.8 million people. Here is what to know and do.
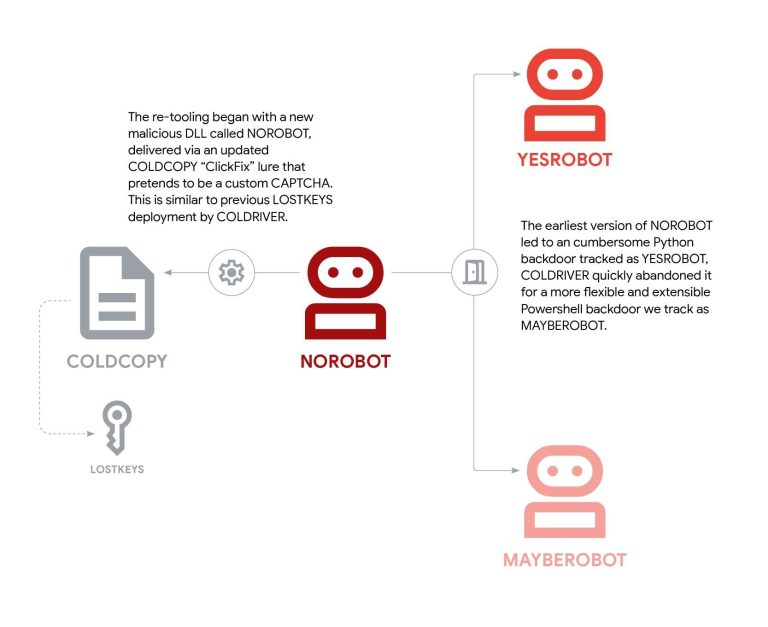
Star Blizzard RedFlick phishing hit 100+ groups that back Ukraine, using scheduled tasks to drop the CosmicPulse backdoor after a single click.
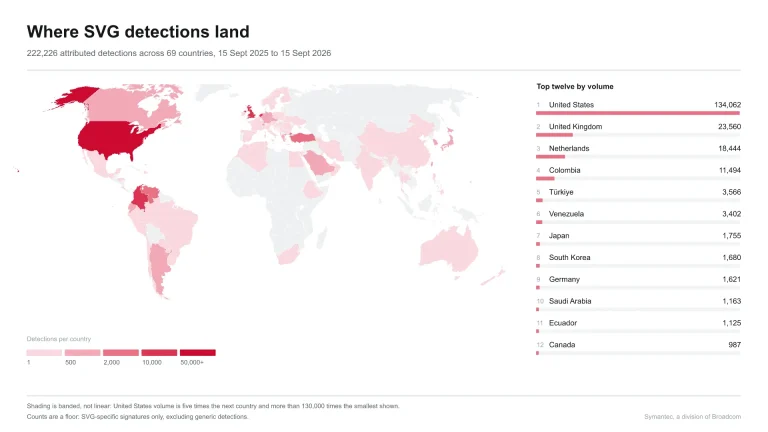
SVG phishing attacks jumped in August 2026. Symantec explains how SVG smuggling hides fake logins and malware inside image files, and how to stop it.
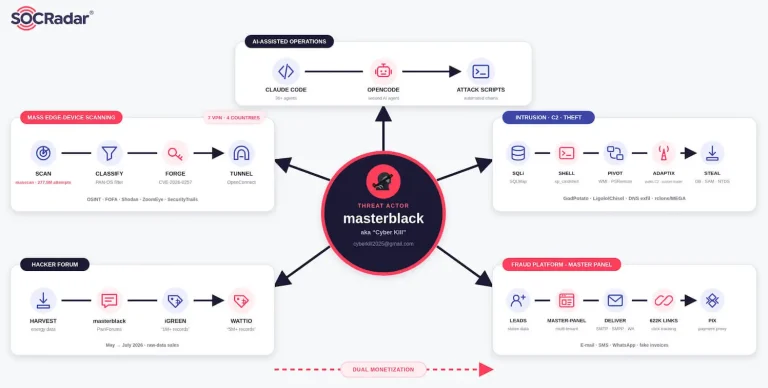
Operation Master used a GlobalProtect flaw to steal utility data, then fed it into an invoice fraud platform that sent 2.4M+ fake bills in Brazil.
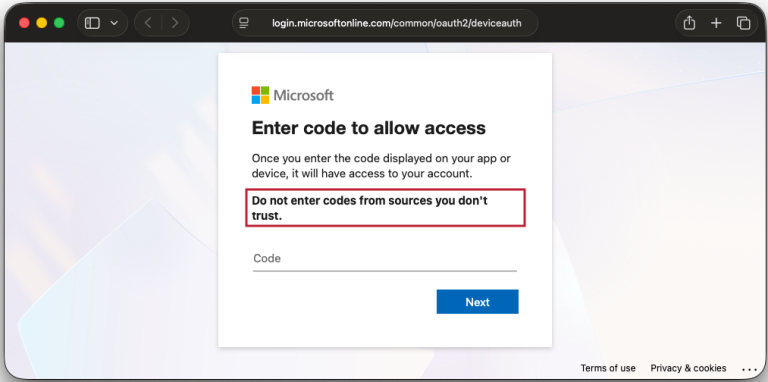
Security researchers uncovered a new GhostCode phishing kit. Learn how the GhostCode phishing kit bypasses MFA to hijack enterprise Microsoft 365 accounts.
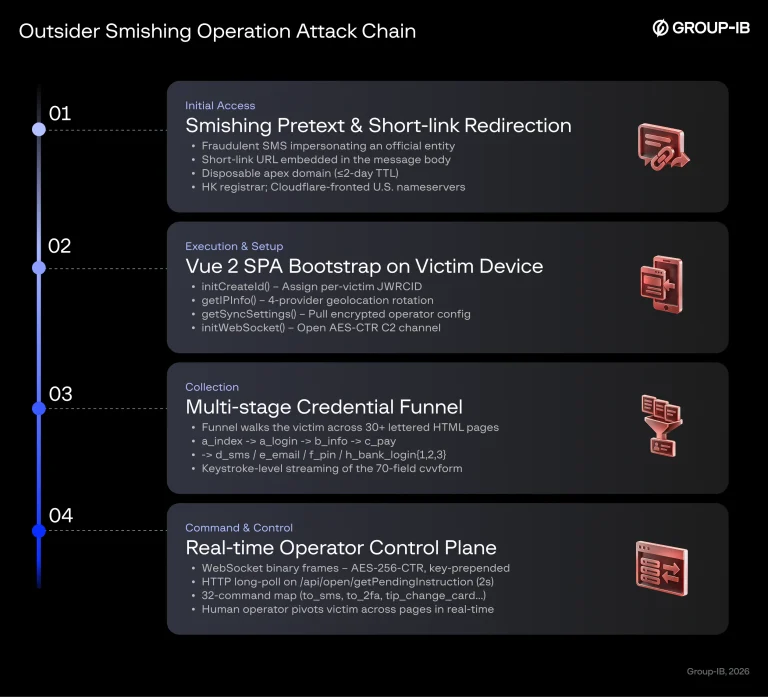
Group-IB exposed a new Smishing Triad phishing kit used by Outsider. Learn how this Smishing Triad phishing kit steals financial data worldwide.
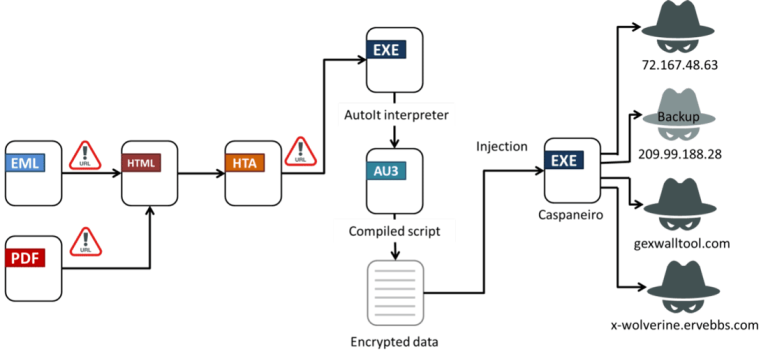
A new Casbaneiro banking trojan campaign hits Latin America. Learn how the Casbaneiro banking trojan evades detection and targets bank logins.

A sophisticated phishing campaign uses redirect chains to abuse Google infrastructure. Learn how attackers abuse Google infrastructure to steal credentials.
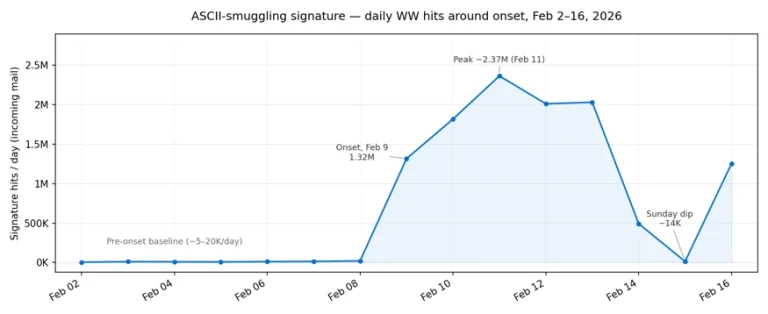
Microsoft uncovered an ASCII smuggling phishing evasion campaign hitting email inboxes. Learn how attackers weaponize invisible Unicode tags.
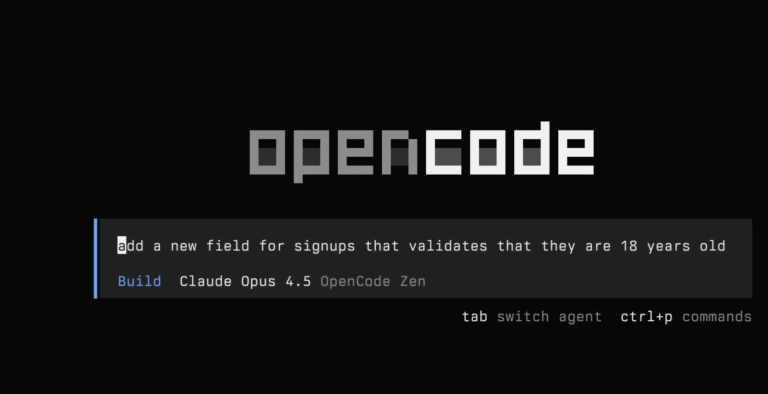
Threat analysts reveal Kimsuky uses AI agent opencode to mass-produce phishing decoys. Discover how the group leverages AI to enhance its LNK attacks.
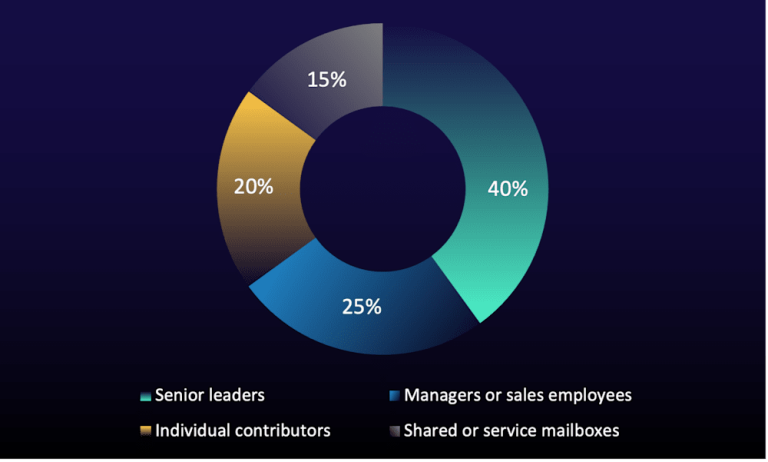
A Microsoft 365 RejectDirectSend bypass lets attackers spoof internal emails. Learn how this RejectDirectSend bypass works and how to protect your tenant.
The Trezor data breach at shipping partner ShipMonk exposed about 80,000 customers' order data. Wallets are safe, but phishing risk is high.
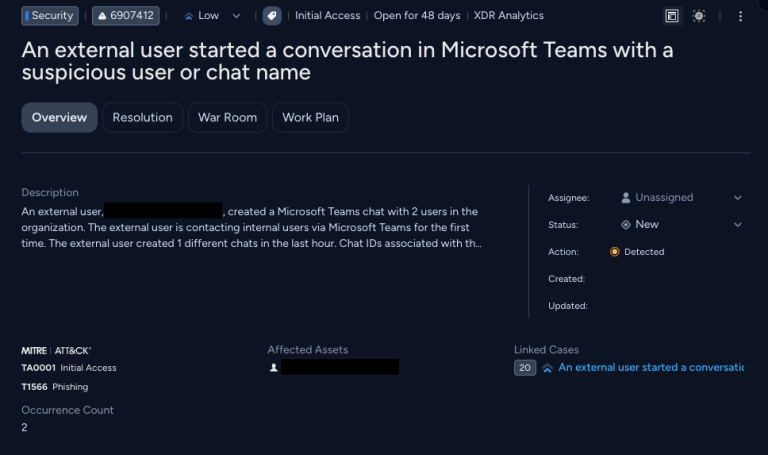
Discover how the Spring Ring vishing campaign uses Microsoft Teams phishing tactics to trick employees into installing malware and giving up remote access.

A new AiTM phishing campaign targets healthcare. Learn how this healthcare AiTM phishing campaign chains compromised accounts to bypass MFA.