
 Do Son
The FBI warns that cyber criminals increasingly use traffic distribution systems to redirect users to malicious websites, phishing pages, and malware scams.
phishing
SHEETCREEP malware is a C# Google Sheets RAT tied to APT36. It hides command-and-control inside Google Sheets to evade network detection.

A new device code phishing campaign abuses Microsoft's OAuth flow to hijack Microsoft 365 accounts, no password stealing needed. How to spot it.

Threat actors are using AI social engineering lures to distribute malware and steal credentials. Learn how fake ChatGPT and DeepSeek campaigns work.

UNK_DeadDrop phishing campaigns are targeting developers with fake jobs to deliver Overlord malware. Learn how to defend against this North Korean threat.

Discover how Fluffy Wolf phishing attacks target Russian organizations with the new PowerLoader malware to deploy PureRAT and Pay2Key ransomware.

Discover how a simple phishing email triggers a complex Agent Tesla infection chain, using process injection and in-memory loading to steal sensitive data.
The Uncanny Automator breach exposed customer data and pushed a backdoored plugin build (7.3.0.5). Here's what happened and how to secure your site.

Operation TaxShadow uses fake tax notices to spread in-memory tax phishing malware with WebSocket C2, per CYFIRMA's new report.

Read the Group-IB phishing report detailing the massive Smishing Error524 campaign targeting millions across 72 countries with advanced evasion tactics.

Cybercriminals are ramping up football fan scams and World Cup 2026 fraud. Protect yourself from fake merchandise, phishing, and lottery traps today.

Paper Werewolf APT targets industrial sectors with PaperGrabber stealer and EchoGather RAT. Learn to detect their AI-assisted loaders and custom tools.
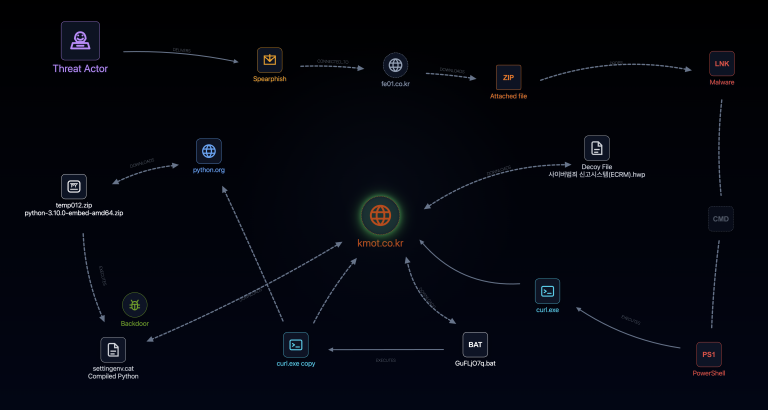
Genians unmasks an APT37 campaign using environment variable tricks and compiled Python malware to bypass EDR. Protect your network from these stealthy lures.
Job seekers beware: The JobStealer trojan poses as video meeting apps to hijack 300+ crypto wallets and Telegram data. Learn how to spot this 2026 threat.
Sophos X-Ops uncovers a fake Claude AI site (claude-pro.com) distributing an undocumented backdoor via DonutLoader. Protect your team from AI-themed lures.
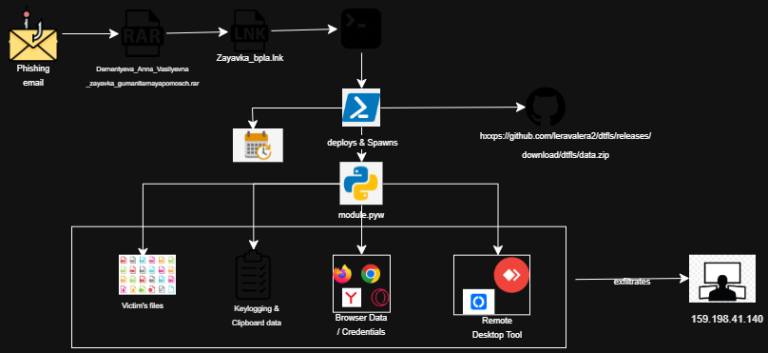
CRIL exposes a cyberespionage campaign using fake humanitarian aid forms to deploy fileless Python malware via GitHub for full-spectrum surveillance.
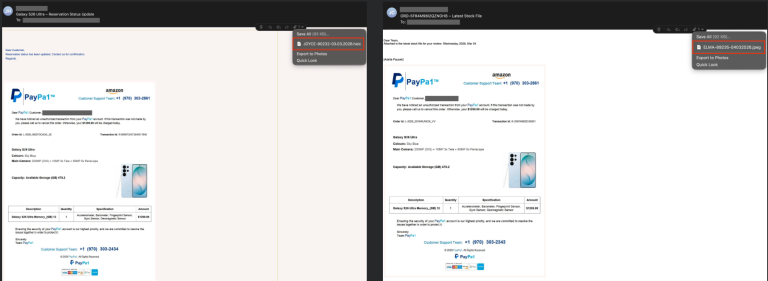
Cisco Talos reveals the rise of TOAD attacks. 55% of scam campaigns now use VoIP "anchors" to bypass email filters and trick victims into calling fraud centers.
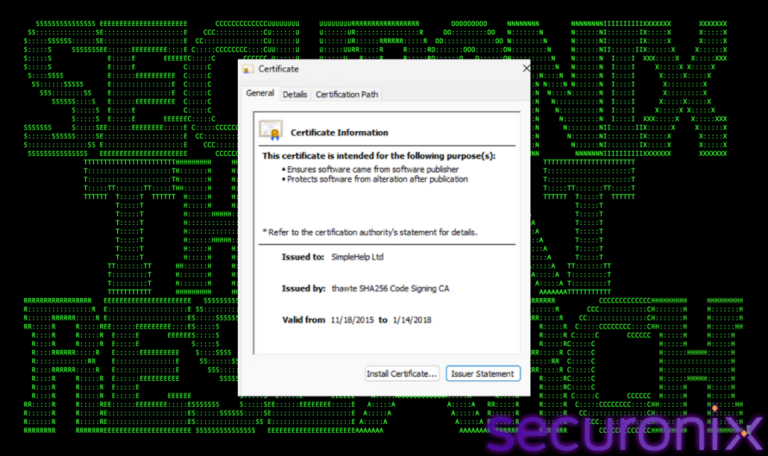
Securonix exposes an 80+ organization breach using "self-healing" RMM tools and Safe Mode persistence. Standard antivirus is blind—learn how to hunt it!

Google AppSheet is being abused by "AccountDumpling" to steal 30,000 Facebook accounts. Learn how this Vietnamese-linked group bypasses SPF/DKIM filters.
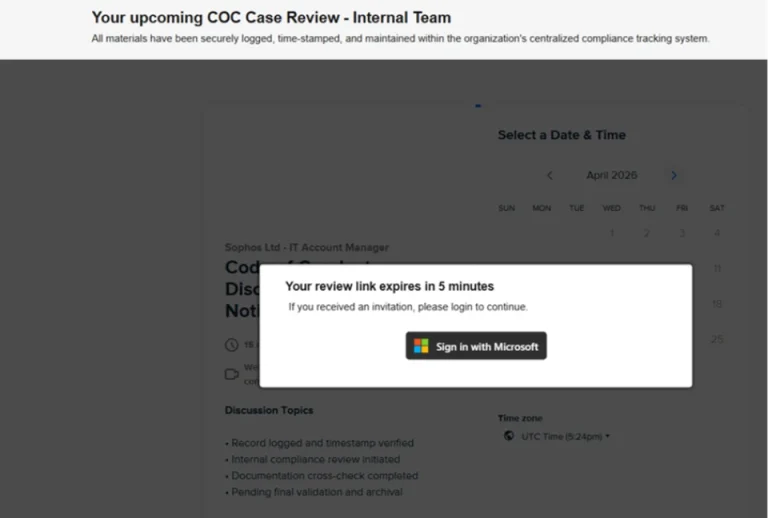
Microsoft warns of a massive AiTM phishing campaign targeting 13,000+ orgs. Using fake disciplinary lures, attackers bypass MFA to hijack active sessions.

Scammers are leveraging Amazon SES and leaked IAM keys to bypass security filters. Learn how to protect your organization from this high-trust phishing surge.
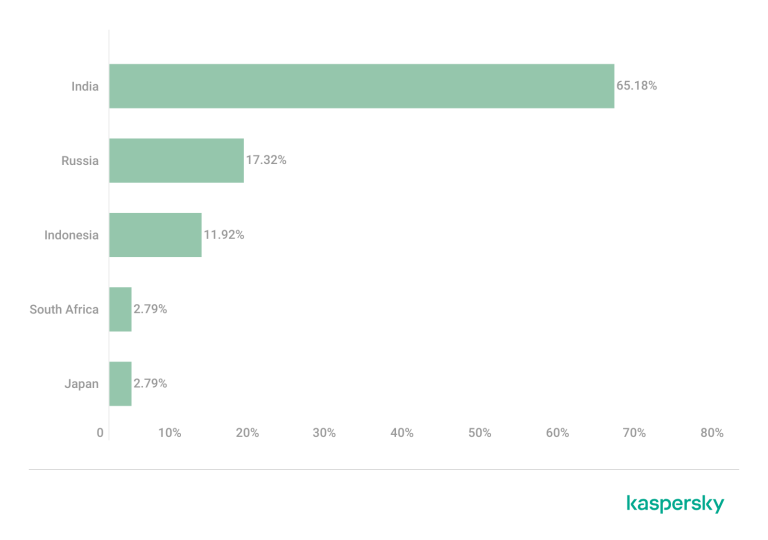
Silver Fox targets India and Russia with tax-themed phishing and the new ABCDoor backdoor. Learn how this Python-based threat hijacks screens and data.